Mastering Nmap: A Comprehensive Guide to Network Discovery and Security
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
InfoSec Compliance & AI Governance For over 20 years, DISC InfoSec has been a trusted voice for cybersecurity professionals—sharing practical insights, compliance strategies, and AI governance guidance to help you stay informed, connected, and secure in a rapidly evolving landscape.

Sep 03 2023
Aug 31 2023
Juniper Networks, a company that manufactures widely used networking equipment as well as security solutions, has issued a warning about vulnerabilities that are present in the operating systems of many of its devices.
The business has acknowledged in not one but two distinct security alerts that were either released or revised this week that the Junos OS and the Junos OS Evolved operating systems may be susceptible to attacks. Additionally, the corporation issued an updated warning about vulnerabilities that are present in the SRX firewalls and EX switches used by the company.
In a fresh warning it said that earlier versions of the operating systems might get stalled due to the processing of erroneous messages in the code known as the Border Gateway Protocol (BGP), which is responsible for directing all traffic on the internet.
To be more specific, a “UPDATE” message that is formatted in a particular manner “will eventually create a sustained Denial of Service (DoS) condition for impacted devices,” which would prevent such devices from carrying out their duties.
A security advisory that had been issued in June and was connected to BGP was also updated by the business on Wednesday. This issue also addressed the possibility of attacks that denied service to users.
In both instances, the corporation was providing workarounds as a means of resolving the problems “out of cycle” from its typical operating system update releases.
A third warning, issued on August 17 and most recently updated on Wednesday, refers to vulnerabilities in J-Web, which is an interface for the SRX firewalls and EX switches used by the firm, which researchers in the security field at Watchtower Labs investigated.
In such a scenario, “an unauthenticated, network-based attacker” has the ability to link together the exploitation of the vulnerabilities “to remotely execute code on the devices.”
In addition, the Cybersecurity and Infrastructure Security Agency (CISA) released a brief advisory on Wednesday about the vulnerabilities in the operating system.
In addition to that, researchers carried out extensive study, the results of which offered a comprehensive understanding about the exploitation of this weakness as well as the vulnerabilities associated to it.
In the course of their investigation, the researchers focused on two particular vulnerabilities in Juniper (CVE-2023-36846 and CVE-2023-36845), both of which were described in the company’s security advisory. Both of these vulnerabilities, Missing authentication for key functions and PHP External Variable Modification, have something in common: they both affect PHP.
After further investigation, it was found that the J-Web was totally developed in PHP, and that the authentication process is handled by a user class. In addition, a PHP file called webauth_operation.php was found.
In addition, a total of 150 distinct functions, which served a variety of purposes ranging from basic aids to the formatting of IP addresses, were found to be in use. These functions ranged in complexity from simple to complicated. Every one of these tasks required interaction with the command line interface (CLI) of the appliance.
Researchers from Watchtwr have produced a comprehensive analysis, which can be seen on their website. The report contains in-depth information on these vulnerabilities as well as the techniques used to attack them.
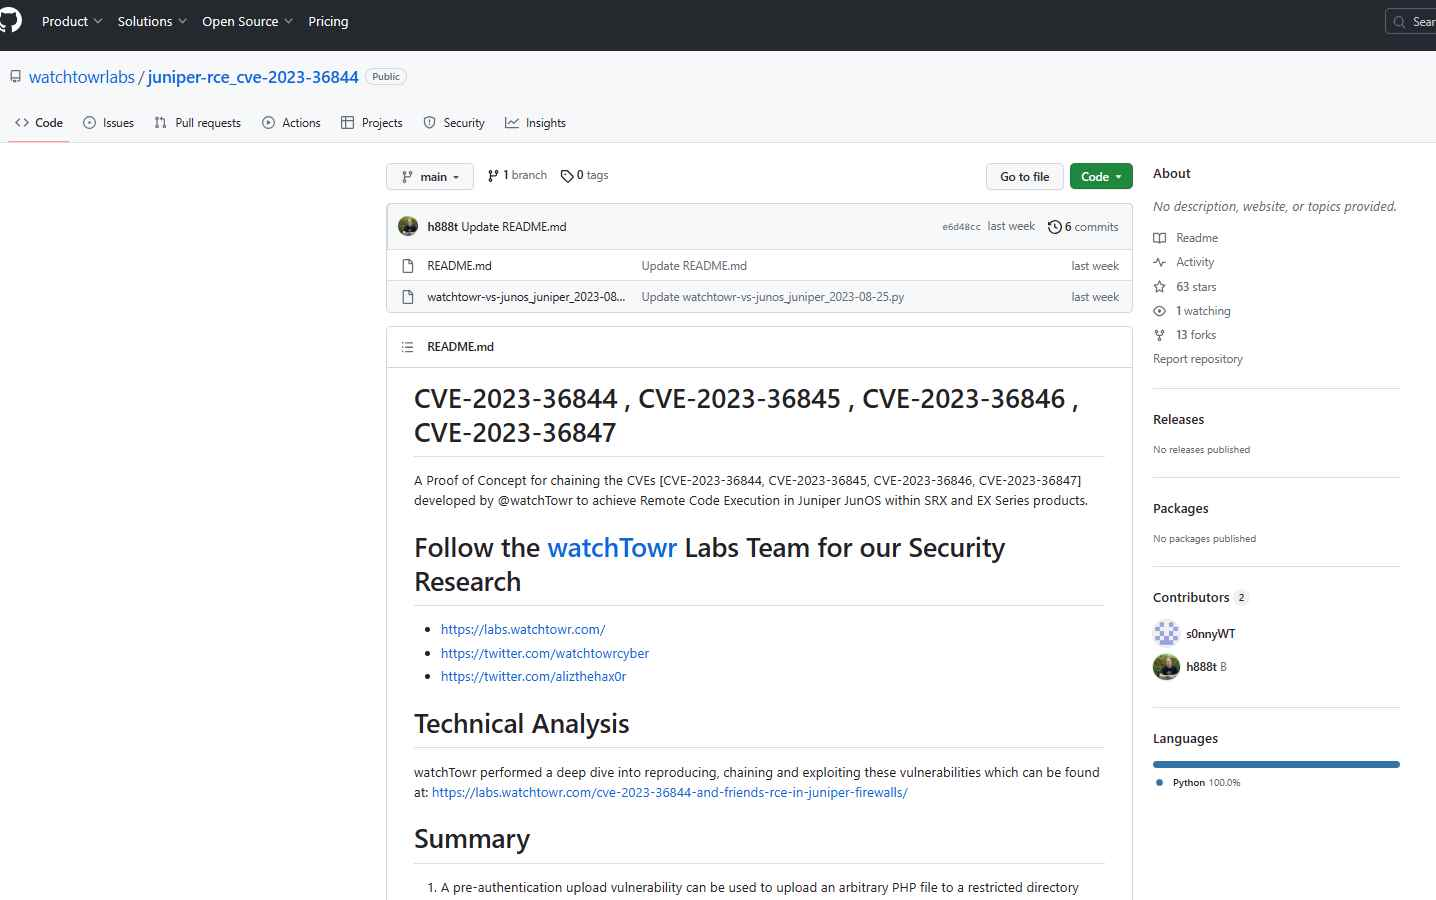
It has been announced that a repository on GitHub containing the Proof-of-concept for this vulnerability has been made available. Security professionals may utilize this repository to test and repair their susceptible environments using the Proof-of-concept.
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 30 2023
Email communication is essential for personal and professional contact in the modern digital environment.
Email is widely used, making it a perfect target for cybercriminals, leading to increased phishing attempts, spam, and email spoofing.
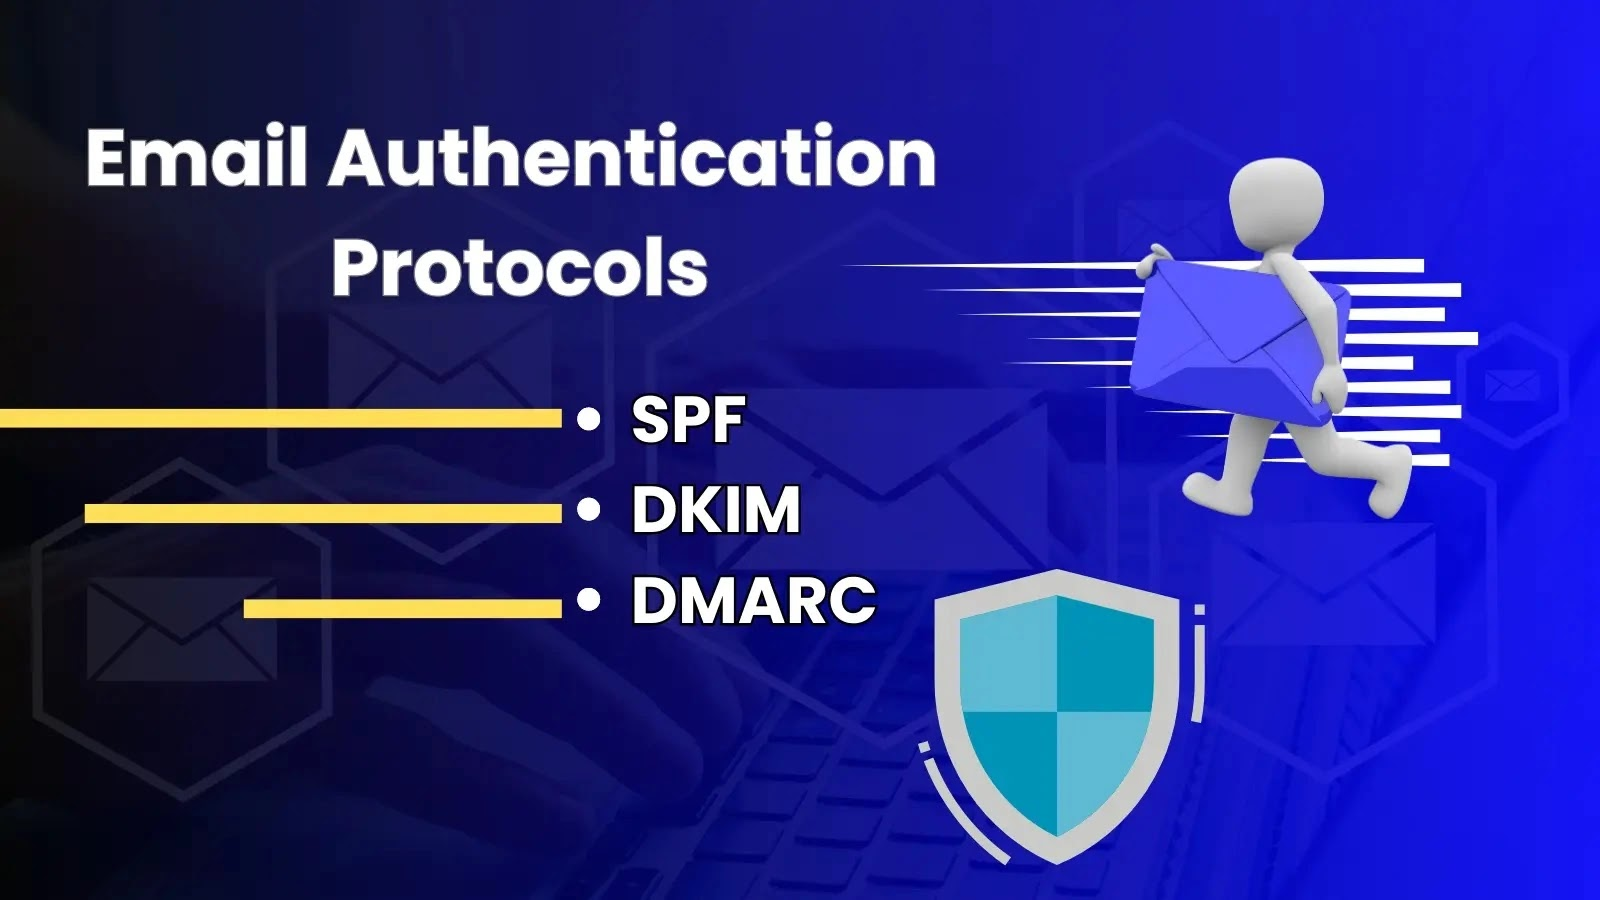
Strong email security measures are becoming essential as these threats become more sophisticated. Email authentication techniques like SPF, DKIM, and DMARC are crucial in situations like this.
By authenticating the sender’s identity and confirming the accuracy of the received messages, these procedures act as the first line of protection against email-based threats.
This article will thoroughly review these three important email authentication methods, including their roles, how they cooperate, and why they are crucial for upholding a reliable and secure email communication infrastructure.
Secure email communications can be achieved through Email Authentication Protocols, standards, or technologies that validate the sender’s identity and protect the message’s integrity.
These standards aim to protect users from spam, phishing, and other malicious email-based assaults.
As a bonus, they make it less likely that a good email will be incorrectly deleted as spam or malware.
Here are the primary email authentication protocols commonly in use:
The Sender Policy Framework (SPF) is an email authentication technology developed to prevent spam.
By letting domain owners choose which mail servers can send emails on their behalf, SPF assists receiving servers in authenticating the sender of incoming messages.
For this purpose, the DNS records of the domain are consulted to ensure that the emails come from the addresses they claim to represent.
The Sender Policy Framework (SPF) aims to improve email security by limiting the possibility that an unauthorized sender may use a specific domain in the “From” address.
This helps keep the sender’s and the recipient’s inboxes free of unwanted messages and strengthens the confidence each party has in email.
Sender Policy Framework (SPF) is an email authentication system that checks the sender’s name to stop email spoofing and phishing. But, like any other system, SPF isn’t completely safe from possible attack vectors. Here are some possible ways to attack SPF:
Manipulating SPF Records: Attackers could try to change or create SPF records by changing the DNS records of a domain. This would let them list unauthorized IP addresses or servers as valid senders. This can make it possible for tactics like spoofing or phishing to work.
Domain Hijacking: If an attacker takes control of a legal domain, they can change the SPF records to include their own malicious servers. This can cause bad emails that look like they came from a trusted source to be sent.
Subdomain Attacks: SPF records are often set up for an organization’s primary domain, but they might forget to set up SPF records for subdomains. Attackers who send emails from subdomains without the proper SPF records can use this against you.
Inadequate SPF Policies: Organizations may have weak SPF policies that let many IP addresses send emails on their behalf. This can give attackers a bigger pool of possible IP numbers to trick people.
DomainKeys Identified Mail (DKIM) is an email authentication technology that uses encryption to confirm an email’s authenticity.
The sending server adds a distinctive DKIM signature using a private key to each email. The receiving server verifies the signature of the incoming email using a public key obtained from the sender’s DNS records.
If it matches, the email can be trusted as genuine and safe from tampering. DKIM is designed to prevent email spoofing and phishing attacks and guarantee the safe delivery of email communications by verifying the sender’s domain and the message’s encrypted signature.
Solution: Organizations should adopt efficient incident response plans, regularly monitor email traffic for anomalies, and stay updated on emerging threats to stay ahead of the evolving email threat landscape with AI-powered solutions like Trustifi.
To improve upon SPF and DKIM, a new email authentication protocol called Domain-based Message Authentication, Reporting, and Conformance (DMARC) was developed.
Domain administrators can instruct receiving mail servers on what to do with messages that do not pass authentication.
Domain owners can direct mail servers to stop accepting spam by adding a DMARC policy record to their DNS settings. Email traffic and any security risks can be better understood using DMARC’s reporting features.
DMARC is designed to strengthen email security by adding an extra layer of verification, decreasing phishing and spoofing, and increasing the credibility and delivery of legitimate communications.
Aggressive Enforcement: Some organizations may choose to use DMARC with a strategy of “quarantine” or “reject” right from the start. This can work, but if the policy isn’t carefully set, it can also cause valid emails to be blocked.
Reporting Address Spoofing: Attackers could try to change the DMARC reporting address to send reports of failed DMARC checks to sites they control. This could give them a chance to learn more about how the organization’s email system works.
Targeted Spoofing: Attackers could try to pose as people or parts of an organization that haven’t fully set up DMARC. This specific method makes it more likely that their emails will be read.
As with other email-related attacks, attackers could use social engineering to get receivers to ignore DMARC warnings or think a DMARC-failed email is real.
SPF records are TXT (text) records in the DNS. Emails from this domain must be sent from the IP addresses or parts specified in these records.
The recipient’s email server will check the SPF record for the sender’s field in the Domain Name System (DNS) to ensure the email is legitimate.
Example SPF record:
v=spf1 ip4:192.0.2.1 ip6:2001:db8::1 include:example.com all
DKIM records are similarly stored in DNS, although they are TXT entries. These entries store the public key to authenticate the domain’s digital signatures in outgoing emails.
The DKIM record is retrieved from the DNS by the receiving email server, which then uses the public key to verify the signature and ensure the email’s authenticity.
Example DKIM record:
v=DKIM1; k=rsa; p=MIGfMA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQDnWLKu6qIH66AjqkMYyq3A5bkD

  sY+T4rQzSXFJWzh7DQoKmmrkRDbCIPRrkRHF/EpTExGDD2P8WOEqdGTfVbRy14

  5k3soVGMItcL1QvWskhNKLQYGJME6XE1WUCmAw29FcYKavqnGQFWFpDBIMVFOFw

7/TZS0Lj1QIDAQABDNS also stores DMARC records in the TXT record format. The measures to take if an email fails SPF or DKIM checks are provided in the domain’s DMARC policy, defined by these records.
To keep the domain owner aware of authentication actions, DMARC additionally provides reporting tools.
Example DMARC record:
v=DMARC1; p=quarantine; pct=25; rua=mailto:reports@example.com; ruf=mailto:forensics@example.comIt takes multiple procedures and the capacity to query DNS records to ensure an email complies with SPF, DKIM, and DMARC.
Here are the measures taken to ensure that an email adheres to these standards:
Example SPF Record: 'v=spf1 ip4:192.168.0.1 -all'This example authorizes the IP address ‘192.168.0.1’ to send emails on behalf of your domain and denies all others.
Example DKIM Record: 'v=DKIM1; k=rsa; p=MIGfMA0...'This example specifies that the key type is RSA and includes the public key.
Example DMARC Record: 'v=DMARC1; p=reject; rua=mailto:report@example.com'This example specifies that emails that fail the DMARC check should be rejected and that reports should be sent to ‘report@example.com’.
The SPF, DKIM, and DMARC standards are essential components of a reliable email security architecture in an age when email is vulnerable to a wide range of attacks.
Though each has advantages and disadvantages, they provide an enormous defense against a significant fraction of email-based attacks.
By implementing these authentication processes, your email systems’ security will improve, and your emails’ deliverability will also be enhanced, reducing the possibility that your legitimate messages will be miscategorized as spam.
Applying these standards to your digital communication infrastructure can significantly improve the safety and dependability of your communications.
The Art of Email Security | Email security: attack and defence
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 29 2023
Aug 29 2023
Does anyone think the chances of surviving a plane crash increase if our tray tables are locked and our carry-on bags are completely stowed under our seats? That we’ll be OK if the plane hits a mountain if we have our seat belts buckled securely across our waists? Not even the flight attendants, who will be responsible for throwing us off the plane if we don’t comply, really believe those rituals make us safer. And yet, we check the box every flight because a government agency said we can’t fly unless we do so...
I’m starting to wonder if the obsession with checking boxes in cybersecurity might be akin to securing our tray tables before take-off. We do as we’re told, check all the boxes, pat ourselves on the back, and in the process, distract ourselves from our ultimate goal: stopping the bad actors and protecting our data.
I started to think about this somewhat disconcerting cybersecurity community reality when scanning the titles of some of the attendees at a recent regional cybersecurity conference. I was surprised by the frequency of titles that combined security with compliance. To wit: Manager Information Security and Compliance, Manager, Security and Compliance Advisory, Senior Manager Internal Controls and Compliance, Sr. Manager – IT Security & Compliance (among others). To add to this: countless “auditor” titles – roles designed specifically to assure fealty to various standards requirements.
Nearly all enterprise breaches originate in one of three ways, and all cybersecurity professionals know this:
So, let’s try an experiment. Ask a CISO or experienced cybersecurity expert how they would defend their organization against these three breach types if:
1. They could completely ignore standards and compliance, and they’d be given no credit for any level of compliance (and there would be no ramifications for non-compliance)
2. They could re-deploy every dollar of budget allotted to standards compliance and auditing any way they liked
3. Their single objective was to win the game (stop the bad actors, and minimize their organization’s risk of a compromise)
How many would determine that the best use of their resources would be to attain or retain compliance with a cybersecurity standard? And how many would deploy those compliance and auditing resources to patch more vulnerabilities, invest in additional cybersecurity expertise, tools to identify and reduce their external threat footprint, and myriad other effective measures to genuinely reduce their organization’s cyber risk?
It’s not as if dedication to compliance is any more of a guarantee against a breach than any other technology, strategy or prayer. Here are a few examples of compliant companies that have suffered high profile breaches (thanks to ChatGPT for saving me the hours of research otherwise required to build this list):
This is, of course, not an exhaustive list. Show me a large enterprise that was breached and I’ll show you a large enterprise adhering to multiple compliance standards.
Indeed, just this month, several US government agencies were victims of an attack exploiting a vulnerability in file transfer software (albeit a zero-day). It’s fair to assume there are several regulations strictly adhered to by the agencies just breached.
So, why do we continue to be obsessed with cybersecurity compliance, standards, frameworks, etc.? The obvious reason is that organizations can be fined for non-compliance.
And yet, there’s been little effort among cybersecurity experts to challenge regulatory agencies. Indeed, many enthusiastically embrace compliance and congratulate themselves and their teams for achieving it. And, of course, no one loves compliance standards more than vendors, just like every barber in the world would celebrate a new law requiring everyone to get a haircut weekly.
The less obvious reason for our community’s love for compliance is that it covers behinds. “Yes, we were breached, but we did everything we were supposed to do, so don’t blame us.” Coaches in every sport will identify that as a loser’s attitude. Champions know there’s no checkbox formula for winning, and there’s no excuse for losing, especially “we did everything we were supposed to and still lost.” It’s cliche’, but the best teams and athletes “just know how to win.”
Am I suggesting we abandon frameworks and compliance? Not immediately, and not without serious debate and analysis. But there is a case to be made that the compliance-centric philosophy governing cybersecurity decision-making today simply isn’t working, and we in cybersecurity are the living embodiment of (not) Einstein’s definition of insanity: doing the same thing over and over and expecting a different result.
Cybersecurity spending continues to increase and yet breach incidents are increasing as well. It shouldn’t be sacrilegious to propose that we consider changing our foundational philosophy from checking boxes on a compliance audit form to doing whatever makes sense to defend our organizations, and win.
CISO Desk Reference Guide Executive Primer: The Executive’s Guide to Security Program
Security Awareness: Applying Practical Cybersecurity in Your World
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 28 2023
Security Onion is a free and open platform for threat hunting, enterprise security monitoring, and log management. It has been downloaded over 2 million times and is being used by security teams worldwide. Security Onion 2.4 comes with many updates, and the hotfix 2.4.10 release is available on GitHub.

For network visibility, they offer signature-based detection via Suricata, rich protocol metadata and file extraction using Zeek or Suricata, full packet capture via Stenographer, and file analysis via Strelka.
For host visibility, Security Onion offers the Elastic Agent, which provides data collection, live queries via osquery, and centralized management using Elastic Fleet. Intrusion detection honeypots based on OpenCanary can be added to your deployment for even more enterprise visibility. All these logs flow into Elasticsearch, and they’ve built their own UIs for alerts, dashboards, threat hunting, case management, and grid management.
Over the past year of developing Security Onion 2.4, the developers added new features to give you a better experience and make you more efficient:
Security Onion Console (SOC) has many new features to make you more efficient as a defender:
SOC has many new administration features, so you can spend less time managing your deployment and more time hunting adversaries.
Endpoint telemetry is more powerful and easier to manage.
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 27 2023
Windows Forensics, include the process of conducting or performing forensic investigations of systems which run on Windows operating systems, It includes analysis of incident response, recovery, and auditing of equipment used in executing any criminal activity.
Malware Forensics Field Guide for Windows Systems: Digital Forensics Field Guides
Windows event log analysis and incident response guide
Diving Deeper Into Windows Event logs for Security Operation Center (SOC) – Guide
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 26 2023
The cybersecurity insurance sector is experiencing swift expansion, with its value surging from around $13 billion in 2022 to a projected $84 billion by 2030, reflecting a robust 26% compound annual growth rate (CAGR). However, insurance providers are encountering challenges when it comes to accurately assessing the potential hazards associated with providing coverage for this category of risk.
Conventional actuarial models are ill-suited for an arena where exceptionally driven, innovative, and astute attackers are actively engaged in orchestrating events that lead to insurable incidents. Precisely gauging potential losses holds utmost importance in establishing customer premiums. However, despite a span of twenty years, there exists a substantial variance in loss ratios across insurance providers, ranging from a deficit of 0.5% to a surplus of 130.6%. The underwriting procedures lack the necessary robustness to effectively appraise these losses and set premiums that reflect a reasonable pricing.
The problem is with the nature of the threat. Cyber attackers escalate and adapt quickly, which undermines the historical-based models that insurance companies rely on. Attackers are continually shifting their maneuvers that identify victims, cause increasing loss, and rapidly shift to new areas of impact.
Denial of service attacks were once popular but were superseded by data breaches, which cause much more damage. Recently, attackers expanded their repertoire to include ransomware-style attacks that increased the insurable losses ever higher.
Trying to predict the cornerstone metrics for actuary modelers – the Annual Loss Expectancy and Annual Rate of Occurrence – with a high degree of accuracy is beyond the current capabilities of insurers. The industry currently conducts assessments for new clients to understand their cybersecurity posture to determine if they are insurable, what should be included/excluded from policies, and to calculate premiums. The current process is to weigh controls against best practices or peers to estimate the security posture of a policyholder.
However, these rudimentary practices are not delivering the necessary level of predictive accuracy.
The loss ratio for insurance firms has been volatile, in a world where getting the analysis wrong can be catastrophic. Variances and unpredictability make insurers nervous. At maximum, they want a 70% loss ratio to cover their payouts and expenses and, according to the National Association of Insurance Commissioners Report on the Cyber Insurance Market in 2021, nearly half of the top 20 insurers, representing 83% of the market, failed to achieve the desired loss ratio.
In response to failures to predict claims, insurers have been raising premiums to cover the risk gap. In Q4 2021 the renewals for premiums were up a staggering 34%. In Q4 2022 premiums continued to rise an additional 15%.
There are concerns that many customers will be priced out of the market and the insurance industry and left without a means of transferring risk. To the detriment of insurers, the companies may make their products so expensive that they undermine the tremendous market-growth opportunity. Additionally, upper limits for insurability and various exception clauses are being instituted, which diminish the overall value proposition for customers.
What is needed are better tools to predict cyber attacks and estimate losses. The current army of insurance actuaries has not delivered, but there is hope. It comes from the cyber risk community that looks to manage these ambiguous and chaotic risks by avoiding and minimizing losses.
These cybersecurity experts are motivated by optimizing limited resources to prevent or quickly undermine attacks. As part of that continuous exercise, there are opportunities to apply best practices to the insurance model to identify the most relevant aspects that include defensive postures (technology, behaviors, and processes) and understanding the relevant threat actors (targets, capabilities, and methods) to determine the residual risks.
The goal would be to develop a unified standard for qualifying for cyber insurance that would adapt to the rapid changes in the cyber landscape. More accurate methodologies will improve assessments to reduce insurers’ ambiguity so they may competitively price their offerings.
In the future, such calculations will be continuous and showcase how a company will benefit by properly managing security in alignment with shifting threats. This should bring down overall premium costs.
The next generation of cyber insurance will rise on the foundations of new risk analysis methodologies to be more accurate and sustain the mutual benefits offered by the insurance industry.
The Cyber Insurance Imperative, 2nd Edition: Updated for Today’s Challenging Risk Landscape
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 25 2023
Cloud Hosting Provider Lost all Customer Data Following Ransomware Attack
There has been a cyber attack on two cloud hosting providers, namely CloudNordic and Azero Cloud, which Certiqa Holding owns. The cyberattack has resulted in complete data loss for all their customers.
The cloud attack was reportedly on Friday, April 18, 2023, at around 4 AM when CloudNordic and Azero cloud were exposed to a ransomware attack in which the threat actors shut down all the systems, including customer systems, e-mail systems, customers’ websites, and everything they gained access to.
Both companies mentioned that they could not and didn’t want to pay the ransom demanded by the threat actors. However, the IT teams of CloudNordic and Azero Cloud are working with external experts to get complete information about the attack and possible recreation.
Unfortunately, the companies could not recover or recreate any customer data, and they have lost every piece of data on their customers, mail servers, web servers, etc.
CloudNordic and Azero Cloud are highly affected by this cyber attack, and they have lost largely critical customer data but have re-established communications.
This means they have now deployed blank systems, including name servers, web servers, and mail servers. However, none of them contain any previous data.
The company has sorted out a way to restore the DNS administration interface that can enable users to get email and the web working again.
As per the report submitted to Cyber Security News, both companies attempted to migrate between data centers and had some infected systems before the migration, which the company did not know.
Nevertheless, some servers used to manage all the servers were still wired to the previous network. Threat actors gained access to the administration systems with this network misconfiguration, which paved their way toward the backup systems (both primary and secondary backup).
The attackers encrypted all the systems they had access to, including all the virtual machines. Large amounts of data were reported to have been encrypted by the ransomware, but there seems to be no evidence of data being copied.
Both companies claimed there seemed to be no evidence of a data breach and regretted the inconvenience caused to their customers.
With the rise in cyberattacks and cybercriminals, every organization must implement multiple security measures and monitor every piece of traffic to prevent these kinds of cyberattacks.
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 24 2023
Google announced security enhancements to Google Workspace focused on enhancing threat defense controls with Google AI.
At a Google Cloud press event on Tuesday, the company announced Google Cloud’s rollout over the course of this year of new AI-powered data security tools bringing zero-trust features to Workspace, Drive, Gmail and data sovereignty. The enhancements to Google Drive, Gmail, the company’s security tools for IT and security center teams and more are designed to help global companies keep their data under lock and encrypted key and security operators outrun advancing threats.
Jump to:
The Executive Guide to Zero Trust: Drivers, Objectives, and Strategic Considerations
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 24 2023
The Internet of Things (IoT) is currently at its peak, with a rapid expansion of capabilities. This involves converting everyday items like light bulbs and plugs into smart devices controlled via smartphones. The number of IoT devices exceeded 13.8 billion in 2021, expected to quadruple by 2025, but this growth also introduces security risks exploited by cybercriminals. Researchers have discovered that even smart light bulbs, like the Tp-Link Tapo Smart Wi-Fi Multicolor Light Bulb, can be hacked to gather Wi-Fi credentials. They employed PETIoT, an IoT-focused Kill Chain, to assess vulnerabilities in these bulbs. This situation highlights challenges for cybersecurity experts dealing with the growing threats in the IoT landscape.
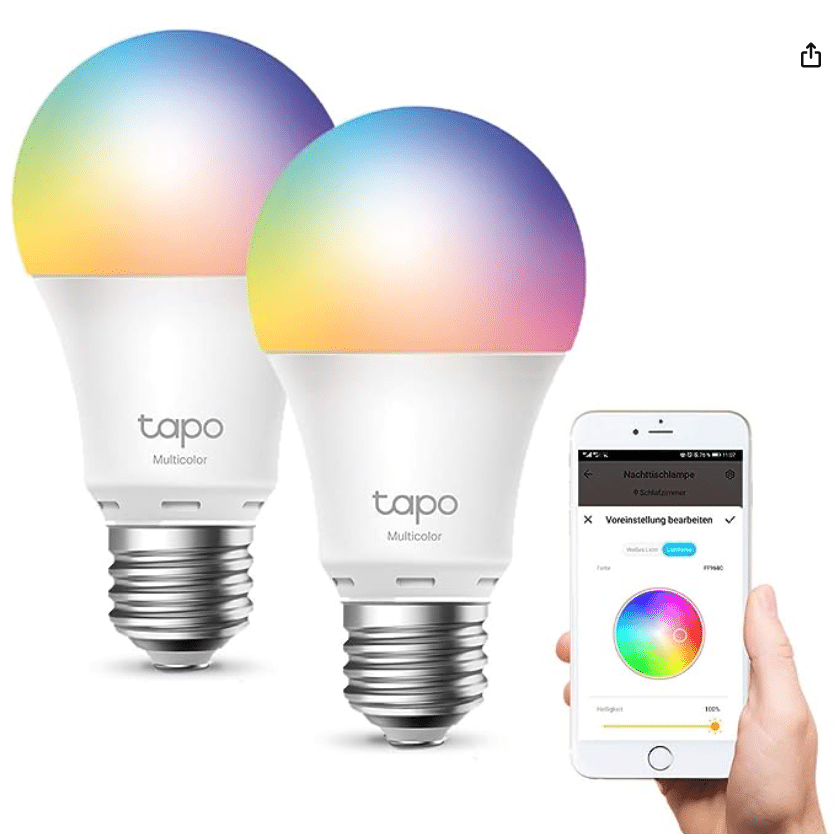
Because it is a cloud-enabled multicolor smart bulb, the Tapo L530E may be operated using the Tapo app on an Android or iOS device without the need for a hub. Instead, it connects directly to the home Wi-Fi network. According to the findings of the researchers, this particular kind of smart bulb is susceptible to each of the following four vulnerabilities:
The examination and testing carried out by the security experts indicate the proximity-based attacks that were carried out on the smart bulb that was the target.The attack scenario that causes the greatest concern is one in which an attacker impersonates a bulb and retrieves information about a Tapo user account by exploiting vulnerabilities.
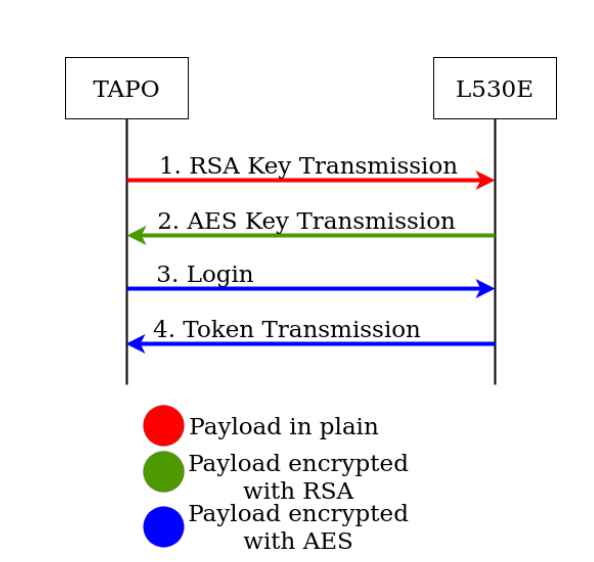
After that, the attacker may extract the victim’s WiFi SSID and password by using the Tapo app, allowing them to obtain access to any and all other devices that are connected to the victim’s network.
In order for the attack to be successful, the device in question must first be put into setup mode. However, the attacker has the ability to deauthenticate the bulb, which will need the user to re-configure it in order to get the light to work again.The researchers also investigated an MITM (Man-In-The-Middle) attack using a configured Tapo L530E device. This form of attack takes advantage of a vulnerability to intercept and control the connection between the app and the bulb, as well as to capture the RSA encryption keys that are used for further data transmission.
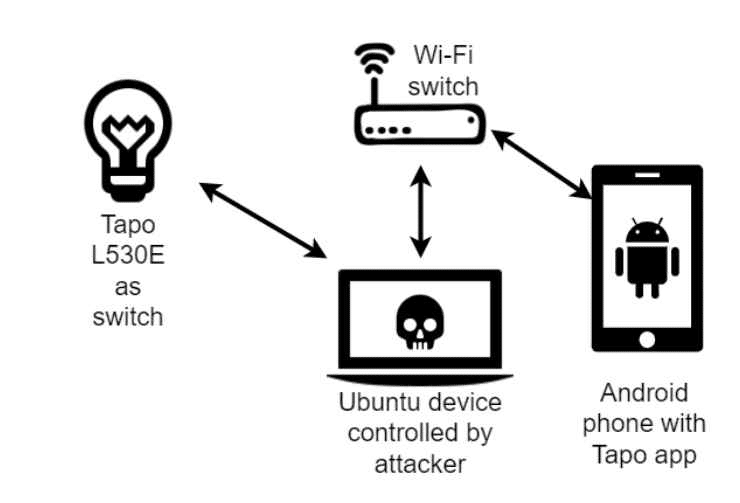
MITM attacks are also possible with unconfigured Tapo devices by leveraging a vulnerability once again by connecting to the WiFi during the setup process, bridging two networks, and routing discovery messages. This will eventually allow the attacker to retrieve Tapo passwords, SSIDs, and WiFi passwords in an easily decipherable base64 encoded form. Last but not least, a further flaw enables attackers to conduct what are known as “replay attacks.” These attacks involve recreating communications that have been sniffed in the past in order to bring about functional changes in the device.
In response, TP-Link gave the researchers their assurance that the issues that were found in their software as well as the firmware of the bulb will be fixed.
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 24 2023
The OWASP Amass project performs network mapping of attack surfaces and external asset discovery using open-source information gathering and active reconnaissance techniques.

Osmedeus is a workflow engine for offensive security that allows you to build and run a reconnaissance system on a wide range of targets, including domains, URLs, CIDRs, and GitHub repositories. It was designed to establish a strong foundation and can adapt and function automatically to perform reconnaissance tasks.
PhoneInfoga is an advanced tool to scan international phone numbers. It allows you to gather basic information such as country, area, carrier, and line type, then use various techniques to find the VoIP provider or identify the owner. It works with a collection of scanners that must be configured for the tool to be effective.
Sherlock allows you to search social media accounts by username across social networks.
Shodan is a search engine for Internet-connected devices. Discover how internet intelligence can help you make better decisions. The entire Shodan platform (crawling, IP lookups, searching, and data streaming) is available to developers. Use their API to understand whether users connect from a VPN, whether the website you’re visiting has been compromised, and more.
Social Analyzer is an API, CLI, and web app for analyzing and finding a person’s profile across social media and websites. It includes different analysis and detection modules; you can choose which modules to use during the investigation process. The analysis and public extracted information from this OSINT tool could help investigate profiles related to suspicious or malicious activities such as cyberbullying, cyber grooming, cyberstalking, and spreading misinformation.
SpiderFoot is an OSINT automation tool. It integrates with just about every data source available and utilizes a range of methods for data analysis, making that data easy to navigate. SpiderFoot has an embedded web-server for providing a clean and intuitive web-based interface but can also be used completely via the command-line.
theHarvester is a simple to use, yet powerful tool designed to be used during the reconnaissance stage of a red team assessment or penetration test. It performs OSINT gathering to help determine a domain’s external threat landscape. The tool gathers names, emails, IPs, subdomains, and URLs by using multiple public resources.
OSINT Tools: A Practical Guide to Collection, Analysis, and Visualization
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 22 2023
One of Mississippi’s largest hospital systems, Singing River Health System, suffered a cyberattack last week, leading to the shutdown of various internal services. The hospital system, which operates multiple hospitals and clinics along the Gulf Coast, detected unusual activity on its network and is cooperating with law enforcement. As a result of the attack, certain internal systems were taken offline to ensure their integrity during the investigation. The hospital’s IT security team is working to restore the offline systems, but the process is expected to take time. The hospital has not confirmed whether the attack involved ransomware or if a ransom will be paid. Patient services, including lab test results and radiology exams, are facing delays due to the attack. The incident highlights the ongoing challenges that hospitals face from cyberattacks, as this year has seen several healthcare institutions targeted by such attacks.
https://therecord.media/mississippi-hospital-system-takes-services-offline-after-cyberattack
InfoSec tools | InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory
Aug 20 2023
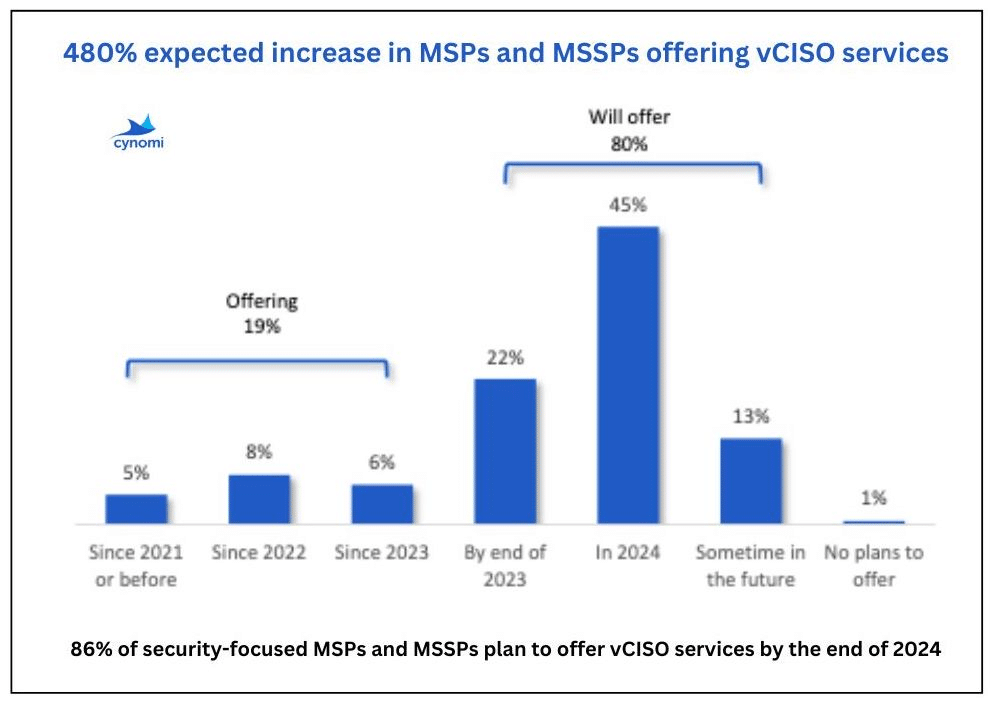
Cynomi Study Reveals Number of MSPs Providing Virtual CISO Services Will Grow Fivefold By Next Year
The frequency of cyberattacks is increasing, particularly targeting smaller businesses. However, most small and mid-size companies cannot afford a full-time security professional. To address this, they are turning to vCISO (virtual Chief Information Security Officer) services offered by Managed Service Providers (MSPs) and Managed Security Service Providers (MSSPs). These services provide access to external cybersecurity experts at a lower cost than hiring an in-house CISO.
A report by Cynomi, based on a survey of 200 executives in the U.S. and Canada, shows the rising demand for vCISO services among SMBs and how MSPs and MSSPs are responding to this demand. The report reveals that 84% of those not currently offering vCISO services but plan to do so by the end of 2024. The number of providers offering these services has been consistently growing, with 8% in 2022, 28% in 2023, and a projected 45% in 2024.
MSPs and MSSPs are motivated to offer vCISO services due to anticipated increased revenue, higher margins, easy upselling of other cybersecurity services, and enhanced client engagement. Although they foresee challenges such as limited in-house security knowledge and a lack of skilled cybersecurity personnel, vCISO platforms help mitigate these concerns.
Cynomi, a leading vCISO platform provider, aims to conduct annual studies on the growing trend of the vCISO role. They have also created a directory of prominent vCISO service providers to help SMBs find trusted security partners, offering details about services and technology platforms used by each provider.
DISC InfoSec Previous posts on vCISO
InfoSec tools | InfoSec services | InfoSec books | Follow our blog
Aug 03 2023
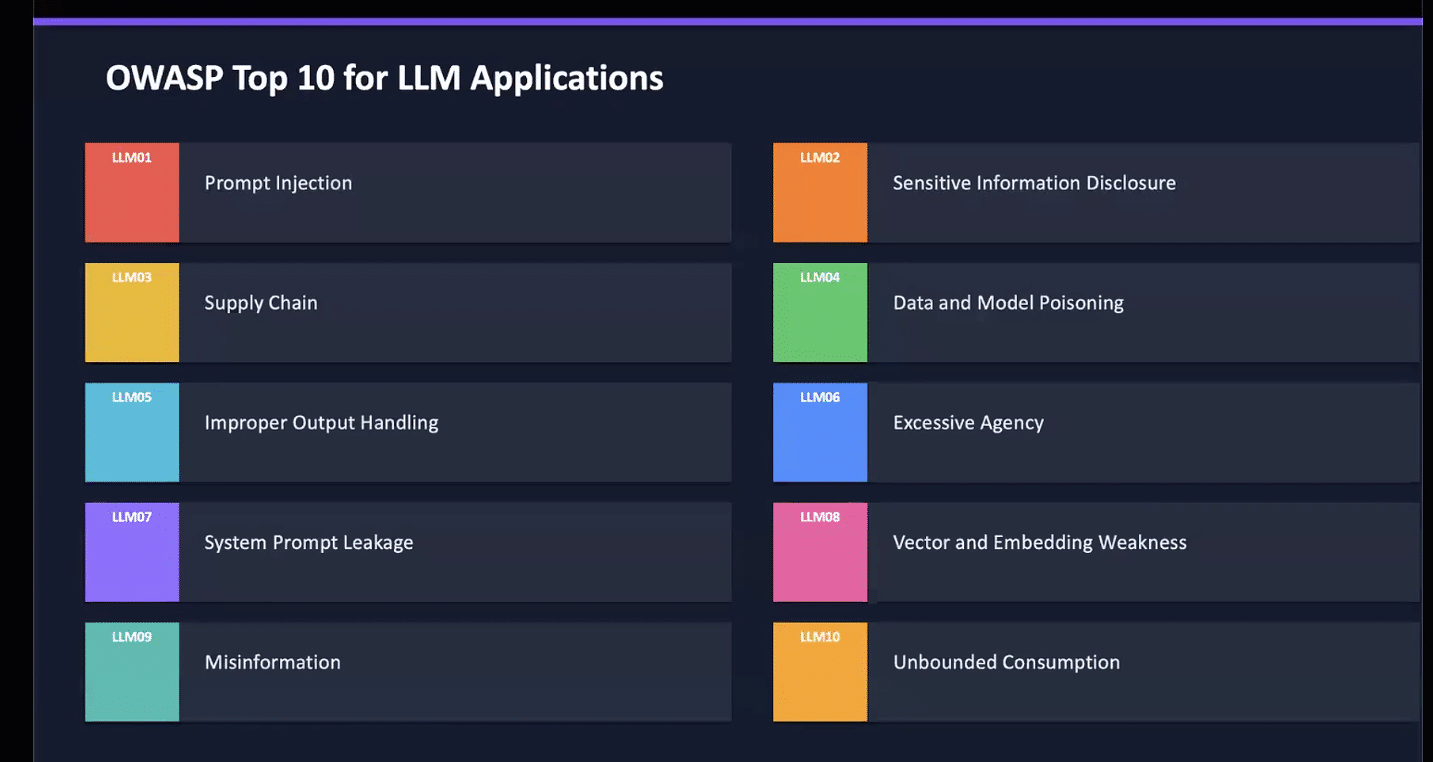
OWASP released the OWASP Top 10 for LLM (Large Language Model) Applications project, which provides a list of the top 10 most critical vulnerabilities impacting LLM applications.
The project aims to educate developers, designers, architects, managers, and organizations about the security issues when deploying Large Language Models (LLMs).
The organization is committed to raising awareness of the vulnerabilities and providing recommendations for hardening LLM applications.
“The OWASP Top 10 for LLM Applications Working Group is dedicated to developing a Top 10 list of vulnerabilities specifically applicable to applications leveraging Large Language Models (LLMs).” reads the announcement of the Working Group. “This initiative aligns with the broader goals of the OWASP Foundation to foster a more secure cyberspace and is in line with the overarching intention behind all OWASP Top 10 lists.”
The organization states that the primary audience for its Top 10 is developers and security experts who design and implement LLM applications. However the project could be interest to other stakeholders in the LLM ecosystem, including scholars, legal professionals, compliance officers, and end users.
“The goal of this Working Group is to provide a foundation for developers to create applications that include LLMs, ensuring these can be used securely and safely by a wide range of entities, from individuals and companies to governments and other organizations.” continues the announcement.
The Top Ten is the result of the work of nearly 500 security specialists, AI researchers, developers, industry leaders, and academics. Over 130 of these experts actively contributed to this guide.
Clearly the project is a work in progress, LLM technology continues to evolve, and the research on security risk will need to keep pace.
Below is the Owasp Top 10 for LLM version 1.0
LLM01: Prompt Injection
This manipulates a large language model (LLM) through crafty inputs, causing unintended actions by the LLM. Direct injections overwrite system prompts, while indirect ones manipulate inputs from external sources.
LLM02: Insecure Output Handling
This vulnerability occurs when an LLM output is accepted without scrutiny, exposing backend systems. Misuse may lead to severe consequences like XSS, CSRF, SSRF, privilege escalation, or remote code execution.
LLM03: Training Data Poisoning
This occurs when LLM training data is tampered, introducing vulnerabilities or biases that compromise security, effectiveness, or ethical behavior. Sources include Common Crawl, WebText, OpenWebText, & books.
LLM04: Model Denial of Service
Attackers cause resource-heavy operations on LLMs, leading to service degradation or high costs. The vulnerability is magnified due to the resource-intensive nature of LLMs and unpredictability of user inputs.
LLM05: Supply Chain Vulnerabilities
LLM application lifecycle can be compromised by vulnerable components or services, leading to security attacks. Using third-party datasets, pre-trained models, and plugins can add vulnerabilities.
LLM06: Sensitive Information Disclosure
LLM’s may inadvertently reveal confidential data in its responses, leading to unauthorized data access, privacy violations, and security breaches. It’s crucial to implement data sanitization and strict user policies to mitigate this.
LLM07: Insecure Plugin Design
LLM plugins can have insecure inputs and insufficient access control. This lack of application control makes them easier to exploit and can result in consequences like remote code execution.
LLM08: Excessive Agency
LLM-based systems may undertake actions leading to unintended consequences. The issue arises from excessive functionality, permissions, or autonomy granted to the LLM-based systems.
LLM09: Overreliance
Systems or people overly depending on LLMs without oversight may face misinformation, miscommunication, legal issues, and security vulnerabilities due to incorrect or inappropriate content generated by LLMs.
LLM10: Model Theft
This involves unauthorized access, copying, or exfiltration of proprietary LLM models. The impact includes economic losses, compromised competitive advantage, and potential access to sensitive information.
The organization invites experts to join it and provide support to the project.
You can currently download version 1.0 in two formats. The full PDF and the abridged slide format.
Web Application Security: Exploitation and Countermeasures for Modern Web Applications
InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory | ISO 27k Chat bot | Comprehensive vCISO Services | ISMS Services | AIMS Services | Security Risk Assessment Services | Mergers and Acquisition Security
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
InfoSec tools | InfoSec services | InfoSec books
Aug 02 2023
How CISOs can succeed in a challenging landscape Reimagining operational resilience and recovery in 2023
#CISOs face mounting demands to develop information security strategies that effectively safeguard their organizations against an ever-evolving threat landscape. A strong information security stance is imperative, but the requirements for security and risk management are intricate and distinct for each organization. The alignment of business priorities and suitable solutions may not always be apparent, while swift results and cost-effective measures are crucial.
In what situations would a vCISO or CISOaaS Service be appropriate?
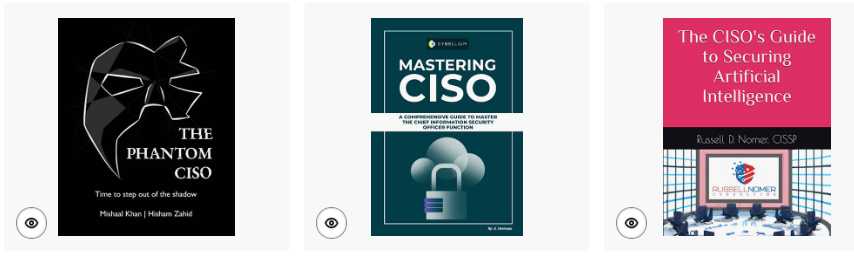
CISO Conversations: The Role of the vCISO
InfoSec tools | InfoSec services | InfoSec books
Aug 02 2023
A CISO needs to wear many hats across the business and juggle many competing priorities. They need to be a customer support representative, a product partner, a manager, a visionary, a strategist, and of course, a security expert.
I have found that some of the most important characteristics are to be friendly, honest, and emphatic. Being a friend to the organization and people you work with, rather than leading with just policies and demands, is critical to getting more done and the success of your team.
It may sound counterintuitive, but a good CISO must get out from behind the technology and understand the people they are serving. Of course, you must maintain a high level of technology knowledge, but if you find yourself only sitting in front of a firewall console, you’re probably in the wrong job.
With the more-rapidly-than-ever changing environment, you can rarely rely solely on multi-year strategies or multi-quarter roadmaps. You must be ready for constant change and quickly adapt to it.
CISOs must create a security strategy built around anticipating outcomes and a feedback loop to gather information during incidents, assessments, threat analysis, and research. The information gathered should then be turned into metrics which will give insights into if the strategy is working, and, if necessary, how to evolve the strategy.
Though CISOs play a lead role in managing an organization’s security posture, it is important that cybersecurity efforts manifest as a shared responsibility across an organization. From new hires to the C-suite, cybersecurity should be a communicated priority for all employees. Everyone should care about security, and if they don’t do it, it’s because they don’t understand something about the situation or ask.
Just as much as a CISO needs to learn about the business, they must also educate other business leaders on what’s out there and the landscape of evolving threats. Then, it’s important to connect these threats and the solutions back to the goals of that part of the business so teams can fully understand the role they can play in mitigating risk.
It’s important to prioritize security and proactively communicate initiatives with stakeholders. However, building and maintaining trust isn’t a one-size-fits-all approach. CISOs must possess the ability to effectively communicate and educate all stakeholders about the specific cyber risks relevant to their organization while also proactively outlining how it is prepared to address those risks. Implementing robust, proactive security measures and emphasizing the protection of sensitive data will reassure customers, stakeholders, and employees alike that their information is secure. Swiftly acting on emerging and existing security threats also reinforces trust and demonstrates an organization’s proactive efforts in addressing threats before they become detrimental.
There are three ways I manage competing priorities: Focus, transparency, and accountability. A CISO must focus on the tasks that have the biggest ROIs, and not get distracted by the noise. Leading with transparency will make it clear to everyone within the organization why we are making changes or asks. And finally, security posture and response can only be improved when accountability is clear. And not just accountability of the security team, but accountability from across the organization where everyone understands the responsibility.
By making data-driven decisions and conducting continuous risk assessments, CISOs can strategically allocate resources to high-priority tasks. The delicate balance lies in leading these various aspects while leveraging the expertise of a skilled team to ensure comprehensive security protection across the organization. By staffing a knowledgeable team of security experts and empowering them to take ownership of their day-to-day responsibilities, CISOs can focus their time on providing strategic and executive-level oversight on key issues.
From a leadership standpoint, the CISO is so much more than just security. It’s truly a business leader position, they are collaborating with the other business leaders to share the same resources. CISOs must understand the organizational goals, the customer needs, and the capacity of each team to prioritize security in collaboration with product management, IT leaders, CTO, etc.
CISOs must maintain fundamental technology knowledge but rely on the team’s subject matter expertise for deeper technical aspects. It’s important to find the right training, like CISSP, and vendor-specific certifications, without overwhelming yourself.
In what situations would a vCISO or CISOaaS Service be appropriate?
CISO Conversations: The Role of the vCISO
InfoSec tools | InfoSec services | InfoSec books
Jul 31 2023
Superstar CISOs stand out from the rest due to their acute understanding of the growing threat landscape and the shortage of cybersecurity skills. However, they refuse to succumb to despair and instead leverage their existing assets effectively, notably by recognizing an overlooked security resource: their development teams.
In the era of DevSecOps hype, it’s common to say that security is everyone’s responsibility. But there are limits to what untrained and unmotivated workers – especially those who don’t work in IT – can do to make their organization more secure against cyberthreats.
For example, in the real world, travelers at a busy airport should feel responsible for reporting an unattended bag sitting alone in a suspicious location. However, they aren’t trained to inspect that bag to look for threats or empowered to take any actions on their own. At a company, it’s one thing to make everyone aware of cybersecurity, and another to educate them to make their organization more secure within the context of their role or to use the defensive tools they already have in place to counter threats and squash vulnerabilities.
For that, companies need to invest in upskilling. It’s far better, and oftentimes easier, to invest in the talented, loyal staff that are already a part of your organization than to try and hire new people from the outside. But even then, putting those learning resources in the best place to get the required results is key.
Developers already understand IT since they write much of the code for the programs being used by their organizations. And they are often ready, willing, and able to upskill in cybersecurity to help make them even more amazing at their jobs. Smart CISOs are tapping into that enthusiasm and providing developers with the education pathways they want and need, with the payoff being a reduction in common vulnerabilities (not to mention less pressure on overworked AppSec personnel).
The best CISOs know that upskilling is critical to success. But not just any training will do, especially for the development community who already have a good baseline understanding of IT. A “check-the-box” program won’t offer much return on investment and will likely frustrate developers into poor performance and a lifelong hatred of working with security teams.
Likewise, any solution that impedes their workflow, fails to stay agile with enterprise security goals, or cannot deliver the right education at the right time in an easily digestible format, is unlikely to result in foundational security awareness or skills.
Exemplary CISOs are also able to address other key pain points that traditionally flummox good cybersecurity programs, such as the relationships between developers and application security (AppSec) teams, or how cybersecurity is viewed by other C-suite executives and the board of directors.
For AppSec relations, good CISOs realize that developer enablement helps to shift security farther to the so-called left and closer to a piece of software’s origins. Fixing flaws before applications are dropped into production environments is important, and much better than the old way of building code first and running it past the AppSec team at the last minute to avoid those annoying hotfixes and delays to delivery. But it can’t solve all of AppSec’s problems alone. Some vulnerabilities may not show up until applications get into production, so relying on shifting left in isolation to catch all vulnerabilities is impractical and costly.
There also needs to be continuous testing and monitoring in the production environment, and yes, sometimes apps will need to be sent back to developers even after they have been deployed. A great CISO, with a foot in development and security, can smooth out those relations and keep everyone working as a team.
Getting other C-suite executives onboard with better security might be an even more difficult challenge, with leadership outside the CISO and CIO normally looking at business objectives and profits before anything else. To counter that, superstar CISOs know how to show a direct correlation between better, more mature cybersecurity and increased revenue, and how it can even provide a competitive advantage against the competition.
It’s not easy being a CISO, and certainly more challenging than at any other point in history. But those CISOs who master that adversity are becoming true superstars within their companies and communities. They competently employ agile developer upskilling, champion security culture, streamline relationships between the traditional rivals of development and AppSec teams, and encourage leadership to foster a security-first approach from the top down.
In what situations would a vCISO or CISOaaS Service be appropriate?
CISO Conversations: The Role of the vCISO
InfoSec tools | InfoSec services | InfoSec books
Jul 30 2023
The cybersecurity talent issue is a significant challenge faced by organizations worldwide. Solving this problem requires a combination of short-term and long-term strategies to attract, develop, and retain skilled cybersecurity professionals. Here are some steps that can help address the cybersecurity talent shortage:
By combining these strategies and adopting a long-term perspective, organizations can start making progress in solving the cybersecurity talent issue. Remember that cybersecurity is an ever-evolving field, and continuous efforts are needed to attract and retain skilled professionals.
Cybersecurity and information resilience – BSI Group
How Does Social Media Affect Teenagers, and Is It Positive?
InfoSec books | InfoSec tools | InfoSec services
InfoSec services | InfoSec books | Follow our blog | DISC llc is listed on The vCISO Directory | ISO 27k Chat bot | Comprehensive vCISO Services | ISMS Services | AIMS Services | Security Risk Assessment Services | Mergers and Acquisition Security
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
May 27 2023
The presence of each third-party application increases the potential for attacks, particularly when end users install them without proper oversight or approval. IT security teams face challenges in obtaining comprehensive knowledge about the apps connected to their corporate SaaS platforms, including their permissions and activities.
In this Help Net Security video, Matt Radolec, Senior Director, Incident Response and Cloud Operations at Varonis, offers advice for CISO-level executives to enhance the security of corporate cloud data.
In what situations would a vCISO Service be appropriate?
Previous DISC InfoSec posts on CISO
InfoSec tools | InfoSec services | InfoSec books