InfoSec Compliance & AI Governance For over 20 years, DISC InfoSec has been a trusted voice for cybersecurity professionals—sharing practical insights, compliance strategies, and AI governance guidance to help you stay informed, connected, and secure in a rapidly evolving landscape.
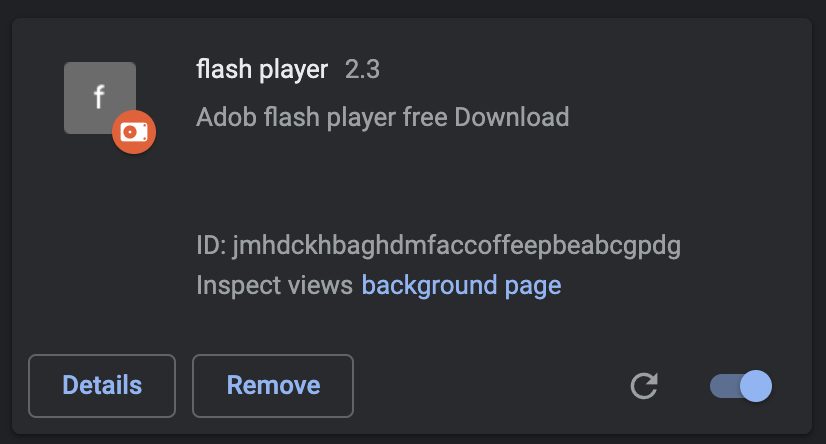
Researchers at Zimperium zLabs recently identified a new Chrome browser botnet called ‘Cloud9’ that is intent on stealing the following information using malicious extensions:-
This method is becoming increasingly attractive for malware developers to target web browsers as they contain the most valuable information about a user.
In the course of everyday activities, we can find out a lot about ourselves through our keystrokes or session cookies. A breach of security or a violation of privacy can be caused by having access to such information.
Cloud9 botnet is a RAT that affects all Chromium-based web browsers, which are popular among consumers like Chrome and Microsoft Edge. Moreover, threat actors could exploit this RAT to remotely execute arbitrary commands.
Technical Analysis
The official Chrome web store doesn’t host this malicious Chrome extension, so it cannot be downloaded from there.
The distribution channel of this malware relies on communities that are operated by threat actors, wherein the malware will be hidden by users of the tool before it gets delivered to the victims by the tool itself.
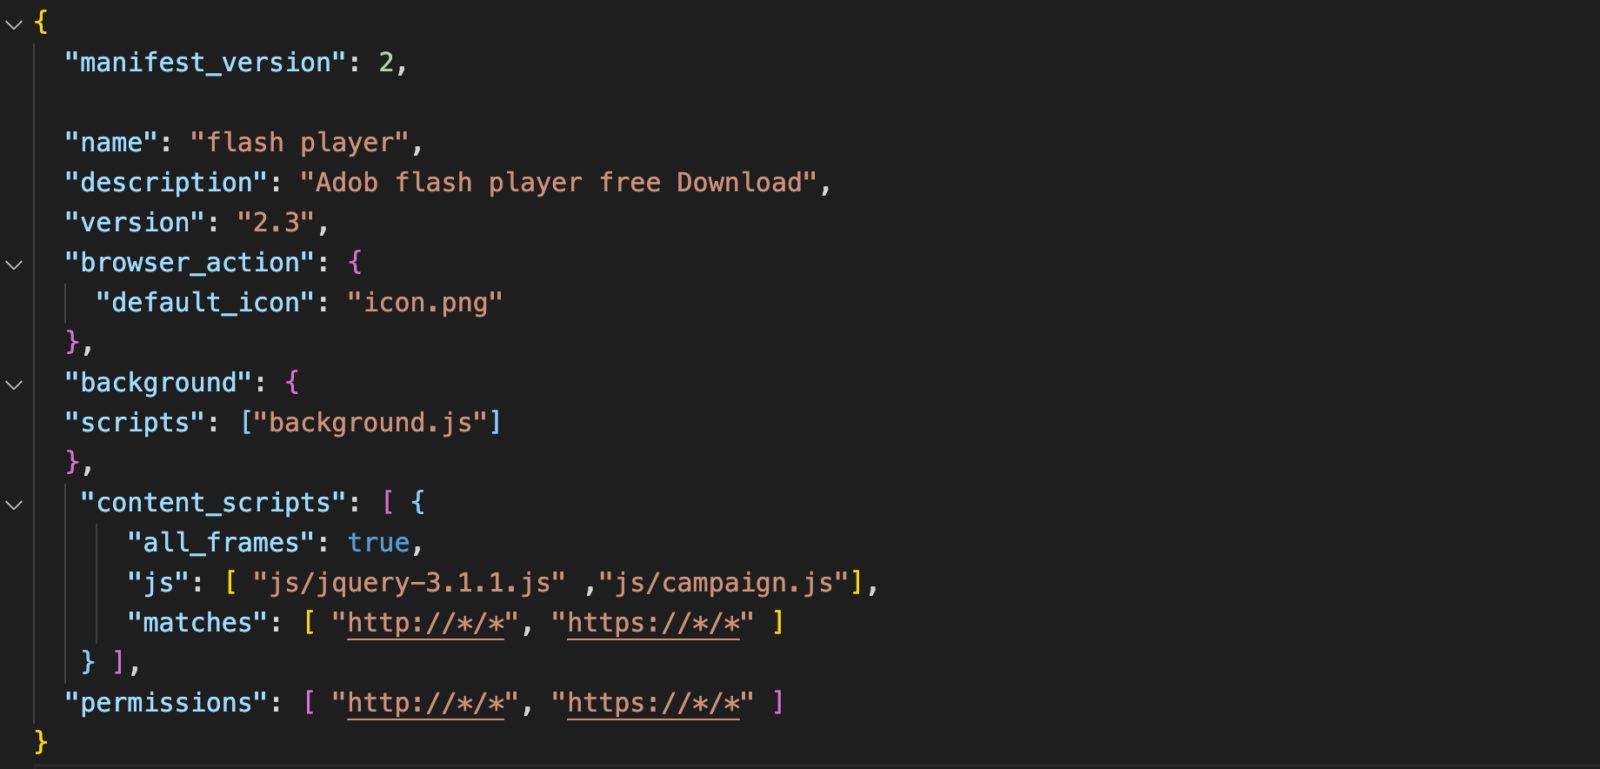
In terms of the Javascript files that make up the extension, there are only three. While the primary functionality of the extension can be located in a file called “campaign.js” which contains most of its functionality.
According to the report, During the initialization of campaign.js, the window.navigator API is used to identify the system’s operating system. Once the target has been identified, a Javascript file is injected into the victim’s computer system as a method to mine cryptocurrency using the resources of the victim’s computer system.
Next, for further proceedings, it injects another script known as cthulhu.js which comprises a full-chain exploit for the following flaws:-
CVE-2019-11708 (Firefox)
CVE-2019-9810 (Firefox)
CVE-2014-6332 (Internet Explorer)
CVE-2016-0189 (Internet Explorer)
CVE-2016-7200 (Edge)
As soon as the vulnerabilities are exploited, Windows malware is automatically installed on the host machine and executed. This gives attackers even more opportunities to compromise systems and carry out even more severe malware attacks.
While one of the sophisticated inclusion of this malware is “Clipper,” a module that keeps scanning the clipboard of the system for copied data like:-
Passwords
Credit cards details
In addition to injecting ads into webpages silently, Cloud9 is also capable of generating revenue for its operators by generating ad impressions.
nformation Security Risks assisted Business models for banking & financial services(BFS) institutions have evolved from being a monolithic banking entity to multi-tiered service entity.
What this means to BFS companies is that they need to be more updated and relevant with regards to technology & the quality of all services provided to their clients. The most opted methodology to do that today is by means of outsourcing services to vendors & 3rd parties.
Though outsourcing is cost beneficial to companies, this approach comes with its own set of drawbacks. It is judicious to say that every outsourcing enterprise should be aware of the risks that vendors bring to the table.
Though vendors bring in a lot of operational Information Security Risks depending on the business engagement, a methodology to manage only the 3rd party Information Security Risks are discussed here.
Just to provide a sense of the impact that vendor Information Security Risks brings to organizations, below are some of the facts from surveys conducted by Big 4 consulting companies like PwC & Deloitte.
“The Number of data breaches attributed to 3rd party vendors has increased by 22% since 2015”- Source PwC
According to Deloitte “94.3% of executives have low to moderate confidence in their third-party risks management tools & technology, and 88.6% have low to moderate confidence in the quality of the underlying Information Security Risks management process” .
We know the problem now, how do you begin resolving it??
A perfect place to begin is with the sourcing team and /or procurement team depending on how your organization is set up. In an ideal world, these teams are expected to have an inventory of all vendors, 3rd parties & Partners of your organization.
Once we have this inventory in place, the IT vendor risk management (IT- VRM) team needs to segregate the IT vendors from the non-IT ones. This is a onetime activity. For future needs, it is recommended to have the sourcing team segregate vendors basis on their business engagement (IT vs Non-IT).
Understanding your Vendors & the Information Security Risks they carry:
One of the simplest & efficient way to understand your vendors is by having a scoping checklist, that details the vendor business with your organization, kind of data touchpoints & exchanges, kind of Information Security Risks that your organization is exposed by this outsourced business.
This information is usually available with the vendor manager representing your organization in the vendor relationships.
Below is the list of Information Security Risks pointers (not limited to) that you might want to consider asking your vendor manager.
Regulatory risk – Does this relationship affect your regulatory posture? What is the penalty associated with such regulatory non-compliance?
Reputational risk– Does this service impact your clients & the reputation you hold with them?
Financial risk– Any financial Information Security Risks associated with business engagement?
Information security risks – what data are shared as part of the business engagement with the vendor? how secure is the vendor with regards to protecting your organization data?
Resiliency risks – Does the vendor introduce any single point of failures to your business practices?
For understanding the level of assessment to be performed with the vendor, you will need to understand the vendor’s business operating model.
Below is an indicative list of themes that you might want to discuss with vendor manager to understand the scope of the vendor assessment.
Data attributes shared & received with the vendor, volume of data & frequency
Mode of communication/interfaces with a vendor – Mail, remote connection to vendor network, the remote connection from vendor to your internal network, data upload only, data download only, vendors are brought on-site & connect from your offices to provide services
Services provided – Data center services, Application provider, Cloud service provider, Data processing services, & many others.
Well-known cybersecurity researcher Fabian Bräunlein has featured not once but twice before on Naked Security for his work in researching the pros and cons of Apple’s AirTag products.
In 2021, he dug into the protocol devised by Apple for keeping tags on tags and found that the cryprography was good, making it hard for anyone to keep tabs on you via an AirTag that you owned.
Even though the system relies on other people calling home with the current location of AirTags in their vicinity, neither they nor Apple can tell whose AirTag they’ve reported on.
But Bräunlein figured out a way that you could, in theory at least, use this anonymous calling home feature as a sort-of free, very low-bandwidth, community-assisted data reporting service, using public keys for data signalling:
He also looked at AirTags from the opposite direction, namely how likely it is that you’d spot an AirTag that someone had deliberately hidden in your belongings, say in your rucksack, so that they could track you under cover of tracking themselves:
Indeed, the issue of “AirTag stalking” hit the news in June 2022 when an Indiana woman was arrested for running over and killing a man in whose car she later admitted to planting an AirTag in order to keep track of his comings and goings.
In that tragic case, which took place outside a bar, she could probably have guessed were he was anyway, but law enforcement staff were nevertheless obliged to bring the AirTag into their investigations.
When security scans reveal more than they should
Now, Bräunlein is back with another worthwhile warning, this time about the danger of cloud-based security lookup services that give you a free (or paid) opinion about cybersecurity data you may have collected.
Many Naked Security readers will be familiar with services such as Google’s Virus Total, where you can upload suspicious files to see what static virus scanning tools (including Sophos, as it happens) make of it.
Sadly, lots of people use Virus Total to gauge how good a security product might be at blocking a threat in real life when its primary purpose is to disambiguate threat naming, to provide a simple and reliable way for people to share suspicious files, and to assist with prompt and secure sample sharing across the industry. (You only have to upload the file once.)
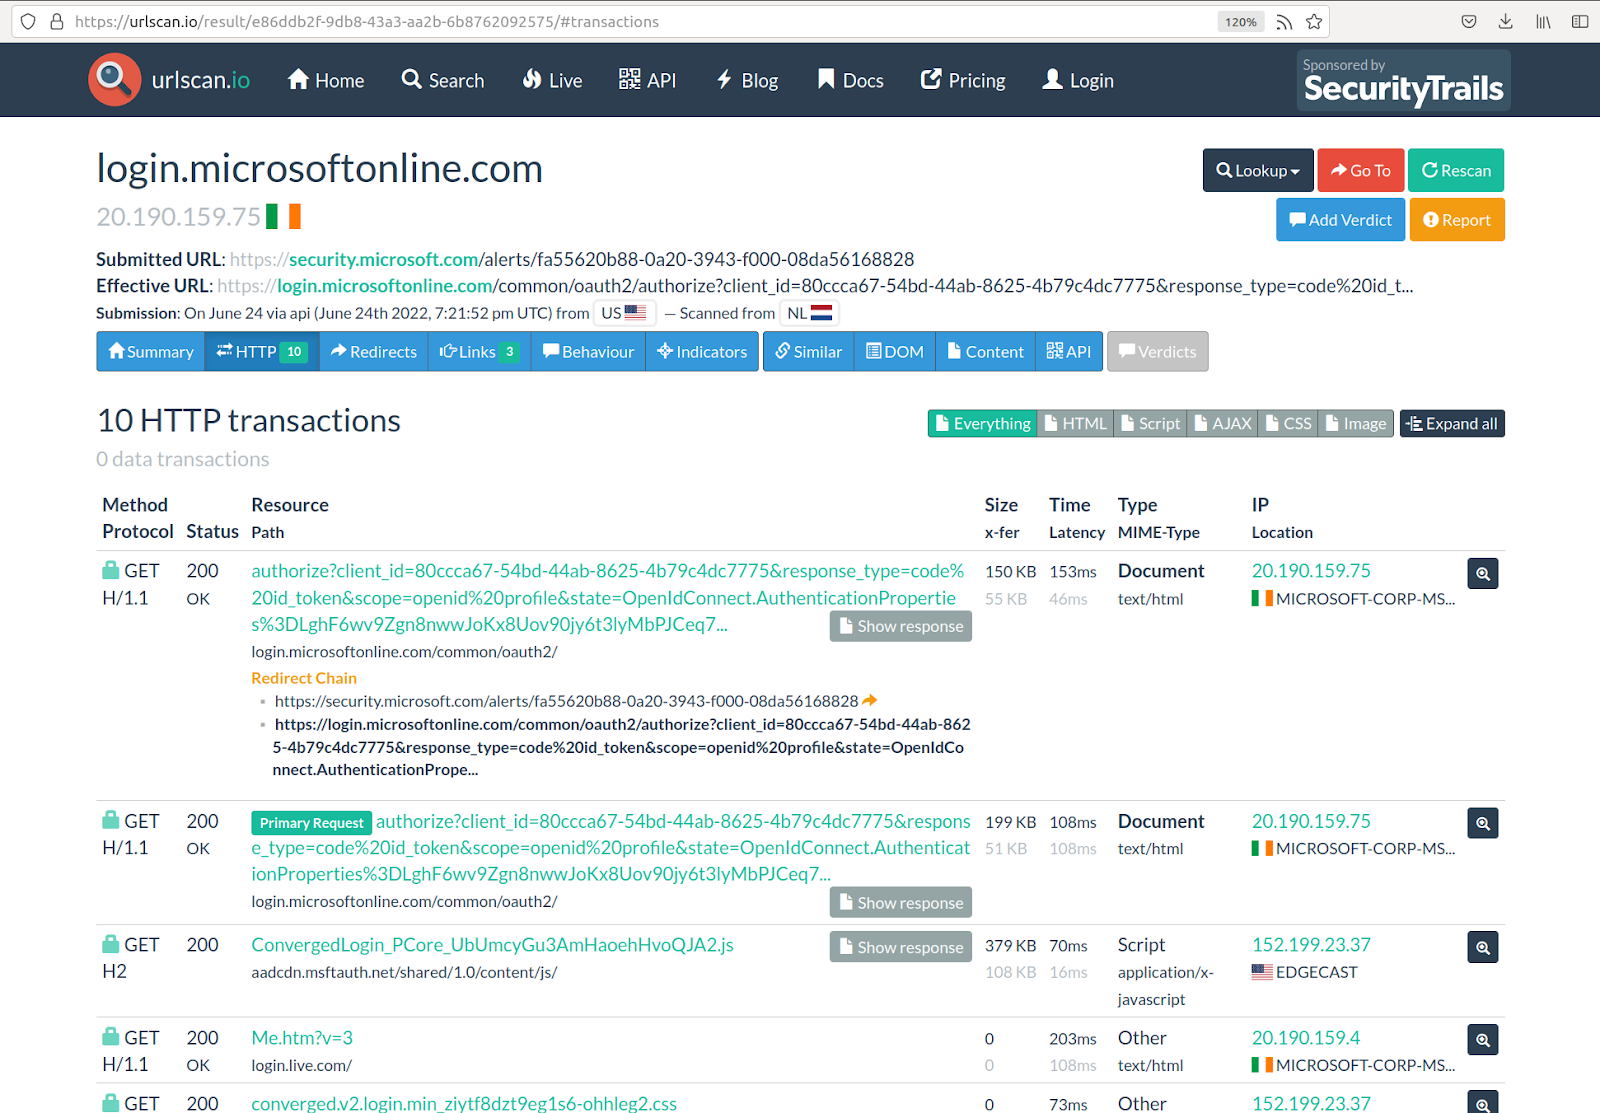
This new report by Bräunlein looks at a similar sort of public service, this time urlscan.io, which aims to provide a public query-and-reporting tool for suspicious URLs.
The idea is simple… anyone who’s worried about a URL they just received, for example in what they think is a phishing email, can submit the domain name or URL, either manually via the website, or automatically via a web-based interface, and get back a bunch of data about it.
Like this, checking to see what the site (and the community at large) think of the URL http://example.com/whatalotoftextthisis:
You can probably see where Fabian Bräunlein went with this if you realise that you, or indeed anyone else with the time to keep an eye on things, may be able to retrieve the URL you just looked up.
Recently, the Forgepoint team announced a new alliance with global banking leader Santander to increase cyber investment worldwide, specifically in Europe, Israel, and Latin America. Santander will also be the primary investor in Forgepoint’s next fund, slated for 2023, with a nearly $300 million goal.
This was the perfect reason to connect with Alberto Yépez, the co-founder and Managing Director of Forgepoint Capital. In this Help Net Security interview, the former Trident Capital leader offers insight into innovation in the cybersecurity market, M&A activity, pitching to VCs, and more.
When you look at today’s cybersecurity industry landscape, what drives innovation?
Innovation is always driven by a need. What does the market need right now? What do customers need? How can the ecosystem adapt to serve those needs? Innovation provides solutions that expedite answers to problems, and successful businesses are built when they do this.
Today’s rapidly changing macro environment combined with the demands of an evolving threat landscape makes this the perfect time for company building. Now, businesses that did not satisfy needs will no longer survive, while those that do will thrive.
The cybersecurity market is prone to mergers and acquisitions. How will this impact the future of the market?
While we may see a wave of consolidation, which is expected given the amount of venture financing committed to cybersecurity in the last few years, organizations now face the decision to either raise more funding in a challenging environment as valuations normalize or seek an acquisition, as growth investors shift away due to market conditions.
Public and larger private companies will continue to buy startups that are innovative and leading-edge, filling gaps in their current offerings to offer wider, more integrated solutions. These companies provide new capabilities that address new threats and give them access to high-growth market segments while helping them stay relevant.
Ultimately, M&A activity will have a positive impact on the industry because large enterprise customers benefit from integrated solutions that reduce the total cost of ownership of these solutions. Customers also benefit from these integrated services as they help meet critical enterprise needs and ease the strain caused by the global shortage of cybersecurity professionals.
Company founders spend a lot of time preparing their pitch, but it can take a long time to get VC, even with massively successful products. What advice would you give to those getting ready to talk to VCs?
I advise founders to take a long-term mindset and remember that fundraising is a people-driven industry. While initial timelines may achieve certain funding goals, securing funding means building real relationships and creating a network of trusted partners. Taking the time to do this well will have an immediate impact upon your success.
In a competitive fundraising environment, VCs have to make quick decisions. To do that, we depend on both our own experience, as well as the experiences of our network and our close connections who we can rely on to provide strong counsel. An introduction to a startup from a trusted friend with relevant expertise and background is one of the most productive relationship builders – for both sides.
These trusted relationships will open the right doors for founders, then it’s all about how you tell your story to the VC. The clarity and direction of your thinking can tell a lot about the company’s market position and opportunity you’re out to tackle, as well as your future priorities. Here, introspection and self-awareness shine.
Having a people-driven mindset is helpful because it has multiple natural side benefits. Networking requires us to build relationships with individuals beyond the short-term, casting a net that can include VCs as well as future startup customers or potential hires. Networking with VCs may also suggest you meet with others and while these introductions may not be directly about fundraising, they can help you get exposure to potential customers, team members, and advisors for input on your tech, business, and model. This leads to opportunities to learn and refine your approach from diverse perspectives.
What do you value most in an entrepreneur you want to invest in?
The traits that I find most important in entrepreneurs are subject matter expertise and the know-how to execute. Prior experience as an entrepreneur with a track record of building commercial offerings successfully commercialized and adopted by customers will allow for deep domain knowledge of the sector that they’re working in, which is very important when scaling organizations. In my experience, serial entrepreneurs typically have a leg up compared to first-timers.
That being said, all of this doesn’t matter if an entrepreneur doesn’t know how to lead. The ability to recruit and retain high quality talent, and then continuing to work with them to grow as the organization expands is a very important trait that is paramount to the success of any organization.
What advice would you give to European and Israeli companies trying to get funding in the US?
Forgepoint partners with emerging companies from Croatia to Mexico, Madrid to Tel Aviv, and has been actively tracking thousands of companies worldwide. It is abundantly clear that the cyber ecosystems across Europe, Latin America and Israel have an incredibly rich talent pool, strong demand signal and robust capital accessibility – and that cybersecurity is a growing, global problem.
While the current macro environment is challenging, organizations looking to get funding in the US will succeed if their product and complete offering solve a demonstrated need in the market. When it comes down to it, it’s all about five fundamentals:
Large market opportunity
Differentiated offerings that are hard to replicate
Sound go-to-market strategy
Ensuring the right team is in place
Product market fit as demonstrated by early customer traction
Israeli and European companies trying to get funding in the US should be able to clearly speak to these fundamentals, demonstrating how they’ll incorporate the US into their go-to-market and growth plans as they partner with investors, form channel alliances, and further develop their businesses. Thinking this through can be enormously helpful in identifying which VCs to approach – which will bring value and help augment your business.
Researchers from Positive Security uncovered a website scanner called “Urlscan” that unintentionally leaking sensitive URLs and data due to misconfiguration.
It appears that a third party accidentally leaked the GitHub Pages URLs, and this incident happened while a metadata analysis was being conducted.
“This information could be used by spammers to collect email addresses and other personal information,” Bräunlein, Co Founder Positive security said. “It could be used by cyber criminals to take over accounts and run believable phishing campaigns.”
The URLscan.io service is described as a sandbox for the web and has been referred to as a web scanner. Several security solutions integrate with its API in order to make their solutions more secure and feature-rich.
The idea behind it is to allow users to identify possible malicious websites with ease and confidence using a simple, straightforward tool. A wide range of open-source projects and enterprise customers are supported by the engine.
Sensitive data can be mined
It was discovered that users who enabled Github Pages as a hosting method for a private repository leaked the name of the repository. There does not seem to have been any public official acknowledgment of this breach as of yet.
There is a possibility that an anonymous user could easily search for and retrieve a vast amount and variety of sensitive data within the API integration.
This is because the API is equipped with several varieties of security tools that run scans on incoming emails and conduct Urlscans on every link that is received.
Several types of information are provided with each scan result that is returned by the service, including:-
Password reset links
Unsubscribe links
Account creation URLs
API keys
Information about Telegram bots
DocuSign signing requests
Amazon gift delivery links
Shared Google Drive links
Dropbox file transfers
Invite links to SharePoint
Invite links to Discord
Government Zoom invites
PayPal invoices
Paypal money claim requests
Links to Cisco Webex meeting recordings
Package tracking links
It has been noted that some API integrations use generic Python requests that use the python-requests/2.X.Y module. This would lead to scans being mistakenly submitted as public if user agents ignored account visibility settings.
Some of the biggest barriers to cloud adoption are security concerns: data loss or leakage, and the associated legal and regulatory concerns with storing and processing data off-premises.
In the last 18 months, 79% of companies have experienced at least one cloud data breach; even more alarmingly, 43% have reported 10 or more breaches in that time. Despite the clear advantages of cloud infrastructure, one of the main challenges that often gets overlooked is the need to: (1) trust that the infrastructure will be secure enough against threats and (2) that the chosen cloud provider won’t purposefully or inadvertently access the data processing on their infrastructure. When dealing with highly sensitive/confidential data (such as banking information or healthcare patient data), this becomes a major concern and a barrier to further cloud adoption.
Traditional approaches for protecting data have relied upon implementing access controls and policies and encrypting data at rest and in transit, but none are able to prevent the threat in its entirety because a fundamental challenge remains: keeping data encrypted when in use, while it is being processed. Confidential computing – projected to be a $54B market by 2026 – is emerging as a way to remove the need for trusting infrastructure and service providers by keeping data protected/encrypted even when in use.
Confidential computing technology uses hardware-based techniques to create isolated environments called enclaves (also known as Trusted Execution Environments or TEEs).
Code and data within enclaves are inaccessible by other applications, users, or processes colocated on the system. The enclave keeps the data encrypted even when in use – while in memory and during computation. With a secure enclave environment, multiple parties can collaborate on analytics and AI use cases without compromising the confidentiality of their individual data and exposing it to other parties.
According to a recent survey, using secure enclaves in the enterprise setting is attractive for implementing safeguards for the following scenarios:
Protect against insider threats. Data in the cloud is accessible to the database administrators of the cloud applications or infrastructure via direct access to the database, application logs, and device memory
Prevent platform software (i.e., a platform hypervisor) from accessing data
Protect data from adjacent workloads in a multitenant/user environment
Protect the integrity of crowdsourced ML models
Confidential data sharing and multi-party collaboration
If these scenarios apply to you and your business, but you’re unsure what you’ll need to know to get started, here are five questions to ask your CISO:
1. Will I need to deploy specialized hardware to keep our data protected?
Confidential computing technology is now available on all major cloud providers. This obviates the need to procure and maintain specialized hardware yourselves. Even though confidential computing and secure enclaves are still in the “emerging technology bucket,” organizations can easily adopt confidential computing through cloud vendors and ISVs. The cloud providers see the benefit of secure enclaves and their future potential as a transformative technology, and so have bought in.
2. Will we need to rewrite applications to use secure enclaves?
Some confidential computing technologies, such as Intel SGX, require application modifications before they can run within enclaves. Other technologies, such as Confidential VMs, provide more flexibility and can run unmodified applications.
But, from a security perspective, this has the downside of having to trust the entire software stack within the VM. So, depending on the use case and requirements, one technology may be preferable over the other. In addition, proper adoption of confidential computing requires orchestrating management of the other constituent technologies, such as remote attestation.
The enclave adoption process can be complex and engineering teams will have to take time to build these capabilities to get their applications up and running. While bandwidth may be tight at times, the ROI is worth it in the long run. A growing ISV ecosystem can also help in the seamless adoption of confidential computing for a rich variety of use cases.
3. Can I use secure enclaves to improve data collaboration with other teams?
Before data can be shared with other teams, organizations typically need to follow a cumbersome governance process to restrict access to sensitive data, eliminate data sets or mask specific data fields, and prevent any level of data sharing.
Integrating secure enclaves provides an opportunity for organizations to increase both productivity and security measures. Multiple data owners can individually encrypt their entire data (including PII), pool it together, and analyze the collective data set within enclaves. Done effectively, multi-party collaboration can drive faster business results by enabling new and higher-quality insights.
4. Will I need to add additional security expertise to the team?
Implementing confidential computing workflows can be difficult to do directly without using existing tools and software. One needs to make sure that confidential data is protected throughout its lifecycle. This can have a variety of moving parts – from integrating with existing key management systems to managing secure enclave infrastructure, rewriting applications, deploying code securely and verifiably to the enclaves, and keeping confidential data encrypted in storage and in transit in/out of the enclaves. However, there is a rich emerging ISV ecosystem of software that alleviates the complexities of confidential computing for a rich variety of use cases, making it easy to use and adopt by non-experts.
5. Will I need to lock myself into a single cloud?
The top CPU vendors all introduced secure enclave and confidential computing solutions in recent years. These were adopted by the leading cloud vendors, some of which now offer solutions based on the same underlying technology. Microsoft Azure and Google Cloud Platform, for example, offer solutions based on AMD’s SEV technology. As software solutions running on top of these cloud platforms evolve, application vendors will introduce cross-platform solutions powered by the common hardware layers.
Conclusion
Businesses considering adopting cloud technology can better do so with secure enclaves. By asking your CISO these five questions, businesses can move into the future, understand what implementing secure enclaves will look like, better secure their data, and create a more efficient analytics process.
This ongoing shift to the cloud will increase efficiency for companies and reduce human error – especially knowing 57% of businesses will move their workloads to the cloud before the end of the year. When secure enclaves are implemented properly, the crucial component of ensuring security is not sacrificed. All businesses working with data should consider integrating confidential computing into their models to allow for analytics and AI on encrypted data.
Healthcare organizations are increasingly using apps for telehealth and beyond. These apps have a significant impact on how they operate. They also have access to lots of sensitive information, such as EMR.
As a result, we have seen an uptick in healthcare application threats globally. The top threat risks in healthcare industry includes ransomware, DDoS and automated attacks.
Healthcare data breaches are the costliest across the globe. They cost healthcare organizations USD 9.23 million on average. The figure is more than twice the pan-industry average of USD 4.24 million. Managing AppSec risks is crucial to healthcare organizations.
How to Reduce Risks of Healthcare Application Threats?
Ongoing Risk Assessments
This is the first, most critical step in risk management in healthcare. It lays the foundation for a robust AppSec program. Risk assessments help you identify, analyze and rank your apps’ risks.
Risk assessments involve the following:
Identifying app vulnerabilities
Evaluating the exploitability of each vulnerability
Identifying application threats
Analysing attack probability
Analysing the potential impact of application threats on mission-critical assets
Allocating resources based on the criticality of risks
Defining ways to keep risks within tolerance levels
This way, you can ensure your mission-critical assets are always available and secure.
Compliance frameworks like HIPAA mandate that these assessments be done once a year. But that isn’t enough. You need to keep assessing and managing risks regularly. Only then can you harden your app security posture.
Establish and Update Security Policies
Clearly defined app security policies are critical to averting application threat risks. These policies should incorporate security, industry, legal and regulatory best practices. The AppSec policies should define security strategies, processes, tools, and procedures. They should define the following:
Incident response and disaster recovery plans
Role-based, strict access controls
Zero trust authentication and password policies
Backup and storage
Data privacy and security policies
AppSec should define processes for users to report suspicious activities. AppSec policies should include proper communication plans too.
Further, you must regularly update these security policies. The policies should reflect the latest best practices and the latest risk posture.
Identify and Secure Threat Entry Points
How do application threats become successful attacks? Attackers keep looking for exploitable entry points. These entry points are vulnerabilities, misconfigurations, and security gaps. They exploit entry points that aren’t secure when they find them. They can then
Introduce malware
Create backdoors
Steal data
Make services unavailable to patients/ employees
So, you need to be proactive in finding and securing entry points. And do so before attackers find them. To this end, you must put in place a vulnerability management program.
Inventory all your healthcare app-related assets. This process should be automated. It should automatically identify all endpoints, APIs, components, third-party services, etc. Make sure to include all assets for crawling by your scanning and next-gen WAF tools.
Deploy an automated scanner to keep identifying known flaws. This way, you can prevent the inaccuracies and inefficiencies of manual scanning. Perform pen-testing and security audits regularly to identify
Unknown vulnerabilities
Logical flaws
Zero-day application threats
Understand the exploitability of flaws
Strength of security defenses
You can rank these flaws based on the level of risks involved. Then, you can remediate through permanent fixes or instant virtual patching. Leverage fully managed security solutions to manage your vulnerabilities better.
Centralized Visibility into Security Posture
You must have real-time visibility into your app security posture. This will help you take immediate action to prevent application threats.
Ensure Your Vendors Prioritize Security
You may use several third-party apps, APIs, and services. It is key that you carefully vet vendors before onboarding services. Why? Your apps will be at risk if they don’t take security seriously. Make sure they take steps to monitor and avert application threats.
You must also ensure vendors are compliant. To this end, you should keep monitoring and auditing them.
Keep Educating All Users
Human errors are top vulnerabilities enabling cyber attacks in healthcare. That is why continuous education of all users is a must. Users include patients/ customers, employees, and partners who use your apps.
All users must know the app security dos and don’ts. They should know what to click and what not to. They must be able to make smart decisions. They must know whom to report to or what action to take when observing unusual activities.
Invest in Reliable Security Solutions
Invest in reliable, fully managed security solutions like AppTrana. AppTrana includes comprehensive security solutions backed by industry expertise in managing your healthcare security risks.
The Way Forward Cyber-attacks on healthcare are becoming more lethal, complex, and severe. Take proactive action to minimize your application threat risk.
CISOs are working overtime and can’t always switch off from work, according to a recent Tessian report.
Recent headlines have shown that security stakes have never been higher, and it’s likely this high level of pressure that’s causing 18% of security leaders to work 25 extra hours a week. That’s double the amount of overtime that they worked in 2021. While many are hopping on the “quiet-quitting” trend, CISOs have the opposite problem.
In this Help Net Security video, Josh Yavor, CISO at Tessian, offers a personal perspective on dealing with burnout as a CISO.
A security flaw in the Galaxy Store allows attackers to trigger remote code execution on affected smartphones.
The now patched vulnerability, which affects Galaxy Store version 4.5.32.4, relates to a cross-site scripting (XSS) bug that occurs when handling certain deep links. An independent security researcher has been credited with reporting the issue.
Vulnerability Details
The now-patched vulnerability is related to a cross-site scripting (XSS) flaw that occurs when handling specific deep links and it affects Galaxy Store version 4.5.32.4. The problem was first reported by an independent security researcher.
Particularly, deeplink can be called from another application or from a browser. The store receives appropriate deeplinks, it will process and show them in a webview.
In this case, by failing to secure the deeplink, the attacker is able to run JS code in the Galaxy Store application’s webview context whenever a user hits a link from a website that contains the deeplink.
The expert focuses on deep links configured for Samsung’s Marketing & Content Service (MCS).
Although the Samsung MCS Direct Page website was extracting the argument from the url and displaying it on the website, it did not encrypt, which resulted in an XSS problem.
“We can see the website is processing the abc, def parameters and displaying as above without encoding, the url is passed directly to href this is very dangerous and will cause XSS.” reads the advisory published by SSD Secure Disclosure.
Experts observed two functions ‘downloadApp’ and ‘openApp’ here these two functions will get the app id and download them from the store or open them.
This indicates that these two functions can be called using JS code. In this case, an attacker has the ability to execute arbitrary code by injecting it into the MCS website.
“To be able to successfully exploit the victim’s server, it is necessary to have HTTPS and CORS bypass of Chrome,” advisory published by SSD Secure Disclosure
Affected Products and Patch Available
The vulnerability impacts Galaxy Store version 4.5.32.4.
Therefore, Samsung has issued patches that are now in wide circulation for all Samsung devices.
33N Ventures is fundraising €150 million for investing in cybersecurity and infrastructure software companies across Europe, Israel, and the US. The fund will mostly target investments at Series A and B, with an average ticket size of around €10 million, and has an investment capacity of €20 million already committed by Alantra and its strategic partners.
Co-founders and managing partners Carlos Alberto Silva and Carlos Moreira da Silva have made more than 20 investments in cybersecurity and infrastructure software over the past 10 years, across Europe, Israel and the US – including most notably Arctic Wolf.
In this Help Net Security interview, they discuss the cybersecurity investment landscape in Europe, the strategies for finding the right companies, and more.
Company founders usually think mainly about California and Tel Aviv when discussing infosec investments. What’s your impression of the current cybersecurity VC landscape in Europe?
Carlos Alberto Silva: There’s no doubt that the US and Israeli startup ecosystems get more attention when it comes to cybersecurity. But that’s not to say there haven’t been success stories in Europe. Take IriusRisk, for example: the automated threat modeling platform raised a $28.7M Series B round just a few weeks ago.
By rights, Europe should be a world leader in this space. Talent is abundant here, and there is a very large addressable market. The challenge for companies in Europe is that, unlike their peers in the US and Israel, they often don’t get the specialized support they need to compete.
While there are a few specialized funds in Europe, most focus naturally only on one country or region and tend to invest in very early-stage companies. As a result, most entrepreneurs face the choice of working with a US investor (that lacks on-the-ground local knowledge) or working with a generalist fund that may not be able to open the right doors for them.
That’s why we’ve decided to create a fund with a truly pan-European focus. There’s such a large opportunity here for firms that are underserved by the current market. We’ll still be investing in some companies in the US and Israel – simply put, there are some amazing opportunities that we just don’t want to miss out on – but we’re most excited about capitalising on this relatively untapped opportunity in Europe.
What sort of challenges and opportunities are you currently facing? What’s your main focus?
Carlos Alberto Silva: Given that we only launched the fund last week, we’ve not run into too many challenges yet! That being said, of course, the economic climate is not the best. This is a challenge that every venture capital fund and company must face.
Cybersecurity as a whole is also well insulated from the economic downturn. That’s because strong cybersecurity is not a ‘nice-to-have’ – but critical. That’s not going to change – from digital transformation to national security, cyber will continue being a top priority for governments, institutions, companies, and investors across the globe, and the market is expected to reach $162 billion in 2022, with robust annual double-digit growth forecast for the coming years – and so the companies we’ll be looking at have some in-built resilience.
How can you find the right balance between locating promising new businesses and researching potential investments?
Carlos Moreira da Silva: This is not generally something we struggle with. This is probably because we follow a thesis-driven approach that means we spend a lot of time looking at which spaces we want to cover before making any investment decisions.
Of course, we stay up to date with the industry, look at all publicly available sources, and attend the most relevant cybersecurity events across Europe, Israel, and the US. This is all fairly common sense.
But we do rely heavily on our proprietary network of close VCs and advisors. Our network is always totally invaluable when we are looking to identify the best leads for future investments. Our strategic advisors – including leading entrepreneurs, experts, and cybersecurity decision-makers such Brian NeSmith (Arctic Wolf), Eyal Hayardeny (Reblaze), Nuno Sebastião (Feedzai), and Pierre Polette (Hackuity) – all founders of companies we’ve invested in in the past – possess an incredible depth and breadth of sector-specific knowledge and experience that, added to our own, really helps us identify and support the founders and companies with the biggest breakthrough and scaling potential.
We spend a long time talking to prospective investee companies, ideally as early in their journey as possible, and working out where we can help them. If we can make an introduction to a potential customer, for example, we will do so even before we have made any investment. We’ve worked hard to build a reputation in the industry for being supportive of the whole industry – that’s really important to us.
How much research does it take to identify companies you want to invest in? When it comes to cutting-edge technology, it can be complicated to distinguish between things that seem important but aren’t and things that don’t seem important but are.
Carlos Alberto Silva: For most first-time funds the process of identifying the right companies to invest in across such a large geographic area would be difficult. But our team has been together for many years now. We may be a first-time fund, but we’re far from a first-time team.
We know this space well and we have a strong network that reaches across the US, Europe, and Israel. In fact, much of the research you refer to has in effect already been done. We already have a list of companies that we’re interested in, and in many cases have already started the conversation.
We want to back visionary companies in emerging sectors. We want to invest in those who are the very first or one of the very first to solve a particular problem. In our view, jumping on bandwagons or entering already saturated markets will inevitably lead to meagre returns. Get in on the ground floor and you’ve got a lot more room to grow into.
What advice would you give to cybersecurity startup founders looking for investors?
Carlos Moreira da Silva: Beyond the obvious – how much are they willing to invest – there are a couple of really important things for founders to look at. Firstly, look at their track record. Cybersecurity is a space where deep technical knowledge is really important. Think of it this way: if you have to explain what your company does through metaphors and hand-holding, then they probably aren’t going to be much help beyond providing cash stimulus.
The second thing to look at is their network. Well-connected investors with the right contacts in cybersecurity will prove invaluable. Most venture capital investors will have a long list of contacts. You can pick that up by going to the right events and spending enough time in the space. But the investors that will provide you with real benefit are those who have a long list of friends – with deep and genuine relationships. The right introduction can be game-changing for a company, so it’s vital your investor’s network is robust.
What tips do you have for maintaining a positive rapport with company founders? What makes for a quality relationship?
Carlos Moreira da Silva: It may sound obvious, but in our experience, the most important thing for building rapport is having a solid understanding of the business. It is important to be there for the founders during the good times, but especially during the challenging times, when they really need that extra help. Of course, you must understand how the company’s key product or service works.
But beyond that, you must understand everything from the pain points of their customers to the market for talent in their sector to the opportunities for growth. This is not stuff you can pick up overnight, and entrepreneurs are good at picking those with genuine knowledge out from the blaggers.
And, in our case, we can share our global perspective regarding the wider market environment. You can provide an enormous amount of value here.
We also think it helps that we’ve been in their position before. We’re not just investors, we’ve held senior executive roles in cybersecurity companies and effectively built them from the ground up. So, we understand the nuances of the day-to-day running of a business, and that helps us build a foundation of trust – which really is essential to a successful relationship.
There is an unofficial patch from 0patch for a Zero-Day flaw in Microsoft Windows that allows bypassing the MotW (Mark-of-the-Web) protections that are built into the operating system and at moment it’s actively exploited.
By utilizing files signed with malformed signatures, this zero-day flaw is able to bypass MotW protections. Various legacy Windows versions as well as all versions that are supported by Microsoft are affected by the issue.
It has been determined by cybersecurity analysts that the Magniber ransomware was being installed on victims’ devices with the help of stand-alone JavaScript files by threat actors.
Why does Windows 8.1 not have the behavior where a corrupt signature skips the MotW prompting? Windows 10 and newer MotW prompting is sort of intermingled with SmartScreen by default. If you turn off "Check apps and files", you'll get behavior more like earlier Windows versions. pic.twitter.com/T6k3xNKOFY
0patch released this unofficial security patch to fix this flaw since it’s a critical zero-day vulnerability and is exploited by threat actors vigorously in the wild.
Why this patch has been tagged as “Unofficial”?
This patch is tagged as unofficial due to its release source, in short, this patch has not been released by Microsoft itself.
But, until the release of any official patch from Microsoft, users can use this security patch to keep their systems protected against threat actors exploiting this zero-day flaw.
Free Micropatch Availability
Due to this zero-day vulnerability, multiple Windows versions are affected and here below we have mentioned all the affected versions of Windows that are eligible for the free micropatches:-
Windows 11 v21H2
Windows 10 v21H2
Windows 10 v21H1
Windows 10 v20H2
Windows 10 v2004
Windows 10 v1909
Windows 10 v1903
Windows 10 v1809
Windows 10 v1803
Windows Server 2022
Windows Server 2019
The installation process for this micropatch will require an account on the 0patch website, and it can be created for free. Once done, you’ll need to download its agent for your Windows device which will automatically install this patch.
During recent research, Microsoft has discovered evidence of a complex interconnected malware ecosystem that is associated with the Raspberry Robin worm.
With other malware families, there are several root links to the Raspberry Robin worm were identified. Even security experts have detected that it uses alternate infection tactics as well.
Infections like these lead to a variety of complications and here below we have listed them:-
Hands-on-keyboard attacks: When attackers are already inside your environment following a breach, a hands-on keyboard attack will occur. It is a two-sided operation; on one end it’s the cybercriminal who sits at a keyboard, while on the other side it’s your compromised network that is being accessed.
Human-operated ransomware activity: It occurs when cybercriminals are involved in an active attack on a victim. Using this approach, an organization’s on-premises infrastructure is penetrated, privileges are elevated, and ransomware is deployed by the threat actors.
Compromised 1,000 Organizations
In the past 30 days, on more than 1000 organizations’ 3000 devices, the Raspberry Robin worm has initiated payload alerts. There have been instances where the Raspberry Robin worm has been installed on the victims’ systems with malware called FakeUpdates.
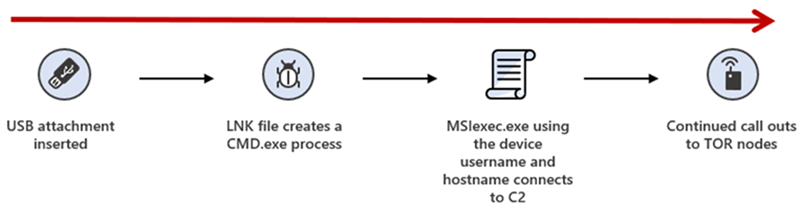
Raspberry Worm is also known as QNAP Worm, as for command-and-control, it uses the compromised QNAP storage servers. Through infected USB drives containing malicious. LNK files, Raspberry Robin spreads to other devices.
The worm will spawn a msiexec process using cmd[.]exe as soon as a USB device is attached.
In order to communicate with its C2 servers, the malware communicates with compromised Windows devices.
Raspberry Robin’s Connection
Microsoft Security Threat Intelligence Center (MSTIC) observed Raspberry Robin in October 2022, and it’s being used by DEV-0950, which is another actor who was also involved in the post-compromise activity.
As a result of the DEV-0950 activity, the Cobalt Strike was compromised through hands-on keyboard activity. The majority of the victims of DEV-0950 are traditionally acquired via phishing scams.
However, the operators of DEV-0950 have moved to use Raspberry Robin instead of the traditional method. The advantage of this approach is that the payloads can be delivered to existing infections and the campaigns can move to the stage of ransomware more quickly.
Mitigations
To mitigate the impact of this threat, it is also possible for defenders to apply the following mitigation measures:-
When mounting the drive, prevent autorun from being used and code from being executed.
Make sure the tamper protection setting is enabled in order to protect Microsoft Defender Antivirus from being interrupted by attacks.
It is very important to turn on cloud-delivered protection for Microsoft Defender Antivirus or your antivirus software counterpart if it supports the feature.
The USB port should be blocked from running untrusted or unsigned processes.
Scripts that may be obfuscated should be blocked from being executed.
It is imperative to block executable files from running unless they fulfill all the trusted criteria.
The local security authority subsystem of Windows should be protected against credential theft.
In this Help Net Security video, Dmitry Bestuzhev, Most Distinguished Threat Researcher at BlackBerry, talks about some of the most interesting tactics, techniques, and procedures employed by cybercriminals in recent months.
A new version of Wireshark has been released recently by the Wireshark Team, it’s Wireshark 4.0.1, which contains several enhancements, new updates, and bug fixes.
Wireshark is one of the most widely used open-source free software packet analyzers that are currently available on the market, and it is available in a variety of options for different platforms.
There are many people who use Wireshark packet analyzers for the analysis of packets, not just network administrators only. As security analysts also use Wireshark packet analyzers for packet analysis purposes.
Several organizations make use of this tool to manage and monitor all the activities of their business operations on a regular basis.
Wireshark recently released its Wireshark 4.0.0 and the current Wireshark 4.0.1 is a quick update from the previous one.
Platform Support
For all the major platforms or operating systems, the Wireshark 4.0.1 packet analyzer is available and here below we have mentioned them:-
Windows
Linux
macOS
BSD
What’s new in Wireshark 4.0.1?
There are several primary purposes for using Wireshark as a network protocol analyzer, including:-
Analysis
Troubleshooting
Education
Development
Wireshark 4.0 and later do not have any official 32-bit Windows packages that you can install on your computer. Qt 5.12.2 is now the standard version that ships with Windows installers. The previous version of these packages was Qt 6.2.3, which was shipped by default.
This release removes the experimental syntax for the display filter used in Wireshark 4.0.0 that allowed literals to be displayed just using angle brackets <…>. You can use the colon prefix instead while dealing with byte arrays.
As part of the criminal case against a former student of the University of Puerto Rico (UPR), a judge in Puerto Rico sentenced him to serve 13 months in federal prison.
The former student, Iván Santell-Velázquez (aka Slay3r_r00t) was accused of hacking over a dozen of the university’s female classmates’ email and Snapchat accounts.
On July 13, Ivan pled guilty to being a cyberstalker, admitting that he had targeted over 100 students in his online campaign. He also engaged in other schemes to steal information such as using spoofing and phishing.
He has been accused of harassing women and in some cases, he has published pictures that he has stolen from them in their nudist states between 2019 and 2021.
Apart from hacking student email accounts, he also managed to get access to multiple university email accounts by spoofing and phishing attempts through which he gathered personal information.
Students Data Stolen
The appellant, Iván Santell-Velázquez targeted 15 female students in total at the University of Puerto Rico. A victim of cyberstalking may experience a significant amount of emotional distress as a result of it.
“The prosecution of cyber criminals is a top priority in the Justice Department. Cybercrimes not only cause financial losses to corporate victims but also result in financial and psychological harm to vulnerable victims, oftentimes children or the elderly. This conduct will not be tolerated.”
“This case also demonstrates the importance of safeguarding personal information and passwords, and the care we must take when responding to suspicious e-mails and text messages.”
As a result of his illicit crimes, Iván Santell-Velázquez was sentenced to 13 months of rigorous imprisonment along with 2 years of supervised release for cyberstalking by Silvia Carreño Coll, the U.S. District Court Judge.
As data breaches’ financial and reputational costs continue to reach new heights, cybersecurity should be on top of mind for leadership across every industry.
Recent Proofpoint research found that 65% of board members believe their organization is at risk of material cyber attack in the next 12 months. Worryingly, 47% feel their organization is unprepared to cope with a targeted attack.
In this Help Net Security interview, Chris Konrad, Area Vice President of Security, Global Accounts at World Wide Technology, offers advice to CISOs that are increasingly under pressure, discusses using a security maturity model, discusses interesting security technologies, and more.
What advice would you give to a newly appointed CISO that strives to improve security strategy?
CISOs can no longer focus strictly on developing technical capabilities and protecting their organizations. Executives and boards are looking to CISOs to make investments that drive growth with a holistic security framework.
First, every CISO needs to know what their board’s mission and vision are, as well as what their risk appetite and tolerance are. You can’t secure what you can’t see. No security program can fully eliminate risk or human error, but a mature approach to cybersecurity can mitigate the risks that pose the most danger to organizational objectives and success.
The next step is conducting a comprehensive cybersecurity program assessment to know at what level of risk you are operating. This type of analysis provides rich insights that can be actioned to increase your security program maturity. This analysis also helps to maximize the use of people, processes and technology to reduce risk and increase efficiencies.
Risk management should be a C-suite priority because it is one of the single most important determinants of business value realization. Risk management is the system by which an organization’s portfolio is directed and controlled.
How can an organization leverage a security maturity model to assess its current infosec position?
A security maturity model can help CISOs measure, communicate and visualize improvements and investments in the security program. There are many different maturity models available to help you measure a security program. One I like is the Capability Maturity Model Integration (CMMI), a process improvement maturity model for the development of products and services, developed and published by the Software Engineering Institute of Carnegie Mellon University in Pittsburgh.
Using CMMI in combination with the National Institute of Standards and Technology (NIST), an organization can have one axis measuring people, process and technology and the other axis measuring maturity from nonexistent capability to optimized.
Of course, there is not a one-size-fits-all approach – so security teams must also work with the business to understand what is key to success, and ultimately, growth.
What cybersecurity technologies are you excited about? What can make a difference in this fast-paced threat landscape?
Most organizations are doing some form of tools rationalization or platform consolidation to get a better handle on their investments and reduce overlapping capability and spend. However, there are a few technologies that have caught my eye.
For me, I love seeing how AIOps can help organizations detect, assess and eliminate potential security vulnerabilities — before they are exploited by adversaries or those acting in bad faith. AIOps is starting to transform the way organizations tackle the complex cybersecurity ecosystem.
Innovative organizations, like Cribl, can receive machine data from any source and cleanse and enrich your data before routing it to any logging or SIEM platform, like Splunk, to reduce the total amount of data that needs to be managed. CrowdStrike is enhancing observability through modern log management with LogScale, which is built to ingest and retain streaming data as quickly as it arrives, regardless of volume. Alerts, scripts and dashboards are updated in real-time, and Live Tail and retained data searches have virtually no latency.
What are the biggest challenges the cybersecurity industry will face in the next five years?
Among the biggest challenges are that our adversaries are getting smarter, and they are leveraging much of the same technology that we use to defend ourselves. There is also a wider, and perhaps more concerning, issue around the shortage of skilled resources at a global level. Cybersecurity is one of the most important industries to safeguard our democratic value but more often than not, it’s seen as an overly technical, and therefore, not attractive career. We need to be shining the light on more routes into cyber roles and also accelerating diversity.
One area that’s often overlooked is identifying people within your organization and up-leveling them. Of course, those with earned experience have the hard skills to succeed, but I think an enthusiasm and drive to achieve is just as important. And by prioritizing STEM in early education, we further raise awareness of the field.
World Wide Technology employs thousands of professionals in the STEM fields across the globe and understands the urgency of supporting future tech leaders. WWT annually hosts its STEM Student Forum, an initiative dedicated to educating high school students on the importance of STEM disciplines and the opportunities they present, while also creating positive change in the St. Louis metropolitan area, where WWT’s global headquarters is located.
At its Dash 2022 conference, Datadog shared a report that found the primary security challenge organizations encounter in the Amazon Web Services (AWS) cloud is lax management of credentials.
Based on data collected from more than 600 organizations that rely on the Datadog platform to monitor their AWS cloud computing environments, the report also noted the complexity of the AWS identity and access management (IAM) service may lead organizations to publicly expose sensitive resources by accident.
Access keys are a static type of credential that do not expire. The Datadog report found 75% of AWS IAM users have an active access key that’s older than 90 days, while 25% have an active access key that’s older than one year and hasn’t been used in the past 30 days.
A total of 40% have also not used their credentials in the past 90 days, while 40% of organizations have at least one IAM user that has AWS Console access without multifactor authentication (MFA) enabled.
Andrew Krug, lead technical evangelist for security at Datadog, said managing cloud credentials is challenging because organizations often lack any offboarding processes to limit access when, for example, an employee leaves the company. As a result, cybercriminals that steal credentials are then able to easily gain access to cloud environments simply because organizations don’t rotate access keys, he added.
Datadog also noted that, by default, AWS provisions users at a root level that provides them with unlimited administrative permissions. Datadog found approximately 10% of organizations have an active root user access key. Some of these keys are up to 13 years old. A quarter of organizations (25%) had someone use root user credentials in the 30 days prior to the Datadog study. There may be a legitimate need for that level of access, but Krug noted the best practice is to employ least-privilege access whenever possible.
Other issues surfaced by Datadog pertain to how organizations configure cross-account access by using a resource-based IAM policy attached to the resource itself. The report found 18% of organizations that use the Amazon Simple Queue Service, for example, have at least one publicly exposed queue that enables anyone to receive or publish messages to those queues. More than a third of organizations that use the AWS S3 cloud storage service have at least one publicly exposed bucket.
Krug said it needs to be less complex to create secure IAM policies that grant least-privilege, granular permissions. It’s simply too easy to make a mistake, he added.
A fourth cloud security issue that’s widely overlooked is continued reliance on the first version of a EC2 Instance Metadata Service (IMDS) service that has known vulnerabilities. AWS has made available a more secure version, but Datadog found the vast majority of EC2 instances (93%) are not enforcing the usage of IMDSv2. Overall, 95% of organizations that use EC2 have at least one vulnerable instance. The second version of IMDS should be the default configuration, said Krug.
Finally, Datadog found at least 41% of organizations have adopted a multi-account strategy in AWS, with 6% of organizations using more than 10 AWS accounts. Datadog recommended centralizing accounts to make it easier to monitor who has gained access to a cloud computing environment.
Despite these issues, cloud platforms are still fundamentally more secure than on-premises IT environments. However, it’s also clear there is plenty of opportunity for mistakes to be made.
Third-party risk assessments are often described as time-consuming, repetitive, overwhelming, and outdated. Think about it: organizations, on average, have over 5,000 third parties, meaning they may feel the need to conduct over 5,000 risk assessments. In the old school method, that’s 5,000 redundant questionnaires. 5,000 long-winded Excel sheets. No wonder they feel this way.
The reason why risk assessments have become so dreaded is that it has always been a process of individual inspection and evaluation. For perspective, that’s roughly 14 risk assessments completed per day in the span of one year. How can we expect security, risk, and procurement professionals to get any other work done with this type of task on their plate? With the state of today’s threat landscape, wouldn’t you rather your security team be focused on actual analysis and mitigation, rather than just assessing? And, not to mention the fact that a tedious risk assessment process will contribute to burnout that can lead to poor employee retention within your security team. With how the cybersecurity job market is looking now, this isn’t a position any organization wants to be in.
So, now that you know how the people actually with their ‘hands in the pot’ feel about risk assessments, let’s take a look at why this approach is flawed and what organizations can do to build a better risk assessment process.
The never-ending risk assessment carousel ride
The key to defeating cybercriminals is to be vigilant and proactive. Not much can be done when you’re reacting to a security incident as the damage is already done. Unfortunately, the current approach to risk management is reactive, and full of gaps that do not provide an accurate view into overall risk levels. How so? Current processes only measure a point-in-time and do not account for the period while the assessment is being completed–or any breaches that occurred after the assessment was submitted. In other words, assessments will need to be routinely refilled out, a never-ending carousel ride, which is not feasible.
It should come to no surprise that assessments are not updated nearly as much as they should be, and that’s to no one’s fault. No one has the time to continually fill out long, redundant Excel sheets. And, not to mention, unless the data collected is standardized, very little can be done with it from an analysis point of view. As a result, assessments are basically thrown in a drawer and never see the light of day.
Every time a third-party breach occurs there is a groundswell of concern and company executives and board members immediately turn to their security team to order risk assessments, sending them on a wild goose chase. What they don’t realize is that ordering assessments after a third-party breach has occurred is already too late. And the organizations that are chosen for a deeper assessment are most likely not the ones with the highest risk. Like a never-ending carousel ride, the chase for risk assessments will never stop unless you hop off the ride now.
Show me the data!
The secret ingredient for developing a better risk management collection process is standardized data. You can’t make bread without flour, and you can’t have a robust risk management program without standardized data. Standardized data is the process of gathering data in a common format, making it easier to conduct an analysis and determine necessary next steps. Think of it this way, if you were looking at a chart comparing student test grades and they were all listed in various formats (0.75, 68%, 3/16, etc.), you would have a difficult time comparing these data points. However, if all the data is listed in percentages (80%, 67%, 92%, etc.), you could easily identify who is failing and needs more support in the classroom. This is the way using standardized data in the risk assessment process works. All data collected from assessments would be in the same format and you can understand which third parties are high risk and require prioritized mitigation.
CISOs who are still focused on point-in-time assessments are not getting it right. Organizations need to understand that risk assessment collection alone does not in fact equal reduced risk. While risk assessments are important, what you do with the risk assessment after it is complete is what really matters. Use it as a catalyst to create a larger, more contextual risk profile. Integrate threat intelligence, security ratings, machine learning, and other data sources and you’ll find yourself with all the data and insights you need and more to proactively reduce risk. You’ll be armed with the necessary information to mitigate risk and implement controls before the breach occurs, not the rushed patchwork after. A data-driven approach to third-party risk assessment will provide a more robust picture of risk and put an end to chasing assessments once and for all.