Nov 08 2020

FBI: Hackers stole source code from US government agencies and private companies

FBI blames intrusions on improperly configured SonarQube source code management tools.

FBI officials say that threat actors have abused these misconfigurations to access SonarQube instances, pivot to the connected source code repositories, and then access and steal proprietary or private/sensitive applications.

Officials provided two examples of past incidents:

“In August 2020, unknown threat actors leaked internal data from two organizations through a public lifecycle repository tool. The stolen data was sourced from SonarQube instances that used default port settings and admin credentials running on the affected organizations’ networks.

“This activity is similar toa previous data leak in July 2020, in which an identified cyber actor exfiltrated proprietary source code from enterprises throughpoorly secured SonarQube instances and published the exfiltrated source codeon a self-hosted public repository.”

Source: FBI: Hackers stole source code from US government agencies and private companies | ZDNet


Nov 06 2020

Pwn2Own Tokyo Day one: NETGEAR Router, WD NAS Device hacked

Category: cyber security,Hacking,Information Security — DISC @ 11:30 am

Pwn2Own Tokyo 2020 hacking competition is started, bug bounty hunters already hacked a NETGEAR router and a Western Digital NAS devices.

The Pwn2Own Tokyo is actually coordinated by Zero Day Initiative from Toronto, Canada, and white hat hackers taking part in the competition have to demonstrate their ability to find and exploit vulnerabilities in a broad range of devices.

On the day one of the competition, bug bounty hunters have successfully hacked a vulnerability in the NETGEAR Nighthawk R7800 router. The participants were the Team Black Coffee, Team Flashback, and teams from cybersecurity firms Starlabs and Trapa Security, and the Team Flashback earned $20,000 for a remote code execution exploit that resulting from the chaining of two bugs in the WAN interface.

“The team combined an auth bypass bug and a command injection bug to gain root on the system. They win $20,000 and 2 points towards Master of Pwn.” reads the post on the official site of the Pwn2Own Tokyo 2020.
The Trapa team successfully chained a pair of bugs to gain code execution on the LAN interface of the router, the experts earned $5,000 and 1 point towards Master of Pwn.

The STARLabs team earned the same amount after using a command injection flaw to take control of the device.

The Western Digital My Cloud Pro series PR4100 NSA device was targeted by The Trapa Security team also earned $20,000 for a working exploit for the Western Digital My Cloud Pro series PR4100 NSA device.

The exploit code chained an authentication bypass bug and a command injection vulnerability to gain root on the device.

Source: Pwn2Own Tokyo Day one: NETGEAR Router, WD NAS Device hacked


Pwn2Own Tokyo (Live from Toronto) 2020 – Day One
httpv://www.youtube.com/watch?v=jX0b8iKXnbI&ab_channel=ZeroDayInitiative

Tags: pwn2own, Pwn2Own Tokyo


Nov 05 2020

Spotting a Common Scam

Spotting a Common Scam 

Image
These scams seek to collect personal information about you, often appearing to come from a real business or agency. Someone may pose as an official disaster aid worker, or send you a fraudulent COVID contact tracing email. If you receive a message with a link, you should not click it as it may download malware to your device to steal passwords and personal information. Government agencies like FEMA or the IRS will never contact you asking for a FEMA registration number, a Social Security number, or a bank account or credit card number to give you a COVID or FEMA payment—or ask you to pay anything up front to fill out an application or to access state or federal resources.
Image


Before sharing, check that what you are reading is from a trustworthy source. Disinformation can be life threatening in a global pandemic.


Image

No cures or vaccines have been approved for COVID-19 yet. Online offers claiming to provide a medicine or device to treat or prevent COVID should be ignored. When there is a new breakthrough in the treatment and prevention of COVID, it will be widely reported on by reputable news sources.


Image


Fake charities often emerge following a crisis, soliciting donations, but not using them for the described purpose. Before donating, check out www.ftc.gov/charity  to research the organization and make sure it’s legitimate.


Image

If you receive a robocall, you should hang up instead of pushing any buttons or giving away any personal information. If a call claims to be from the IRS or FEMA, but demands immediate payment through debit card or wire transfer, it is fraudulent. Federal agencies will never demand immediate payment over the phone, threaten immediate arrest, or ask you to make a payment to anyone other than the U.S. Treasury.

Warning Signs that a Loved One may be the Victim of a Scam 
Victims to a scam may be embarrassed or uncomfortable asking for help. It’s not always obvious when someone has been scammed, so check in with your loved ones frequently, especially if they are older, live alone, or are otherwise high risk.

Warning signs include large ATM withdrawals, charges, or checks; secretiveness and increased anxiety about finances; large quantities of goods being delivered that they do not need; an unusual number of phone calls or visits from strangers; and a sudden lack of money, unpaid bills, or a change in daily habits.


For more information, and to get help with a potential FEMA fraud, you can call the National Center for Disaster Fraud Hotline at 866-720-5721 or FEMA’s Public Inquiry Unit at 916-210-6276. For questions about pandemic scams, go to www.ftc.gov/coronavirus or www.cdc.goc/coronavirus/2019-ncov .


Tags: common scam, scam


Nov 03 2020

Privacy-focused Brave browser grew over 130% in the past year

Category: Information Privacy,Web Security — DISC @ 1:07 pm

Brave Browser, the privacy-focused web browser, announced today that it grew in usage by over 130% in its first year of the release of its ‘Stable’ version.

Source: Privacy-focused Brave browser grew over 130% in the past year


Brave Browser Review 2020: Should you make the switch?
httpv://www.youtube.com/watch?v=cQuTwpUFIXU&ab_channel=dottotech


Why you should download Brave Browser NOW!

Tags: data privacy, Information Privacy, loss of privacy


Nov 02 2020

Cyber Security Training Courses

Category: cyber security,Security Awareness,Security training — DISC @ 11:17 pm

Cyber Security Training Courses via Simpliv

[pdf-embedder url=”https://blog.deurainfosec.com/wp-content/uploads/2020/11/Simpliv-Links.pdf” title=”Simpliv Links”]

To review each course download a pdf of Cyber Security Training Courses

Tags: Cyber Security Training Courses


Nov 01 2020

Open Shell brings back the glory days of the Windows Start Menu

Category: Windows Security — DISC @ 11:14 pm

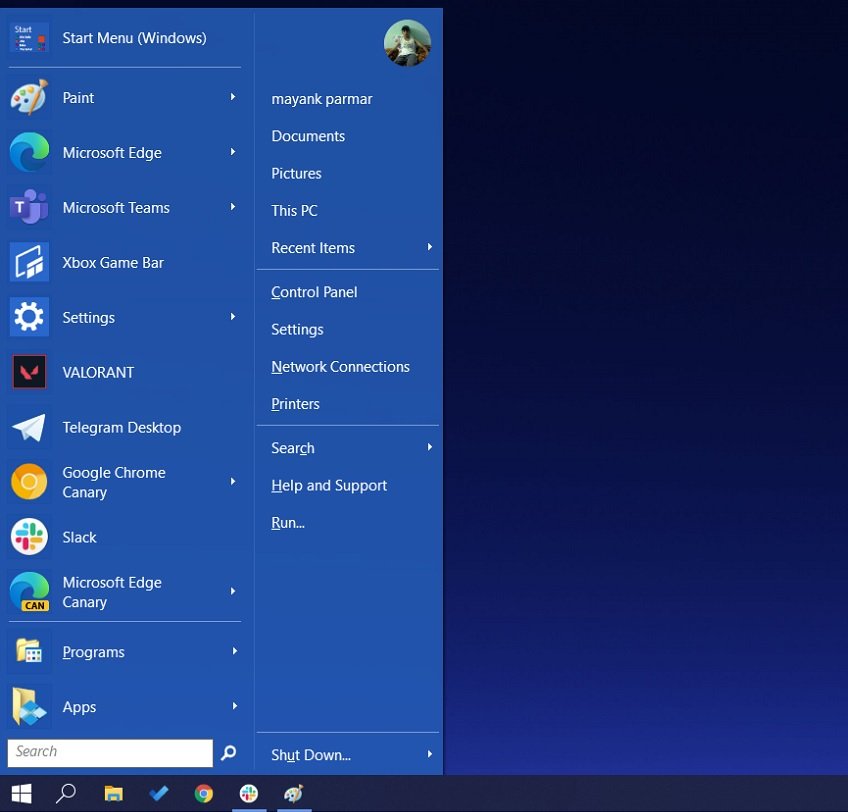
Open Shell, originally known as Classic Shell, is open-source software that allows you to replace the standard Start Menu on Windows 10 and Windows 8.

Source: Open Shell brings back the glory days of the Windows Start Menu


Make Your Start Menu Look Like Windows 7 With Open Shell
httpv://www.youtube.com/watch?v=WlBVCNHB8uQ&ab_channel=majorgeeks

Tags: Open Shell, Windows Start Menu


Oct 30 2020

In a first, researchers extract secret key used to encrypt Intel CPU code

Category: Crypto,Cryptograghy — DISC @ 2:49 pm

Hackers can now reverse-engineer updates or write their own custom firmware.

Source: In a first, researchers extract secret key used to encrypt Intel CPU code


Oct 29 2020

Buer Loader “malware-as-a-service” joins Emotet for ransomware delivery

Category: Ransomware — DISC @ 2:05 pm

A relative newcomer in the “malware-as-a-service” scene is starting to attract the big-money ransomware criminals.

Source: Buer Loader “malware-as-a-service” joins Emotet for ransomware delivery


Understanding malware as a service
httpv://www.youtube.com/watch?v=VoOJaKZvZ-o&ab_channel=BitdefenderOEM


MaaS Chaos. Is Malware-as-a-Service Growing?
In the legitimate business world, there’s something known as Software-as-a-Service, or SaaS. Here’s a definition: A software licensing-and-delivery model in which centrally located and controlled software is made available and licensed/rented on a subscription basis by users. SaaS clients are generally businesses.

Now, organized online crooks have moved into that space and business model too. It didn’t take long for that large-scale approach to not only hit the Internet, but to create a lucrative malware business for criminals who are selling viruses and more to anyone who wants it and is willing to pay for it. It’s “MBA-like” thinking for the purpose of making money by committing technologically based crimes.

Malware-as-a-Service is the latest term for the business of a network of sophisticated cyber-crooks providing illegal services, for a fee.


One of the reasons that cybercrime has grown so rapidly is that the criminals at the top of the “food chain” have built scalable business models for their crimes. This allows experienced hacking groups to collaborate, and new criminals to leverage the resources of veteran hackers. “Crime-as-a-service” is nothing new, but the tools change rapidly as crimeware developers work to exploit the latest vulnerabilities and stay ahead of security. The Emotet banking trojan has emerged as a leader in providing malware delivery services to other hacking groups, and you will want to make sure you understand and defend against this threat.

Emotet emerges as a leader in Malware-as-a-Service

Tags: Emotet, malware-as-a-service


Oct 27 2020

Google Mending Another Crack in Widevine

Category: data security — DISC @ 12:05 pm

For the second time in as many years, Google is working to fix a weakness in its Widevine digital rights management (DRM) technology used by online streaming sites like Disney, Hulu and Netflix to prevent their content from being pirated.

The latest cracks in Widevine concern the encryption technology’s protection for L3 streams, which is used for low-quality video and audio streams only. Google says the weakness does not affect L1 and L2 streams, which encompass more high-definition video and audio content.

“As code protection is always evolving to address new threats, we are currently working to update our Widevine software DRM with the latest advancements in code protection to address this issue,” Google said in a written statement provided to KrebsOnSecurity.

In January 2019, researcher David Buchanan tweeted about the L3 weakness he found, but didn’t release any proof-of-concept code that others could use to exploit it before Google fixed the problem.

Source: Google Mending Another Crack in Widevine


Tags: digital rights management, DRM


Oct 26 2020

Botnet Infects Hundreds of Thousands of Websites

Category: Botnet — DISC @ 9:02 pm

KashmirBlack has been targeting popular content management systems, such as WordPress, Joomla, and Drupal, and using Dropbox and GitHub for communication to hide its presence.

The botnet, dubbed KashmirBlack, uses a modular infrastructure that includes features such as load balancing communications with command-and-control servers and storing files on cloud storage services, such as Dropbox and GitHub, to speed access to any new code updates for the systems infected with the software. The KashmirBlack botnet mainly infects popular CMS platforms, exploiting dozens of known vulnerabilities on targeted servers and performing millions of attacks per day on average, according to a pair of reports published by Imperva researchers today.

Source: Botnet Infects Hundreds of Thousands of Websites


CyberHub Podcast – Practitioner Brief 10-26-20 Emotet upgrades, Kashmirblack & ransomware surge
httpv://www.youtube.com/watch?v=2td9wQ4LleY&ab_channel=TheCyberHubPodcast


Oct 21 2020

PayPal to allow cryptocurrency buying, selling and shopping on its network

Category: Crypto,Cryptograghy — DISC @ 10:36 am

PayPal Holdings Inc joined the cryptocurrency market on Wednesday, allowing customers to buy, sell and hold bitcoin and other virtual coins using the U.S. digital payments company’s online wallets.

Source: PayPal to allow cryptocurrency buying, selling and shopping on its network


PayPal to Allow Cryptocurrency Buying, Selling and Shopping on its Network ₿₿₿
httpv://www.youtube.com/watch?v=QdOvU6YzNbU&ab_channel=RulesForRebels


Tags: cryptocurrency, PayPal


Oct 19 2020

Hackers hijack Telegram, email accounts in SS7 mobile attack

Category: Hacking — DISC @ 3:12 pm

Hackers with access to the Signaling System 7 (SS7) used for connecting mobile networks across the world were able to gain access to Telegram messenger and email data of high-profile individuals in the cryptocurrency business.

Source: Hackers hijack Telegram, email accounts in SS7 mobile attack


Telegram SS7 attack
httpv://www.youtube.com/watch?v=dkvQqatURdM&ab_channel=ThomasBrewster


Oct 15 2020

Confirmed: Barnes & Noble hacked, systems taken offline for days, miscreants may have swiped personal info

Category: Data Breach,Security Breach — DISC @ 8:44 am

Nook, line and sinker: Servers restored from backups, punters unable to download purchased e-books

Source: Confirmed: Barnes & Noble hacked, systems taken offline for days, miscreants may have swiped personal info


Oct 12 2020

Microsoft and others orchestrate takedown of TrickBot botnet

Category: Botnet — DISC @ 9:41 pm

FS-ISAC, ESET, Lumen’s Black Lotus Labs, NTT, Symantec, and the Microsoft Defender team participated in the takedown.

Source: Microsoft and others orchestrate takedown of TrickBot botnet | ZDNet


Microsoft takes action against Trickbot ransomware attacks
httpv://www.youtube.com/watch?v=39MFGABNf2U&ab_channel=CBCNews%3ATheNational

Tags: botnet, TrickBot


Oct 09 2020

So you thought your personal data was deleted? Not so fast

Category: Information Privacy — DISC @ 4:37 pm

Here’s why it may be impossible to delete your personal information from Houseparty and other social media services – despite privacy legislation!

Source: So you thought your personal data was deleted? Not so fast | WeLiveSecurity


How to erase your iPhone — Apple Support
httpv://www.youtube.com/watch?v=zX4xvkJDHVw&ab_channel=AppleSupport


Oct 08 2020

Massachusetts school district shut down by ransomware attack

Category: Ransomware — DISC @ 11:13 pm

The Springfield Public Schools district in Massachusetts has become the victim of a ransomware attack that has caused the closure of schools while they investigate the cyberattack.

Source: Massachusetts school district shut down by ransomware attack


FBI warning schools to create a ransomware attack plan
httpv://www.youtube.com/watch?v=riLtsU9IKiI&ab_channel=News5Cleveland


Oct 06 2020

HP Printer Bug Bounty Expands To Include Cartridge Security

Category: cyber security — DISC @ 11:06 pm

Including HP Official Ink and Toner cartridge security, HP announced rewards up to $10,000 under the new printer bug bounty program.

After pioneering a bug rewards program for printer security, HP takes another step in this direction. As announced, HP has expanded its bug bounty program for printers to include cartridge security vulnerabilities.

Source: HP Printer Bug Bounty Expands To Include Cartridge Security

Tags: Bug Bounty, Cartridge Security


Oct 05 2020

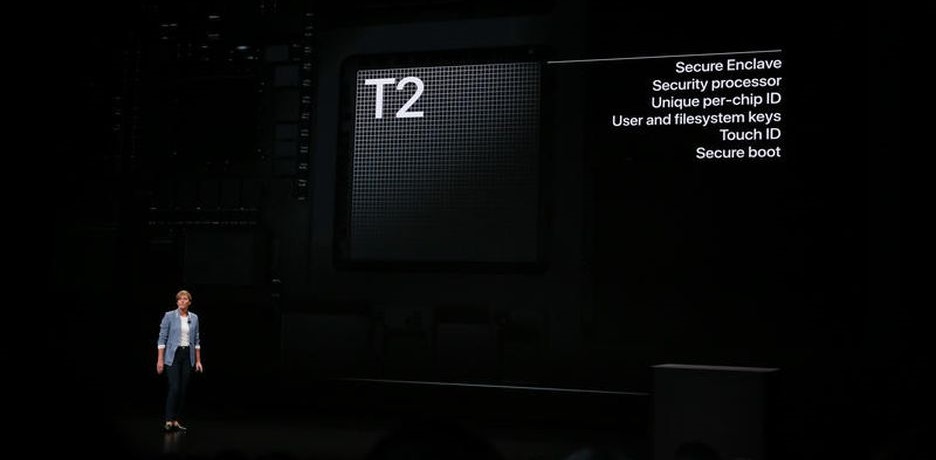
Hackers claim they can now jailbreak Apple’s T2 security chip

Category: Jail break — DISC @ 10:54 pm

Jailbreak involves combining last year’s checkm8 exploit with the Blackbird vulnerability disclosed this August.

Source: Hackers claim they can now jailbreak Apple’s T2 security chip | ZDNet


How to Disable T2 Security
httpv://www.youtube.com/watch?v=rzjXgPmVtdQ


👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet

Download a Security Risk Assessment Steps paper!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email


Oct 04 2020

Clinical Trials Hit by Ransomware Attack on Health Tech Firm

Category: Ransomware — DISC @ 9:53 pm

No patients were affected, but the incident was another reminder of the risks in the increasingly common assaults on healthcare computer networks.

A Philadelphia company that sells software used in hundreds of clinical trials, including the crash effort to develop tests, treatments and a vaccine for the coronavirus, was hit by a ransomware attack that has slowed some of those trials over the past two weeks.

The attack on eResearch Technology, which has not previously been reported, began two weeks ago when employees discovered that they were locked out of their data by ransomware, an attack that holds victims’ data hostage until they pay to unlock it. ERT said clinical trial patients were never at risk, but customers said the attack forced trial researchers to track their patients with pen and paper.

Source: Clinical Trials Hit by Ransomware Attack on Health Tech Firm


Clinic.al Trials Hit by Ransomware Attack on Health Tech Firm
httpv://www.youtube.com/watch?v=9wYhmwTtZ3w&ab_channel=NewsHotDailyc


👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet

Download a Security Risk Assessment Steps paper!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email


Oct 02 2020

The Cybersecurity Maturity Model Certification (CMMC)

Category: Cyber maturity — DISC @ 1:32 pm

CMMC – A pocket guide | Available now for pre-order 📢

Suitable for senior management and the C-suite, general or legal counsel, IT executives, IT organizations, and IT and security students, this pocket guide will give you a solid introduction to the CMMC and its requirements.

A clear, concise primer on the CMMC (Cybersecurity Maturity Model Certification), this pocket guide:

  • Summarizes the CMMC and proposes useful tips for implementation
  • Discusses why the scheme has been created
  • Covers who it applies to and why being non-compliant will result in missed business opportunities
  • Highlights the requirements for achieving and maintaining compliance

Available for pre-order! Buy today and we’ll email you as soon as The Cybersecurity Maturity Model Certification (CMMC) – A pocket guide becomes available on 11/10/2020. Buy Now


Tags: CMMC


« Previous Page — Next Page »