DISC InfoSec: A reliable information security solutions tailored to individual business needs and our mantra is securing the business
Infosec books | InfoSec tools | InfoSec services
InfoSec Compliance & AI Governance For over 20 years, DISC InfoSec has been a trusted voice for cybersecurity professionals—sharing practical insights, compliance strategies, and AI governance guidance to help you stay informed, connected, and secure in a rapidly evolving landscape.

Jan 05 2023
Jan 05 2023
According to a post on a well-known hacker forum, Volvo Cars has experienced a new data breach, with stolen information allegedly being made available for sale.
Anis Haboubi, a French cybersecurity expert, was the first to discover that a threat actor was seeking to sell data purportedly taken from Volvo Cars on a well-known hacking site.

On December 31, 2022, a forum member operating online with the moniker IntelBroker reported that VOLVO CARS had been the target of a ransomware attack. He alleges that the Endurance Ransomware gang attacked the company and stole 200GB of private information that is now being sold.
The seller mentioned that he doesn’t demand a ransom because he thinks the victim won’t pay it.
“The company has not been approached with a ransom demand. Based on the information available, the company does not currently see an impact on its business or operations”, according to a Volvo representative.
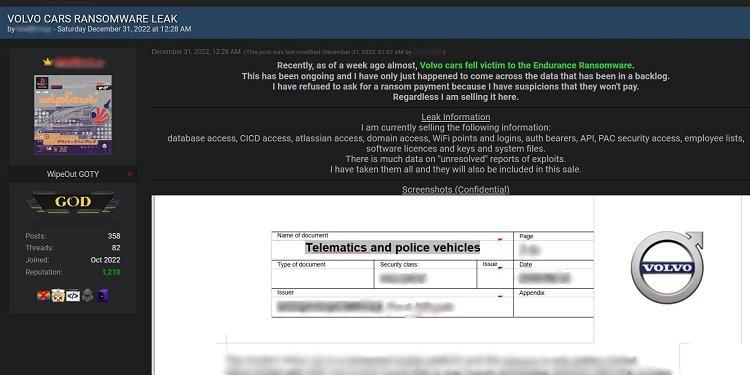
IntelBroker is offering the relevant data for $2500 in Monero, and he shared a number of screenshots as evidence of the hack. He forbids any escrow, which is a highly suspicious situation.
According to reports, the leak included sensitive data like access to several of the company’s databases, WiFi logins and points, employee listings, software keys, and other private data.
“I am currently selling the following information:
Database access, CICD access, Atlassian access, domain access, WiFi points, and logins, auth bearers, API, PAC security access, employee lists, software licenses, and keys and system files.” reads the announcement on the hacking forum.
“There is much data on “unresolved” reports of exploits. I have taken them all and they will also be included in this sale.”
It’s notable that the attacker shared screenshots of allegedly stolen data that indicate details about vehicles the company sells to law enforcement agencies, especially in Europe.
Threat actors have set a relatively low price of $2,500 for the dataset, indicating that the data may not be as sensitive as the seller would want.
If genuine, this would be Volvo’s second security compromise in less than 18 months. The company claimed that a “small portion” of its R&D assets had been taken during the breach in late 2021.
Hence, it’s unclear at this moment whether the seller is seeking to sell information from the 2021 data breach or if there has been a new data leak. Some users of the same hacker site said that since last week, the company’s unsecured Citrix access has been exposed online.
Security researchers released their car hacking research discussing vulnerabilities affecting millions of vehicles, and lots of different car companies such as Kia, Toyota, BMW, Rolls Royce, Ferrari, Ford, and many more. If an attacker were able to find vulnerabilities in the API endpoints that vehicle telematics systems used, they could honk the horn, flash the lights, remotely track, lock/unlock, and start/stop vehicles, completely remotely. Their goal was to find vulnerabilities affecting the automotive industry. This write-up details their work exploring the security of telematic systems, automotive APIs, and the infrastructure that supports them. Details: https://samcurry.net/web-hackers-vs-the-auto-industry/

Infosec books | InfoSec tools | InfoSec services
Dec 16 2022
Microsoft revised the severity rate for the CVE-2022-37958 vulnerability, the IT giant now rated it as “critical” because it discovered that threat actors can exploit the bug to achieve remote code execution.
The CVE-2022-37958 was originally classified as an information disclosure vulnerability that impacts the SPNEGO Extended Negotiation (NEGOEX) security mechanism.
The SPNEGO Extended Negotiation Security Mechanism (NEGOEX) extends Simple and Protected GSS-API Negotiation Mechanism (SPNEGO) described in [RFC4178].
The SPNEGO Extended Negotiation (NEGOEX) Security Mechanism allows a client and server to negotiate the choice of security mechanism to use.
The issue was initially rated as high severity because the successful exploitation of this issue required an attacker to prepare the target environment to improve exploit reliability.
Microsoft addressed the vulnerability with the release of Patch Tuesday security updates for September 2022.
IBM Security X-Force researcher Valentina Palmiotti demonstrated that this vulnerability is a pre-authentication remote code execution issue that impacts a wide range of protocols. It has the potential to be wormable and can be exploited to achieve remote code execution.
“The vulnerability could allow attackers to remotely execute arbitrary code by accessing the NEGOEX protocol via any Windows application protocol that authenticates, such as Server Message Block (SMB) or Remote Desktop Protocol (RDP), by default.” reads the post published by IBM. “This list of affected protocols is not complete and may exist wherever SPNEGO is in use, including in Simple Message Transport Protocol (SMTP) and Hyper Text Transfer Protocol (HTTP) when SPNEGO authentication negotiation is enabled, such as for use with Kerberos or Net-NTLM authentication.”
Unlike the CVE-2017-0144 flaw triggered by the EternalBlue exploit, which only affected the SMB protocol, the CVE-2022-37958 flaw could potentially affect a wider range of Windows systems due to a larger attack surface of services exposed to the public internet (HTTP, RDP, SMB) or on internal networks. The expert pointed out that this flaw can be exploited without user interaction or authentication.
IBM announced it will release full technical details in Q2 2023 to give time organizations to apply the security updates.

Mastering Windows Security and Hardening: Secure and protect your Windows environment from intruders, malware attacks, and other cyber threats
Dec 14 2022
Original post at https://cybernews.com/security/millions-ip-cameras-exposed/
When you spy on your neighborhood or your cafe customers, do you wonder if someone is watching Big Brother – you, in this case?
Businesses and homeowners increasingly rely on internet protocol (IP) cameras for surveillance. All too often, this gives them a false sense of security: when in fact, threat actors can not only access and watch your camera feed but exploit the unsecured device to hack into your network.
New research by Cybernews shows an exponential rise in the uptake of internet-facing cameras. After looking at 28 of the most popular manufacturers, our research team found 3.5 million IP cameras exposed to the internet, signifying an eightfold increase since April 2021.
While the default security settings have improved over the review period, some popular brands either offer default passwords or no authentication, meaning anyone can spy on the spies.
What is more, the overwhelming majority of internet-facing cameras are manufactured by Chinese companies. And while cosmetic security measures are in place, security leaders have long warned that technologies produced by Chinese companies can be exploited by China’s government.
Surge in internet-facing cameras
When we last did similar research, we discovered over 400,000 internet-facing cameras online. This time, the Cybernews research team found 3.5 million internet-facing cameras.
Since this is a convenient and cheap tool to surveil anything from a parking lot, a warehouse, your doorstep, or even monitor your child’s sleep using a baby camera, it’s not surprising to see a surge in IP camera usage.
While not surprising, the trend is worrying since internet-connected devices might be vulnerable to attacks – threat actors can gain access to the camera’s live feed, collect sensitive data, and launch further attacks on the network.
It is worrying that all analyzed brands have at least some models that allow users to keep default passwords or have no authentication setup whatsoever.
The reign of a Chinese brand
Most of the public-facing cameras we discovered are manufactured by the Chinese company Hikvision: the Cybernews research team found over 3.37 million of its cameras worldwide.
According to our researchers, they have the necessary security practice in place as they force users to create their unique passwords during an initial setup process. Nevertheless, the global popularity of Hikvision cameras has raised some eyebrows and, as is typical with China-manufactured technology, it and other companies are facing a backlash from Western governments.
Recently, the UK parliament instructed government agencies to cease the deployment of Chinese equipment, including surveillance cameras, on to sensitive sites, saying the technology is produced by companies subject to the National Intelligence Law of the People’s Republic of China.
Hikvision’s website advertised optional demographic profiling facial analysis algorithms, including gender, race, ethnicity, and age. Following an investigation by the Guardian, the ad was removed.
In November, the US Federal Communications Commission banned authorizations for Chinese telecommunications and video surveillance equipment, saying that Huawei, ZTE, Hytera, Hikvision, and Dahua are “deemed to pose a threat to national security.”

Most insecure brands
Most analyzed brands (96.44% of the discovered cameras) force users to set passwords or generate unique default passwords on the newest models and firmware versions. While this is a good trend, it doesn’t mean that all the cameras are safe since the lion’s share of these cameras is probably comprised of older models or those operating with outdated firmware using default or weak passwords.
Anyhow, this is a fundamental shift in the trend since last year, when we found that only 5.25% of analyzed cameras asked users to set their passwords.
As of today, 3.56% (127,000) of all analyzed cameras recommend changing the default password but do not enforce it. Sometimes, they don’t even mention it in the initial setup process, with the recommendation being on a blog post instead.
Even more concerning is that over 21,000 cameras did not have any authentication setup, allowing anyone to access them, leaving owners at risk of cyberattack.

According to the research, most public-facing cameras that might be using default credentials are operational in the United States, where we identified over 458,000 such devices.
Germany, which took second place in our research last year, covering over 50,000 cameras, didn’t even make it into the top 10 countries this time.
The second most affected country is Vietnam, with nearly 365,000 cameras, followed by the UK (nearly 250,000).
Visual here: Top 10 Countries with the most internet-connected cameras that could be using default credentials:

If you want to know how to secure your IP camera give a look at the original post published on CyberNews:
About the author: Jurgita Lapienytė, Chief Editor
A Security System for a Digital Camera: Using Cryptographic Secrecy in Steganographic Embedding
#InfoSecTools and #InfoSectraining
Ask DISC an InfoSec & compliance related question
Dec 06 2022
The majority of major automobile manufacturers have addressed vulnerability issues that would have given hackers access to their vehicles to perform the following activities remotely:-
SiriusXM, one of the most widely used connected vehicle platforms available on the market, has a critical bug in its platform that affects all major vehicle brands.
There is a particular interest among security researchers in the area of connected cars, like Yuga Labs’ Sam Curry. In fact, he’s the one who was responsible for discovering a security hole in the connected cars of major car manufacturers during his routine research.
There are a number of car manufacturers who use Sirius XM telematics and infotainment systems as a part of their vehicle technology.
Here below we have mentioned the brands’ names that are affected due to this critical bug in SiriusXM:-
During the process of analyzing the data, it was found that there is a domain (http://telematics(.)net) that is used during the vehicle enrollment process for the remote management of Sirius XM.
The flaw is associated with the enrollment process for SiriusXM’s remote management functionality which results in the vehicle being tampered with.
There is not yet any technical information available about the findings of the researchers at the present time, since they haven’t shared anything in detail.
Upon further analysis of the domain, it becomes apparent that the Nissan Car Connected App is one of the most plentiful and frequently referenced apps in this domain.
In order for the data exchanged through the telematics platform to be authorized, the vehicle identification number (VIN) only needs to be used. The VIN of the vehicle can therefore be used to carry out a variety of commands by anyone who knows the number.
The next step would be to log in to the application later on, and then the experts examined the HTTPS traffic that came from a Nissan car owner.
Researchers discovered one HTTP request during the scan in which they conducted a deep analysis.
It is possible to obtain a bearer token return and a “200 OK” response by passing a VPN prefixed ID through as a customerID in the following way:-

Using the Authorization bearer in an HTTP request, researchers attempted to obtain information about the user profile of the victim and, as a result, they successfully retrieved the following information:-
In addition to this, the API calls used by SiriusXM for its telematics services worked even if the user did not have an active subscription with SiriusXM.
As long as the developers or owners are not involved in the process of securing a vulnerable app, it is impossible to guarantee the security of that app. This is why they should be the only ones who can issue security updates and patches.
Here below we have mentioned the recommendations made by the security analysts:-

The Car Hacker’s Handbook: A Guide for the Penetration Tester
Nov 18 2022
The online world has never been risk-free and in 2022 the risks posed by cybercriminals are a threat to all internet users. As scams and phishing methods become more complex there is a greater need for the individual to adopt a range of best practices to protect their personal information.
Cybercriminals can target both individuals and businesses using a wide range of methods: malware can be activated by clicking on malicious links; personal details can be harvested simply by visiting unsecure sites.
Whether you like to surf the internet for fun and recreation, use it as a platform for online trading, or buy a range of products and services, staying safe online should always be a priority. It is a sobering fact that thousands of pieces of malware are created every day.
Stay safer online by following these three top tips.
Millions of people around the world now regularly trade online and increasingly that trade is in cryptocurrencies such as Bitcoin. With a wide range of cryptocurrencies now available, it is more important than ever to check that the site you trade on is secure.
As a rule, you should only trade on sites that feature the padlock icon in their web address, such as can be seen at OKX. This padlock icon proves that the site is secure and uses SSL encryption to ensure that any financial or personal information is transmitted safely.
It is also good practice to look at reviews from trading platforms. Customer experiences of using these sites can be a valuable source of information on the security of a platform. When trading online or undertaking any type of internet purchasing activity, it is also important to remember not to use unsecured networks.
Surfing in coffee shops and shopping malls can be an attractive proposition but should be avoided whenever any transactions are taking place; otherwise, a cybercriminal could easily pose as a contact from a website you have visited – leaving you open to phishing attacks in the future.
Whilst most people realize the value of having strong passwords across all the sites they use, it is still surprising how many people do not adhere to this best practice. Many consumers use the same passwords across numerous platforms and sites or use exceptionally weak passwords that can be cracked with a minimum amount of effort.
Today, search engines can suggest strong passwords and store them securely. This method can make consumers safer online whilst also freeing the need to memorize complex passwords. Put simply, if you use weak or repetitive passwords across sites, you are making it easy for a cybercriminal to harvest your personal details or hack your accounts.
Another common practice that tends to be overlooked by millions of web visitors is to keep applications and devices up to date with the latest firmware. It is vitally important to check for system and firmware updates on a regular basis. Whilst many updates offer stability improvements or bug fixes, they often contain the latest security updates that keep devices and applications more secure.
Running software or operating systems that do not have the latest patches leaves them far more vulnerable to attack, so make a point of checking for updates across your devices on a regular basis to ensure that you benefit from the latest security features.
In summary, follow the above advice to avoid falling victim to one (or more) of the 300,000 pieces of malware that are created every day.

HOW TO STAY SAFE ON SOCIAL MEDIA: Social Media Dos and Don’ts
Nov 15 2022
As we continue to rely on technology more and more, we should also be increasingly thinking about protection. According to Cyber Security Hub, two-thirds of companies are spending more on cybersecurity in 2022 than last year — a pattern that should only continue.
On the heels of National Cybersecurity Awareness Month, it is the perfect time for business leaders and organizations to consider the cybersecurity safeguards they use to protect sensitive information. Cybersecurity can be a complex task for many organizations. Businesses, educational institutions and government entities often struggle to navigate the available options. Aside from IT professionals, finding the right solution requiressubject matter experts, a group of leaders who represent different lines of business, C-suite representatives and a thorough risk assessment to determine where to strike a balance between security and productivity.
Security is a constant discipline of due care and due diligence over time. It requires a mindset shift for employees and extends far beyond computers. Printers, scanners, fax machines, document management systems and other hardware and software solutions must contain the latest security features as well. While updating these devices may not be top of mind, neglecting them can pose a serious threat to your organization if compromised.
If you are just getting started, or need a refresher on cybersecurity, here are some of the first steps you should take:
Layered security Standard Requirements
Nov 08 2022
Recently, the Forgepoint team announced a new alliance with global banking leader Santander to increase cyber investment worldwide, specifically in Europe, Israel, and Latin America. Santander will also be the primary investor in Forgepoint’s next fund, slated for 2023, with a nearly $300 million goal.
This was the perfect reason to connect with Alberto Yépez, the co-founder and Managing Director of Forgepoint Capital. In this Help Net Security interview, the former Trident Capital leader offers insight into innovation in the cybersecurity market, M&A activity, pitching to VCs, and more.
Innovation is always driven by a need. What does the market need right now? What do customers need? How can the ecosystem adapt to serve those needs? Innovation provides solutions that expedite answers to problems, and successful businesses are built when they do this.
Today’s rapidly changing macro environment combined with the demands of an evolving threat landscape makes this the perfect time for company building. Now, businesses that did not satisfy needs will no longer survive, while those that do will thrive.
While we may see a wave of consolidation, which is expected given the amount of venture financing committed to cybersecurity in the last few years, organizations now face the decision to either raise more funding in a challenging environment as valuations normalize or seek an acquisition, as growth investors shift away due to market conditions.
Public and larger private companies will continue to buy startups that are innovative and leading-edge, filling gaps in their current offerings to offer wider, more integrated solutions. These companies provide new capabilities that address new threats and give them access to high-growth market segments while helping them stay relevant.
Ultimately, M&A activity will have a positive impact on the industry because large enterprise customers benefit from integrated solutions that reduce the total cost of ownership of these solutions. Customers also benefit from these integrated services as they help meet critical enterprise needs and ease the strain caused by the global shortage of cybersecurity professionals.
I advise founders to take a long-term mindset and remember that fundraising is a people-driven industry. While initial timelines may achieve certain funding goals, securing funding means building real relationships and creating a network of trusted partners. Taking the time to do this well will have an immediate impact upon your success.
In a competitive fundraising environment, VCs have to make quick decisions. To do that, we depend on both our own experience, as well as the experiences of our network and our close connections who we can rely on to provide strong counsel. An introduction to a startup from a trusted friend with relevant expertise and background is one of the most productive relationship builders – for both sides.
These trusted relationships will open the right doors for founders, then it’s all about how you tell your story to the VC. The clarity and direction of your thinking can tell a lot about the company’s market position and opportunity you’re out to tackle, as well as your future priorities. Here, introspection and self-awareness shine.
Having a people-driven mindset is helpful because it has multiple natural side benefits. Networking requires us to build relationships with individuals beyond the short-term, casting a net that can include VCs as well as future startup customers or potential hires. Networking with VCs may also suggest you meet with others and while these introductions may not be directly about fundraising, they can help you get exposure to potential customers, team members, and advisors for input on your tech, business, and model. This leads to opportunities to learn and refine your approach from diverse perspectives.
The traits that I find most important in entrepreneurs are subject matter expertise and the know-how to execute. Prior experience as an entrepreneur with a track record of building commercial offerings successfully commercialized and adopted by customers will allow for deep domain knowledge of the sector that they’re working in, which is very important when scaling organizations. In my experience, serial entrepreneurs typically have a leg up compared to first-timers.
That being said, all of this doesn’t matter if an entrepreneur doesn’t know how to lead. The ability to recruit and retain high quality talent, and then continuing to work with them to grow as the organization expands is a very important trait that is paramount to the success of any organization.
Forgepoint partners with emerging companies from Croatia to Mexico, Madrid to Tel Aviv, and has been actively tracking thousands of companies worldwide. It is abundantly clear that the cyber ecosystems across Europe, Latin America and Israel have an incredibly rich talent pool, strong demand signal and robust capital accessibility – and that cybersecurity is a growing, global problem.
While the current macro environment is challenging, organizations looking to get funding in the US will succeed if their product and complete offering solve a demonstrated need in the market. When it comes down to it, it’s all about five fundamentals:
Israeli and European companies trying to get funding in the US should be able to clearly speak to these fundamentals, demonstrating how they’ll incorporate the US into their go-to-market and growth plans as they partner with investors, form channel alliances, and further develop their businesses. Thinking this through can be enormously helpful in identifying which VCs to approach – which will bring value and help augment your business.
Start-Up Secure: Baking Cybersecurity into Your Company from Founding to Exit

Oct 13 2022
From the basics to advanced techniques, here’s what you should know.
Cybersecurity has been compared to a never-ending game of whack-a-mole, with an ever-changing cast of threats and threat actors. While the attacks that make headlines may change from year to year, the basic fact remains: Any network, no matter how obscure the organization it supports, most likely will come under attack at some point. Thus, attaining and maintaining a strong security posture is of critical importance for organizations of any size.
An organization’s security posture, however, is constantly changing. Employees join or leave the company; endpoints are added and discarded; and network and security technologies are deployed, decommissioned, configured, and updated. Each change in network elements can represent a potential attack vector for malware and other threats.
That’s why security teams should review their security processes periodically and keep aligned with new developments in defensive and offensive testing and modeling. Doing so can help move the needle on security maturity from the most basic to an advanced, much stronger security posture, and from a reactive to a proactive model.
The first step most IT organizations undertake is vulnerability scanning, which seeks out potential weaknesses in the network and endpoints that could be exploited by attackers. There’s a wide variety of scanners available as open source or commercial software, as managed services, and on cloud platforms like AWS and Alibaba. Some of the more popular scanners include Nessus, Burp Suite, Nmap, and Qualys, though each has its own area of focus. Several offer automatic patch remediation, as well.
Another consideration is whether to perform an external scan — which can discover potential vulnerabilities that hackers can exploit — or internal scanning that can find potential paths attackers would take once inside the network. Many, if not most, IT teams will do both.
While vulnerability scanning is relatively easy to use, it’s not the end-all, be-all of a security strategy. For example, scanning might not detect subtle misconfigurations or the more complicated attack paths that advanced persistent threats (APTs) might take. They’re also often prone to false positives and must be updated consistently.
Overall, though, vulnerability scanning is an important baseline step. Once it’s running well, the next step is penetration testing.
Penetration testing typically entails human ethical hackers who attempt to gain access to the network interior, much as an outside hacker would. Here, too, there’s a wide variety of tools and services available — many of the aforementioned vulnerability scanners offer tools that can be used in pen testing. Others include Metasploit, Kali Linux, Cobalt.io, and Acunetix.
Run periodically, pen testing can uncover weaknesses that aren’t found by vulnerability scanners. Furthermore, human-managed pen testing can explore more complex pathways and technique combinations that hackers increasingly leverage to exploit victims, such as phishing.
Not surprisingly, the biggest trends impacting networking and cybersecurity are essentially the same trends noted in penetration testing this year: rampant ransomware attacks, the newly distributed workforce, and the rise of Web applications and cloud usage to support remote workers. Each of these trends will require thoughtful consideration in choosing tools and designing plans for penetration testing.
While penetration testing can provide a great deal of benefit, it’s a good idea to periodically review the wealth of information on best practices available online.
The third step in the quest for security maturity is usually the establishment of a red team that will manually attempt to attack and penetrate the organization’s security defenses. This may be a completely separate team, or it may be closely allied with the blue team (the defenders) in a combination called a purple team. As another option, some vendors offer red-team services on a subscription or one-off basis.
A red team will imitate the tactics, techniques, and procedures (TTPs) that attackers use — which usually turns up more points of vulnerability than penetration testing can reveal. The blue team can then begin to resolve these weaknesses, further hardening the network against attack.
But too often, red and blue teams devolve into an adversarial relationship that’s counterproductive. It’s also quite expensive to set up a red team, and given the shortage of cybersecurity professionals, it may not be feasible. Therefore, many CISOs are investigating two newer trends: adversary emulation and adversary simulation.
There are vast, freely available libraries of common tactics, techniques, and procedures used during attacks, such as MITRE’s ATT&CK framework. Adversary emulation and simulation leverage these libraries to evaluate security based on intelligence for specific attacks and then simulating the TTPs used.
For example, MITRE developed a sample adversary emulation plan for APT3, an advanced persistent threat that previously targeted mostly US entities. The emulation plan covers three phases from command-and-control setup to initial access; from host compromise through to execution; and data collection through exfiltration. The Center for Threat-Informed Defense has posted other emulation plans.
Adversary emulation lets security teams assess their defenses against real-world attacks. It can also be used to test the security infrastructure’s detection and response rates.
Security vendors are moving beyond simply advocating the concept of MITRE’s ATT&CK and MITRE Shield. Many vendors are leveraging one or both to improve their own products and services. For example, some security vendors map anomalies and events to the ATT&CK framework, making it easier for security teams to respond.
MITRE’s CALDERA also deserves attention. It provides an intelligent, automated adversary emulation system that can be programmed for a specific attack profile and launched into the network to test its defenses. Caldera can also be used to train blue teams on detecting and remediating specific attacks.
There are also open source projects for adversary behavior simulation in development. A few of them of note include Uber’s Metta, Nextron Systems’ APT Simulator, Elastic/Endgame’s Red Team Automation, CyberMonitor’s Invoke-Adversary, and Red Canary’s Atomic Red Team.
Keeping abreast of developments in key security processes is important for security teams as they strive to defend the network against changing threats. By so doing, they can move the organization closer to a far stronger security posture.
Source:
Sep 19 2022
Coalition announced the mid-year update to its 2022 Cyber Claims Report detailing the evolution of cyber trends, revealinig that small businesses have become bigger targets, overall incidents are down, and ransomware attacks are declining as demands go unpaid.
During the first half of 2022, the average cost of a claim for a small business owner increased to $139,000, which is 58% higher than levels during the first half of 2021.
“Across industries, we continue to see high-profile attacks targeting organizations with weak or exposed infrastructure — which has become exacerbated by today’s remote working culture and companies’ dependence on third-party vendors,” said Catherine Lyle, Coalition’s Head of Claims.
“Small businesses are especially vulnerable because they often lack resources. For these businesses, avoiding downtime and disruption is essential, and they must understand that Active Insurance is accessible.”
The good news: both Coalition and the broader insurance industry observed a decrease in ransomware attack frequency and the amount of ransom demanded between the second half of 2021 and the first half of 2022. Ransomware demands decreased from $1.37M in H2 2021 to $896,000 in H1 2022. Of the incidents that resulted in a payment, Coalition negotiated down to roughly 20% of the initial demand.
More good news: Coalition policyholders experienced 50% fewer claims compared to the broader market. The severity of these claims has also declined, with 45% of incidents resolved at no cost. The substantial decrease in overall claims stems from Coalition’s combination of cybersecurity tools, including active monitoring and alerting, access to digital forensics and incident response, and broad insurance coverage.
“Organizations are increasingly aware of the threat ransomware poses. They have started to implement controls such as offline data backups that allow them to refuse to pay the ransom and restore operations through other means,” said Chris Hendricks, Coalition’s Head of Incident Response. “As ransomware is on the decline, attackers are turning to reliable methods. Phishing, for example, has skyrocketed – and only continues to grow.”
Other key findings:

Cybersecurity for Small and Midsize Businesses
Aug 29 2022
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added 10 new vulnerabilities to its Known Exploited Vulnerabilities Catalog, including a high-severity security flaw (CVE-2021-38406 CVSS score: 7.8) impacting Delta Electronics industrial automation software.
According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the identified vulnerabilities by the due date to protect their networks against attacks exploiting the flaws in the catalog.
Experts recommend also private organizations review the Catalog and address the vulnerabilities in their infrastructure.
According to the US agency, Delta Electronics DOPSoft 2 lacks proper validation of user-supplied data when parsing specific project files (improper input validation). An attacker can trigger the flaw to cause an out-of-bounds write and achieve code execution.
It is important to highlight that there are no security patches to fix this issue and that the impacted product is end-of-life.
CISA also added to the catalog a Sanbox Bypass Vulnerability, tracked as CVE-2021-31010 (CVSS score: 7.5), in Apple iOS, macOS, and watchOS.
“In affected versions of Apple iOS, macOS, and watchOS, a sandboxed process may be able to circumvent sandbox restrictions.” reads the advisory.
The other vulnerabilities added to the catalog are:
CISA orders federal agencies to fix these vulnerabilities by September 15, 2022.

CyberWire Inc. (Author)Flash cybersecurity advisories from the US Government. These alerts provide timely technical and operational information, indicators of compromise, and mitigations for current major security threats, vulnerabilities, and exploits. These alerts have been edited and adapted for audio by The CyberWire as a public service.
Free podcast:

Aug 28 2022
As technology advances, so must our ability to use such technology ethically. The rise of AI (artificial intelligence) and big data raises concerns about data privacy and cyber security. ITG have combined their latest titles into one bundle, saving you 20% – ideal for bank holiday reading.
| Digital Ethics Book Bundle Understand the growing social, ethical and security concerns of advancing technology with this new collection: Digital Earth – Cyber threats, privacy and ethics in an age of paranoia Artificial Intelligence – Ethical, social, and security impacts for the present and the future The Art of Cyber Security – A practical guide to winning the war on cyber crime Save 20% when you buy the Digital Ethics Book Bundle online (RRP: £80.85). | 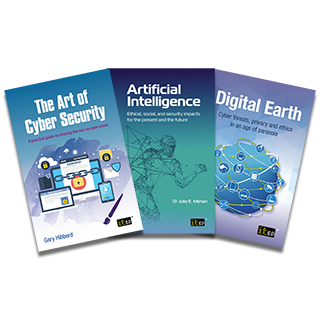 Buy now |
Aug 07 2022
You can choose the course based on your specific needs:
The online courses are suitable both for beginners and experienced professionals.
Learn at your preferred speed from any location at any time.
If you have any questions, feel free to send us an email to info@deurainfosec.com
Aug 03 2022

Whether you are getting ready for back-to-school season, getting new work laptop or fancying a new gamer’s pc, learn the steps to protect your new PC from cyberthreats.
With Windows 11 making headlines for all the right reasons, it could be a great time to invest in a new PC for the family or the home office. But any new household computing device should come with an attendant safety warning. Hackers will be after your data the minute it’s connected to the internet. And they have numerous ways to get it.
That’s why you need to think about cybersecurity even before plugging your machine in and switching it on. Take time out now to refresh your memory and make cyber-hygiene a number one priority.
As soon as you’re connected to the internet, malicious actors will be looking to steal your data, encrypt and hold your machine ransom, lift financial details, secretly mine for cryptocurrency, and much more. They’ll do so via some tried and true methods, which often rely on cracking, stealing or guessing passwords, or exploiting software vulnerabilities. Top threats include:
Phishing: One of the oldest con tricks in the book. Cybercriminals masquerade as legitimate and trustworthy sources (banks, tech providers, retailers etc) and try to persuade users into clicking on links and/or opening attachments in emails. Doing so will take users to a spoofed site requesting that they fill in personal information (like logins and/or address/financial details) or could trigger a covert malware download.
Drive-by downloads and malicious ads: Sometimes merely visiting an infested website or a site running a malicious ad could trigger a malware download. We may think that well-known sites may be less compromised in this way as they are better resourced and can afford enhanced protection. But there have been plenty of counter-example through the years showing that it’s not always the case. That’s why its essential to invest in security software from a reputable provider and ensure that your browser’s security settings are correct.
Digital skimming: Hackers may also compromise the payment pages of e-commerce sites with malware designed to silently harvest your card data as it is entered. This is difficult to guard against as the issue is with the provider. However, shopping with better-known sites can reduce risk.
Malicious apps and files: Cybercriminals also hide malware inside legitimate-looking applications and downloads. Many of these are posted to online forums, P2P sites, and other third-party platforms. That’s why it makes sense to download only from trusted sources, and to use an effective security software tool to scan for malicious software.
Many of the below steps may be taken care of automatically by your PC manufacturer/Microsoft, but it pays to dig a little deeper to make sure all the settings are as secure as you need them to be. Here are our top 10 tips for computer safety:
It goes without saying that, even by following these best practices, you could still be at risk when browsing online. Always proceed with caution, don’t reply to unsolicited emails/online messages, and ensure device encryption is switched on.
by Phil Muncaster, ESET
https://wordpress.com/read/blogs/19067844/posts/17162
Internet attack on computer systems is pervasive. It can take from less than a minute to as much as eight hours for an unprotected machine connected to the Internet to be completely compromised. It is the information security architect’s job to prevent attacks by securing computer systems. This book describes both the process and the practice of assessing a computer system’s existing information security posture. Detailing the time-tested practices of experienced security architects, Securing systems explains how to deliver the right security at the right time in the implementation lifecycle.
Aug 02 2022

#InfoSecTools and #InfoSectraining
Ask DISC an InfoSec & compliance related question
Jul 28 2022
State of Cybersecurity 2022 – via ISACA

State of Cybersecurity 2022, Global Update on Workforce Efforts, Resources and Cyberoperations reports the results of an eighth annual global study that looks at the following topics and more:
See what your peers have to say and how your organization’s challenges, actions and priorities compare to other companies around the world.
Get your free copy by completing the form on ISACA site.
Jun 02 2022
Cybersecurity is required to be a dynamic industry because cybercriminals don’t take days off. Cybersecurity professionals must be innovative, creative, and attentive to keep gaining the upper hand on cybercriminals. Unfortunately, there are millions of unfilled cybersecurity job openings around the globe.
The problem of not enough cybersecurity professionals is exacerbated by a lack of diversity in the sector. There is a disproportionately low ratio of women to men within the entire technology industry. In the science, technology, engineering and math (STEM) industries, women make up only 24% of the workforce, and while this has increased from just 11% in 2017, there is clearly still a sizeable disparity.
The cybersecurity industry is performing only marginally better than STEM, with women making up roughly 24% of cybersecurity jobs globally, according to (ISC)².
There is also a parallel trend here: women have superior qualifications in cybersecurity than their male counterparts. Over half of women – 52% – have postgraduate degrees, compared to just 44% of men. More importantly, 28% of women have cybersecurity-related qualifications, while only 20% of men do. This raises one important point, which is that women feel that they must be more qualified than men to compete for and hold the same cybersecurity roles. The industry is, therefore, losing a significant pool of talent because of this perception. Untapped talent means less innovation and dynamism in the products and services businesses offer.
Unfortunately, the challenges for women do not appear to stop once they enter the cybersecurity workforce. Pay disparity continues to blight the industry. Women reported being on smaller salaries at a higher proportion than men. 17% of women reported earning between $50,000 and $99,000 compared to 29% of men. However, there are signs that this disparity in pay is closing. For those in cybersecurity who earned over $100,000, the difference in percentage between men and women was much closer. This is encouraging and shows that once women are in the industry, they can enjoy as much success as men.
Nevertheless, reaching these higher levels of the cybersecurity industry is far from straightforward for women at present. It is an unavoidable fact that women still struggle to progress as easily compared to male counterparts. A key reason for this is cultural: women are disinclined to shout about their achievements, as such they regularly go unnoticed when promotions and other opportunities come round.
The cybersecurity industry is starting to embrace diversity in the workforce, but there is a long way to go before women are as valued in cybersecurity as men. With the current skills deficit hampering the growth of cybersecurity providers, this is a perfect opportunity for the industry and individual providers to break the bias and turn to women to speed up innovation and improve defense against cybercriminals.

Women Know Cyber: 100 Fascinating Females Fighting Cybercrime
Mar 09 2022
Mar 04 2022
When CISOs, CIOs, CTOs, security engineers, security analysts and security architects were asked to rank the primary capabilities of a traditional SIEM according to how satisfied they were with those capabilities, an interesting picture emerged. The survey results indicated that every primary capability of traditional SIEM solutions, at best, only somewhat met the majority of users’ needs. Some capabilities were irrelevant to many users. This tepid level of satisfaction is what drove many security teams to undertake the effort to build their own security monitoring tools.
Less than 25% of the respondents believed that their SIEM covered more than 75% of their security-relevant data. Nearly 17% responded that their existing platform covered less than a quarter of their data.
Furthermore, when asked if they believed their current SIEM platform were capable of handling the volume of security data their organization will generate in the future, a third of the respondents said they expected their existing platform to keep falling behind.
These results underscore the risks security teams (and their organizations) are forced to tolerate due to the cost and overhead required to bring high volumes of security-relevant data into traditional SIEM platforms. Without full visibility into all necessary data, security teams will undoubtedly have blind spots that impede their ability to protect their organizations.
OK, so what can they do instead? Well, a cloud-native architecture capable of ingesting, normalizing and analyzing terabytes of data per day cost-effectively is necessary to keep up.
Security professionals are well aware of the static nature of traditional SIEM platforms. Many believe they pay too much for the capabilities provided and are concerned about what the future holds.
SIEMs were designed over ten years ago when the world was a very different place. The technology hasn’t evolved its approach to keep up with the needs of cloud-scale environments. Adequate security today depends on full visibility into security-relevant data, structured, scalable data lakes, cloud-native workflows and fast detection and response times. Security teams need a modern approach to security monitoring built for the cloud-first world.
Security Information and Event Management (SIEM) Implementation
Feb 28 2022