Mar 18 2023

How CISOs Can Work With the CFO to Get the Best Security Budget

Category: CISO,vCISO — DISC @ 11:02 am

CISOs can and should push back when they’re presented with budget costs that affect the business. Here’s how.
The CISO challenge of budgeting – Intelligent CISO

Today’s enterprise security executives face situations that could really hurt the company’s bottom line. Security teams are trying to modernize security operations in an increasingly porous network environment with ever more sophisticated threats. There are also economic pressures from layoffs, budget cuts, and restructuring.

Even worse, CFOs have heard from CISOs the doom-and-gloom predictions of the potential fiscal disaster of data breaches so often that it’s no longer resonating with them.

The doomer scenario is not hypothetical — global compliance requirements and privacy regulations drive the cost of a breach even higher than just the technical costs. However, CFOs and other C-level executives have heard these warnings so often now that it’s just background information that doesn’t drive their decision making.

Is there a more effective way to help the CFO understand why security needs to be far better funded? Yes: Present the CFO with a shared-risk scenario.

Setting Protection Priorities

Allan Alford, who was a CISO in various industries including technology, communications, and business services before morphing into a CISO consultant, says CISOs should use a different approach to describe cybersecurity issues to the CFO. They should begin by asking the CFO to identify the six most important strategic elements of the business — possibly including the supply chain, manufacturing operations, sensitive future product plans, etc. — then detail their plans for protecting each of those critical areas, Alford says.

The CISO can present the situation to the CFO in the following manner: “Thanks for sharing those priorities. Now, you are saying we need to cut the security budget by 37%. Given the state of the economy in our sectors, that is completely understandable. To make the cuts possible, can you tell me which of these six areas I should stop protecting? We will also need to bring in the line-of-business executive so that you can explain how these changes will impact that area.”

Historically, CISOs, CSOs, CROs, and other security-adjacent executives have been good soldiers, accepting the CFO-ordered cuts and deciding where changes have to be made, Alford says. This conflicts with the CISO’s job: to protect the company — including all intellectual property and all assets.

If the CFO decides to cut back security funding, they need to work with the COO, the CEO, the board, and other senior executives to decide which operations they can afford to not protect. It should not be left to the CISO to make those calls or defend the choices.

In fairness, the decision is rarely black-and-white. But if the CISO positions the budget decisions in this manner, the CFO will see the actual business impact the reductions would have. When the CFO is forced to decide where the cuts will happen and to choose which top-priority division is left undefended, the conversation shifts, Alford says. The CISO can say to the CFO, “We’ll jointly figure out what risks are tolerable, but make no mistake: A 37% cut will put various units at extreme risk. Can the business afford that deep a cut in our defenses?”

The CISO can present cost-effective alternatives to reduce security defenses, rather than eliminating them entirely. Now there is the possibility of negotiating a smaller budget cut. Maybe that 37% cut becomes a 23% cut.

Negotiating as a Group

The conversation shouldn’t begin and end with the CFO, says Daniel Wallance, an associate partner with McKinsey. It should involve the board’s risk committee, the CEO, the COO, and other colleagues who have a role in security spending, such as the CIO and the CRO.

“There is also spend coming from risk management [and] compliance on top of IT. I would engage those functions, as they have shared [security] responsibility and they may actually have dedicated resources,” Wallance says. “I need this to not be a one-on-one conversation. I want to make it a group.”

These conversations with other security executives should happen before and after the CFO meeting, but not during.

The CISO needs to meet with the other security players before meeting with the CFO to learn what overlaps and redundancies currently exist. The CISO also needs to know how much budget flexibility those other executives are willing to offer. That will be crucial information to have while working with the CFO. After meeting with the CFO, the CISO can go back to the other executives and see what they can negotiate as a group.

The actual CISO-CFO meeting should be just the two executives, to avoid making the CFO feel ganged up on. The discussion should be as friendly as possible to allow for reasonable compromises.

Involving the board’s risk committee is critical, as it is ultimately the board’s role — working with the CEO — to dictate the company’s risk tolerance. If the CFO’s requested budget reductions conflict with that risk tolerance, the board needs to know about it.

“The CISO should be meeting with the risk committee regularly,” Wallance says. “The business may not understand the implications of the budget cut. The CFO is not the only person at issue here.”

Adapting to Market Conditions

Larger trends in the economy also affect CISO budgetary needs.

There is a realistic existential threat to cyber insurance, the net that CFOs have relied on for more than 20 years. Lloyds of London said that it would stop covering the losses from state actor attacks, which is problematic given how difficult it is to prove an attack’s origin and who funded it. Insurance giant Zurich warned it might abandon cyber insurance entirely. And an Ohio Supreme Court decision raised the prospect of other cyber insurance limitations. Those changes could sharply increase the pressure on the CFO to better fund security, given that the enterprise will now be on the hook for the full amount of damages.

A complicating factor is the much-ballyhooed cybersecurity talent shortage. Whether the gap is as big as some say, it’s true that the cost of talent today is higher than what most budgets allow. So, yes, you will have difficulty finding qualified people, but increase the salary enough and, poof — no more talent shortage.

Richard Haag, the VP for compliance services at consulting firm Intersec Worldwide Inc., maintained that the difficulty in acquiring sufficiently experienced talent is a powerful argument in those CFO discussions.

“[I]n security, labor is about the only thing that can possibly be cut. You can’t just swap out firewalls. These agreements are locked in,” Haag says. “You need to say ‘I can barely protect your top strategic areas now. With the cuts you want, I simply won’t be able to defend your top targets and certainly not your not-so-top targets. I need more people, certainly not fewer people.'”

Alford also suggests the CISO point out how they negotiate lower vendor costs. Document it and share it with the CFO to demonstrate that the budget is being spent wisely.

“Demonstrate your efficiencies by driving vendor discounts as low as you can get them to go. CFOs want to know the money is being well spent, and ‘we got a heck of a deal’ does that well,” Alford says.

Finally, the CISO can also make the case for better security delivering more revenue. Does higher security investment make prospective customers more comfortable? Is lack of security making some existing customers leave? For example, if a financial institution chooses to reimburse customers in all fraud situations — rather than what most FIs do, which is to only reimburse in some situations — it could boast that its customers are better protected against fraud, prompting customers to leave competitors. That move would justify higher cybersecurity spend because of the greater acceptance of fraud costs.

“If you can shorten that sales cycle and prove that security gained more sales, it can be highly persuasive to CFOs: ‘Today, three customers walked away, but tomorrow none will,'” Alford says.

https://www.darkreading.com/edge-articles/how-cisos-can-work-with-the-cfo-to-get-the-best-security-budget

The Business-Minded CISO: How to Organize, Evangelize, and Operate an Enterprise-wide IT Risk Management Program

Tags: CISO


Mar 17 2023

Top 5 Insider Threats to Look Out For in 2023

Category: Insider Threat — DISC @ 9:12 am

Unquestionably, ‘insider threats’ is one of the most neglected aspects of cybersecurity and some companies fail to recognize associated dangers.

Cyberattacks are growing more complex as technology advances. Many businesses concentrate their cybersecurity efforts solely on external attacks, which leaves more openings for internal risks. Some companies fail to recognize the danger of losing confidential information owing to employee negligence or malice. Unquestionably, ‘insider threats’ is one of the most neglected aspects of cybersecurity. According to statistics on insider threats, these threats may originate from employees, business contractors, or other reliable partners with simple access to your network. However, insider threat reports and recent developments have shown a sharp rise in the frequency of insider attacks. Because of these, cybersecurity professionals are now paying more attention to the detrimental effects of insider attacks.

In general, security experts need more confidence in their ability to identify and thwart insider threats successfully. 74% of respondents in an insider attack said their company was moderately to extremely vulnerable. 74% of respondents—a 6% increase from 2021—also claim that insider threat assaults have become more regular. In 2022, 60% of respondents said they had an insider attack, while 8% said more than 20. Insider assaults are more challenging to identify and thwart than external attacks, according to 48% of respondents. It can be challenging for defenses to distinguish between insider threats and regular user activity since insider threats employ genuine accounts, passwords, and IT technologies. Overall, insider threats are becoming a more significant threat. These findings imply that security teams should prepare for them in 2023.

Organizations must be able to address the risks from malicious insiders who intentionally steal sensitive data for personal reasons and users who can accidentally expose information due to negligence or simple mistakes. 

Here are the top 5 threats security teams should look out for in 2023:

Employee Negligence

Employee carelessness or ignorance may result in unintentional data leaks, improper handling of sensitive information, or a failure to adhere to security policies and procedures. Negligence is to blame for more than two of every three insider incidents. Workers could not be cognizant of the possible hazards they bring to the company or might not prioritize security measures. They act carelessly, repeating passwords for personal and professional accounts or leaving flash drives with private data at a coffee shop without intending to cause harm. Some are unaware of their involvement and fall victim to social engineering techniques like phishing scams. Others may engage in negligent behavior, such as evading security measures for convenience.

Malicious Insiders

Insiders who intend to cause harm to the company by stealing data, interfering with business processes, or selling confidential information are considered malicious insiders. These people might be driven by greed, retaliation, or a desire to upend the business. These people are currently employed. They might not be the most ardent supporters of your business, and they frequently vent their resentment by erasing or changing important data sets, leaking confidential information, or taking other sabotage measures. Turn cloaks are malicious insiders who consciously do something terrible to an organization. A trustworthy business partner, contractor, or employee could be the insider. Turn cloaks may have ideological, vengeful, or pecuniary motivations. Some engage in clandestine activities like stealing private information or sensitive documents.

Insider Collusion

When two or more employees collaborate to steal information, commit fraud, or participate in other nefarious acts, this is called insider collusion. As a result of the employees’ collaboration and potential ability to conceal their activities, this type of danger might be challenging to identify. Whether intentionally or unintentionally, these threats serve a foreign power. They might be forced to divulge information by outsiders through blackmail or bribery, or they might be tricked into disclosing their login information via social engineering. The most challenging insider risks to identify are moles, which are potentially the most damaging. Moles function similarly to turn cloaks, except they join a firm intending to harm the organization. Whether they support a nation-state or an unknown cause, they are frequently motivated by an intense political motive.

Third-Party Vendors and Contractors

Companies with access to sensitive data or systems may be at risk of insider threats from third-party suppliers and contractors. These individuals might adhere to different security procedures than full-time employees and have a lower stake in the company’s success. Not every insider works for the company. Suppliers, contractors, vendors, and other outside parties with limited inside access can pose an equal threat to staff members with the same rights. Most businesses outsource some of their work to specialized companies or outside agencies. These third parties are occasionally easy targets for cyber attackers because they lack advanced security protocols. Suppose these companies are provided privileged access to part of your company network. In that case, you can bet that the bad actors will infiltrate your system after compromising the partner’s security network, resulting in a third-party data breach.

Security Policy Evaders

The group of workers that prefer to ignore security policies and protocols is last but certainly not least. The business frequently has security policies created to safeguard its personnel and data. Some regulations could be burdensome and inconvenient, and some employees might choose the simple route. Contemporary businesses have security procedures in place to protect their critical data. These safeguards may bother some employees, who may devise workarounds that raise the risk of a data leak. These workarounds could jeopardize the security and data protection of the organization. Policy evaders might be considered insider threats since they purposefully break security policies, procedures, and best practices.

Conclusion

Organizations can employ technological solutions like access restrictions, monitoring, data loss prevention technologies and insider threat solutions “to rein in their insider risk and prevent threats.” A thorough security plan should be in place and periodically reviewed and updated when new risks arise. Your company’s reputation, future growth, customers, and employees can all be protected by knowing how insider threats show themselves.

About the Author: Mosopefoluwa Amao is a certified Cybersecurity Analyst and Technical writer. She has experience working as a Security Operations Center (SOC) Analyst with a history of creating relevant

insider threats

Managing the Insider Threat: No Dark Corners and the Rising Tide Menace

Tags: Insider Threat


Mar 16 2023

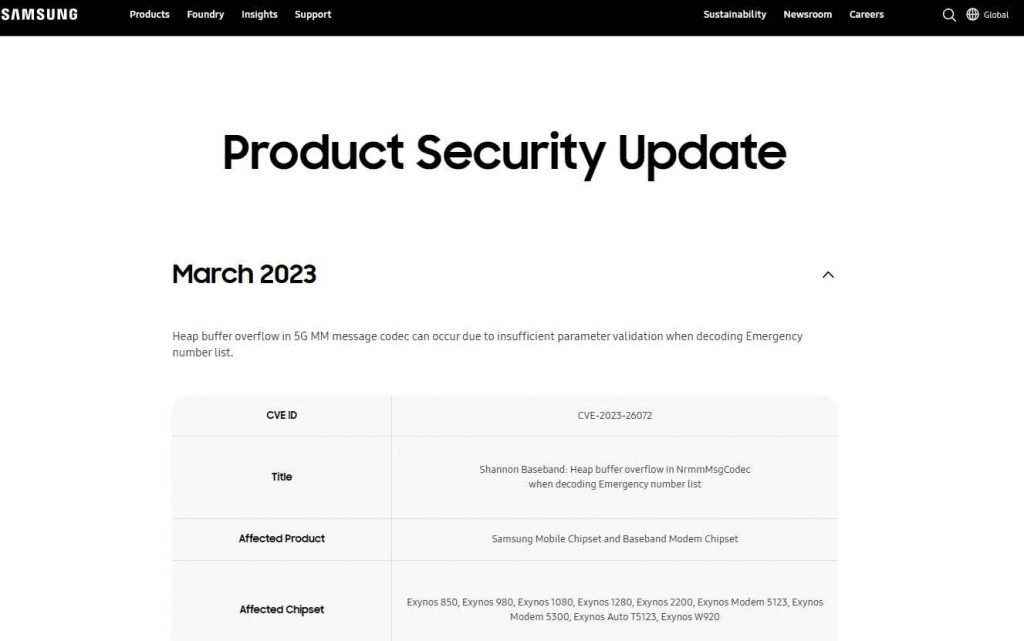
ZERO-DAY VULNERABILITIES IN EXYNOS CHIPSET ALLOW HACKING SAMSUNG, VIVO AND PIXEL PHONES

Category: Hacking,Mobile Security — DISC @ 10:47 pm

The Exynos Modems manufactured by Samsung Semiconductor were found to have eighteen 0-day vulnerabilities, as revealed by Project Zero. Internet-to-baseband remote code execution was possible due to the four vulnerabilities that were deemed to be the most serious among these eighteen flaws (CVE-2023-24033 and three further vulnerabilities that have not yet been allocated CVE-IDs). Tests that were carried out by Project Zero have shown that the aforementioned four vulnerabilities make it possible for an attacker to remotely compromise a phone at the baseband level without any interaction from the user; all that is required is for the attacker to know the phone number of the victim. We anticipate that highly competent adversaries would be able to swiftly design an operational exploit to compromise impacted devices in a stealthy and remote manner if they were just given access to modest extra research and development resources.

The fourteen other similar vulnerabilities (CVE-2023-26072, CVE-2023-26073, CVE-2023-26074, CVE-2023-26075, CVE-2023-26076, and nine additional vulnerabilities that have yet to be granted CVE-IDs) were not as serious since they need either a hostile mobile network operator or an attacker with local access to the device.

The list of Exynos chipsets that are susceptible to these vulnerabilities may be found in the advisory published by Samsung Semiconductor. On the basis of information obtained from public sources that provide a mapping of chipsets to devices, the following devices are likely to be affected:

Devices from Samsung’s S22, M33, M13, M12, A71, A53, A33, A21, A13, A12, and A04 series;

Devices from Vivo’s S16, S15, S6, X70, X60, and X30 series

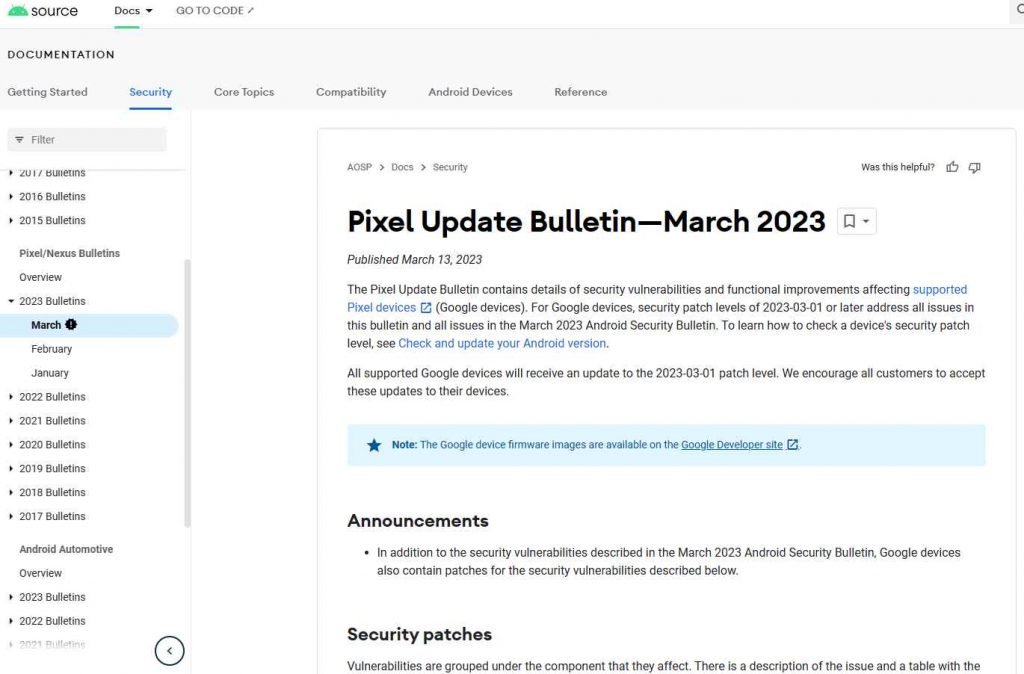
Devices from Google’s Pixel 6 and Pixel 7 series

Any wearables that use the Exynos W920 chipset and vehicles that use the Exynos Auto T5123 chipset.

Timelines for patches to address these vulnerabilities will differ depending on the manufacturer. Those who have devices that are vulnerable may protect themselves from baseband remote code execution vulnerabilities in the meanwhile by turning off Wi-Fi calling and Voice-over-LTE (VoLTE) in the settings of their devices.

Due to the unusual combination of the level of access that these vulnerabilities provide and the speed at which they believe a reliable operational exploit could be crafted, the Google Security Team has decided to make an exception to their standard disclosure policy and delay the disclosure of the four most severe vulnerabilities. This decision was made because the Google Security Team believes that a reliable operational exploit could be crafted relatively quickly.

But, they will maintain their tradition of openness by publicly publishing disclosure policy exclusions, and after all of the concerns have been identified, they will add these problems to the list. Five of the remaining fourteen vulnerabilities (CVE-2023-24072, CVE-2023-24073, CVE-2023-24074, CVE-2023-24075, and CVE-2023-24076) have surpassed Project Zero’s regular 90-day limit and have been publicly revealed in their issue tracker. The other nine vulnerabilities will be publicly disclosed at that time if they are still unfixed.

End users are strongly urged by the Google Security Team to upgrade their devices as soon as is practically practicable in order to guarantee that they are using the most recent releases, which patch security flaws that have been made public as well as those that have not been made public. It is very vital to maintain vigilance and adopt the appropriate safety measures in order to safeguard one’s personal information and electrical devices from possible security risks.

Tags: samsung, VIVO, VIVO AND PIXEL PHONES


Mar 16 2023

Multiple threat actors exploited Progress Telerik bug to breach U.S. federal agency

Category: Data Breach,Security Breach — DISC @ 9:00 am

Multiple threat actors exploited a critical flaw in Progress Telerik to breach an unnamed US federal agency, said the US government.

A joint advisory issued by the Cybersecurity and Infrastructure Security Agency (CISA), Federal Bureau of Investigation (FBI), and Multi-State Information Sharing and Analysis Center (MS-ISAC) revealed that multiple threat actors, including a nation-state actor, exploited a critical vulnerability in Progress Telerik to breach an unnamed US federal agency.

The three-year-old vulnerability, tracked as CVE-2019-18935 (CVSS score: 9.8), is a .NET deserialization issue that resides in the Progress Telerik UI for ASP.NET AJAX. Exploitation can result in remote code execution.

“CISA analysts determined that multiple cyber threat actors, including an Advanced Persistent Threat (APT) actor, exploited a .NET deserialization vulnerability in Progress Telerik user interface for ASP.NET AJAX. Exploitation of this vulnerability allowed malicious actors to successfully execute remote code on a federal civilian executive branch (FCEB) agency’s Microsoft Internet Information Services (IIS) web server.” reads the advisory. “Actors were then able to upload malicious dynamic-link library (DLL) files (some masqueraded as portable network graphics [PNG] files) to the C:\Windows\Temp\ directory.” 

Threat actors exploited the vulnerability to execute arbitrary code on a Microsoft Internet Information Services (IIS) web server used by a federal civilian executive branch (FCEB) agency.

In 2020 and 2021, this flaw was included by the US National Security Agency (NSA) in the list of the top 25 vulnerabilities exploited by Chinese state-sponsored hacking groups in attacks in the wild.

The flaw was also used in the past by the NetWalker ransomware gang in its operations.

The joint alert recommends network defenders review the Malware Analysis Report, MAR-10413062-1.v1 Telerik Vulnerability in U.S. Government IIS Server, to reference CISA’s analysis for the identified malicious files.

According to the MAR, CISA received 18 files for analysis from a forensic analysis engagement conducted at a Federal Civilian Executive Branch (FCEB) agency. Experts reported that 11 of the dynamic link library (DLL) files employed in the attack allows threat actors to read, create, and delete files on the target systems.

“If the DLL contains a hardcoded Internet Protocol (IP) address, status messages will be sent to the IP. One DLL file will attempt to collect the target system’s Transmission Control Protocol (TCP) connection table, and exfiltrate it to a remote Command and Control server (C2).” reads the MAR. “Five of the files drop and decode a reverse shell utility that can send and receive data and commands. In addition, the files drop and decode an Active Server Pages (ASPX) webshell. Two DLL files are capable of loading and executing payloads.”

US CISA has also provided Indicators of Compromise (IOCs) and YARA rules for detection in the Malware Analysis Report (MAR).

CISA Known Exploited Vulnerabilities Catalog Progress Telerik bug

Tags: Telerik bug, U.S. federal agency


Mar 15 2023

Self-paced online training InfoSec courses

Category: Security Awareness,Security training — DISC @ 12:40 pm

Whether your looking to develop a career in data privacy or cybersecurity, we have the perfect training solution for you! Pick bestselling ITG self-paced online training courses today and receive 15% off till March 31st 2023

Self-paced online training courses

Business Continuity Management Lead Implementer Self-Paced Online Training Course  Business Continuity Management Lead Implementer Self-Paced Online Training CourseCalifornia Privacy Rights Act (CPRA) Foundation Self-Paced Online Training Course California Privacy Rights Act (CPRA) Foundation Self-Paced Online Training Course
Certified Cybersecurity Foundation Self-Paced Online Training Course Certified Cyber Security Foundation Self-Paced Online Training CourseCertified ISO 27001:2013 ISMS Lead Implementer and ISO 27001:2022 Transition Self-Paced Online Training Package Certified ISO 27001:2013 ISMS Lead Implementer and ISO 27001:2022 Transition Self-Paced Online Training Package
Certified ISO 27001:2022 ISMS Foundation Self-Paced Online Training Course Certified ISO 27001:2022 ISMS Foundation Self-Paced Online Training CourseCertified ISO 27001 ISMS Lead Implementer Self-Paced Online Training Course Certified ISO 27001:2022 ISMS Internal Auditor Self-Paced Online Training Course  
Certified ISO 27001:2022 ISMS Lead Auditor Self-Paced Online Training Course Certified ISO 27001:2022 ISMS Lead Auditor Self-Paced Online Training CourseCertified ISO 27001:2022 ISMS Lead Implementer Self-Paced Online Training Course Certified ISO 27001:2022 ISMS Lead Implementer Self-Paced Online Training Course
Certified ISO 27001:2022 ISMS Transition Self-Paced Online Training Course Certified ISO 27001:2022 ISMS Transition Self-Paced Online Training CourseCISMP Self-Paced Online Training Course CISMP Self-Paced Online Training Course  
Cyber Incident Response Management Foundation Self-Paced Online Training Course Cyber Incident Response Management Foundation Self-Paced Online Training CourseCybersecurity for IT Support Self-Paced Online Training Course Cybersecurity for IT Support Self-Paced Online Training Course
Certified GDPR Practitioner Self-Paced Online Training Course Certified GDPR Practitioner Self-Paced Online Training CourseThe ITIL 4 Foundation Distance Learning Course – learn about IT service management at your own pace. ITIL® 4 Foundation Self-Paced Online Training Course


Tags: InfoSec courses


Mar 15 2023

OpenAI Announces GPT-4, the Successor of ChatGPT

Category: AI — DISC @ 10:18 am

A powerful new AI model called GPT-4 has been released recently by OpenAI, which is capable of comprehending images and texts. The company describes this as the next-stage milestone in its effort to scale up deep learning.

In November 2022, ChatGPT was launched and has since been used by millions of people worldwide. The all-new GPT-4 is now available through ChatGPT Plus, while it is the paid GPT subscription option of OpenAI available for $20 per month.

However, currently, there is a cap on the usage amount, and to access the API, the developers need to be registered on a waitlist.

The GPT-4 can also perform a number of tasks at once, with a maximum word count of 25,000. That is eight times more than the ChatGPT can.

GPT-4

Pricing & Implementation

Here below, we have mentioned the pricing tags:-

  • For 1,000 “prompt” tokens (Raw text), which is about 750 words will cost $0.03.
  • For 1,000 “completion” tokens (Raw text), which is about 750 words will cost $0.06.

A prompt token is part of a word that has been fed into GPT-4 in order for it to function. While the content that is generated by the GPT-4 is referred to as completion tokens.

In addition, Microsoft recently announced that it is using the GPT-4 version for its Bing Chat chatbot. Since the investment from Microsoft into OpenAI has amounted to $10 billion.

Stripe is another early adopter of GPT-4, which uses it to scan business websites. By doing so, it provides a summary of the results to customer service staff as part of the scanning process.

A new subscription tier for language learning has been developed by Duolingo based on the GPT-4. In order to provide financial analysts with access to information retrieved from company documents, Morgan Stanley is creating a GPT-4-powered system.

It appears that Khan Academy is also working towards automating some sort of tutoring process using GPT-4 that can help students.

A simulated bar exam was given to GPT-4, and it performed particularly well in it, as it managed to achieve scoring around the top 10% of test takers. Interestingly, GPT-3.5, on the other hand, scored in the bottom 10% of the group.  

GPT-4 Action

The GPT-4 algorithm is a form of generative artificial intelligence, similar to the ChatGPT algorithm. With the help of algorithms and predictive text, the generating AI constructs the content based on the prompts that are presented by the user. 

As you can see in the image below, GPT-4 generates recipes based on images that have been uploaded.

The reasoning skills of GPT-4 are more advanced than those of ChatGPT. In order to find available meeting times, the model can, for instance, search for three schedules with three available times.

In short, the GPT-4 is much smarter and more capable as compared to the GPT-3.5. GPT-4 is capable of receiving and processing textual and visual information, one of its most impressive features.

At the moment, it is not yet possible for OpenAI customers to utilize the image understanding capability of GPT-4. However, currently, OpenAI is testing this technology with only one partner, Be My Eyes.

OpenAI has warned that, just like its predecessors, the GPT-4 is still not entirely reliable. This model needs to be further improved by the entire community by building on top of the model, exploring it, and contributing to it through collective efforts. 

There is still a lot of work to be done, and the company affirmed that they are looking forward to working together to improve it.

CHATGPT-4 Revealed 500 Prompts to Ride the AI Wave (Mastering ChatGPT-4 Prompts & Beyond)

Tags: ChatGPT, GPT-4


Mar 14 2023

TWO VERY CRITICAL VULNERABILITIES PATCHED IN NEW APACHE HTTP SERVER UPDATE

Category: Security vulnerabilities,Web Security — DISC @ 8:22 am

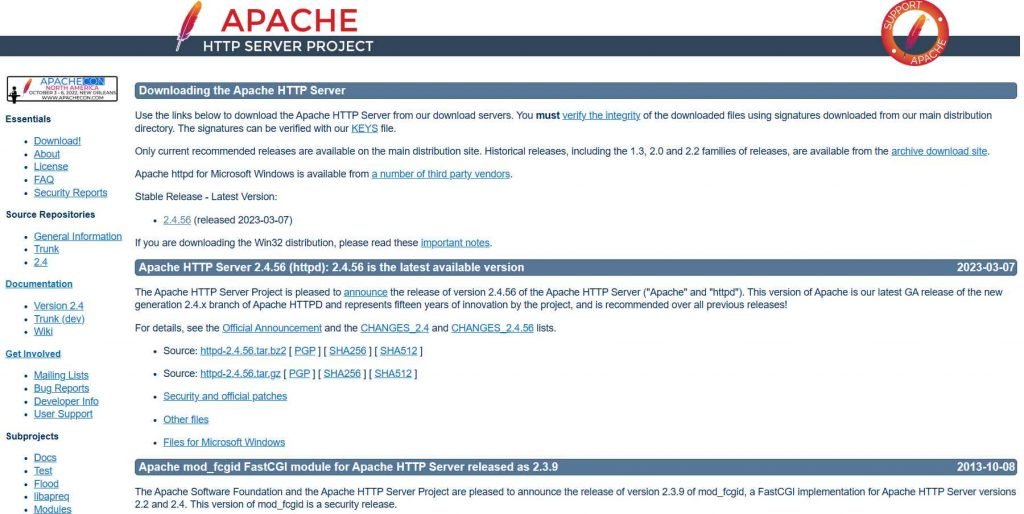
Apache HTTP Server is one of the web servers that is used the most often throughout the globe. It is responsible for providing power to millions of websites and apps. Recent vulnerabilities found in the server, on the other hand, have the ability to disclose sensitive information and make it easier for attackers to carry out further attacks. The Apache HTTP Server has recently been found to contain two significant vulnerabilities, both of which are detailed below. It is imperative that you rapidly upgrade Apache HTTP Server to the most recent version in order to protect your system against the vulnerabilities described.

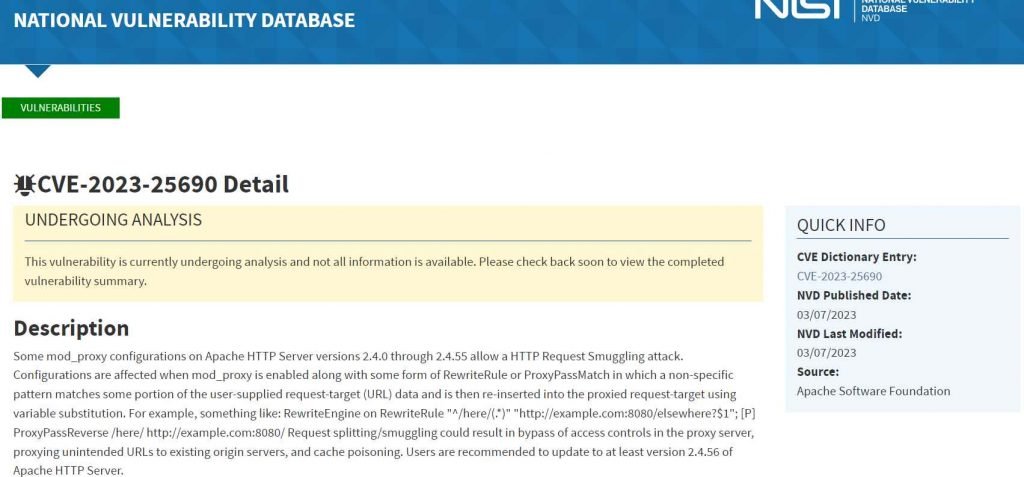
Apache HTTP Server request splitting vulnerability, CVE-2023-25690. This vulnerability is brought about by an issue that occurs in mod proxy whenever it is activated with a RewriteRule or ProxyPassMatch of some kind. This vulnerability might be used by a remote attacker to overcome access constraints in the proxy server, route undesired URLs to existing origin servers, and poison cache. Attacks using HTTP Request Smuggling are possible on Apache HTTP Server versions 2.4.0 through 2.4.55, if the server is configured with certain mod proxy settings. It occurs when mod proxy is enabled along with some form of RewriteRule or ProxyPassMatch. In these configurations, a non-specific pattern matches some portion of the user-supplied request-target (URL) data, and the matched data is then re-inserted into the proxied request-target utilizing variable substitution. This causes CVE-2023-25690 to be triggered. This might result in requests being split or smuggled, access rules being bypassed, and unwanted URLs being proxied to existing origin servers, all of which could lead to cache poisoning.

Versions of the Apache HTTP Server ranging from 2.4.30 to 2.4.55 are impacted by the problem. This attack is carried out by introducing unusual characters into the header of the origin response, which has the potential to either truncate or divide the response that is sent to the client. An attacker might take use of this vulnerability to inject their own headers into the request, causing the server to produce a split response.

Secure By Design

Tags: Apache HTTP Server


Mar 14 2023

Cyber Security Training Courses

Category: Security training — DISC @ 7:55 am
Cyber Security Course Online – Fees, Syllabus, Eligibility

70+ Cyber Security Training Courses

“Security should be built in, not bolt-on.”

Cyber Security CoursesLinks
Finding your cybersecurity-career pathedx.sjv.io/BXm2G4  
MYCS computer science for beginnersedx.sjv.io/e4yQ5r  
IBM cybersecurity fundamentalsedx.sjv.io/gbMAjv
Ethical hacking essentials eheedx.sjv.io/e4yAJZ  
Online master science cybersecurity Georgia techedx.sjv.io/NK1QOP  
Usmx umgc cloud computingedx.sjv.io/LPAxb3
w3cx front end web developeredx.sjv.io/2rbQPM
Snhux data management with python and sqledx.sjv.io/qn5ERq
Python data scienceedx.sjv.io/AoqqJN
Introduction to python programmingedx.sjv.io/mgDDPy  
Online master of science computer science utaustinxedx.sjv.io/rnkzvj
Master of information and cybersecurityedx.sjv.io/5bXXzj  
Linux foundation x introduction to devops practices and toolsedx.sjv.io/LPAZZY
Uwashingtonx essentials cybersecurityedx.sjv.io/jWxOO0
Hecmontrealx ux design and evaluationedx.sjv.io/ORVmbn
Cybersecurity the cisos viewedx.sjv.io/MXGNbo
Ec council cybersecurity essentialsedx.sjv.io/9W4JE3
building-a-cybersecurity-toolkitedx.sjv.io/6b3gdG
Programming basicsedx.sjv.io/DV9ked  
Computer science 101edx.sjv.io/DV9ke2
Umd usmx agile project managementedx.sjv.io/Vyz6BO
Computer forensicedx.sjv.io/ORVm4W
Delftx inclusive and sustainable citiesedx.sjv.io/5b27Y2
Cybersecurity and privacy in the IoTedx.sjv.io/6b3gVN
Cybersecurity risk managementedx.sjv.io/YgEy2O  
Linuxfoundationx secure software development fundamentalsedx.sjv.io/QOZ60Y
Harvardx leadership and communicationedx.sjv.io/WDWGg3
AWS getting started with cloud securityedx.sjv.io/3P6dYv  
AWS cloud technical essentialsedx.sjv.io/kj7ZGn  
Building modern python applications on awsedx.sjv.io/DVjnzj  
Getting started with data analytics on awsedx.sjv.io/rnAOxQ  
Cyberwar surveillance and securityedx.sjv.io/7mRJd3  
Online master data science utausedx.sjv.io/jWxO5n  
Harvardx data scienceedx.sjv.io/KeooMv  
Uc san diego x data scienceedx.sjv.io/b3WWYg
Introduction to computer science and programmingedx.sjv.io/qn520O
Ritx cybersecurityedx.sjv.io/5b27qD  
Linux basics the command line interfaceedx.sjv.io/n1r2Aa  
Ibm full stack cloud application developmentedx.sjv.io/Ryg6Yy  
Basic network and database securityedx.sjv.io/qn52d5  
Scripting and programming foundationsedx.sjv.io/P0JAvz  
Application security for developersedx.sjv.io/zaZqxW  
Unlocking information security part 1edx.sjv.io/n1D1NX  
Unlocking information security part 2edx.sjv.io/kjDbBN  
Berkeleyx entrepreneurship for all the startup guide by silicon valley insidersedx.sjv.io/DV91Xd
Programming for everybody getting started with pytedx.sjv.io/e4yxkZ
Google cloud computing foundationsedx.sjv.io/15nkma  
Harvardx computer science for web programmingedx.sjv.io/MXGzQN
Mit sloan machine learning in business online programedx.sjv.io/AoxeKD
Cyber security basics a hands on approachedx.sjv.io/jWxEQ5  
Imd blockchain and the future of finance online programedx.sjv.io/zaZWD6
Introduction to linuxedx.sjv.io/yRJzPW  
Google power searching with googleedx.sjv.io/rnkVqv  
Basic network and database securityedx.sjv.io/BXqXKq  
AI chatbots without programmingedx.sjv.io/0J0jVV  
Imd cybersecurity risk and strategy online programedx.sjv.io/0JkGQO  
Network security protocolsedx.sjv.io/dobXWW
Digital forensics essentials dfeedx.sjv.io/7mWA6Y  
The quantum internet and quantum computers how w2edx.sjv.io/QORREP
Wharton strategic managementedx.sjv.io/5bXXvo  
Umd usmx agile project managementedx.sjv.io/e4OOL6  
tumx-lean-six-sigma-green-belt-certificationedx.sjv.io/x900gx  
Harvardx tiny machine learningedx.sjv.io/GjAA7n  
Berkeleyx science-of happiness at workedx.sjv.io/ZdPP7K  
Uqx business leadershipedx.sjv.io/0JkkVO  

Professional Certificates, Bachelors & Masters Program

InfoSec Threats | InfoSec books | InfoSec tools | InfoSec services

Tags: Cyber Security Training Courses


Mar 13 2023

Vendor Security Checklist

Category: Information Security,Vendor Assessment — DISC @ 12:36 pm

Vendor Security Checklist – by Ministry of Security

Third Party Risk Management

Previous posts on Vendor Assessment

DISC performs Vendor assessment, we’d love to hear from you! If you have any questions, comments, or feedback, please don’t hesitate to contact us. Our team is here to help and we’re always looking for ways to improve our services. You can reach us by email (info@deurainfosec.com), or through our website’s contact form

InfoSec Threats | InfoSec books | InfoSec tools | InfoSec services

Tags: Third Party Risk Management


Mar 13 2023

Data Security With Cloud Compliance: Meeting Regulations & Standards

Category: Cloud computing,data security — DISC @ 10:21 am

Businesses from all industries are aware of the benefits of cloud computing. Some organizations are just getting started with migration as part of digital transformation initiatives, while others are implementing sophisticated multi-cloud, hybrid strategies. However, data security in cloud computing is one of the most challenging deployment concerns at any level due to the unique risks that come with the technology.

The cloud compromises the conventional network perimeter that guided cybersecurity efforts in the past. As a result, a distinct strategy is needed for data security in cloud computing, one that takes into account both the complexity of the data compliance,  governance, and security structures as well as the dangers.

The Shifting Business Environment and Its Effects on Cloud Security

The top investment businesses implementing digital transformation initiatives want to make over the next three years is bolstering cybersecurity defenses. A paradigm shift in cybersecurity is being brought about by the rising trend of remote and hybrid workplaces, which is altering investment priorities.

Cloud computing provides the underlying technology for this transition as organizations want to increase resilience, and people want the freedom to work from anywhere. Yet, the lack of built-in security safeguards in many cloud systems highlights the need for data security in cloud computing.

What Is Cloud Data Security?

Cloud data security involves adopting technological solutions, policies, and processes to safeguard cloud-based systems and apps and the data and user access that go with them. The fundamental tenets of information security and data governance apply to the cloud as well:

Confidentiality: Protecting the data from illegal access and disclosure is known as confidentiality.

Integrity: Preventing unauthorized changes to the data so that it may be trusted

Accessibility: Making sure the data is completely accessible and available when it’s needed.

Cloud data security must be taken into account at every stage of cloud computing and the data lifecycle, including during the development, deployment, and administration of the cloud environment.

Data Risks in Cloud

Cloud computing has revolutionized the way data is gathered, stored, and processed, but it has also introduced new risks to data security. As more organizations rely on the cloud, cyberattacks and data breaches have become the biggest threats to data protection. While cloud technology is subject to the same cybersecurity risks as on-premises solutions, it poses additional risks to data security.

Application Programming Interfaces (APIs) with Security Flaws

Security flaws in APIs used for authentication and access are a common risk associated with the cloud. These flaws can be exploited by hackers to gain unauthorized access to sensitive data. Common issues include insufficient or improper input validation and insufficient authentication mechanisms. APIs can also be vulnerable to denial-of-service attacks (DoS), causing service disruptions and data loss.

Account Takeover or Account Hijacking

Account takeover or hijacking is a common threat in cloud computing, where hackers gain unauthorized access to user accounts and can steal or manipulate sensitive data. Hackers can gain access to cloud accounts due to weak or stolen passwords used by users. This is because users often use simple, easy-to-guess passwords or reuse the same password across multiple accounts. Once a hacker gains access to one account, they can potentially access other accounts that use the same password.

Insider Risks

Insider threats are a significant concern in cloud computing due to the lack of visibility into the cloud ecosystem. Cloud providers typically have a vast and complex infrastructure, which can make it challenging to monitor user activity and detect insider threats. Insider threats can occur when insiders, such as employees, contractors, or partners, intentionally or unintentionally access or disclose sensitive data.

Security Measures Protecting Data in Cloud Computing

Identity governance is the first step in securing data in the cloud. Across all of your on-premises and cloud platforms, workloads, and data access, you need a thorough, unified perspective. Identity management gives you the following:

Install Encryption

Encryption is an essential security measure for protecting sensitive and important data, including Personally Identifiable Information (PII) and intellectual property, both in transit and at rest. 

Third-party encryption solutions can offer additional layers of security and flexibility beyond what is provided by CSPs. For example, some third-party encryption solutions may offer more robust encryption algorithms or the ability to encrypt data before it is uploaded to the cloud. They can also provide granular access controls, enabling organizations to determine who can access specific data and under what circumstances.

Archive the Data

Backing up cloud data is critical for data protection and business continuity. The 3-2-1 rule is a best practice, involving having at least three copies of the data, stored in two different types of media, with one backup copy stored offsite. Businesses should have a local backup in addition to the cloud provider’s backup, providing an extra layer of protection in case the cloud provider’s backup fails or is inaccessible.

Put Identity and Access Management (IAM) into Practice

IAM (Identity and Access Management) is essential for securing cloud resources and data. IAM components in a cloud environment include identity governance, privileged access control, and access management, such as SSO or MFA. To ensure effective IAM in a cloud environment, organizations must include cloud resources in their IAM framework, create appropriate policies and procedures, and regularly review and audit IAM policies and procedures.

Control Your Password Rules

Poor password hygiene is a common cause of security events. Password management software can help users create, store and manage strong, unique passwords for each account, making it easier to follow safe password procedures. This can encourage better password hygiene and reduce the risk of password-related security incidents.

Use Multi-factor Authentication (MFA)

MFA (Multi-factor authentication) is a security mechanism that adds an extra layer of security beyond traditional password-based authentication. It reduces the chance of credentials being stolen and makes it more challenging for threat actors to gain unauthorized access to cloud accounts. 

MFA is particularly valuable in cloud environments, where many employees and contractors may access cloud accounts from various locations and devices. However, it is important to ensure that it is implemented correctly, easy to use, and integrated with existing security infrastructure and policies.

Summary

Your environment will get more complicated as you continue to utilize the cloud, particularly if you begin to rely on the hybrid multi-cloud. Data security in cloud computing is essential for reducing the dangers to your business and safeguarding not just your data but also your brand’s reputation.

Consider deploying solutions for controlling cloud access and entitlements to protect yourself from the always-changing cloud risks. For a thorough approach to identity management, incorporate these solutions into your entire IAM strategy as well.

A complete, identity-centered solution ensures that you constantly implement access control and employ governance more wisely, regardless of whether your data is on-premises or in the cloud. You will also profit from automation and other factors that increase identity efficiency and save expenses.

Cloud Computing Security: Foundations and Challenges

AWS Security Cookbook: Practical solutions for managing security policies, monitoring, auditing, and compliance with AWS

Let AWS Solutions Architects start you on your journey to secure your cloud resources.

InfoSec Threats | InfoSec books | InfoSec tools | InfoSec services

Tags: cloud security, Data Security With Cloud


Mar 12 2023

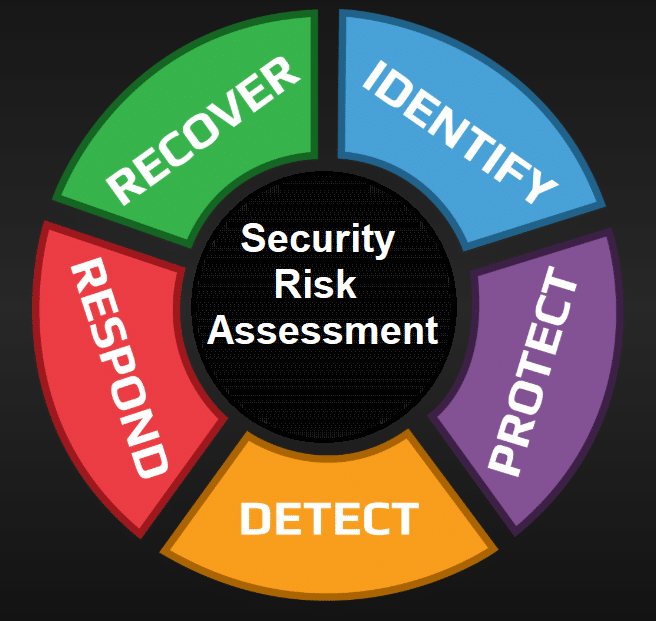
Security Risk Assessment Services

Category: Risk Assessment,Security Risk Assessment — DISC @ 11:16 pm

Security risk assessment services are crucial in the cybersecurity industry as they help organizations identify, analyze, and mitigate potential security risks to their systems, networks, and data. Here are some opportunities for providing security risk assessment services within the industry:

  1. Conducting Vulnerability Assessments: As a security risk assessment service provider, DISC can conduct vulnerability assessments to identify potential vulnerabilities in an organization’s systems, networks, and applications. You can then provide recommendations to mitigate these vulnerabilities and enhance the organization’s overall security posture.
  2. Performing Penetration Testing: Penetration testing involves simulating a real-world attack on an organization’s systems and networks to identify weaknesses and vulnerabilities. As a security risk assessment service provider, DISC can perform penetration testing to identify potential security gaps and provide recommendations to improve security.
  3. Risk Management: DISC can help organizations identify and manage risks associated with their information technology systems, data, and operations. This includes assessing potential threats, analyzing the impact of these threats, and developing plans to mitigate them.
  4. Compliance Assessment: DISC can help organizations comply with regulatory requirements by assessing their compliance with industry standards such as ISO 27001, HIPAA, or NIST-CSF. DISC can then provide recommendations to ensure that the organization remains compliant with these standards.
  5. Cloud Security Assessments: As more organizations move their operations to the cloud, there is a growing need for security risk assessment services to assess the security risks associated with cloud-based systems and applications. As a service provider, DISC can assess cloud security risks and provide recommendations to ensure the security of the organization’s cloud-based operations.
  6. Security Audit Services: DISC can provide security audit services to assess the overall security posture of an organization’s systems, networks, and applications. This includes reviewing security policies, processes, and procedures and providing recommendations to improve security.

By providing these services, DISC can help organizations identify potential security risks and develop plans to mitigate them, thereby enhancing their overall security posture.

In what situations would a vCISO Service be appropriate?

Transition plan from ISO 27001 2013 to ISO 27001 2022

We’d love to hear from you! If you have any questions, comments, or feedback, please don’t hesitate to contact us. Our team is here to help and we’re always looking for ways to improve our services. You can reach us by email (info@deurainfosec.com), or through our website’s contact form

Contact DISC InfoSec if you need further assistance in your ISO 27001 2022 transition Plan

InfoSec Threats | InfoSec books | InfoSec tools | InfoSec services

Tags: Security Risk Assessment


Mar 12 2023

Bring a firewall anywhere you go with this Deeper Connect Pico

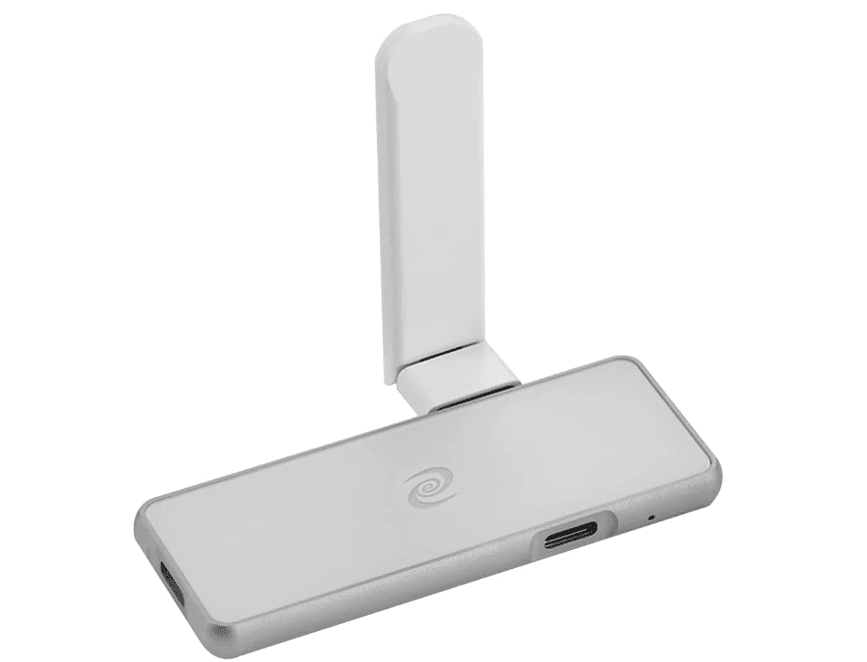
As threats to both data security and personal privacy pile up, fighting back has never been more important. The Deeper Connect Pico packs both privacy tools and cybersecurity protection into a unit you can drop into your pocket.

The Pico is easy to install, taking just a minute to set up and connect. It has no subscriptions to manage or add-ons to buy, as it’s a hardware tool. Nor will it require any updates, as it’s built to be a plug-and-play device and comes with a wireless adapter.

Powered from any USB source and drawing only 1W of power, it weighs just .11 lbs and is only 3.4 inches long by 1.2 inches wide. The brushed aluminum casing is rugged and discreet, so you can throw it in your bag, hang it off your keychain, or keep it in your pocket.

Once connected, the Pico drops an enterprise-grade seven-layer firewall in front of snoops and malicious actors. Using an onboard quad-core ARM processor strong enough to work on the blockchain while you’re idle, the firewall prevents common attacks and alerts you when they happen, so you can take further action.

Also built into the hardware is an ad blocker that cuts off certain attacks and guards your privacy. It’s backed up by one-click parental control, so kids can log onto public networks while you keep the rules in place.

Providing extra security, the decentralized private network (DPN) uses other Picos as nodes for its network, with smart routing, multi-routing, and other functions across an ever-changing network that adds an extra layer of obfuscation for would-be snoops.

The world is becoming more complex, with more risks to your data when you connect to public networks. This hardware cybersecurity and VPN tool takes the worry out of connecting with others.

TP-Link ER7206 | Multi-WAN Professional Wired Gigabit VPN Router | Increased Network Capacity| SPI Firewall | Omada SDN Integrated | Load Balance | Lightning Protection


InfoSec Threats
 | InfoSec books | InfoSec tools | InfoSec services

Tags: Deeper Connect Pico


Mar 12 2023

Professional Certificates, Bachelors & Masters Program

Category: Security training — DISC @ 12:13 am
Talent Development | Human Resources | Drexel University
“Learning is an experience. Everything else is just an information.”

The quote implies that true learning is not just about acquiring information but also experiencing it in a way that creates a deeper understanding and meaning.

Learning involves more than just memorizing facts or acquiring knowledge. It requires actively engaging with the material, processing it, and making connections between different concepts. When we experience something, we engage with it on a deeper level, and this can lead to a more meaningful and lasting learning experience.

For example, imagine learning a new language by simply memorizing vocabulary words and grammar rules without ever actually practicing the language with native speakers or immersing oneself in the culture. In contrast, if we actively engage with the language by speaking it, listening to it, and experiencing the culture, we are more likely to develop a deeper understanding and appreciation for the language.

Therefore, while information is necessary for learning, it is not sufficient on its own. To truly learn and understand something, we must engage with it and experience it in a meaningful way.


Professional Certificate

PartnerProgram NameLink
HarvardXData Sciencehttps://edx.sjv.io/KeooMv
GTxIntroduction to Python Programminghttps://edx.sjv.io/mgDDPy
UCSDPython Data Sciencehttps://edx.sjv.io/AoqqJN
WhartonStrategic Managementhttps://edx.sjv.io/5bXXvo
UMD / USMxAgile Project Managementhttps://edx.sjv.io/e4OOL6
TUMxLean Six Sigma Green Belt Certificationhttps://edx.sjv.io/x900gx
IBMApplied AIhttps://edx.sjv.io/x900gx
HarvardXTiny Machine Learning (TinyML)https://edx.sjv.io/GjAA7n
BerkeleyXThe Science of Happiness at Workhttps://edx.sjv.io/ZdPP7K
ColumbiaXCorporate Financehttps://edx.sjv.io/gbvvYg

MicroMasters® Programs

PartnerProgram NameLink
IUxAccountingedx.sjv.io/EKbbGD
UQxBusiness Leadershiphttps://edx.sjv.io/0JkkVO
USMx, UMUCCloud Computinghttps://edx.sjv.io/Ea557W
UCSanDiegoXData Sciencehttps://edx.sjv.io/b3WWYg
RITxDesign Thinkinghttps://edx.sjv.io/OR667Z
IUxInformation Systemshttps://edx.sjv.io/2rGGZ0
USMx, UMUCInstructional Design and Technologyhttps://edx.sjv.io/3PVVgr
BerkeleyXMarketing Analyticshttps://edx.sjv.io/Ry447X
MITxSupply Chain Managementhttps://edx.sjv.io/vnooY3
HECxUX Design and Evaluationhttps://edx.sjv.io/dobbYW

MicroMasters® Programs

PartnerProgram NameLink
StanComputer Science 101edx.sjv.io/DV9ke2
RITCybersecurity Fundamentalsedx.sjv.io/Jzbbov
RICExElements of Data Sciencehttps://edx.sjv.io/Keoo77
NYUxIntroduction to Databasesedx.sjv.io/ZQbbJz
UC3MxProgramming & Data Structuresedx.sjv.io/B0EEeJ
WGUxIntroduction to Information Technologyhttps://edx.sjv.io/x900Yx
DoaneXMarketing Essentialshttps://edx.sjv.io/QORR7a

Quotes About Professional Learning. QuotesGram

InfoSec Threats | InfoSec books | InfoSec tools | InfoSec services


Mar 11 2023

Linux 101 Hacks

Category: Hacking,Linux Security,Security Tools — DISC @ 12:09 pm

Looking to enhance your Linux skills? Practical examples to build a strong foundation in Linux – credit: Ramesh Nararajan
*******************************************

Mastering Linux Security and Hardening: A practical guide to protecting your Linux system from cyber attacks

InfoSec Threats | InfoSec books | InfoSec tools | InfoSec services

Tags: Hacking, Hacking tool, Linux, OSINT


Mar 10 2023

US Lawmakers Face Cyberattacks, Potential Physical Harm After DC Health Link Breach

The threat actor who posted the data for sale has claimed credit for multiple other breaches, including one at grocery platform Weee! that exposed data on more than 1.1 million customers.

Jai VijayanContributing Writer, Dark Reading

US House of Representatives seal
Source: Ron Adar via Shutterstock

Hundreds of US lawmakers and their families are at risk of identity theft, financial scams, and potentially even physical threats after a known info-theft threat actor called IntelBroker made House of Representatives members’ personally identifiable information (PII) available for sale on the “Breached” criminal forum.

The information, confirmed as being obtained via a breach at health insurance marketplace DC Health Link, includes names, Social Security numbers, birth dates, addresses, and other sensitive identifying information. The data on the House members was part of a larger data set of PII belonging to more than 170,000 individuals enrolled with DC Health Link that the threat actor put up for sale this week.

DC Health Link: A Significant Breach

In a March 8 email to members of the House and their staff, US House Chief Administrative Officer Catherine Szpindor said the attack on DC Health Link does not appear to have specifically targeted US lawmakers. But the breach was significant and potentially exposed PII on thousands of people enrolled with DC Health Link.

“The FBI also informed us that they were able to purchase this PII, along with other enrollee information, on the Dark Web,” Speaker of the House Kevin McCarthy (R-Calif.) and House Minority Leader Hakeem Jeffries (D-N.Y.) said in a joint letter to the executive director at DC Health Link on March 8. The letter sought specifics from the health exchange on the breach, including details on the full scope of the attack and DC Health Link’s plans to notify affected individuals and offer credit monitoring services for them.

Despite the letter, details of the intrusion at DC Health Link are not yet available. The organization, governed by an executive board appointed by the DC mayor, did not immediately respond to a request for comment on the incident.

A report in BleepingComputer this week first identified the threat actor as the appropriately named IntelBroker, after the cybercriminals put the stolen data up for sale on March 6. According to the underground forum ad, the data set is available for “an undisclosed amount in Monero cryptocurrency.” Interested parties are asked to contact the sellers via a middleman for details.

IntelBroker’s Resume of Previous Breaches

This is not the first big heist for the group: A threat actor, using the same moniker in February, had claimed credit for a breach at Weee!, an Asian and Hispanic food delivery service. IntelBroker later leaked some 1.1 million unique email addresses and detailed information on over 11.3 million orders placed via the service. 

Security vendor BitDefender, which covered the incident in its blog at the time, published an ad that IntelBroker placed on BreachedForums that showed the attacker boasting about obtaining full names, email addresses, phone number, and even order notes which included apartment and building access codes.

Meanwhile, Chris Strand, chief risk and compliance officer at Cybersixgill says his company has been tracking IntelBroker since 2022 and is about to release a report on the actor. “IntelBroker is a highly active Breached member with an 9/10 reputation score, who claimed in the past to be the developer of Endurance ransomware,” Strand says.

IntelBroker’s use of Breached to sell the health exchange PII, instead of a dedicated leak site or a Telegram channel, is consistent with the threat actor’s previous tactics. It suggests either a lack of resources or inexperience on the individual’s part, Strand says. 

“In addition to IntelBroker’s presence on Breached, the threat actor has maintained a public GitHub repository titled Endurance-Wiper,” he tells Dark Reading.

In November, IntelBroker claimed that it used Endurance to steal data from high level US government agencies, Strand notes. The threat actor has in total made some 13 claims about breaching top US government agencies, likely to attract customers to a ransomware-as-a-service (RaaS) program. Other organizations that IntelBroker claims to have broken into include Volvo, cult footwear maker Dr. Martens, and an Indonesian subsidiary of The Body Shop.

“Our intelligence analysts have been tracking IntelBroker since 2022, and we have been collecting intel attributed to that threat actor since then, as well as associated threats that have been related or attributed to IntelBroker,” Strand says.

Is House Members’ PII a National Security Threat?

Justin Fier, senior vice president of red team operations at Darktrace, says the threat actor’s reason for putting the data up for sale appears to be purely financially motivated rather than political. And given the high profile of the victims, IntelBroker may find that the attention the breach is garnering will increase the value of the stolen data (or bring more heat than it would like).

The buyers might be another story. Given the availability of physical addresses and electronic contact information, the kinds of potential follow-on attacks are myriad, ranging from social engineering for identity theft or espionage, to physical targeting, meaning that interested parties could run the gamut in terms of motivation.

“The amount tells you a great deal about who they may be thinking of in terms of buyers,” he says. If all that the threat actor ends up asking is a couple of thousand dollars, they are likely to be a smaller criminal enterprise. But “you start talking millions, they are clearly then catering to nation-state buyers,” he says.

Fier assesses that the data that the threat actor stole on US House members as potentially posing a national security issue. “We shouldn’t only think external nation-states that might want to purchase this,” Fier says. “Who is to say that other political parties and/or activists couldn’t weaponize it?”

https://www.darkreading.com/application-security/us-lawmakers-cyberattacks-physical-harm-dc-health-link-breach

Previous posts on Cyber Attacks

InfoSec Threats | InfoSec books | InfoSec tools | InfoSec services

Tags: Cyberattacks, US Lawmakers


Mar 10 2023

Akamai mitigated a record-breaking DDoS attack that peaked 900Gbps

Category: DDoS — DISC @ 10:42 am

Akamai reported that on February 23, 2023, at 10:22 UTC, it mitigated the largest DDoS attack ever. The attack traffic peaked at 900.1 gigabits per second and 158.2 million packets per second. The record-breaking DDoS was launched against a Prolexic customer in Asia-Pacific (APAC).

“On February 23, 2023, at 10:22 UTC, Akamai mitigated the largest DDoS attack ever launched against a Prolexic customer based in Asia-Pacific (APAC), with attack traffic peaking at 900.1 gigabits per second and 158.2 million packets per second.” reads the post published by Akamai.

DDoS

The company pointed out that the attack was intense and short-lived, with most attack traffic bursting during the peak minute of the attack. The overall attack lasted only a few minutes.

Akamai mitigated the attack by redirecting the malicious traffic through its scrubbing network.

Most of the malicious traffic (48%) was managed by scrubbing centers in the APAC region, but the company claims that all its 26 centers were loaded, with only one center in HKG handling 14,6% of the total traffic.

Akamai states that there was no collateral damage thanks to its defense.

The previous record-breaking distributed denial of service attack mitigated by Akamai hit a company customer in Europe on September 2022. At the time, the malicious traffic peaked at 704.8 Mpps and appeared to originate from the same threat actor behind another record-breaking attack that Akamai blocked in July and that hit the same customer.

In January, Microsoft announced that its Azure DDoS protection platform has mitigated a record 3.47 Tbps attack that targeted one of its customers with a packet rate of 340 million packets per second (pps).

The attack took place in November and hit a customer in Asia, it originated from approximately 10,000 sources and from multiple countries across the globe, including the United States, China, South Korea, Russia, Thailand, India, Vietnam, Iran, Indonesia, and Taiwan.

The 3.47 Tbps attack was the largest one Microsoft has mitigated to date, likely the massive one ever recorded.

Previous posts on DDoS

Distributed Denial of Service Attacks: Real-world Detection and Mitigation


InfoSec Threats
 | InfoSec books | InfoSec tools | InfoSec services

Tags: ddos, Distributed Denial of Service Attacks


Mar 09 2023

Security Professionals Battle Burnout as Threat Landscape Evolves

Category: cyber security — DISC @ 11:14 am

A surge of cybersecurity incidents and a general feeling of work overload is leading to widespread burnout among IT security professionals, two surveys indicated.

A Cynet survey of chief information security officers (CISOs) of small to midsize businesses found nearly two-thirds (65%) said their ability to protect their organization is compromised due to an overwhelming workload–with nearly 100% admitting they needed additional resources.

The stress levels are affecting entire IT security teams, with nearly three-quarters (74%) of CISOs surveyed admitting they have lost team members because of work-related stress issues.

Nearly half (47%) of these CISOs have had more than one team member exit their role over the last 12 months.

Burning Out and Fading Away

Respondents to a Magnet Forensics survey said the rapid evolution of cybercrime is weighing on security teams substantially more than it did last year, leading to widespread burnout. Alert and investigation fatigue are twin contributing factors, the survey revealed.

The study also revealed that the evolving nature of threats is extending response times beyond what they feel is acceptable—43% of respondents said it takes them between one week and more than a month.

Nearly a third of respondents said that identifying the root cause of an incident requires either a “complete overhaul” or “major improvements” in the organization’s threat posture.

“We’re seeing a direct correlation between burnout and the increased activity of cybercriminals who are relying on more complex strategies and bombarding organizations with more attacks,” explained Adam Belsher, CEO of Magnet. “New cybersecurity regulations also impacted our respondents who said they’re now under increased pressure to get answers faster.”

He pointed out that a global talent shortage resulted in hiring challenges, and that digital forensics and incident response practitioners (DFIR) find themselves in a difficult situation.

“They need to respond to more incidents, get answers faster and do so while knowing no reinforcements are on the way,” Belsher noted. “It’s no surprise that they’re burned out.”

George Tubin, director of product marketing for Cynet, added that what stood out most is what a vicious cycle this work-related stress is. Their stress at work spills over into their personal lives, which increases their stress at work—and repeat.

“Because of their workload and stress, these CISOs said they’re missing vacations and private events and they’re also losing their tempers with family and friends. This only exacerbates their stress levels,” he says.

In addition, 80% of them have received complaints about how they handled security tasks and two-thirds said their ability to protect their organizations is compromised due to work overload and stress.

More Cybersecurity Staff Needed to Combat Burnout

The Cynet survey also asked CISOs whether they need more people, and the general consensus is that they could use 30% more staff.

They also said they’ve compromised on hiring decisions because it’s so hard to find good cybersecurity people.

“But, when we asked them what initiatives could help them reduce stress levels, rather than say hire more, more CISOs stated technology consolidation and automation, as well as outsourcing,” Turbin says. “Cybersecurity technology has become so complicated and so expensive that the cure is almost as bad as the disease.”

Belsher noted that each factor contributing to the burnout of DFIR practitioners is out of their hands.

“They can’t control how often cybercriminals attack their organizations or the methods they use,” he said. “Cybercriminals have continued to find new threat vectors and ways to scale the volume of their attacks. That won’t change in 2023.”

That means organizations must adapt to this threat landscape beyond trying to hire themselves out of this problem.

“If we maintain the status quo, burnout will only get worse,” he says. “Automation is essential to scaling the capacity of DFIR teams.”

Turbin agreed, noting a couple of the survey questions asked the respondents to compare the past year with previous years; the results were consistent or have become slightly worse.

“Unless these security leaders can somehow relieve their stress, mainly through simplifying and automating their cybersecurity technology, I expect the situation to get worse before it gets any better,” he said.

He added that CEOs and the board should be concerned about the threat of burnout, especially considering that this stress is leading to a degradation in security outcomes that increased risk for the organization.

“CEOs and board members should proactively reach out to their security leaders to discuss ways to reduce stress and improve the company’s security posture,” he advised.

Belsher pointed out that cybersecurity and IT personnel can’t tackle burnout alone.

“Mental health is a company-wide imperative that executives, HR departments and all people leaders should play an active role in addressing,” he said.

CISO Zoom burnout

7 Steps From Burnout to Happiness

InfoSec Threats | InfoSec books | InfoSec tools | InfoSec services

Tags: cybersecurity burnout


Mar 09 2023

ChatGPT for Offensive Security

Category: AI — DISC @ 10:39 am

ChatGPT for Offensive Security – via SANS Institute

Can ChatGPT (AI) be used for offensive security?

It is possible to use AI for offensive security, just as it is possible to use any technology for malicious purposes. However, the use of AI for offensive security raises significant ethical concerns and legal considerations.

AI could be used to automate and scale attacks, such as phishing, malware propagation, or social engineering. It could also be used to analyze large amounts of data to identify vulnerabilities or weaknesses in security systems, and to develop targeted attacks.

However, the use of AI for offensive security could also have unintended consequences, such as collateral damage or false positives. Furthermore, it raises concerns about accountability and responsibility, as it may be difficult to trace the origin of an attack that is automated and conducted by a machine learning system.

Overall, the use of AI for offensive security is a complex and controversial issue that requires careful consideration of the ethical and legal implications. It is important to always use technology responsibly and ethically.

Chat GPT is just the tip of the iceberg! 15 Artificial Intelligence tools that may be useful to you:
1.Midjourney: a tool that creates images from textual descriptions, similar to OpenAI’s DALL-E and Stable Diffusion.
2. RunwayML: Edit videos in real time, collaborate and take advantage of over 30 magical AI tools.
3. Otter AI: Transform audio into text with high accuracy. Use this tool for meeting notes, content creation and much more.
4. Copy.AI: This is the first copyright platform powered by artificial intelligence. This tool helps generate content for websites, blog posts, or social media posts, helping increase conversions and sales.
5. Murf AI: Convert text to audio: generate studio-quality narrations in minutes. Use Murf’s realistic AI voices for podcasts, videos and all your professional presentations.
6. Flow GPT: Share, discover and learn about the most useful ChatGPT prompts.
7. Nocode.AI: The Nocode platform is a way to create AI solutions without ever writing a single line of code. It’s a great way to quickly test ideas, create new projects, and launch businesses and new products faster.
8. Supernormal: This tool helps create incredible meeting notes without lifting a finger.
9. TLDRthis: This AI-based website helps you summarize any part of a text into concise and easy-to-digest content, so that you can rid yourself of information overload and save time.
10. TheGist: Summarize any Slack channel or conversation with just one click! This AI analyzes Slack conversations and instantly creates a brief summary for you.
11. Sitekick: Create landing pages with AI by telling it what you want via text.
12. Humanpal: Create Avatars with ultra-realistic human appearances!
13. ContentBot: – Write content for articles, ads, products, etc.
14. Synthesia – Create a virtual presenter that narrates your text for you.
Synthesia is a video creation platform using AI. It’s possible to create videos in 120 languages, saving up to 80% of your time and budget.
15. GliaCloud: This tool converts your text into video. Generate videos for news content, social media posts, live sports events, and statistical data in minutes.

The role of human insight in AI-based cybersecurity

Employees Are Feeding Sensitive Biz Data to ChatGPT, Raising Security Fears

The Art of Prompt Engineering with chatGPT: A Hands-On Guide for using chatGPT

Previous posts on AI

InfoSec Threats | InfoSec books | InfoSec tools | InfoSec services

Tags: AI-based cybersecurity, ChatGPT, human insight, Offensive security


Mar 08 2023

What Are The 4 Main Roles Of A SIEM?

Category: SIEM — DISC @ 9:26 am

With the rise of online commerce, digital marketing, online data storage and internet communication, big and small businesses should already know the importance of cybersecurity. Statistics report that more than 50% of cyberattacks happen every week to different companies worldwide. Inadequate cybersecurity precautions can increase the risk of a company losing its customers’ sensitive or confidential data and security breaches. For this reason, entrepreneurs and business owners from all industries must implement a robust security information and event (SIEM) strategy in their companies.

What Is SIEM?

SIEM is a technological security solution that provides a comprehensive view of all data and activities happening in an IT infrastructure. It monitors network activities and detects unusual or suspicious behaviours to mitigate cyberattacks. With many businesses expanding their IT systems and networks, new risks emerge with this upgrade. These risks often include potential breach compliance and increased susceptibility to cybercriminals.

You must have an efficient Security Operations Center (SOC) to implement SIEM technology in your organisation. The SOC is responsible for managing all the security monitoring and analysing the data gathered from the SIEM platform.

Suppose you don’t have a SOC on your side yet. You can work with services like Castra or any managed security operations agency that can work for your company. You’ll work with a team of experts who proactively monitors your business’ security 24/7, giving you peace of mind that your organisation and its highly sensitive data are always protected.

Both the SIEM and SOC are crucial to each other. Without SIEM, the SOC will have difficulty monitoring your company’s IT infrastructure. And without SOC, no experts will be there to analyse the data gathered from the SIEM tool.

What Are The Main Roles Of SIEM?

There’s a lot more to this cybersecurity solution than simply detecting abnormalities and suspicious activities in all your network applications. To learn more, here are the primary roles of SIEM that will significantly benefit your business:

1. Log Collection And Management

SIEM solutions will collect and analyse event data from different sources across your company’s network and IT infrastructure to gain better network visibility. SIEM analyses various applications, external and internal technologies, multiple cloud environments and even logs from different users in real time. This process makes it easier for the SOC or security experts to manage the company’s network flow from one centralised location.

This increase and improvement in network visibility also help reduce false positive alerts. All potential cyber threats and issues are catalogued according to their type, status and severity. This categorisation makes it easier for the security team to identify and review false and true security alerts.

2. Event Correlation and Analytics

Another role that SIEM plays in effective log analysis is employing event correlation, forensics and analytics. These processes are necessary to quickly detect cyberattacks and data breaches in real time and mitigate threats to business security. With this function, SIEM can eliminate the need for manual processes, significantly improving the IT security experts’ mean time to detect (MTTD) and mean time to respond (MTTR) against any cyberattack.

3. Incident Tracking and Security Alerts

SIEM’s centralised network management can be an efficient tool for incident tracking and security alerts. This solution enables security and IT experts to identify and track all entities across all connected applications, devices and users from one platform.

This tool also has customisable and predefined correlation rules where the management or business administrators can be alerted immediately in case of any cyberattack. This way, they can take the necessary actions before the threat worsens into more complicated and dangerous security issues.

For example, SIEM detected a potential cyber threat from one of your employees’ computers. Instead of manually checking the employee’s computer to run some security tests, the SIEM will automatically trigger the alert and employ security controls to stop the suspicious attack from progressing. This significantly minimises the time it takes for the security team to deal with the security concern.

Furthermore, SIEM’s incident management will help ensure that the compromised, corrupted, or attacked data/device will be quarantined, along with its malicious codes. This will prevent the cyberattack from spreading and attacking more devices, avoiding large-scale breaches.

Regardless of how small or big your organisation is, SIEM is highly effective in protecting your network from ever-evolving threats. Most importantly, your company can customise this solution to meet your business’s requirements.

4. Compliance Management and Reporting

Most organisations from different industries must report different forms of regulatory compliance. Since SIEM is an efficient tool for collecting and verifying various data from the company’s entire infrastructure, this makes SIEM a popular choice for retrieving compliance reports.

SIEM can produce real-time compliance reports for various compliance standards. It also reduces the hassle of the security team manually creating reports that are only at risk of inaccuracy.

Conclusion

SIEM allows businesses and organisations to protect their networks and IT infrastructures from various security challenges. Its comprehensive security surveillance and other major roles for your company make SIEM a worthy investment for your organisation.

Security Information and Event Management (SIEM) Implementation

InfoSec Threats | InfoSec books | InfoSec tools | InfoSec services

Tags: SIEM


« Previous Page — Next Page »