InfoSec Compliance & AI Governance For over 20 years, DISC InfoSec has been a trusted voice for cybersecurity professionals—sharing practical insights, compliance strategies, and AI governance guidance to help you stay informed, connected, and secure in a rapidly evolving landscape.
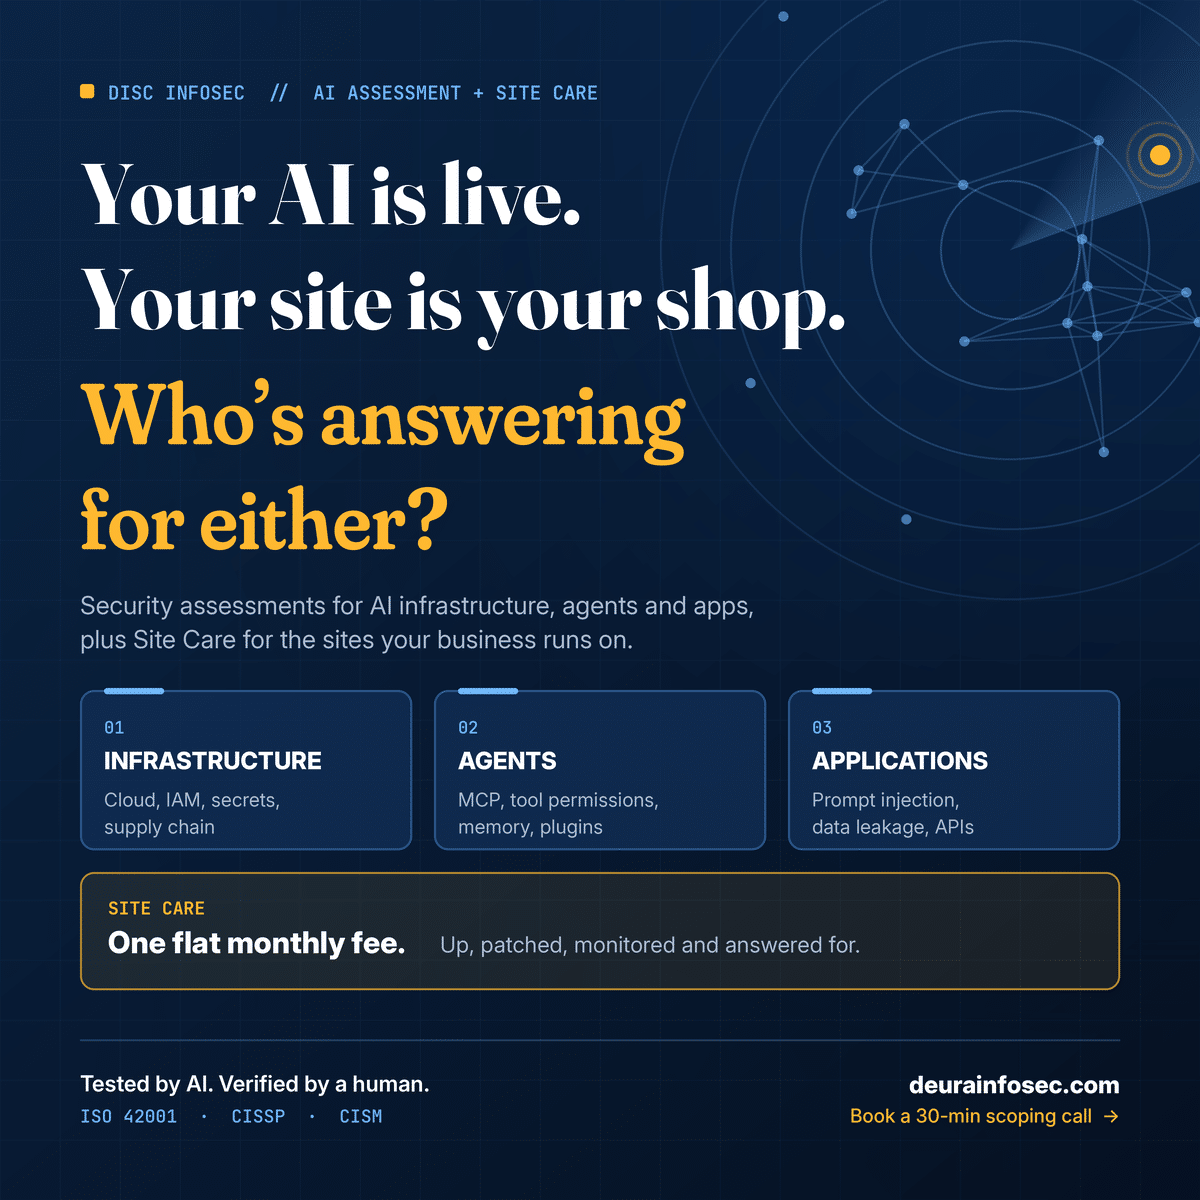
Your AI Is Already in Production. Is It Governed? DISC InfoSec AI Infrastructure, Agents & Applications Assessment
Most small firms didn’t design their AI stack; it piled up. There’s a model API in the website, an agent with inbox access, and a plugin someone installed to solve last Tuesday’s problem. Each one works, and each one opens a door nobody has checked.
DISC InfoSec runs security and AI infrastructure assessments for SMBs. We also build governed AI infrastructure for firms whose name goes on the work: founders, agencies, and research and consulting teams who need AI that fixes this week’s problem without creating next quarter’s liability.
How we test. We run authorized, scoped testing with a modern AI-driven offensive toolkit: Claude Guide for Pentesting, Burp Suite Professional with Burp AI, Microsoft PyRIT, CyberSentinel-AI, CyberStrike, Metatron, PentestCode, SecureSecSuite, SecSuite, Xalgorix, and PenTestSwarmAI. Automation gives us breadth, and a senior practitioner checks every finding, so you get real risk and not scanner noise. AI-assisted testing, vulnerability verification, validation, and report generation.
AI-powered penetration testing tools that leverage AI models to support security assessments, verify and validate vulnerabilities, reduce false positives, and automate technical report generation.
What we cover
Infrastructure: cloud, identity, secrets, and supply chain.
Agents: tool permissions, MCP servers, memory, and third-party plugins, tested against the OWASP Agentic Top 10.
Applications: prompt injection, data leakage, and API and web flaws, tested against the OWASP LLM and Web Top 10.
Governance: alignment with ISO 42001, NIST AI RMF, and the EU AI Act, so your fixes also hold up in customer due diligence.
Site Assurance: Your website is your storefront. Who’s protecting it when you’re not there?
Keep your website secure, updated, monitored, and running smoothly—all for one predictable monthly fee.
Don’t wait for downtime or a security breach to take action. Contact us today for a Site Assurance consultation and discover how affordable proactive website protection can be.
Annual prepay: $2,490 a year, two months free.
Multi-site discount: $249 per site, $199 per site from the third site on.
One-time onboarding fee: around $299 to audit the site.
Sites with ecommerce, logins, or AI features such as chatbots, agents, or forms connected to models carry more risk. Consider a separate “Site Care Plus” around $449, DISC scope them as a project instead of stretching the flat fee to cover them.
Why DISC InfoSec. We led Virtual Data Room to ISO 42001 certification on the first attempt and authored their MCP Governance Standard. Our credentials include AICP, CISSP, CISM, and ISO 42001 and 27001 Lead Implementer. You get enterprise rigor at a size that fits your firm.
Book a 30-minute scoping call: calendly.com/hd-deurainfosec · info@deurainfosec.com
Identify AI Vulnerabilities, Reduce Business Risk, and Prevent Costly Security Incidents.
Download AI Penetration Testing Datasheet to Explore Our Testing Approach and Business Benefits.
AI risk is moving faster than most organizations’ governance programs.
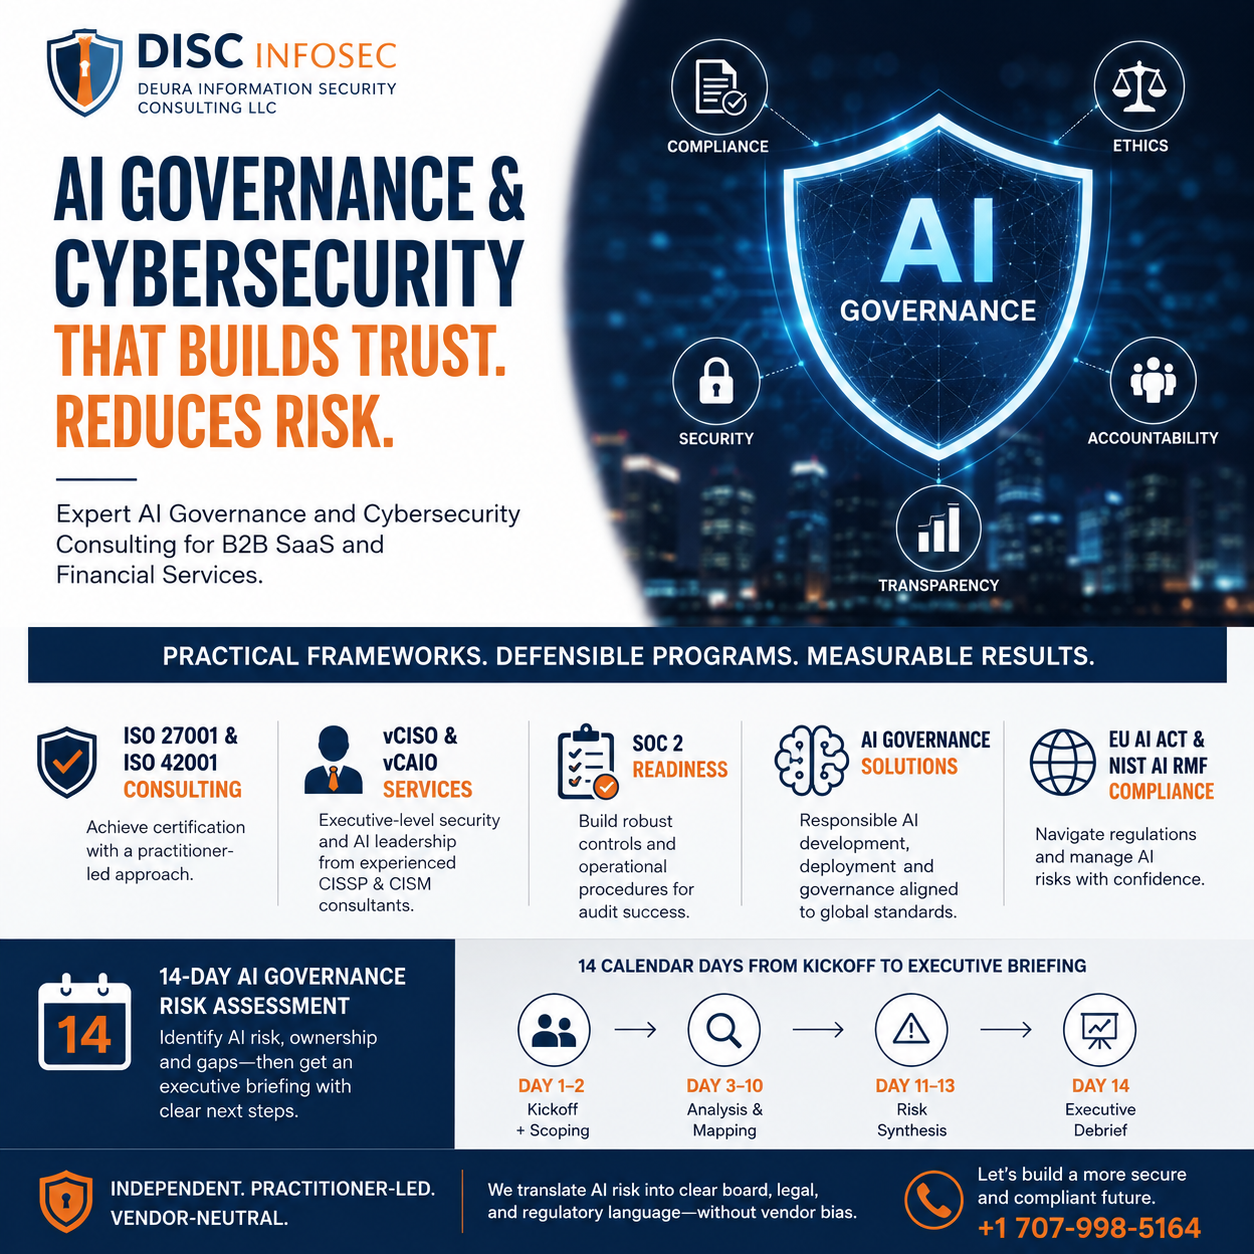
Expert AI Governance and Cybersecurity Consulting
Strengthening B2B SaaS and Financial Services with Robust Compliance Frameworks – DISC InfoSec turn AI governance and cybersecurity requirements into practical, defensible programs—not another stack of policies.
Deura Information Security Consulting LLC provides expert guidance for B2B SaaS and financial services companies seeking to establish practical and defensible security and AI governance programs. We specialize in transforming compliance from a theoretical exercise into an operational reality. Our approach ensures your organization not only meets but exceeds industry standards, building significant customer trust and reducing risk.
Comprehensive AI Governance Services
In an era defined by artificial intelligence, robust governance is not optional. We offer specialized ai governance services to help your business navigate the complexities of AI ethics, accountability, and regulatory requirements. Our consultants implement frameworks that align with your strategic objectives, ensuring responsible and secure AI deployment. We focus on creating sustainable programs that stand up to rigorous scrutiny from auditors and stakeholders.
Mastering NIST AI RMF Compliance
Achieving nist ai rmf compliance is critical for organizations looking to manage risks associated with artificial intelligence systems. Our team provides hands-on consulting to implement the NIST AI Risk Management Framework, helping you identify, assess, and mitigate AI-related risks effectively. We guide you through every step, from building the initial framework to preparing for audits, ensuring your AI systems are trustworthy and secure.
Our Core Consulting Expertise
Deura Information Security Consulting LLC delivers tangible results through a suite of specialized services designed for the modern digital landscape. We move beyond simple documentation, building functioning programs that produce the evidence required for successful certification.
ISO 27001 & ISO 42001 Consulting: We guide companies to successful certification with a practitioner-led approach, including first-audit ISO 42001 certification.
vCISO and vCAIO Services: Access executive-level security and AI leadership from our CISSP and CISM certified consultants with over 20 years of experience.
SOC 2 Readiness: We prepare your organization for SOC 2 audits by building robust security controls and operational procedures.
Holistic Security Programs: Unlike firms that treat compliance as a checkbox, we integrate security and AI governance into the core of your operations.
Specialized AI Compliance Solutions
ISO 42001 Consulting: Achieve certification for the first international standard for AI Management Systems. Our ISO 42001 consulting service helps implement a framework for responsible AI development and deployment.
NIST AI RMF Compliance: Align your AI governance program with the National Institute of Standards and Technology’s framework. We facilitate NIST AI RMF compliance to manage the risks associated with AI technologies.
EU AI Act Compliance: Prepare for the future of AI regulation. Our consulting for EU AI Act compliance ensures your organization is ready to meet the requirements of this landmark legislation.
Why DISC InfoSec
Independent AI Governance & Security Expertise – 20+ years in regulated environments. We translate AI risk into clear board, legal, and regulatory language—without vendor bias. In two weeks, we show leadership where AI risk lives, who owns it, and what must be fixed before AI becomes a liability
Timeline 14 calendar days from kickoff to executive briefing:
Day 1–2: Kickoff + scoping | Day 3–10: Analysis & mapping | Day 11–13: Risk synthesis
Day 14: Executive debrief
Partner with Deura Information Security Consulting LLC for practitioner-level insight and implementation. Contact us at +17079985164 to begin building a more secure and compliant future.
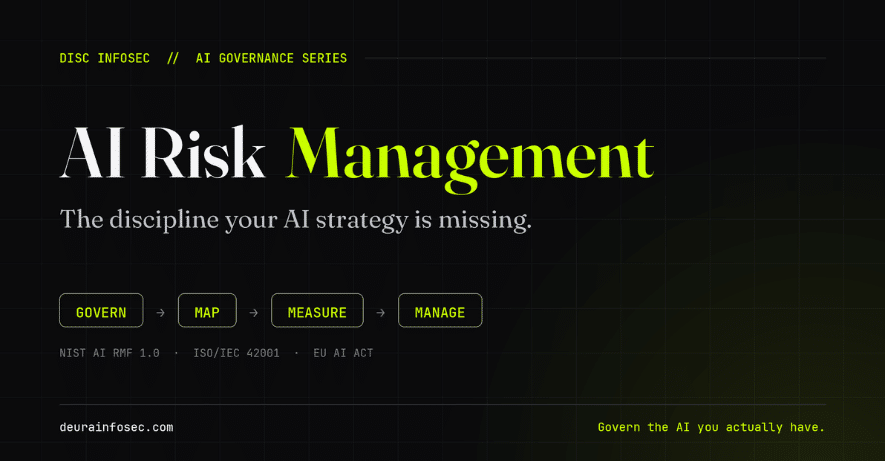
AI Risk Management: The Discipline Your AI Strategy is Missing
Most organizations discovered last year just how much AI they were already running. A customer support chatbot here. Copilot in the IDE. Einstein scoring leads in the CRM. A fraud model someone built in 2021 that nobody owns anymore. When I run AI inventories for clients, the number of AI systems they think they have and the number they actually have are never the same — and the gap is where the risk lives.
That gap is exactly what AI risk management exists to close.
What Is AI Risk Management?
AI risk management is the discipline of identifying, evaluating, and treating the risks that AI systems introduce across their entire lifecycle — not just the security risks, but the fairness, robustness, transparency, privacy, and accountability risks that traditional security programs were never designed to catch.
Here’s the distinction that matters: prompt injection and jailbreaks are the security slice of AI risk. They get the headlines. But the risks that actually put organizations in front of regulators look different. A hiring model that screens out candidates from a protected class. A credit model that’s 95% accurate overall but 60% accurate on the demographic it impacts most. A production LLM that hallucinates a policy your company never had — to a customer, in writing. A model that drifted quietly for eighteen months because nobody was watching, and no one could explain its decisions when a regulator asked.
None of those are breaches. All of them are business-ending risks in the wrong context.
The most widely adopted framework for managing this is the NIST AI Risk Management Framework (AI RMF 1.0). It’s voluntary, but it has become the lingua franca of AI risk — cited in contracts, RFPs, executive orders, and increasingly in customer security questionnaires. If you speak NIST CSF, the shape will feel familiar. The AI RMF organizes the work into four functions:
GOVERN is the persistent layer: written AI principles, a named AI risk owner, approval gates for high-impact deployments, and — critically — someone with the authority to stop a deployment. If nobody in your organization can say “no” to an AI system, you don’t have governance. You have hope.
MAP establishes context per system: what does this AI actually do, who does it affect, what does “broken” look like, and — the question I find most clarifying in practice — is the decision reversible? A spam filter making a wrong call is an annoyance. A mortgage denial is not.
MEASURE is where the engineering happens: accuracy evaluated on data slices rather than aggregates, fairness metrics (demographic parity, equalized odds, calibration — which conflict, and choosing among them is a governance decision, not a technical one), robustness against adversarial inputs and distribution shift, and explainability. A model you cannot explain is a model you cannot defend in a regulatory inquiry.
MANAGE treats what MEASURE surfaces: retrieval-augmented generation for hallucination, monitoring and scheduled retraining for drift, human-in-the-loop for high-stakes decisions, vendor risk reviews for third-party models — and a decommissioning plan for every model, because an unowned production model is the AI equivalent of an unmaintained dependency.
Layer the regulatory landscape on top — the EU AI Act with its risk tiers and phased enforcement, the Colorado AI Act, NYC’s bias audit law for automated hiring tools, FTC and EEOC enforcement authority — and the picture is clear: AI risk management is no longer optional for any organization deploying AI in consequential decisions.
My Perspective: What a Proper AI Risk Management Program Actually Buys You
I led the ISO 42001 AI Management System implementation at ShareVault, a virtual data room platform serving M&A and financial services clients — an environment where the data is deal-sensitive and the tolerance for AI failure is effectively zero. Taking that program through a successful Stage 2 audit taught me what separates AI risk management as a paper exercise from AI risk management as a working system. Here’s what a proper program delivers:
It converts unknown risk into managed risk. The inventory step alone is worth the engagement. You cannot govern what you haven’t cataloged, and shadow AI — the tools employees adopted without review — is present in every organization I’ve assessed. Visibility precedes control, always.
It prevents the expensive failures, not just the embarrassing ones. Biased outcomes in hiring or credit carry regulatory penalties, litigation exposure, and remediation costs that dwarf the price of evaluating the model before deployment. Fairness testing during MEASURE costs days. A disparate-impact claim costs years.
It turns compliance from a scramble into a byproduct. Organizations with a working AI RMF-aligned program aren’t rebuilding from scratch when the EU AI Act’s high-risk requirements apply to them, or when a state law lands, or when an enterprise customer’s due-diligence questionnaire asks how they govern AI. The documentation, the impact assessments, the human oversight mechanisms — they already exist. Frameworks like NIST AI RMF and ISO 42001 map cleanly onto each other and onto the regulations. Build once, answer everywhere.
It becomes a sales asset. This is the part most organizations underestimate. In B2B — especially financial services — your customers’ risk teams are now asking about your AI. Being able to hand over an AI system inventory, model documentation, and evidence of independent audit doesn’t just pass procurement. It shortens sales cycles. At ShareVault, ISO 42001 certification became a differentiator precisely because the market is full of AI claims and short on AI evidence.
It lets you move faster, not slower. The counterintuitive one. Teams without governance hesitate on every AI deployment because nobody knows what’s acceptable. Teams with clear approval gates — rigorous review for high-impact systems, lightweight paths for low-impact ones — ship with confidence. Good governance is a throttle, not a brake. Overengineering the process kills it; right-sizing it accelerates everything.
The organizations getting AI risk management right in 2026 aren’t the ones with the thickest policy binders. They’re the ones who treated it as an operating discipline: inventory what you have, understand what it affects, measure what matters, treat what you find, and build the governance layer that keeps it working after the consultants leave.
Leadership must treat regulatory security, privacy & AI compliance as a strategic risk management priority. Noncompliance can lead to financial penalties, litigation exposure, reputational damage, and loss of customer trust. Top management should ensure that security, privacy & AI compliance risks are incorporated into enterprise risk assessments, evaluated using risk-based decision-making frameworks, reported regularly to executive leadership and governing bodies, and addressed through mitigation strategies aligned with organizational risk tolerance.
The ones getting it wrong will find out the way organizations always find out — in production, in public, or in front of a regulator.
HD is Principal Consultant at DISC InfoSec, a boutique cybersecurity and AI governance consultancy. He holds CISSP, CISM, AICP, ISO 27001 Lead Implementer, and ISO 42001 credentials, and led the ISO 42001 AIMS implementation and internal audit at ShareVault through a successful Stage 2 certification audit.
If your organization is deploying AI and can’t yet answer “how do you govern it?” — let’s talk. Book a consultation: info@deurainfosec.com
This is the AI RMF gap assessment, not the checklist version. Most write-ups treat GOVERN, MAP, MEASURE, and MANAGE as four boxes to tick. In practice, the interesting failure isn’t which box is empty — it’s the pattern across the boxes. That pattern is what tells you whether your AI program is actually managing risk or just documenting that it thought about risk once.
The trap: treating AI RMF like a checklist
NIST AI RMF 1.0 is voluntary and non-prescriptive by design. That flexibility is the point — it’s supposed to flex to your context, your risk tolerance, your regulatory exposure. But voluntary frameworks have a predictable failure mode: organizations write the GOVERN policy, feel the box getting checked, and stop.
Nineteen categories across four functions look like a checklist. They’re not. They’re a chain. And chains break at the weakest link, not the first one.
The four functions, in the order risk actually moves through them
Function
What it does
The practitioner question
GOVERN
Sets accountability, roles, and risk tolerance — underpins everything else
Who actually owns this when it breaks?
MAP
Establishes context before a system ships — intended use, stakeholders, foreseeable misuse
What did we assume this AI system would not be used for?
MEASURE
Applies quantitative and qualitative tools to assess risk across the lifecycle
Are we measuring drift, or just measuring at launch?
MANAGE
Prioritizes, resources, and actions the response — then feeds lessons back to GOVERN
Does anything we learn in production change the policy?
Most organizations can point to artifacts for GOVERN. Far fewer can show a MAP document for a specific deployed AI system. Almost none have MEASURE instrumented as an ongoing signal rather than a one-time test.
The gap pattern that actually predicts failure
Here’s the part the generic AI RMF explainer post skips: which combination of strong/weak functions you have tells you why your program is weak, not just that it’s weak.
What we see in the field
What’s really going on
Where to focus first
GOVERN complete, MAP/MEASURE weak
Policy was written, never operationalized against a real system
Run a system-level risk assessment (MAP) on your highest-exposure AI use case — not a hypothetical one
MAP done, MEASURE absent
Risk was identified in a workshop, never instrumented
Define metrics for each identified risk and put monitoring behind them
MEASURE present, no MANAGE action
You’re collecting data nobody owns
Assign a risk owner and a review date to every metric that’s tracked
Engineering-led program with no outside perspective
Bring legal, ethics, or affected-user perspective into MAP 3 and MEASURE 2
No lifecycle coverage
Only deployment gets attention
Extend coverage back to design/development and forward to decommission
If you recognize your organization in the first row — GOVERN strong, everything else thin — that’s not a failed program. That’s a program that stopped at the easiest 20%.
Financial services is the hard mode of AI RMF, not the easy mode
Every AI RMF post talks about bias in hiring algorithms. Financial services has that problem and three others stacked on top of it:
Credit decision fairness — disparate impact analysis isn’t optional; it’s tested against the EEOC’s four-fifths rule, and adverse action notices have to be explainable to a person, not just accurate to a model.
Explainability under legal obligation — ECOA and CFPB guidance mean MEASURE 2 (“system evaluated for trustworthiness”) isn’t a nice-to-have property, it’s the difference between a defensible decision and a discrimination claim.
Fraud model drift — a fraud-detection model that was 94% accurate at launch and hasn’t been re-measured since is a MEASURE 3 gap with a very expensive failure mode.
For a platform handling M&A due diligence or financial data rooms, the stakes compound further: the AI risk profile has to sit on top of an existing confidentiality and access-control posture, not replace it.
Building the profile: current state vs. target state
The mechanism that actually closes gaps is simpler than the framework makes it look:
Scope — pick the AI systems in scope. Not “all AI, eventually.” One system, real and deployed.
Rate current state — for each of the 19 categories: Not Started (0) → Partial (1) → Implemented (2) → Optimized (3).
Set target state — driven by regulatory exposure and risk tolerance, not aspiration.
Gap = Target minus Current. Anywhere that’s positive is where the roadmap lives.
Weight by risk, not by ease. The gap that’s easiest to close isn’t necessarily the one that matters.
Most organizations we assess land at Implementation Tier 1 or 2 — ad hoc or risk-informed. Tier 3 (Repeatable) is the realistic target for a regulated environment. Tier 4 (Adaptive) is for organizations where AI is the product, not a feature.
Why AI RMF pairs with ISO 42001 instead of competing with it
AI RMF is voluntary; it doesn’t get you a certificate. ISO/IEC 42001 does. The two aren’t rival frameworks — AI RMF is the risk methodology; ISO 42001 is the management system that makes it auditable.
Concretely: GOVERN 1 (policies in place) maps to ISO 42001 Clause 5 and Annex A.2. MEASURE 3 (ongoing monitoring) maps to Clause 9.1. If you’re already running an ISMS under ISO 27001, this isn’t a parallel program — it’s an extension with about 70% conceptual overlap and a genuinely new 30% around bias, explainability, and AI-specific incident response.
That’s the sequence that actually gets audited in production: AI RMF gives you the risk logic; ISO 42001 gives you the certifiable structure to prove you’re running it.
The one-sentence version
If your AI governance program can describe its policy but can’t name the owner, the metric, and the last review date for a single deployed AI system — you don’t have a gap in one function. You have a program that only did the part that doesn’t get tested.
Building or auditing an AI risk management program against NIST AI RMF, ISO 42001, or the EU AI Act? That’s the work — happy to talk through where your program actually stands.
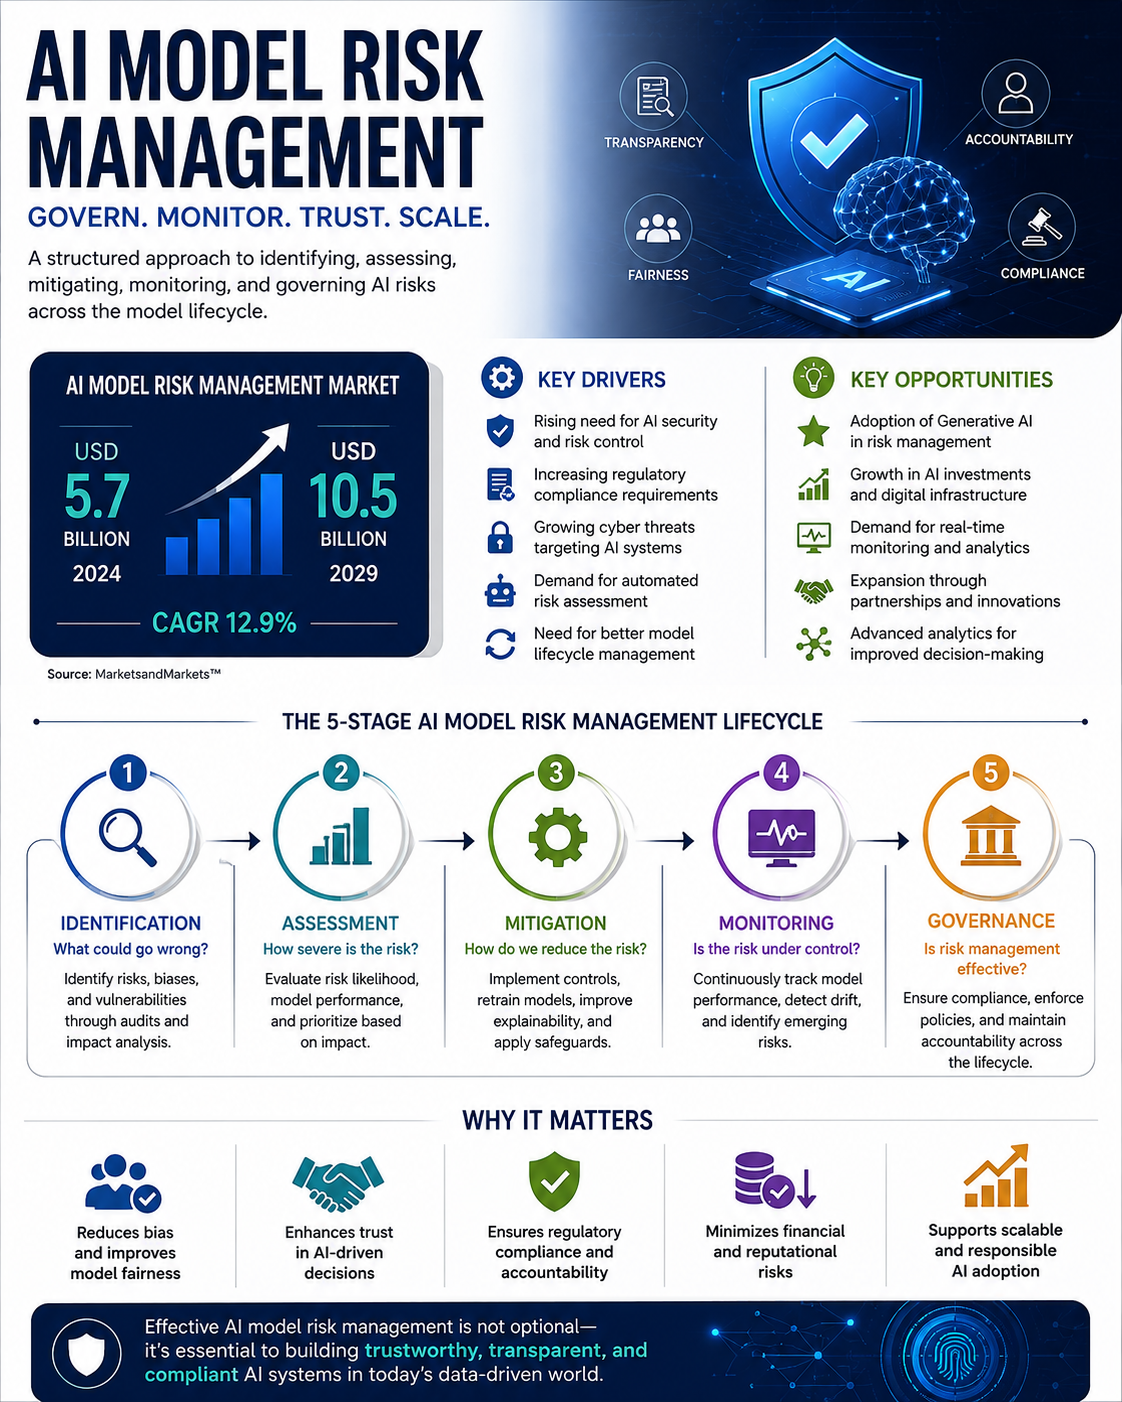
As enterprise AI adoption accelerates, AI Model Risk Management is rapidly becoming one of the most important disciplines in modern governance, risk, and compliance programs. Organizations are no longer experimenting with isolated AI models — they are deploying AI across critical business operations, customer interactions, analytics, automation, and decision-making systems. With that scale comes a new category of operational, regulatory, and security risk that cannot be ignored.
The market momentum reflects this shift. The AI Model Risk Management market is projected to grow from USD 5.7 billion in 2024 to USD 10.5 billion by 2029, representing a strong CAGR of 12.9%. This growth highlights a broader reality: organizations now recognize that AI innovation without governance creates significant exposure across compliance, cybersecurity, reputational trust, and business resilience.
Several major drivers are accelerating investment in AI risk management programs. Security leaders are facing increasing cyber threats targeting AI systems, including model manipulation, prompt injection, data poisoning, and unauthorized model access. At the same time, regulators worldwide are introducing stricter AI governance requirements focused on transparency, accountability, explainability, and ethical AI deployment.
Another major factor is the growing need for automated risk assessment and lifecycle visibility. AI models are dynamic systems that evolve over time, making continuous oversight essential. Without proper controls, organizations risk model drift, inaccurate predictions, biased outcomes, compliance failures, and operational instability that can directly impact business performance and customer trust.
The rise of Generative AI and agentic AI systems is also creating new opportunities and new governance challenges. Organizations are investing heavily in AI-powered decision support, copilots, autonomous workflows, and intelligent automation. These technologies offer enormous business value, but they also introduce complex risks around data privacy, hallucinations, excessive permissions, intellectual property exposure, and accountability gaps.
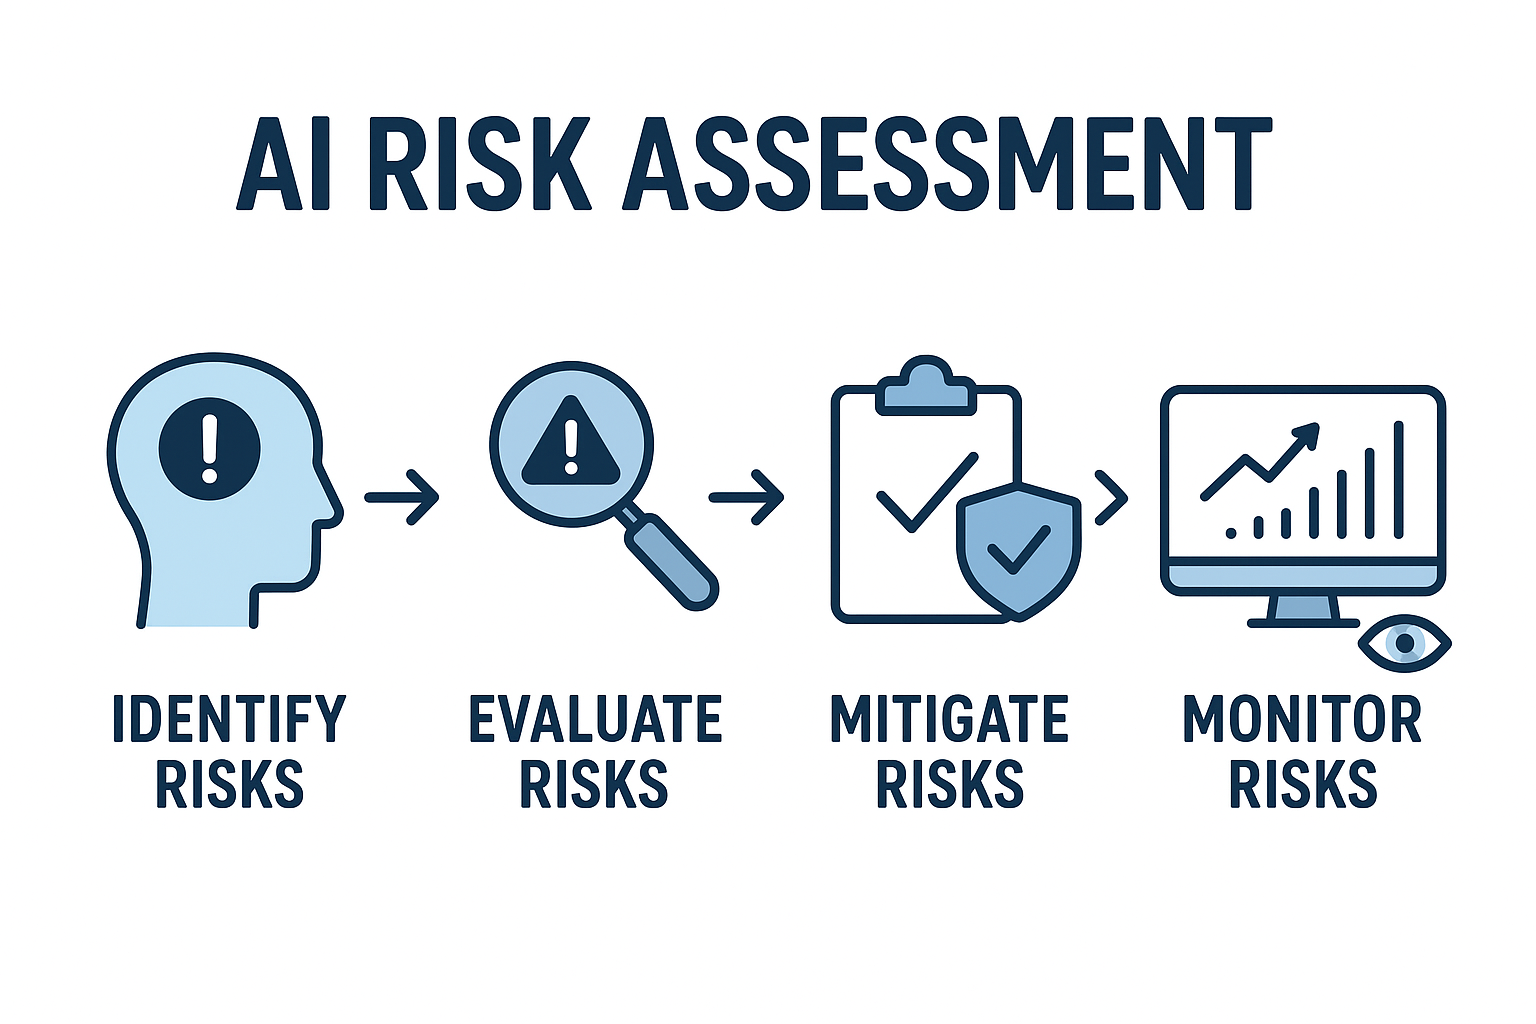
A strong AI Model Risk Management program typically follows a structured five-stage lifecycle approach. The first stage is Identification — understanding what could go wrong. This includes identifying vulnerabilities, ethical concerns, model weaknesses, bias risks, and business impact through assessments, audits, and impact analysis.
The second stage is Assessment, where organizations evaluate the severity, likelihood, and operational impact of identified risks. This step helps prioritize remediation efforts while measuring model reliability, explainability, resilience, and alignment with business objectives and regulatory expectations.
The third stage is Mitigation, which focuses on reducing risk through safeguards and controls. Organizations may retrain models, improve data quality, implement human oversight, strengthen explainability, apply access controls, and establish governance guardrails to minimize exposure and improve trustworthiness.
The fourth and fifth stages — Monitoring and Governance — are where mature AI programs separate themselves from basic AI deployments. Continuous monitoring helps detect model drift, abnormal behavior, and emerging threats in real time, while governance ensures policies, accountability, compliance obligations, and executive oversight remain active throughout the AI lifecycle.
Effective AI Model Risk Management ultimately delivers measurable business value. It reduces bias, strengthens trust in AI-driven decisions, improves compliance readiness, minimizes financial and reputational exposure, and enables organizations to scale AI responsibly with confidence. In today’s environment, AI governance is no longer a theoretical discussion — it is becoming a board-level business requirement.
My perspective: Many organizations are still approaching AI governance as a documentation exercise instead of an operational discipline. The companies that will succeed with AI over the next five years will be the ones that treat AI governance like cybersecurity — continuous, measurable, risk-based, and integrated directly into business operations. AI risk management is no longer optional; it is becoming the foundation for trustworthy and sustainable AI adoption.
DISC InfoSec is an active ISO 42001 implementer and PECB Authorized Training Partner specializing in AI governance for B2B SaaS and financial services organizations.
The risk management process is designed to help organizations systematically identify, assess, prioritize, and mitigate risks related to AI systems throughout the entire AI lifecycle. It is part of the broader AI governance capabilities of the GRC platform, which supports compliance with frameworks like ISO 42001, ISO 27001, the EU AI Act, and the NIST AI RMF.
Below is a clear breakdown of the core steps in the GRC platform risk management process.
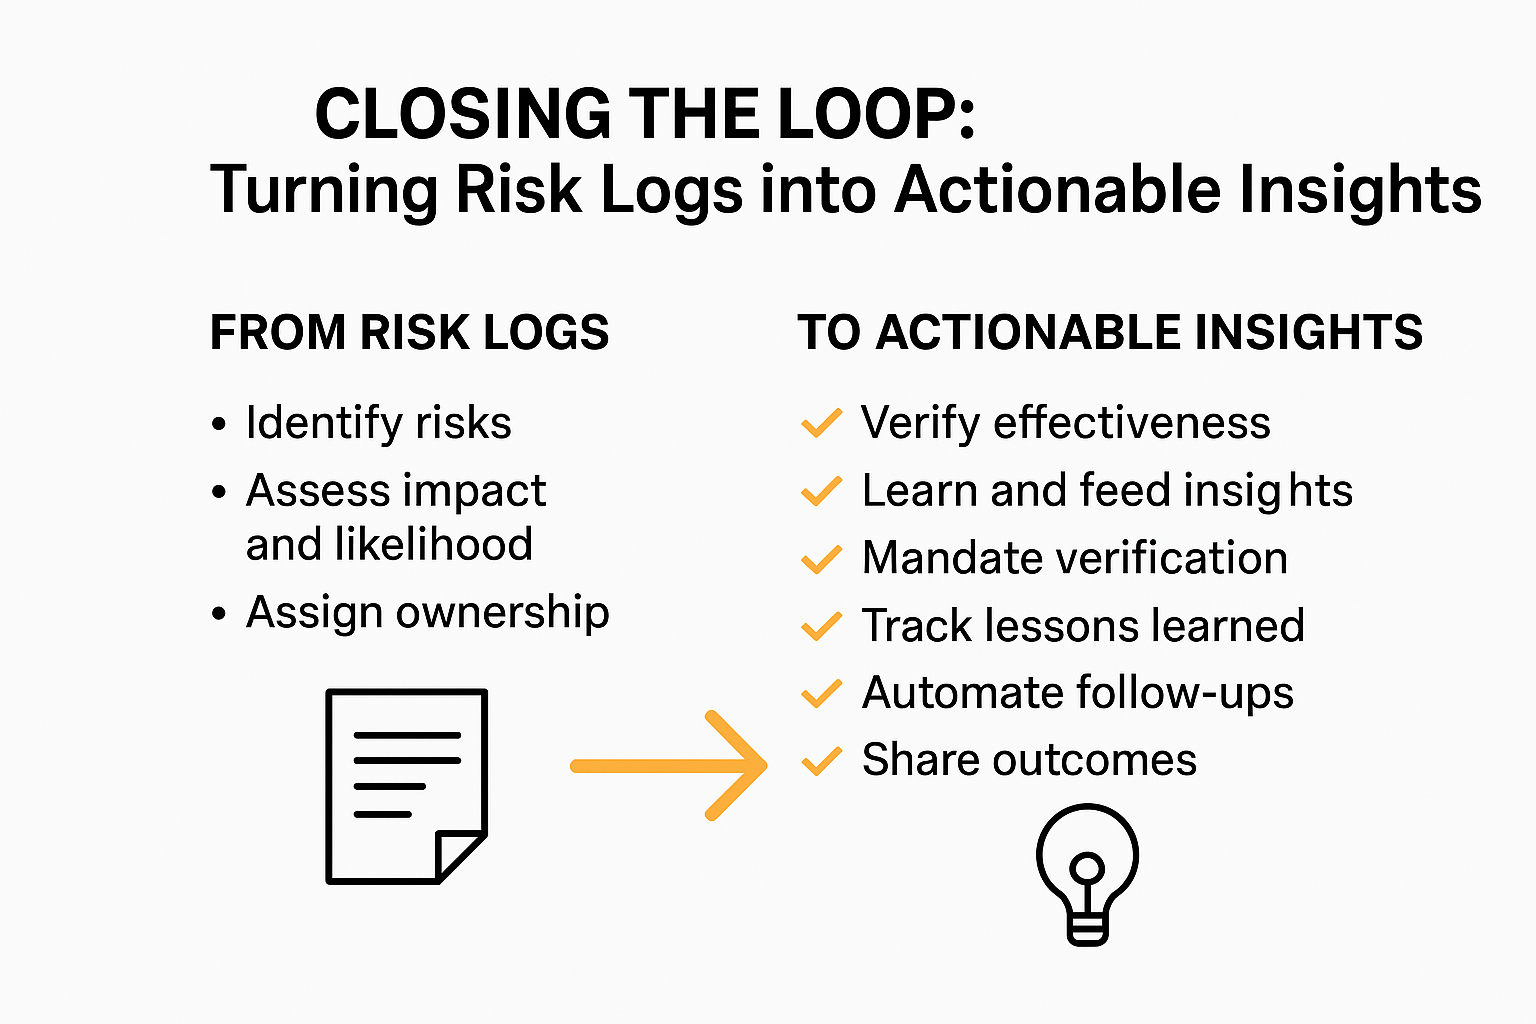
1. Risk Identification
The process begins by identifying risks across AI projects, models, and vendors. These risks may include issues such as bias in training data, model failures, security vulnerabilities, regulatory non-compliance, or third-party vendor risks.
GRC platform centralizes all identified risks in a unified risk register, which provides a single view of risks across the organization.
Typical information captured includes:
Risk name and description
AI lifecycle phase (design, training, deployment, etc.)
Potential impact
Risk category
Assigned owner
This step ensures that AI risks are visible and documented rather than scattered across spreadsheets or emails.
2. Risk Assessment
Once risks are identified, they are evaluated based on likelihood and severity.
GRC platform automatically calculates a risk score using a weighted formula:
Risk Score = (Likelihood × 1) + (Severity × 3)
This method intentionally weights severity three times higher than probability, ensuring that high-impact risks are prioritized even if they seem unlikely.
The resulting score maps to six risk levels:
No Risk
Very Low
Low
Medium
High
Very High
This structured scoring allows organizations to prioritize the most critical AI risks first.
3. Risk Classification
GRC platform organizes risks into three main categories to improve governance and traceability:
Project Risks – Risks related to the AI system or use case itself.
Model Risks – Risks related to algorithm performance, bias, or failure.
Vendor Risks – Risks associated with third-party AI tools or providers.
This three-dimensional risk tracking approach allows organizations to understand where risks originate and how they propagate across the AI ecosystem.
4. Risk Mitigation Planning
After risk evaluation, the next step is to develop a mitigation strategy.
Each risk entry includes:
Mitigation plan
Implementation strategy
Responsible owner
Target completion date
Residual risk evaluation
The system tracks mitigation through a structured workflow, ensuring accountability and visibility across teams.
5. Workflow and Approval Process
GRC platform uses a 7-stage mitigation workflow to track progress:
Not Started
In Progress
Completed
On Hold
Deferred
Cancelled
Requires Review
This structured workflow ensures that risk remediation activities are tracked, reviewed, and approved rather than forgotten.
6. Control and Framework Mapping
Each identified risk can be mapped to regulatory or compliance controls, such as:
EU AI Act requirements
ISO 42001 clauses
ISO 27001 controls
NIST AI RMF categories
This mapping provides audit-ready traceability, allowing organizations to demonstrate how specific risks are addressed within governance frameworks.
7. Monitoring and Continuous Improvement
Risk management in GRC platformis continuous rather than one-time.
The platform provides:
Historical risk tracking
Time-series analytics
Risk posture monitoring over time
Organizations can analyze how risk levels evolve as mitigation actions are implemented, improving governance maturity and transparency.
✅ Summary of the GRC platformRisk Management Process
Identify AI risks
Assess likelihood and severity
Calculate risk score and classify risk level
Develop mitigation plans
Assign ownership and track workflow
Map risks to compliance frameworks
Monitor and review risks continuously
💡 My perspective (given your background in security and compliance:
GRC platformessentially applies traditional GRC risk management concepts to AI systems, but with AI-specific risk categories (model, vendor, lifecycle) and framework traceability (ISO 42001, EU AI Act, NIST AI RMF).
The key differentiator is that it treats AI risk as dynamic and lifecycle-based, rather than static like traditional IT risk registers. That approach aligns well with emerging AI governance practices.
How risk management to ISO 42001 Clause 6 (Risk & Opportunity Management) and broader AI governance principles, tailored for organizations managing AI systems:
1. Context Establishment (ISO 42001 Clause 6.1.1)
ISO 42001 requirement: Understand internal and external context, including stakeholders, regulatory requirements, and AI objectives, before managing risks.
GRC platform mapping:
Allows defining AI projects, systems, and stakeholders in a centralized register.
Captures regulatory requirements like EU AI Act, NIST AI RMF, or state AI laws.
Provides a holistic view of AI assets, vendors, and models, ensuring all relevant context is captured before risk assessment.
AI governance impact: Ensures that AI governance decisions are context-aware, not ad hoc.
ISO 42001 requirement: Identify risks and opportunities that could affect the achievement of AI objectives.
GRC platform mapping:
Identifies project, model, and vendor risks across the AI lifecycle.
Risks include bias, security vulnerabilities, regulatory non-compliance, and operational failures.
Supports opportunity identification by noting areas for model improvement, regulatory alignment, or vendor efficiency.
AI governance impact: Ensures that AI systems are proactively monitored for both threats and improvement areas, aligning with responsible AI principles.
3. Risk Assessment & Evaluation (Clause 6.1.3)
ISO 42001 requirement: Assess likelihood and impact of risks and determine priority.
GRC platform mapping:
Calculates risk scores using weighted likelihood × severity formula.
Maps risks to six risk levels (No Risk → Very High).
Provides a prioritized list of risks based on impact and probability.
AI governance impact: Helps organizations focus governance resources on high-impact AI risks, such as models affecting safety, fairness, or regulatory compliance.
ISO 42001 requirement: Determine actions to mitigate risks or exploit opportunities, assign responsibility, and set deadlines.
GRC platform mapping:
Each risk entry includes:
Mitigation plan
Assigned owner
Target completion date
Residual risk evaluation
Tracks mitigation through a 7-stage workflow (Not Started → Requires Review).
AI governance impact: Ensures accountability and traceability in AI risk treatment, meeting governance and audit requirements.
5. Integration into AI Governance (Clause 6.2)
ISO 42001 requirement: Embed risk management into overall AI governance, strategy, and operations.
GRC platform mapping:
Links risks to AI lifecycle phases (design, training, deployment).
Maps each risk to regulatory or framework controls (ISO 42001 clauses, ISO 27001, NIST AI RMF).
Supports continuous monitoring and reporting, integrating risk management into AI governance dashboards.
AI governance impact: Makes risk management a core part of AI governance, not an afterthought.
6. Monitoring & Review (Clause 6.3)
ISO 42001 requirement: Monitor risks, evaluate effectiveness of mitigation, and update as needed.
GRC platform mapping:
Provides time-series analytics and historical tracking of risks.
Flags changes in risk levels over time.
Ensures audit-readiness with documented mitigation history.
AI governance impact: Enables dynamic governance that adapts to model updates, new AI deployments, and regulatory changes.
✅ Summary of Mapping
ISO 42001 Clause
Requirement
GRC platform Feature
AI Governance Benefit
6.1.1 Context
Understand context
Stakeholder, AI system, vendor, regulatory registry
Context-aware AI governance
6.1.2 Identification
Identify risks & opportunities
Project/Model/Vendor risk register
Proactive risk & opportunity capture
6.1.3 Assessment
Evaluate risk likelihood & impact
Risk scoring & prioritization
Focus on high-impact AI risks
6.1.4 Treatment
Mitigate risks / assign ownership
Mitigation plans + workflow
Accountability & traceability
6.2 Integration
Embed in AI governance
Lifecycle & control mapping
Risk mgmt part of governance strategy
6.3 Monitoring
Review & update
Analytics + historical tracking
Continuous governance & audit readiness
💡 Perspective: GRC platform aligns ISO 42001’s structured risk management approach with AI-specific considerations like bias, model failure, and vendor dependency. By integrating risk scoring, workflow management, and framework mapping, it operationalizes risk-based AI governance—a critical requirement for regulatory compliance and responsible AI deployment.
Feel free to reach out to schedule a demo. We’ll walk you through the GRC platform and show how it dynamically supports comprehensive risk management or for that matter any question regarding AI Governance.
Get Your Free AI Governance Readiness Assessment – Is your organization ready for ISO 42001, EU AI Act, and emerging AI regulations?
AI Governance Gap Assessment tool
15 questions
Instant maturity score
Detailed PDF report
Top 3 priority gaps
Click below to open an AI Governance Gap Assessment in your browser or click the image to start assessment.
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
Risk Management Vocabulary: A Comprehensive Overview
Risk management is a structured discipline that enables organizations to identify, assess, and address potential threats before they cause harm. At its broadest level, Total Risk Management (TRM) provides a comprehensive, organization-wide approach to handling all categories of risk, ensuring no threat goes unaddressed. Supporting this is Enterprise Risk Management (ERM), a framework that systematically identifies, assesses, and mitigates risks across every business unit, helping organizations align their risk appetite with strategic objectives. Together, these two approaches form the backbone of a mature risk culture.
To prepare for worst-case scenarios, organizations rely on a Business Continuity Plan (BCP) — a documented strategy for maintaining critical operations during disruptions such as cyberattacks, natural disasters, or system failures. This is further reinforced by ISO 22301, the international standard for business continuity, which provides certified guidelines ensuring that continuity plans are robust, tested, and auditable. On the governance side, the Committee of Sponsoring Organizations (COSO) framework establishes best practices for internal control and risk management, helping organizations build accountability and reduce fraud or operational failures. Complementing this is Operational Risk Management (ORM), which focuses specifically on risks arising from internal processes, human error, and system failures — areas commonly exploited in cybersecurity incidents.
Effective risk management also depends on the right standards and frameworks. ISO 31000 is the globally recognized standard offering universal guidelines for risk management practices, applicable across industries and risk types. The Risk Management Framework (RMF) provides a specific set of criteria and structured steps — particularly relevant in government and regulated industries — for selecting, implementing, and monitoring security controls. These frameworks are complemented by Risk and Control Self-Assessment (RCSA), a process by which teams internally evaluate the effectiveness of their controls and identify gaps in risk exposure, fostering a proactive rather than reactive security posture.
Once risks are identified, they must be documented and tracked. The Risk Register (RR) serves as a centralized record of all identified risks, their owners, likelihood, impact, and treatment status — making it an essential tool for accountability and audit readiness. Risk Assessment (RA) is the analytical process of identifying and evaluating those risks, determining which threats pose the greatest danger based on probability and potential damage. To stay ahead of emerging threats, organizations monitor Key Risk Indicators (KRIs) — quantifiable metrics that signal when risk levels are approaching critical thresholds, enabling early intervention before a risk materializes into a breach or loss.
When risks are identified and evaluated, organizations must act on them through Risk Treatment (RT) — the application of methods such as mitigation, transfer, avoidance, or acceptance to reduce risk to an acceptable level. The effectiveness of these treatments is sustained through Risk Monitoring (RM), which involves the continuous tracking and reviewing of risks to ensure controls remain effective as the threat landscape evolves. Tying everything together, the Risk Management Framework (RMF) ensures that all these processes operate cohesively within a structured governance model.
In summary, these terms collectively define the lifecycle of risk management — from establishing enterprise-wide strategy, to identifying and assessing threats, implementing treatments, and continuously monitoring outcomes. For security professionals, understanding and applying this vocabulary is foundational to building resilient organizations that can withstand, adapt to, and recover from an ever-changing threat environment.
My Perspective on the Risk Management Vocabulary Post
Overall, this is a solid foundational reference — the kind of content that bridges the gap between technical security practitioners and business stakeholders. Here are my honest thoughts:
What It Does Well
The post succeeds in making risk management accessible. By condensing complex frameworks like COSO, ISO 31000, and RMF into digestible definitions, it lowers the barrier for entry-level professionals or non-technical executives who need to speak the language of risk without necessarily being deep practitioners. The visual format of the original infographic also makes it easy to reference quickly — something useful in training or awareness campaigns.
Where It Falls Short
Honestly, the definitions are surface-level at best. Listing what an acronym stands for is not the same as understanding how it functions operationally. For example:
Defining a Risk Register as simply “a centralized record” understates its role as a living governance document that drives accountability, audit trails, and board-level reporting.
KRIs are described as metrics that “identify potential risks,” but their real power lies in being leading indicators — they tell you a risk is developing, not just that it exists. That distinction is critical in a security operations context.
The post treats COSO and ISO 31000 as parallel concepts, when in practice they serve different purposes — COSO is governance and internal control-oriented, while ISO 31000 is a pure risk management process standard. Conflating them can create confusion during actual framework implementation.
The Missing Pieces
From a cybersecurity and AI governance standpoint — which is increasingly where risk management is headed — the post notably omits several critical concepts:
Threat Modeling — arguably more actionable than a generic risk assessment in security contexts
Residual Risk vs. Inherent Risk — a distinction that matters enormously when presenting risk posture to boards or auditors
Risk Appetite and Risk Tolerance — without these, organizations have no objective baseline for deciding what level of risk is acceptable
Third-Party and Supply Chain Risk — one of the most significant and undermanaged risk vectors today, especially relevant for organizations handling sensitive data
AI-specific risk concepts like algorithmic bias, model drift, and data provenance risk — none of which map cleanly onto traditional frameworks like COSO or ISO 31000 without deliberate adaptation
The Bigger Picture
What this post represents is risk management vocabulary without risk management thinking. Knowing what “Risk Treatment” means is useful. Understanding when to accept risk versus transfer it versus mitigate it — and being able to defend that decision to a regulator or client — is what actually builds organizational resilience.
The vocabulary is the starting point, not the destination. For organizations genuinely serious about risk — particularly those in regulated industries like financial services, healthcare, or AI-driven businesses — these terms need to be lived and operationalized, not just defined. A risk register that nobody updates is just a document. A BCP that has never been tested is just a plan on paper.
Bottom line: It’s a useful primer, but practitioners should treat it as a glossary, not a playbook. The real skill in risk management lies in the judgment calls made between the definitions.
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
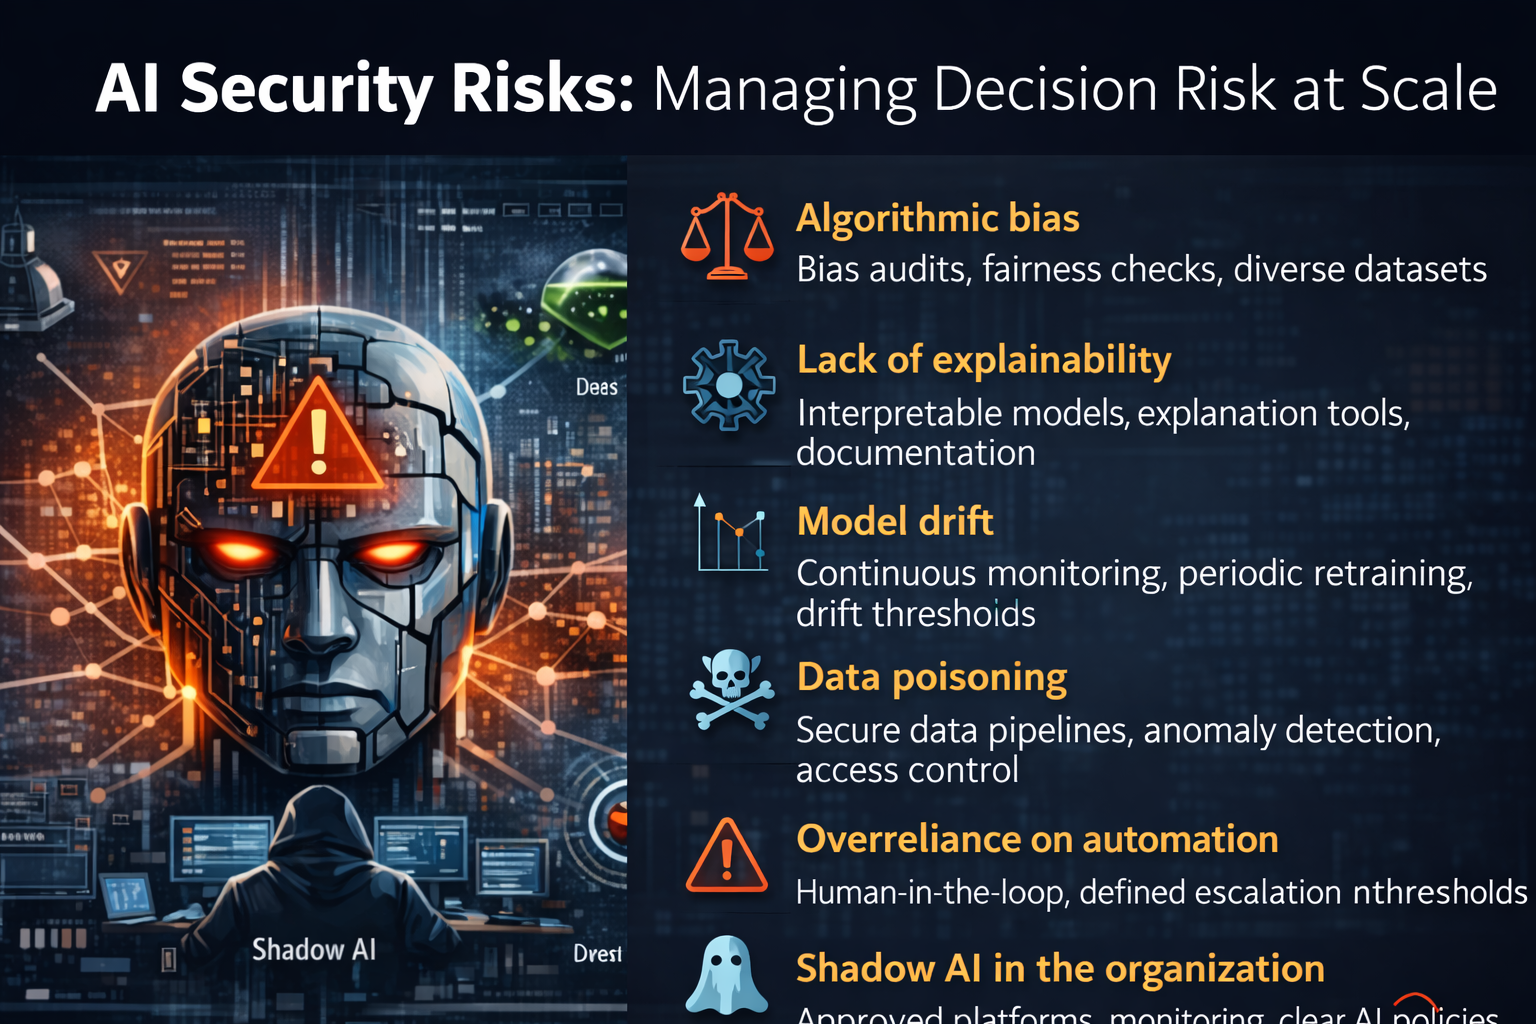
Artificial Intelligence introduces a new class of security risks because it combines data, code, automation, and autonomous decision-making at scale. Unlike traditional software, AI systems continuously learn, adapt, and influence business outcomes — often without full transparency. This creates compounded risk across data integrity, compliance, ethics, operational resilience, and governance. When poorly governed, AI doesn’t just fail quietly; it can amplify errors, bias, and security weaknesses across the enterprise in real time.
Algorithmic bias occurs when models produce systematically unfair or discriminatory outcomes due to biased training data or flawed assumptions. This can expose organizations to regulatory, reputational, and legal risk. Remediation: Implement diverse and representative datasets, conduct bias testing before deployment, perform fairness audits, and establish AI governance committees that review high-impact use cases.
Lack of explainability refers to “black box” models whose decisions cannot be clearly interpreted or justified. This becomes critical in regulated industries where decisions must be defensible. Remediation: Use interpretable models where possible, deploy explainability tools (e.g., SHAP, LIME), document model logic, and enforce transparency requirements for high-risk AI systems.
Model drift happens when model performance degrades over time because real-world data changes from the original training environment. This silently increases operational and decision risk. Remediation: Continuously monitor performance metrics, implement automated retraining pipelines, define drift thresholds, and establish lifecycle governance with periodic validation.
Data poisoning is a security threat where attackers manipulate training data to influence model behavior, potentially creating backdoors or skewed outputs. Remediation: Secure data pipelines, validate data integrity, restrict training data access, use anomaly detection, and implement supply chain security controls for third-party datasets.
Overreliance on automation occurs when organizations defer too much authority to AI without sufficient human oversight. This increases systemic failure risk when models make incorrect or unsafe decisions. Remediation: Maintain human-in-the-loop controls for high-impact decisions, define escalation thresholds, and conduct regular performance and scenario testing.
Shadow AI in the organization mirrors Shadow IT — employees deploying AI tools without governance, security review, or compliance alignment. This creates uncontrolled data exposure and compliance violations. Remediation: Establish clear AI usage policies, provide approved AI platforms, monitor AI-related API traffic, conduct awareness training, and align AI governance with enterprise risk management.
Perspective: AI Risk = Decision Risk at Scale
Traditional IT risk is system risk. AI risk is decision risk — multiplied. AI systems don’t just process data; they make or influence decisions that affect customers, finances, compliance, and operations. When a flawed model is deployed, its errors scale instantly across thousands or millions of transactions. That’s why AI governance is not simply a technical concern — it is a board-level risk issue.
Organizations that treat AI risk as decision governance — integrating security, compliance, model validation, and executive oversight — will reduce loss expectancy while improving operational efficiency. Those that don’t will eventually discover that unmanaged AI doesn’t fail gradually — it fails at scale.
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
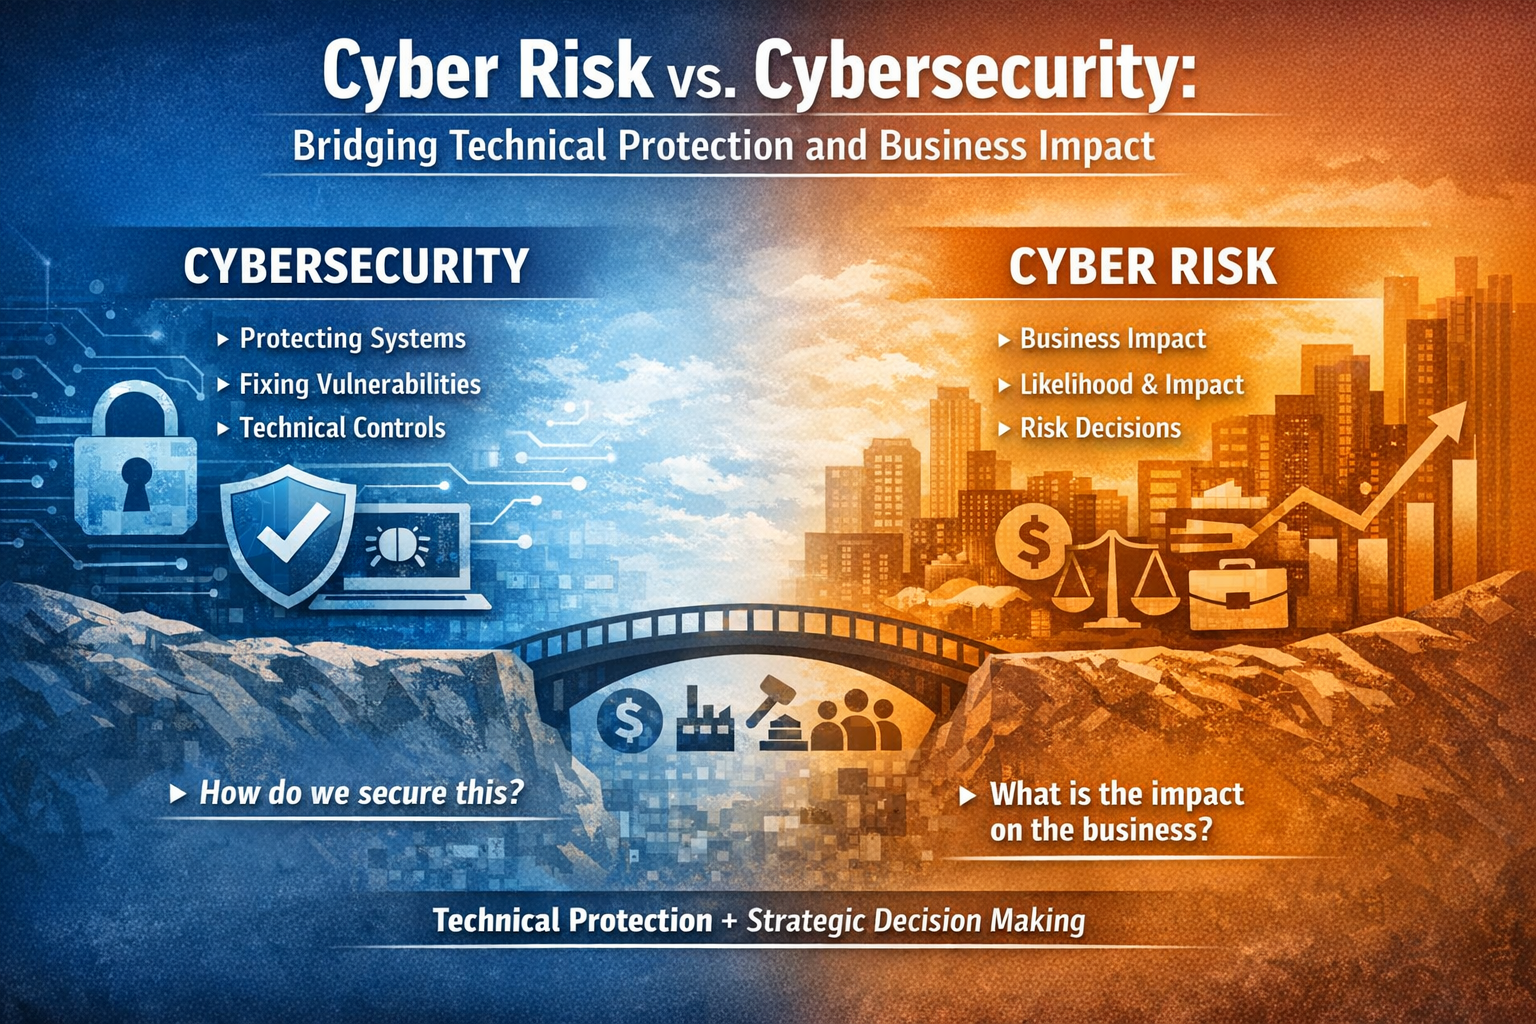
Cybersecurity and cyber risk are closely related, but they operate with different priorities and lenses. Cybersecurity is primarily concerned with defending systems, networks, and data from threats. It focuses on identifying vulnerabilities, applying controls, and fixing technical weaknesses. The central question in cybersecurity is often, “How do we remediate this issue to make the system more secure?” It is action-oriented and technical, aiming to reduce exposure through engineering and operational safeguards.
Cyber risk, in contrast, shifts the conversation from technical fixes to business consequences. It asks, “If this system fails or is compromised, what does that mean for the organization?” This perspective evaluates the likelihood of an event and its potential impact on finances, operations, compliance, and reputation. Not every vulnerability translates into significant business risk, and some of the most serious risks may stem from strategic or process gaps rather than isolated technical flaws. Cyber risk management therefore emphasizes context, prioritization, and tradeoffs, helping leaders decide where to invest resources and which risks are acceptable.
From my perspective, the distinction between cyber risk and cybersecurity represents a maturation of the field. Cybersecurity is essential as the execution arm — it provides the tools and controls that protect assets. Cyber risk is the decision framework that ensures those efforts align with business objectives. Organizations that focus only on cybersecurity can become trapped in an cycle of chasing vulnerabilities without clear prioritization. Conversely, a cyber risk approach connects technical findings to measurable business outcomes, enabling informed decisions at the executive level. The strongest programs integrate both: cybersecurity delivers protection, while cyber risk guides strategy, investment, and governance so the organization can operate confidently amid uncertainty.
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
In the AI-driven era, organizations are no longer just protecting traditional IT assets—they are safeguarding data pipelines, training datasets, models, prompts, decision logic, and automated actions. AI systems amplify risk because they operate at scale, learn dynamically, and often rely on opaque third-party components.
An Information Security Management System (ISMS) provides the governance backbone needed to:
Control how sensitive data is collected, used, and retained by AI systems
Manage emerging risks such as model leakage, data poisoning, hallucinations, and automated misuse
Align AI innovation with regulatory, ethical, and security expectations
Shift security from reactive controls to continuous, risk-based decision-making
ISO 27001, especially the 2022 revision, is highly relevant because it integrates modern risk concepts that naturally extend into AI governance and AI security management.
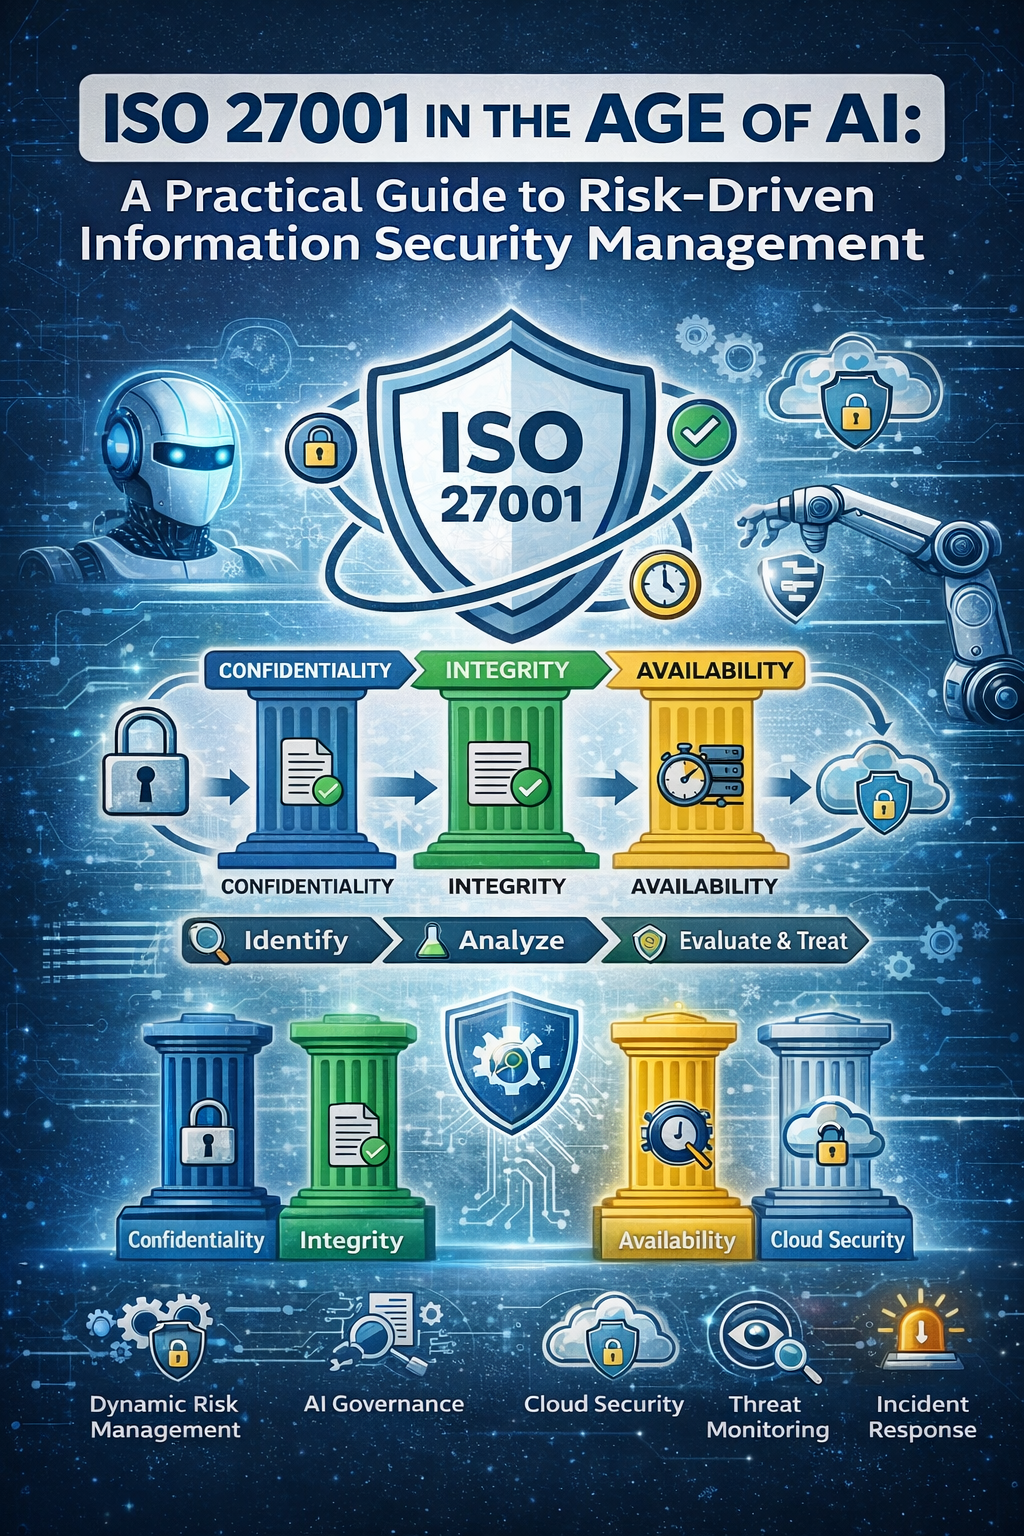
1. Core Philosophy: The CIA Triad
At the foundation of ISO 27001 lies the CIA Triad, which defines what information security is meant to protect:
Confidentiality Ensures that information is accessed only by authorized users and systems. This includes encryption, access controls, identity management, and data classification—critical for protecting sensitive training data, prompts, and model outputs in AI environments.
Integrity Guarantees that information remains accurate, complete, and unaltered unless properly authorized. Controls such as version control, checksums, logging, and change management protect against data poisoning, model tampering, and unauthorized changes.
Availability Ensures systems and data are accessible when needed. This includes redundancy, backups, disaster recovery, and resilience planning—vital for AI-driven services that often support business-critical or real-time decision-making.
Together, the CIA Triad ensures trust, reliability, and operational continuity.
2. Evolution of ISO 27001: 2013 vs. 2022
ISO 27001 has evolved to reflect modern technology and risk realities:
2013 Version (Legacy)
114 controls spread across 14 domains
Primarily compliance-focused
Limited emphasis on cloud, threat intelligence, and emerging technologies
2022 Version (Modern)
Streamlined to 93 controls grouped into 4 themes: People, Organization, Technology, Physical
Strong emphasis on dynamic risk management
Explicit coverage of cloud security, data leakage prevention (DLP), and threat intelligence
Better alignment with agile, DevOps, and AI-driven environments
This shift makes ISO 27001:2022 far more adaptable to AI, SaaS, and continuously evolving threat landscapes.
3. ISMS Implementation Lifecycle
ISO 27001 follows a structured lifecycle that embeds security into daily operations:
Define Scope – Identify what systems, data, AI workloads, and business units fall under the ISMS
Risk Assessment – Identify and analyze risks affecting information assets
Statement of Applicability (SoA) – Justify which controls are selected and why
Implement Controls – Deploy technical, organizational, and procedural safeguards
Employee Controls & Awareness – Ensure roles, responsibilities, and training are in place
Internal Audit – Validate control effectiveness and compliance
Certification Audit – Independent verification of ISMS maturity
This lifecycle reinforces continuous improvement rather than one-time compliance.
4. Risk Assessment: The Heart of ISO 27001
Risk assessment is the core engine of the ISMS:
Step 1: Identify Risks Identify assets, threats, vulnerabilities, and AI-specific risks (e.g., data misuse, model bias, shadow AI tools).
Step 2: Analyze Risks Evaluate likelihood and impact, considering technical, legal, and reputational consequences.
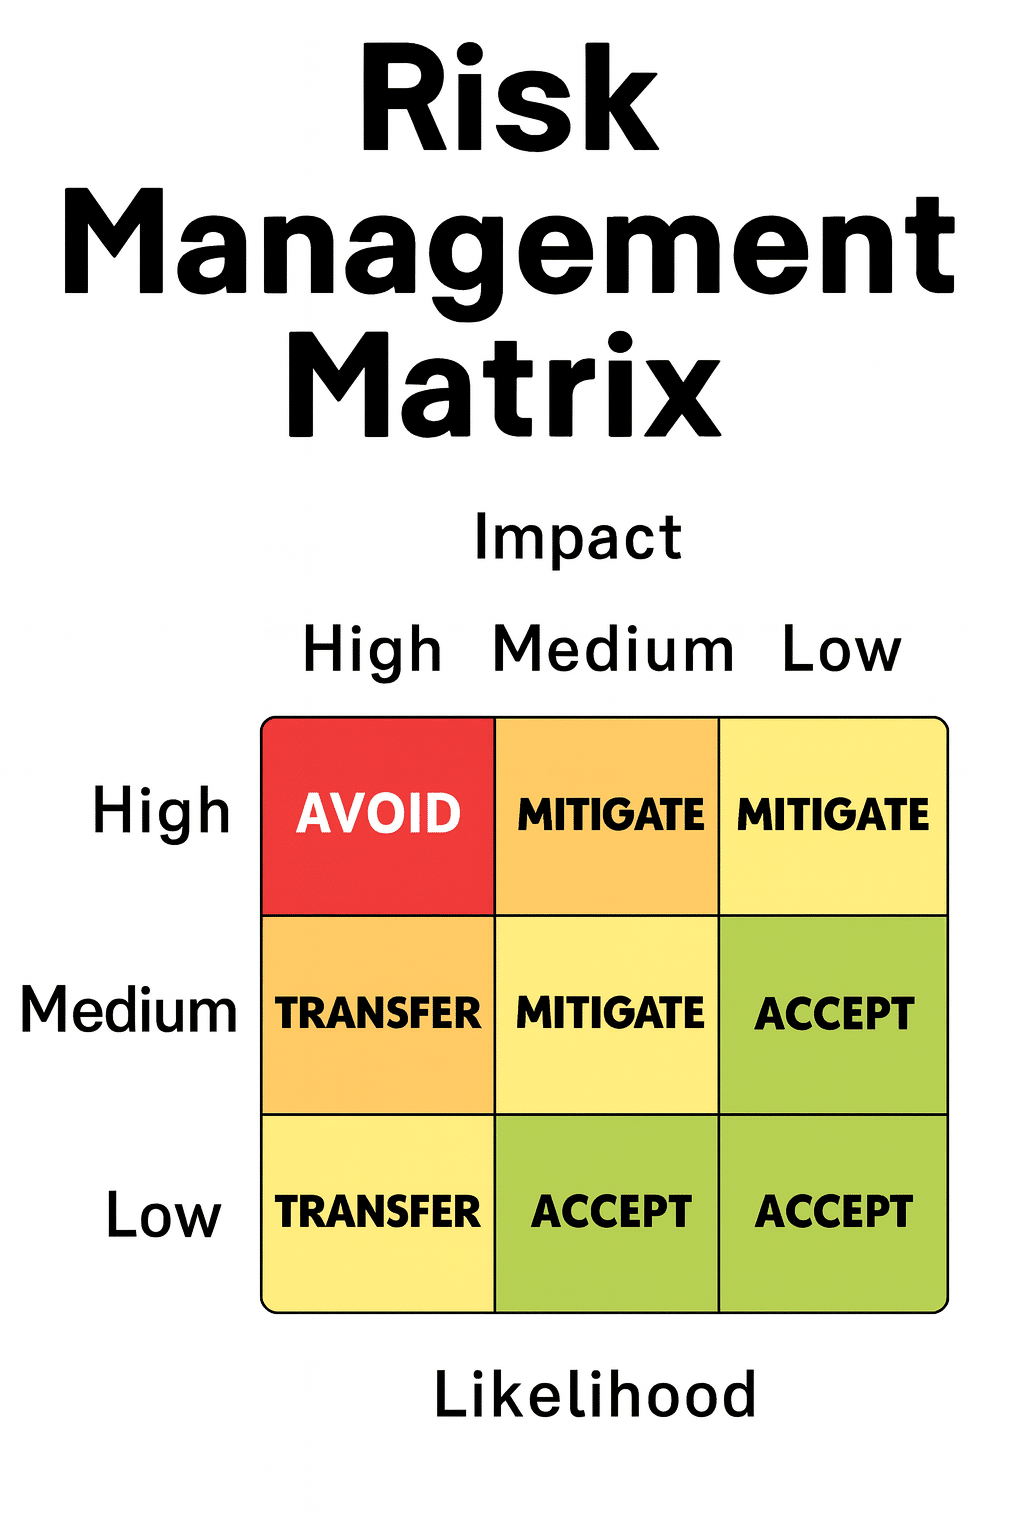
Step 3: Evaluate & Treat Risks Decide how to handle risks using one of four strategies:
Avoid – Eliminate the risky activity
Mitigate – Reduce risk through controls
Transfer – Shift risk via contracts or insurance
Accept – Formally accept residual risk
This risk-based approach ensures security investments are proportionate and justified.
5. Mandatory Clauses (Clauses 4–10)
ISO 27001 mandates seven core governance clauses:
Context – Understand internal and external factors, including stakeholders and AI dependencies
Leadership – Demonstrate top management commitment and accountability
Planning – Define security objectives and risk treatment plans
Support – Allocate resources, training, and documentation
Operation – Execute controls and security processes
Performance Evaluation – Monitor, measure, audit, and review ISMS effectiveness
Improvement – Address nonconformities and continuously enhance controls
These clauses ensure security is embedded at the organizational level—not just within IT.
6. Incident Management & Common Pitfalls
Incident Response Flow
A structured response minimizes damage and recovery time:
Assess – Detect and analyze the incident
Contain – Limit spread and impact
Restore – Recover systems and data
Notify – Inform stakeholders and regulators as required
Common Pitfalls
Organizations often fail due to:
Weak or inconsistent access controls
Lack of audit-ready evidence
Unpatched or outdated systems
Stale risk registers that ignore evolving threats like AI misuse
These gaps undermine both security and compliance.
My Perspective on the ISO 27001 Methodology
ISO 27001 is best understood not as a compliance checklist, but as a governance-driven risk management methodology. Its real strength lies in:
Flexibility across industries and technologies
Strong alignment with AI governance frameworks (e.g., ISO 42001, NIST AI RMF)
Emphasis on leadership accountability and continuous improvement
In the age of AI, ISO 27001 should be used as the foundational control layer, with AI-specific risk frameworks layered on top. Organizations that treat it as a living system—rather than a certification project—will be far better positioned to innovate securely, responsibly, and at scale.
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
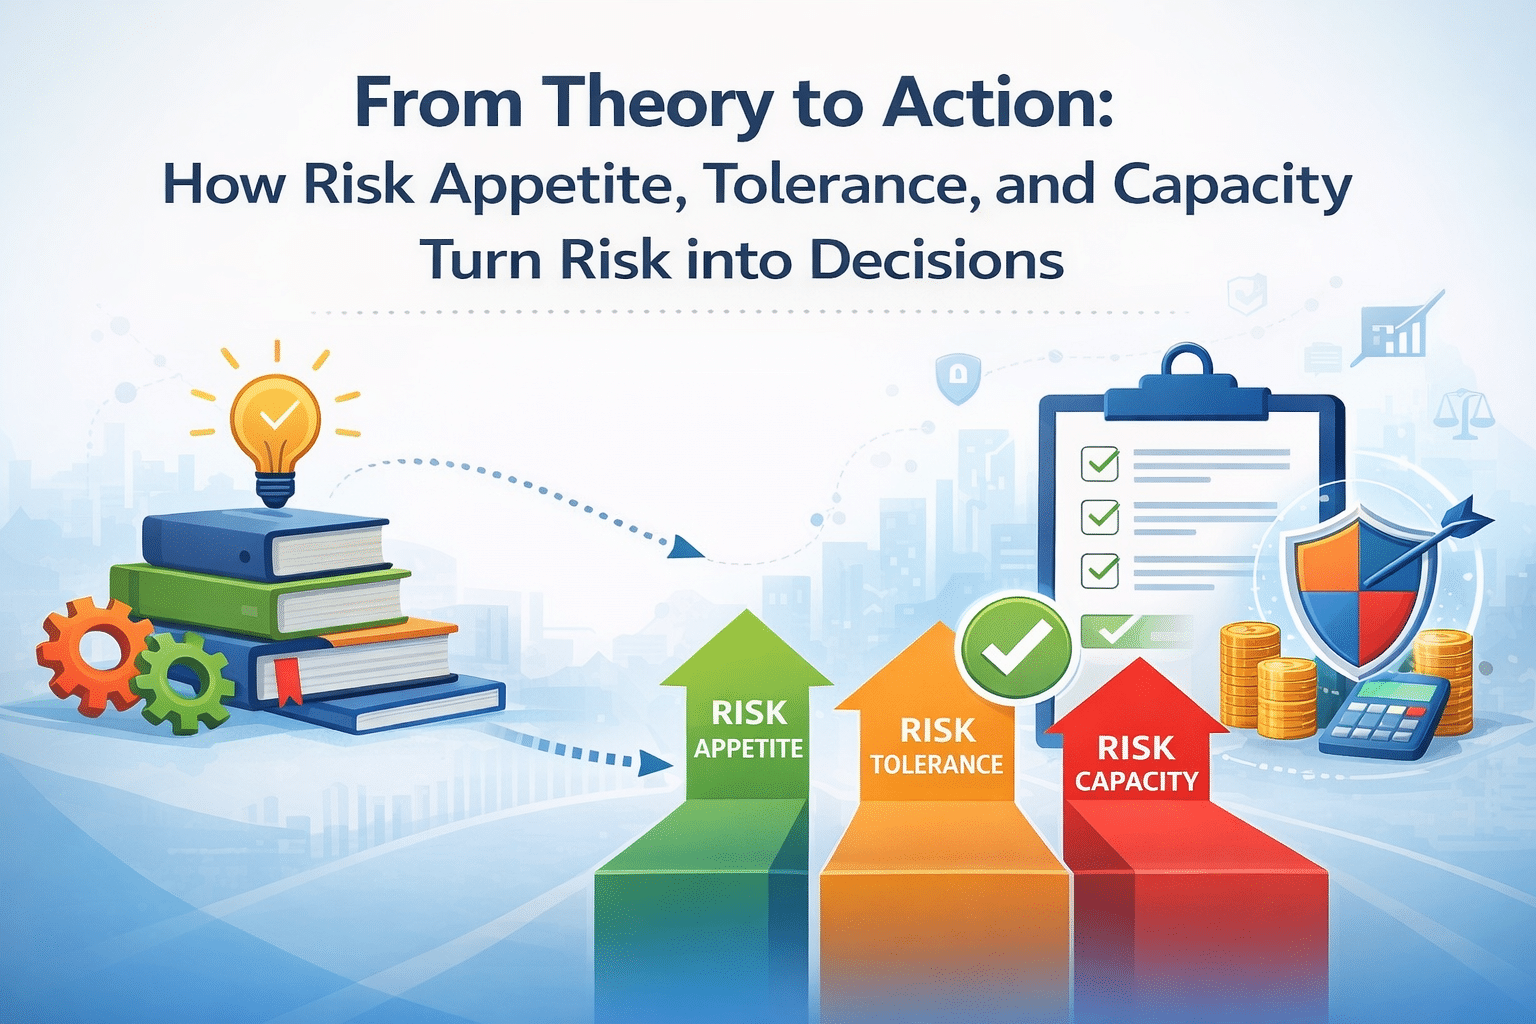
Defining risk appetite, risk tolerance, and risk capacity is foundational to effective risk management because they set the boundaries for decision-making, ensure consistency, and prevent both reckless risk-taking and over-conservatism. Each plays a distinct role:
1. Risk Appetite – Strategic Intent
What it is: The amount and type of risk an organization is willing to pursue to achieve its objectives.
Why it’s necessary:
Aligns risk-taking with business strategy
Guides leadership on where to invest, innovate, or avoid
Prevents ad-hoc or emotion-driven decisions
Provides a top-down signal to management and staff
Example:
“We are willing to accept moderate cybersecurity risk to accelerate digital innovation, but zero tolerance for regulatory non-compliance.”
Without a defined appetite, risk decisions become inconsistent and reactive.
2. Risk Tolerance – Operational Guardrails
What it is: The acceptable variation around the risk appetite—usually expressed as measurable limits.
Why it’s necessary:
Translates strategy into actionable thresholds
Enables monitoring and escalation
Supports objective decision-making
Prevents “death by risk avoidance” or uncontrolled exposure
Example:
Maximum acceptable downtime: 4 hours
Acceptable phishing click rate: <3%
Financial loss per incident: <$250K
Risk appetite without tolerance is too abstract to manage day-to-day risk.
3. Risk Capacity – Hard Limits
What it is: The maximum risk the organization can absorb without threatening survival (financial, legal, operational, reputational).
Why it’s necessary:
Establishes non-negotiable boundaries
Prevents existential or catastrophic risk
Informs stress testing and scenario analysis
Ensures risk appetite is realistic, not aspirational
Example:
Cash reserves can absorb only one major ransomware event
Loss of a specific license would shut down operations
Risk capacity is about what you can survive, not what you prefer.
How They Work Together
Concept
Question It Answers
Focus
Risk Appetite
What risk do we want to take?
Strategy
Risk Tolerance
How much deviation is acceptable?
Operations
Risk Capacity
How much risk can we survive?
Survival
Golden Rule:
Risk appetite must always stay within risk capacity, and risk tolerance enforces appetite in practice.
Why This Matters (Especially for Governance & Compliance)
Required by ISO 27001, ISO 31000, COSO ERM, NIST, ISO 42001
Enables defensible decisions for auditors and regulators
Strengthens board oversight and executive accountability
Critical for cyber risk, AI risk, third-party risk, and resilience planning
In One Line
Defining risk appetite, tolerance, and capacity ensures an organization takes the right risks, in the right amount, without risking its existence.
Risk appetite, risk tolerance, and risk capacity describe different but closely related dimensions of how an organization deals with risk. Risk appetite defines the level of risk an organization is willing to accept in pursuit of its objectives. It reflects intent and ambition: too little risk appetite can result in missed opportunities, while staying within appetite is generally acceptable. Exceeding appetite signals that mitigation is required because the organization is operating beyond what it has consciously agreed to accept.
Risk tolerance translates appetite into measurable thresholds that trigger action. It sets the boundaries for monitoring and review. When outcomes fall below tolerance, they are usually still acceptable, but when outcomes sit within tolerance limits, mitigation may already be required. Once tolerance is exceeded, the situation demands immediate escalation, as predefined limits have been breached and governance intervention is needed.
Risk capacity represents the absolute limit of risk an organization can absorb without threatening its viability. It is non-negotiable. Operating below capacity still requires mitigation, operating within capacity often demands immediate escalation, and exceeding capacity is simply not acceptable. At that point, the organization’s survival, legal standing, or core mission may be at risk.
Together, these three concepts form a hierarchy: appetite expresses willingness, tolerance defines control points, and capacity marks the hard stop.
Opinion on the statement
The statement “When appetite, tolerance, and capacity are clearly defined (and consistently understood), risk stops being theoretical and becomes a practical decision guide” is accurate and highly practical, especially in governance and security contexts.
Without clear definitions, risk discussions stay abstract—people debate “high” or “low” risk without shared meaning. When these concepts are defined, risk becomes operational. Decisions can be made quickly and consistently because everyone knows what is acceptable, what requires action, and what is unacceptable.
Example (Information Security / vCISO context): An organization may have a risk appetite that accepts moderate operational risk to enable faster digital transformation. Its risk tolerance might specify that any vulnerability with a CVSS score above 7.5 must be remediated within 14 days. Its risk capacity could be defined as “no risk that could result in regulatory fines exceeding $2M or prolonged service outage.” With this clarity, a newly discovered critical vulnerability is no longer a debate—it either sits within tolerance (monitor), exceeds tolerance (mitigate and escalate), or threatens capacity (stop deployment immediately).
Example (AI governance): A company may accept some experimentation risk (appetite) with internal AI tools, tolerate limited model inaccuracies under defined error rates (tolerance), but have zero capacity for risks that could cause regulatory non-compliance or IP leakage. This makes go/no-go decisions on AI use cases clear and defensible.
In practice, clearly defining appetite, tolerance, and capacity turns risk management from a compliance exercise into a decision-making framework. It aligns leadership intent with operational action—and that is where risk management delivers real value.
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
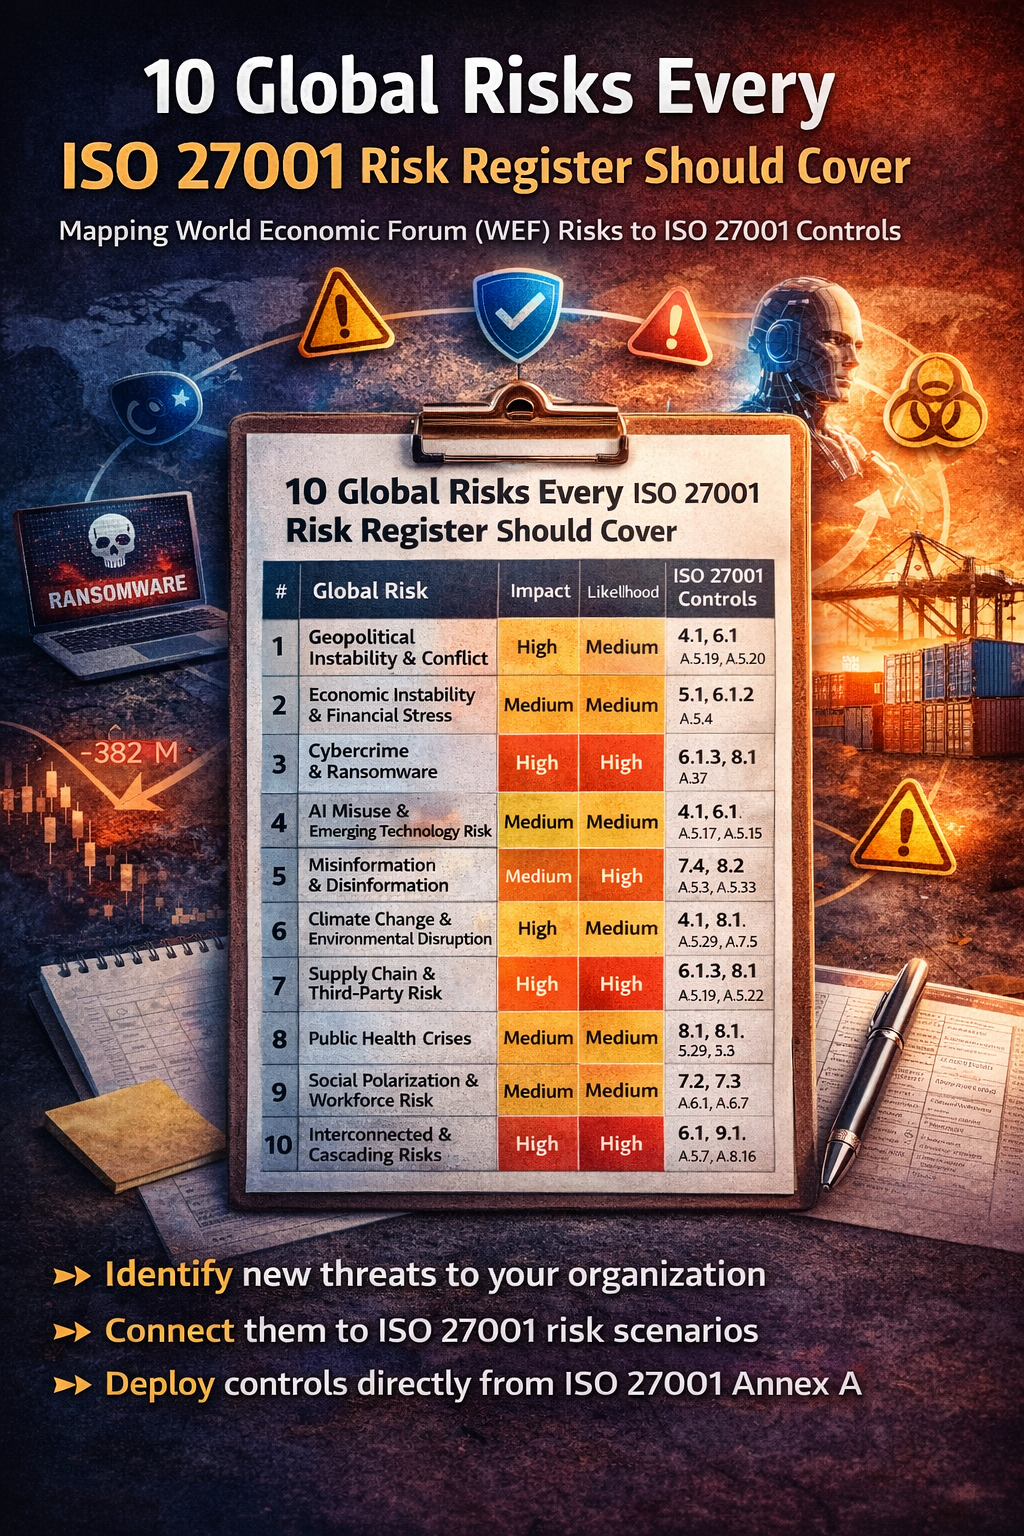
In developing organizational risk documentation—such as enterprise risk registers, cyber risk assessments, and business continuity plans—it is increasingly important to consider the World Economic Forum’s Global Risks Report. The report provides a forward-looking view of global threats and helps leaders balance immediate pressures with longer-term strategic risks.
The analysis is based on the Global Risks Perception Survey (GRPS), which gathered insights from more than 1,300 experts across government, business, academia, and civil society. These perspectives allow the report to examine risks across three time horizons: the immediate term (2026), the short-to-medium term (up to 2028), and the long term (to 2036).
One of the most pressing short-term threats identified is geopolitical instability. Rising geopolitical tensions, regional conflicts, and fragmentation of global cooperation are increasing uncertainty for businesses. These risks can disrupt supply chains, trigger sanctions, and increase regulatory and operational complexity across borders.
Economic risks remain central across all timeframes. Inflation volatility, debt distress, slow economic growth, and potential financial system shocks pose ongoing threats to organizational stability. In the medium term, widening inequality and reduced economic opportunity could further amplify social and political instability.
Cyber and technological risks continue to grow in scale and impact. Cybercrime, ransomware, data breaches, and misuse of emerging technologies—particularly artificial intelligence—are seen as major short- and long-term risks. As digital dependency increases, failures in technology governance or third-party ecosystems can cascade quickly across industries.
The report also highlights misinformation and disinformation as a critical threat. The erosion of trust in institutions, fueled by false or manipulated information, can destabilize societies, influence elections, and undermine crisis response efforts. This risk is amplified by AI-driven content generation and social media scale.
Climate and environmental risks dominate the long-term outlook but are already having immediate effects. Extreme weather events, resource scarcity, and biodiversity loss threaten infrastructure, supply chains, and food security. Organizations face increasing exposure to physical risks as well as regulatory and reputational pressures related to sustainability.
Public health risks remain relevant, even as the world moves beyond recent pandemics. Future outbreaks, combined with strained healthcare systems and global inequities in access to care, could create significant economic and operational disruptions, particularly in densely connected global markets.
Another growing concern is social fragmentation, including polarization, declining social cohesion, and erosion of trust. These factors can lead to civil unrest, labor disruptions, and increased pressure on organizations to navigate complex social and ethical expectations.
Overall, the report emphasizes that global risks are deeply interconnected. Cyber incidents can amplify economic instability, climate events can worsen geopolitical tensions, and misinformation can undermine responses to every other risk category. For organizations, the key takeaway is clear: risk management must be integrated, forward-looking, and resilience-focused—not siloed or purely compliance-driven.
Source: The report can be downloaded here: https://reports.weforum.org/docs/WEF_Global_Risks_Report_2026.pdf
Below is a clear, practitioner-level mapping of the World Economic Forum (WEF) global threats to ISO/IEC 27001, written for CISOs, vCISOs, risk owners, and auditors. I’ve mapped each threat to key ISO 27001 clauses and Annex A control themes (aligned to ISO/IEC 27001:2022).
WEF Global Threats → ISO/IEC 27001 Mapping
1. Geopolitical Instability & Conflict
Risk impact: Sanctions, supply-chain disruption, regulatory uncertainty, cross-border data issues
ISO 27001 Mapping
Clause 4.1 – Understanding the organization and its context
Clause 6.1 – Actions to address risks and opportunities
Annex A
A.5.31 – Legal, statutory, regulatory, and contractual requirements
Risk impact: Compound failures across cyber, economic, and operational domains
ISO 27001 Mapping
Clause 6.1 – Risk-based thinking
Clause 9.1 – Monitoring, measurement, analysis, and evaluation
Clause 10.1 – Continual improvement
Annex A
A.5.7 – Threat intelligence
A.5.35 – Independent review of information security
A.8.16 – Continuous monitoring
Key Takeaway (vCISO / Board-Level)
ISO 27001 is not just a cybersecurity standard — it is a resilience framework. When properly implemented, it directly addresses the systemic, interconnected risks highlighted by the World Economic Forum, provided organizations treat it as a living risk management system, not a compliance checkbox.
Here’s a practical mapping of WEF global risks to ISO 27001 risk register entries, designed for use by vCISOs, risk managers, or security teams. I’ve structured it in a way that you could directly drop into a risk register template.
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
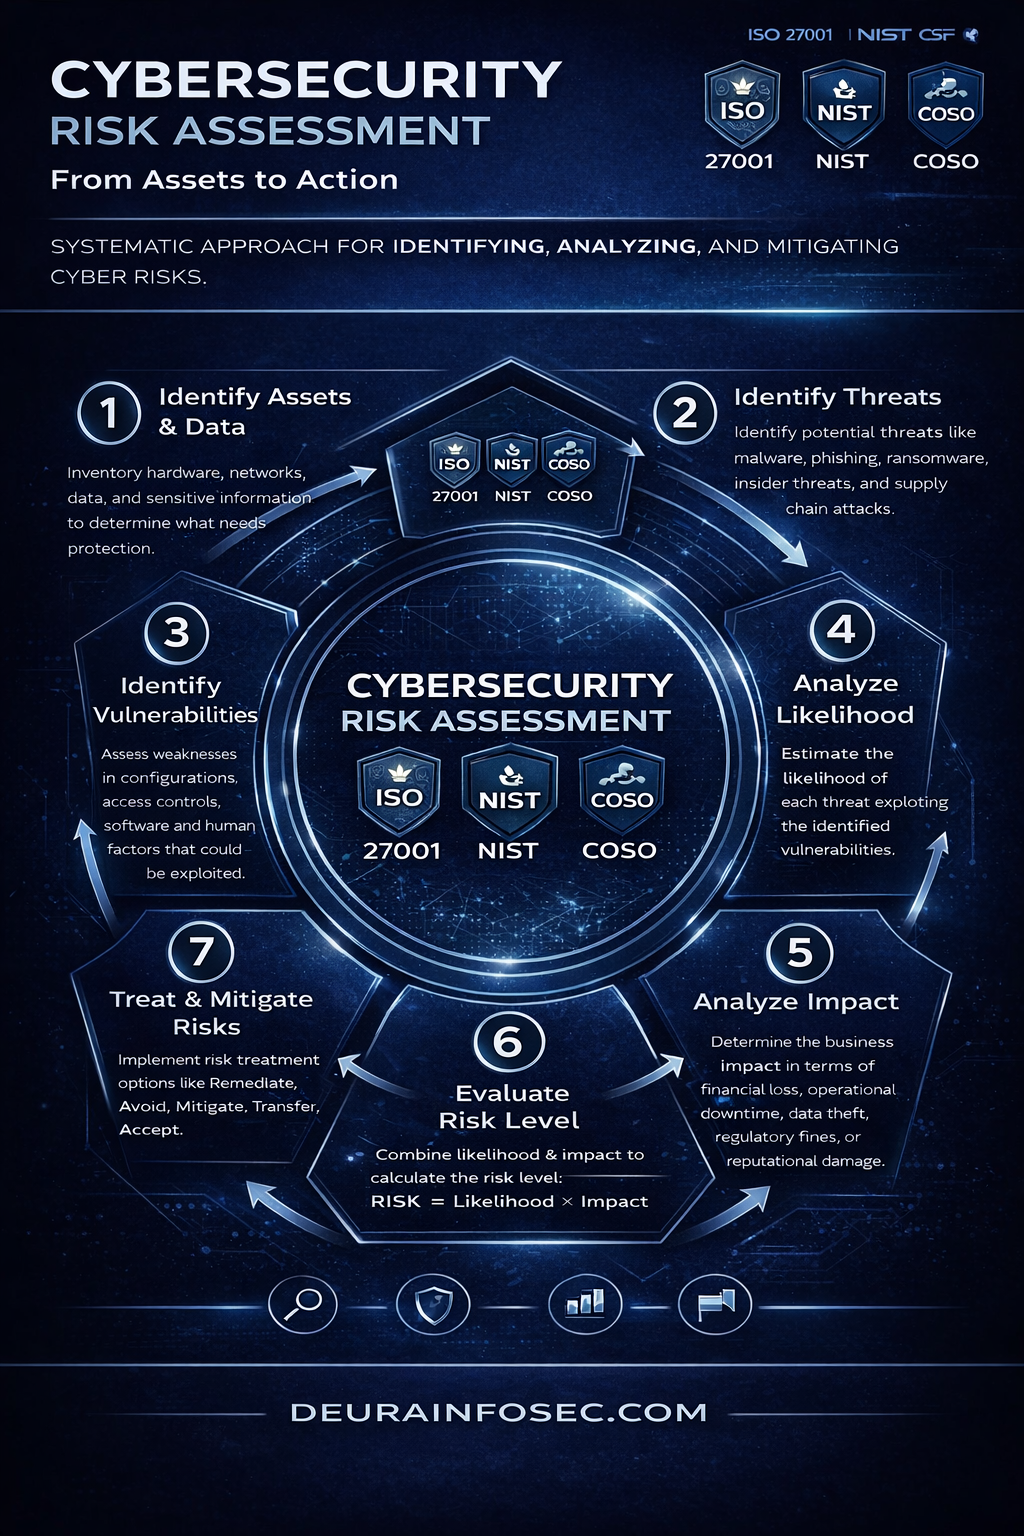
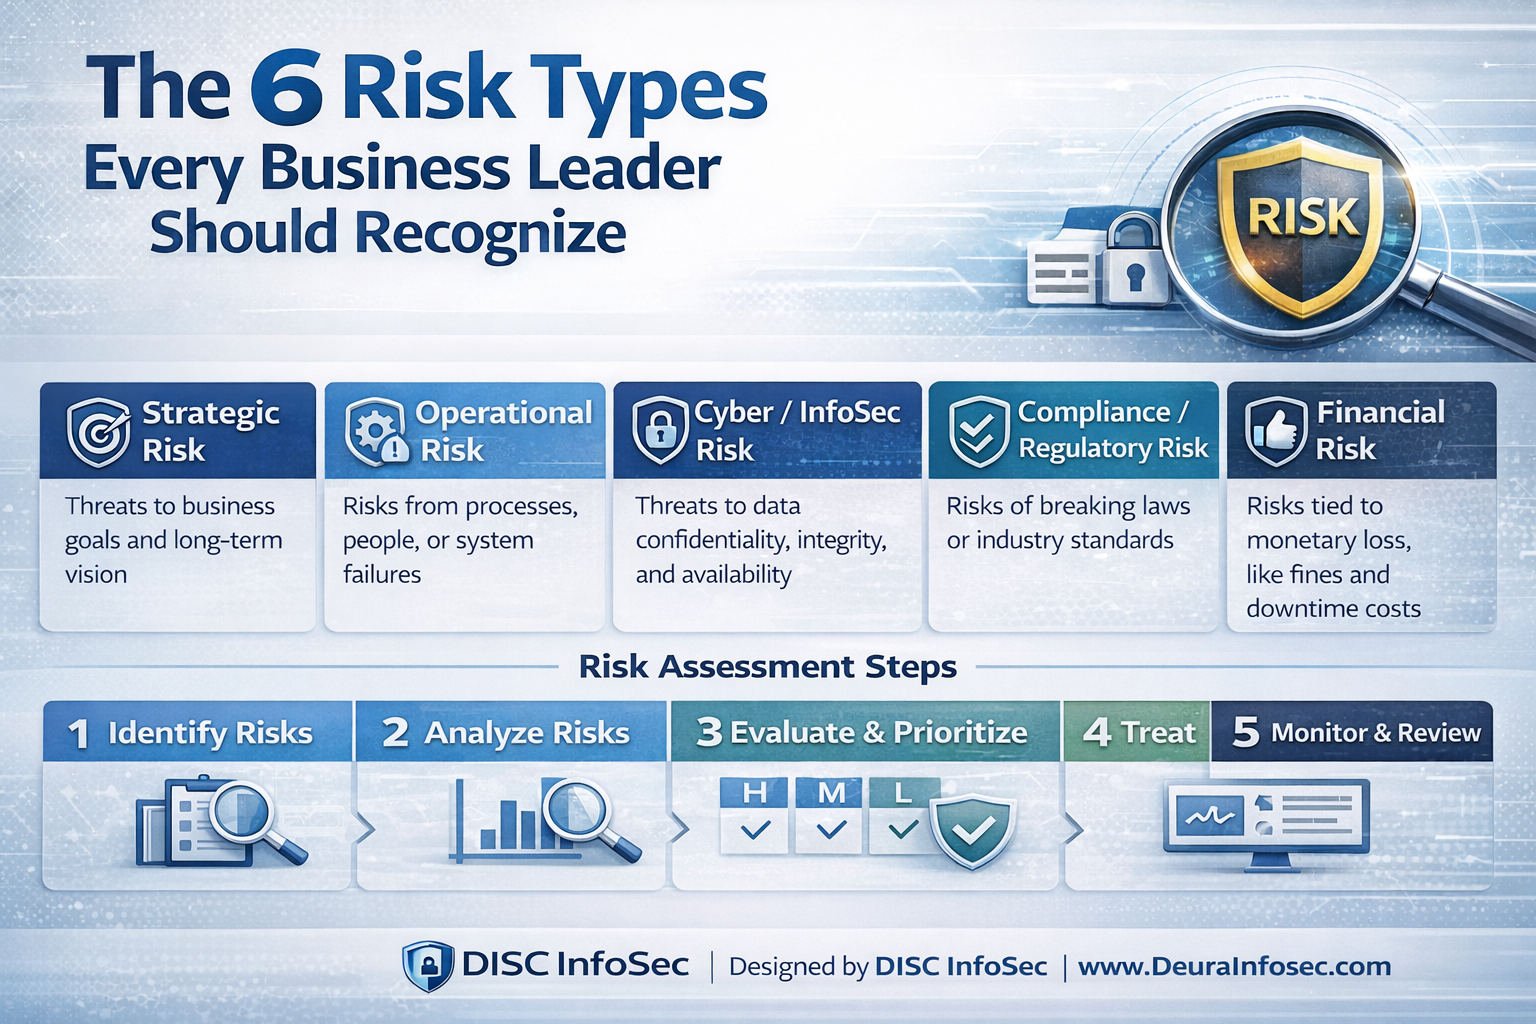
Below is a clear, structured explanation Cybersecurity Risk Assessment Process
What Is a Cybersecurity Risk Assessment?
A cybersecurity risk assessment is a structured process for understanding how cyber threats could impact the business, not just IT systems. Its purpose is to identify what assets matter most, what could go wrong, how likely those events are, and what the consequences would be if they occur. Rather than focusing on tools or controls first, a risk assessment provides decision-grade insight that leadership can use to prioritize investments, allocate resources, and accept or reduce risk knowingly. When aligned with frameworks like ISO 27001, NIST CSF, and COSO, it creates a common language between security, executives, and the board.
1. Identify Assets & Data
The first step is to identify and inventory critical assets, including hardware, software, cloud services, networks, data, and sensitive information. This step answers the fundamental question: what are we actually protecting? Without a clear understanding of assets and their business value, security efforts become unfocused. Many breaches stem from misconfigured or forgotten assets, making visibility and ownership essential to effective risk management.
2. Identify Threats
Once assets are known, the next step is identifying the threats that could realistically target them. These include external threats such as malware, ransomware, phishing, and supply chain attacks, as well as internal threats like insider misuse or human error. Threat identification focuses on who might attack, how, and why, based on real-world attack patterns rather than hypothetical scenarios.
3. Identify Vulnerabilities
Vulnerabilities are weaknesses that threats can exploit. These may exist in system configurations, software, access controls, processes, or human behavior. This step examines where defenses are insufficient or outdated, such as unpatched systems, excessive privileges, weak authentication, or lack of security awareness. Vulnerabilities are the bridge between threats and actual incidents.
4. Analyze Likelihood
Likelihood analysis evaluates how probable it is that a given threat will successfully exploit a vulnerability. This assessment considers threat actor capability, exposure, historical incidents, and the effectiveness of existing controls. The goal is not precision but reasonable estimation, enabling organizations to distinguish between theoretical risks and those that are most likely to occur.
5. Analyze Impact
Impact analysis focuses on the potential business consequences if a risk materializes. This includes financial loss, operational disruption, data theft, regulatory penalties, legal exposure, and reputational damage. By framing impact in business terms rather than technical language, this step ensures that cyber risk is understood as an enterprise risk, not just an IT issue.
6. Evaluate Risk Level
Risk level is determined by combining likelihood and impact, commonly expressed as Risk = Likelihood × Impact. This step allows organizations to rank risks and identify which ones exceed acceptable thresholds. Not all risks require immediate remediation, but all should be understood, documented, and owned at the appropriate level.
7. Treat & Mitigate Risks
Risk treatment involves deciding how to handle each identified risk. Options include remediating the risk through controls, mitigating it by reducing likelihood or impact, transferring it through insurance or contracts, avoiding it by changing business practices, or accepting it when the risk is within tolerance. This step turns analysis into action and aligns security decisions with business priorities.
8. Monitor & Review
Cyber risk is not static. New threats, technologies, and business changes continuously reshape the risk landscape. Monitoring and review ensure that controls remain effective and that risk assessments stay current. This step embeds risk management into ongoing governance rather than treating it as a one-time exercise.
Bottom line: A cybersecurity risk assessment is not about achieving perfect security—it’s about making informed, defensible decisions in an environment where risk is unavoidable. When done well, it transforms cybersecurity from a technical function into a strategic business capability.
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
Today’s most serious risks are no longer loud or obvious. Whether you are protecting an organization, leading people, or building resilience in your own life, the real threats — and opportunities — increasingly exist below the surface, hidden in systems, environments, and assumptions we rarely question.
Leadership, cybersecurity, and performance are being reshaped quietly. The rules aren’t changing overnight; they’re shifting gradually, often unnoticed, until the impact becomes unavoidable. Staying ahead now requires understanding these subtle shifts before they turn into crises. Everything begins with awareness. Not just awareness of cyber threats, but of the deeper drivers of vulnerability and strength. Intellectual property, environmental influence, and decision-making systems are emerging as critical factors that determine long-term success or failure.
This shift demands a move away from late-stage reaction. Instead of responding after alarms go off, leaders must understand the battlefield in advance — identifying where value truly lives and how it can be exposed without obvious warning signs. Intellectual property has become one of the most valuable — and most targeted — assets in the modern threat landscape. As traditional perimeter defenses weaken, attackers are no longer just chasing systems and data; they are pursuing ideas, research, trade secrets, and innovation itself.
IP protection is no longer a legal checkbox or an afterthought. Nation-states, competitors, and sophisticated actors are exploiting digital access to siphon knowledge and strategic advantage. Defending intellectual capital now requires executive attention, governance, and security alignment. Cybersecurity is also deeply personal. Our environments — digital and physical — quietly shape how we think, decide, perform, and recover. Factors like constant digital noise, poor system design, and unhealthy surroundings compound over time, leading to fatigue, errors, and burnout.
This perspective challenges leaders to design not only secure systems, but sustainable lives. Clear thinking, sound judgment, and consistent performance depend on mastering the environment around us as much as mastering technology or strategy. When change happens quietly, awareness becomes the strongest form of defense. Whether protecting intellectual property, navigating uncertainty, or strengthening personal resilience, the greatest risks — and advantages — are often the ones we fail to see at first glance.
Opinion In my view, this shift marks a critical evolution in how we think about risk and leadership. The organizations and individuals who win won’t be those with the loudest tools, but those with the deepest awareness. Seeing beneath the surface — of systems, environments, and value — is no longer optional; it’s the defining capability of modern resilience and strategic advantage.
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
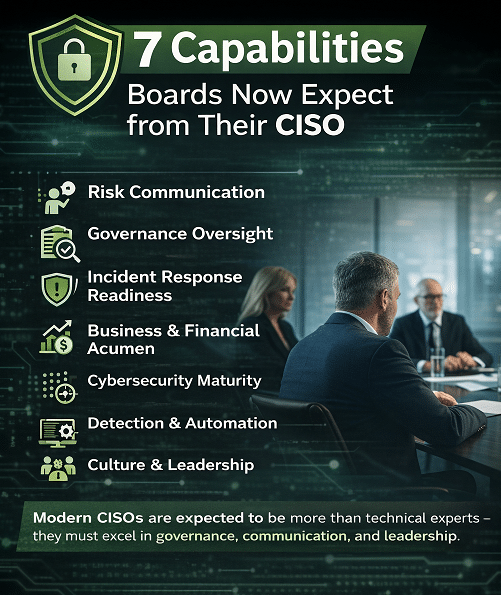
A CISO must design and operate a security governance model that aligns with corporate governance, regulatory requirements, and the organization’s risk appetite. This ensures security controls are consistent, auditable, and defensible. Without strong governance, organizations face regulatory penalties, audit failures, and fragmented or overlapping controls that create risk instead of reducing it.
2. Cybersecurity Maturity Management
The CISO should continuously assess the organization’s security posture using recognized maturity models such as NIST CSF or ISO 27001, and define a clear target state. This capability enables prioritization of investments and long-term improvement. Lacking maturity management leads to reactive, ad-hoc spending and an inability to justify or sequence security initiatives.
3. Incident Response (Response Readiness)
A core responsibility of the CISO is ensuring the organization is prepared for incidents through tested playbooks, simulations, and war-gaming. Effective response readiness minimizes impact when breaches occur. Without it, detection is slow, downtime is extended, and financial and reputational damage escalates rapidly.
The CISO must ensure the organization can rapidly detect threats, alert the right teams, and automate responses where possible. Strong SOC and SOAR capabilities reduce mean time to detect (MTTD) and mean time to respond (MTTR). Weakness here results in undetected breaches, slow manual responses, and delayed forensic investigations.
5. Business & Financial Acumen
A modern CISO must connect cyber risk to business outcomes—revenue, margins, valuation, and enterprise risk. This includes articulating ROI, payback, and value creation. Without this skill, security is viewed purely as a cost center, and investments fail to align with business strategy.
6. Risk Communication
The CISO must translate complex technical risks into clear, business-impact narratives that boards and executives can act on. Effective risk communication enables informed decision-making. When this capability is weak, risks remain misunderstood or hidden until a major incident forces attention.
7. Culture & Cross-Functional Leadership
A successful CISO builds strong security teams, fosters a security-aware culture, and collaborates across IT, legal, finance, product, and operations. Security cannot succeed in silos. Poor leadership here leads to misaligned priorities, weak adoption of controls, and ineffective onboarding of new staff into security practices.
My Opinion: The Three Most Important Capabilities
If forced to prioritize, the top three are:
Risk Communication If the board does not understand risk, no other capability matters. Funding, priorities, and executive decisions all depend on how well the CISO communicates risk in business terms.
Governance Oversight Governance is the foundation. Without it, security efforts are fragmented, compliance fails, and accountability is unclear. Strong governance enables everything else to function coherently.
Incident Response (Response Readiness) Breaches are inevitable. What separates resilient organizations from failed ones is how well they respond. Preparation directly limits financial, operational, and reputational damage.
Bottom line: Technology matters, but leadership, governance, and communication are what boards ultimately expect from a CISO. Tools support these capabilities—they don’t replace them.
At DISC InfoSec, we help organizations navigate this landscape by aligning AI risk management, governance, security, and compliance into a single, practical roadmap. Whether you are experimenting with AI or deploying it at scale, we help you choose and operationalize the right frameworks to reduce risk and build trust. Learn more at DISC InfoSec.
Organizations face multiple types of risks that can affect strategy, operations, compliance, and reputation. Strategic risks arise when business objectives or long-term goals are threatened—such as when weak security planning damages customer confidence. Operational risks stem from human errors, flawed processes, or technology failures, like a misconfigured firewall or inadequate incident response.
Cyber and information security risks affect the confidentiality, integrity, and availability of data. Examples include ransomware attacks, data breaches, and insider threats. Compliance or regulatory risks occur when companies fail to meet legal or industry requirements such as ISO 27001, ISO 42001, GDPR, PCI-DSS, or IEC standards.
Financial risk is tied to monetary losses through fraud, fines, or system downtime. Reputational risks damage stakeholder trust and the public perception of the organization, often triggered by events like public breach disclosures. Lastly, third-party/vendor risks originate from suppliers and partners, such as when a vendor’s weak cybersecurity exposes the organization.
Risk assessment is the structured process used to protect the business from these threats, ensuring vulnerabilities are addressed before causing harm. The assessment lifecycle involves five key phases: 1️⃣ Identifying risks through understanding assets and their vulnerabilities 2️⃣ Analyzing likelihood and impact 3️⃣ Evaluating and prioritizing based on risk severity 4️⃣ Treating risks through mitigation, transfer, acceptance, or avoidance 5️⃣ Monitoring and continually improving controls over time
Opinion: Why Knowing Risk Types Helps Businesses
Understanding the distinct categories of risks allows companies to take a proactive approach instead of reacting after damage occurs. It provides clarity on where threats originate, which helps leaders allocate resources more efficiently, strengthen compliance, protect revenue, and build trust with customers and stakeholders. Ultimately, knowing the types of risks empowers smarter decision-making and leads to long-term business resilience.
The article reports on a new “safety report card” assessing how well leading AI companies are doing at protecting humanity from the risks posed by powerful artificial-intelligence systems. The report was issued by Future of Life Institute (FLI), a nonprofit that studies existential threats and promotes safe development of emerging technologies.
This “AI Safety Index” grades companies based on 35 indicators across six domains — including existential safety, risk assessment, information sharing, governance, safety frameworks, and current harms.
In the latest (Winter 2025) edition of the index, no company scored higher than a “C+.” The top-scoring companies were Anthropic and OpenAI, followed by Google DeepMind.
Other firms, including xAI, Meta, and a few Chinese AI companies, scored D or worse.
A key finding is that all evaluated companies scored poorly on “existential safety” — which covers whether they have credible strategies, internal monitoring, and controls to prevent catastrophic misuse or loss of control as AI becomes more powerful.
Even though companies like OpenAI and Google DeepMind say they’re committed to safety — citing internal research, safeguards, testing with external experts, and safety frameworks — the report argues that public information and evidence remain insufficient to demonstrate real readiness for worst-case scenarios.
For firms such as xAI and Meta, the report highlights a near-total lack of evidence about concrete safety investments beyond minimal risk-management frameworks. Some companies didn’t respond to requests for comment.
The authors of the index — a panel of eight independent AI experts including academics and heads of AI-related organizations — emphasize that we’re facing an industry that remains largely unregulated in the U.S. They warn this “race to the bottom” dynamic discourages companies from prioritizing safety when profitability and market leadership are at stake.
The report suggests that binding safety standards — not voluntary commitments — may be necessary to ensure companies take meaningful action before more powerful AI systems become a reality.
The broader context: as AI systems play larger roles in society, their misuse becomes more plausible — from facilitating cyberattacks, enabling harmful automation, to even posing existential threats if misaligned superintelligent AI were ever developed.
In short: according to the index, the AI industry still has a long way to go before it can be considered truly “safe for humanity,” even among its most prominent players.
My Opinion
I find the results of this report deeply concerning — but not surprising. The fact that even the top-ranked firms only get a “C+” strongly suggests that current AI safety efforts are more symbolic than sufficient. It seems like companies are investing in safety only at a surface level (e.g., statements, frameworks), but there’s little evidence they are preparing in a robust, transparent, and enforceable way for the profound risks AI could pose — especially when it comes to existential threats or catastrophic misuse.
The notion that an industry with such powerful long-term implications remains essentially unregulated feels reckless. Voluntary commitments and internal policies can easily be overridden by competitive pressure or short-term financial incentives. Without external oversight and binding standards, there’s no guarantee safety will win out over speed or profits.
That said, the fact that the FLI even produces this index — and that two firms get a “C+” — shows some awareness and effort towards safety. It’s better than nothing. But awareness must translate into real action: rigorous third-party audits, transparent safety testing, formal safety requirements, and — potentially — regulation.
In the end, I believe society should treat AI much like we treat high-stakes technologies such as nuclear power: with caution, transparency, and enforceable safety norms. It’s not enough to say “we care about safety”; firms must prove they can manage the long-term consequences, and governments and civil society need to hold them accountable.
The European Union’s Artificial Intelligence Act represents the world’s first comprehensive regulatory framework for artificial intelligence. As organizations worldwide prepare for compliance, one of the most critical first steps is understanding exactly where your AI system falls within the EU’s risk-based classification structure.
At DeuraInfoSec, we’ve developed a streamlined EU AI Act Risk Calculator to help organizations quickly assess their compliance obligations.🔻 But beyond the tool itself, understanding the framework is essential for any organization deploying AI systems that touch EU markets or citizens.
The EU AI Act takes a pragmatic, risk-based approach to regulation. Rather than treating all AI systems equally, it categorizes them into four distinct risk levels, each with different compliance requirements:
1. Unacceptable Risk (Prohibited Systems)
These AI systems pose such fundamental threats to human rights and safety that they are completely banned in the EU. This category includes:
Social scoring by public authorities that evaluates or classifies people based on behavior, socioeconomic status, or personal characteristics
Real-time remote biometric identification in publicly accessible spaces (with narrow exceptions for law enforcement in specific serious crimes)
Systems that manipulate human behavior to circumvent free will and cause harm
Systems that exploit vulnerabilities of specific groups due to age, disability, or socioeconomic circumstances
If your AI system falls into this category, deployment in the EU is simply not an option. Alternative approaches must be found.
2. High-Risk AI Systems
High-risk systems are those that could significantly impact health, safety, fundamental rights, or access to essential services. The EU AI Act identifies high-risk AI in two ways:
Safety Components: AI systems used as safety components in products covered by existing EU safety legislation (medical devices, aviation, automotive, etc.)
Specific Use Cases: AI systems used in eight critical domains:
Biometric identification and categorization
Critical infrastructure management
Education and vocational training
Employment, worker management, and self-employment access
Access to essential private and public services
Law enforcement
Migration, asylum, and border control management
Administration of justice and democratic processes
High-risk AI systems face the most stringent compliance requirements, including conformity assessments, risk management systems, data governance, technical documentation, transparency measures, human oversight, and ongoing monitoring.
3. Limited Risk (Transparency Obligations)
Limited-risk AI systems must meet specific transparency requirements to ensure users know they’re interacting with AI:
Chatbots and conversational AI must clearly inform users they’re communicating with a machine
Emotion recognition systems require disclosure to users
Biometric categorization systems must inform individuals
Deepfakes and synthetic content must be labeled as AI-generated
While these requirements are less burdensome than high-risk obligations, they’re still legally binding and require thoughtful implementation.
4. Minimal Risk
The vast majority of AI systems fall into this category: spam filters, AI-enabled video games, inventory management systems, and recommendation engines. These systems face no specific obligations under the EU AI Act, though voluntary codes of conduct are encouraged, and other regulations like GDPR still apply.
Why Classification Matters Now
Many organizations are adopting a “wait and see” approach to EU AI Act compliance, assuming they have time before enforcement begins. This is a costly mistake for several reasons:
Timeline is Shorter Than You Think: While full enforcement doesn’t begin until 2026, high-risk AI systems will need to begin compliance work immediately to meet conformity assessment requirements. Building robust AI governance frameworks takes time.
Competitive Advantage: Early movers who achieve compliance will have significant advantages in EU markets. Organizations that can demonstrate EU AI Act compliance will win contracts, partnerships, and customer trust.
Foundation for Global Compliance: The EU AI Act is setting the standard that other jurisdictions are likely to follow. Building compliance infrastructure now prepares you for a global regulatory landscape.
Risk Mitigation: Even if your AI system isn’t currently deployed in the EU, supply chain exposure, data processing locations, or future market expansion could bring you into scope.
Using the Risk Calculator Effectively
Our EU AI Act Risk Calculator is designed to give you a rapid initial assessment, but it’s important to understand what it can and cannot do.
What It Does:
Provides a preliminary risk classification based on key regulatory criteria
Identifies your primary compliance obligations
Helps you understand the scope of work ahead
Serves as a conversation starter for more detailed compliance planning
What It Doesn’t Replace:
Detailed legal analysis of your specific use case
Comprehensive gap assessments against all requirements
Technical conformity assessments
Ongoing compliance monitoring
Think of the calculator as your starting point, not your destination. If your system classifies as high-risk or even limited-risk, the next step should be a comprehensive compliance assessment.
Common Classification Challenges
In our work helping organizations navigate EU AI Act compliance, we’ve encountered several common classification challenges:
Boundary Cases: Some systems straddle multiple categories. A chatbot used in customer service might seem like limited risk, but if it makes decisions about loan approvals or insurance claims, it becomes high-risk.
Component vs. System: An AI component embedded in a larger system may inherit the risk classification of that system. Understanding these relationships is critical.
Intended Purpose vs. Actual Use: The EU AI Act evaluates AI systems based on their intended purpose, but organizations must also consider reasonably foreseeable misuse.
Evolution Over Time: AI systems evolve. A minimal-risk system today might become high-risk tomorrow if its use case changes or new features are added.
The Path Forward
Whether your AI system is high-risk or minimal-risk, the EU AI Act represents a fundamental shift in how organizations must think about AI governance. The most successful organizations will be those who view compliance not as a checkbox exercise but as an opportunity to build more trustworthy, robust, and valuable AI systems.
At DeuraInfoSec, we specialize in helping organizations navigate this complexity. Our approach combines deep technical expertise with practical implementation experience. As both practitioners (implementing ISO 42001 for our own AI systems at ShareVault) and consultants (helping organizations across industries achieve compliance), we understand both the regulatory requirements and the operational realities of compliance.
Take Action Today
Start with our free EU AI Act Risk Calculator to understand your baseline risk classification. Then, regardless of your risk level, consider these next steps:
Conduct a comprehensive AI inventory across your organization
Perform detailed risk assessments for each AI system
Develop AI governance frameworks aligned with ISO 42001
Implement technical and organizational measures appropriate to your risk level
Establish ongoing monitoring and documentation processes
The EU AI Act isn’t just another compliance burden. It’s an opportunity to build AI systems that are more transparent, more reliable, and more aligned with fundamental human values. Organizations that embrace this challenge will be better positioned for success in an increasingly regulated AI landscape.
Ready to assess your AI system’s risk level? Try our free EU AI Act Risk Calculator now.
Need expert guidance on compliance? Contact DeuraInfoSec.com today for a comprehensive assessment.
DeuraInfoSec specializes in AI governance, ISO 42001 implementation, and EU AI Act compliance for B2B SaaS and financial services organizations. We’re not just consultants—we’re practitioners who have implemented these frameworks in production environments.
Building an Effective AI Risk Assessment Process: A Practical Guide
As organizations rapidly adopt artificial intelligence, the need for structured AI risk assessment has never been more critical. With regulations like the EU AI Act and standards like ISO 42001 reshaping the compliance landscape, companies must develop systematic approaches to evaluate and manage AI-related risks.
Why AI Risk Assessment Matters
Traditional IT risk frameworks weren’t designed for AI systems. Unlike conventional software, AI systems learn from data, evolve over time, and can produce unpredictable outcomes. This creates unique challenges:
Regulatory Complexity: The EU AI Act classifies systems by risk level, with severe penalties for non-compliance
Operational Uncertainty: AI decisions can be opaque, making risk identification difficult
Rapid Evolution: AI capabilities and risks change as models are retrained
Multi-stakeholder Impact: AI affects customers, employees, and society differently
Check your AI 👇 readiness in 5 minutes—before something breaks. Free instant score + remediation plan.
The Four-Stage Assessment Framework
An effective AI risk assessment follows a structured progression from basic information gathering to actionable insights.
Stage 1: Organizational Context
Understanding your organization’s AI footprint begins with foundational questions:
Company Profile
Size and revenue (risk tolerance varies significantly)
Industry sector (different regulatory scrutiny levels)
This baseline helps calibrate the assessment to your organization’s specific context and risk appetite.
Stage 2: AI System Inventory
The second stage maps your actual AI implementations. Many organizations underestimate their AI exposure by focusing only on custom-built systems while overlooking:
Each system type carries different risk profiles. For example, biometric identification and emotion recognition trigger higher scrutiny under the EU AI Act, while predictive analytics may have lower inherent risk but broader organizational impact.
Stage 3: Regulatory Risk Classification
This critical stage determines your compliance obligations, particularly under the EU AI Act which uses a risk-based approach:
High-Risk Categories Systems that fall into these areas require extensive documentation, testing, and oversight:
Mobile-responsive design for completion flexibility
Data Collection Strategy
Mix question types: multiple choice for consistency, checkboxes for comprehensive coverage
Require critical fields while making others optional
Save progress to prevent data loss
Scoring Algorithm Transparency
Document risk scoring methodology clearly
Explain how answers translate to risk levels
Provide immediate feedback on assessment completion
Automated Report Generation
Effective assessments produce actionable outputs:
Risk Level Summary
Clear classification (HIGH/MEDIUM/LOW)
Plain language explanation of implications
Regulatory context (EU AI Act, ISO 42001)
Gap Analysis
Specific control deficiencies identified
Business impact of each gap explained
Prioritized remediation recommendations
Next Steps
Concrete action items with timelines
Resources needed for implementation
Quick wins vs. long-term initiatives
From Assessment to Action
The assessment is just the beginning. Converting insights into compliance requires:
Immediate Actions (0-30 days)
Address critical HIGH RISK findings
Document current AI inventory
Establish incident response contacts
Short-term Actions (1-3 months)
Develop missing policy documentation
Implement data governance framework
Create impact assessment templates
Medium-term Actions (3-6 months)
Deploy monitoring and logging
Conduct comprehensive impact assessments
Train staff on AI governance
Long-term Actions (6-12 months)
Pursue ISO 42001 certification
Build continuous compliance monitoring
Mature AI governance program
Measuring Success
Track these metrics to gauge program maturity:
Coverage: Percentage of AI systems assessed
Remediation Velocity: Average time to close gaps
Incident Rate: AI-related incidents per quarter
Audit Readiness: Time needed to produce compliance documentation
Stakeholder Confidence: Survey results from users, customers, regulators
Conclusion
AI risk assessment isn’t a one-time checkbox exercise. It’s an ongoing process that must evolve with your AI capabilities, regulatory landscape, and organizational maturity. By implementing a structured four-stage approach—organizational context, system inventory, regulatory classification, and control gap analysis—you create a foundation for responsible AI deployment.
The assessment tool we’ve built demonstrates that compliance doesn’t have to be overwhelming. With clear frameworks, automated scoring, and actionable insights, organizations of any size can begin their AI governance journey today.
Ready to assess your AI risk? Start with our free assessment tool or schedule a consultation to discuss your specific compliance needs.
About DeuraInfoSec: We specialize in AI governance, ISO 42001 implementation, and information security compliance for B2B SaaS and financial services companies. Our practical, outcome-focused approach helps organizations navigate complex regulatory requirements while maintaining business agility.
Free AI Risk Assessment: Discover Your EU AI Act Classification & ISO 42001 Gaps in 15 Minutes
A progressive 4-stage web form that collects company info, AI system inventory, EU AI Act risk factors, and ISO 42001 readiness, then calculates a risk score (HIGH/MEDIUM/LOW), identifies control gaps across 5 key ISO 42001 areas. Built with vanilla JavaScript, uses visual progress tracking, color-coded results display, and includes a CTA for Calendly booking, with all scoring logic and gap analysis happening client-side before submission. Concise, tailored high-level risk snapshot of your AI system.
What’s Included:
✅ 4-section progressive flow (15 min completion time) ✅ Smart risk calculation based on EU AI Act criteria ✅ Automatic gap identification for ISO 42001 controls ✅ PDF generation with 3-page professional report ✅ Dual email delivery (to you AND the prospect) ✅ Mobile responsive design ✅ Progress tracking visual feedback
Your Risk Program Is Only as Strong as Its Feedback Loop
Many organizations are excellent at identifying risks, but far fewer are effective at closing them. Logging risks in a register without follow-up is not true risk management—it’s merely risk archiving.
A robust risk program follows a complete cycle: identify risks, assess their impact and likelihood, assign ownership, implement mitigation, verify effectiveness, and feed lessons learned back into the system. Skipping verification and learning steps turns risk management into a task list, not a strategic control process.
Without a proper feedback loop, the same issues recur across departments, “closed” risks resurface during audits, teams lose confidence in the process, and leadership sees reports rather than meaningful results.
Building an Effective Feedback Loop:
Make verification mandatory: every mitigation must be validated through control testing or monitoring.
Track lessons learned: use post-mortems to refine controls and frameworks.
Automate follow-ups: trigger reviews for risks not revisited within set intervals.
Share outcomes: communicate mitigation results to teams to strengthen ownership and accountability.
Pro Tips:
Measure risk elimination, not just identification.
Highlight a “risk of the month” internally to maintain awareness.
Link the risk register to performance metrics to align incentives with action.
The most effective GRC programs don’t just record risks—they learn from them. Every feedback loop strengthens organizational intelligence and security.
Many organizations excel at identifying risks but fail to close them, turning risk management into mere record-keeping. A strong program not only identifies, assesses, and mitigates risks but also verifies effectiveness and feeds lessons learned back into the system. Without this feedback loop, issues recur, audits fail, and teams lose trust. Mandating verification, tracking lessons, automating follow-ups, and sharing outcomes ensures risks are truly managed, not just logged—making your organization smarter, safer, and more accountable.