Sep 01 2020

Is China the World’s Greatest Cyber Power?

Category: cyber security,Cyber War — DISC @ 11:32 pm

While the US, Russia, Israel, and several European nations all have sophisticated cyber capabilities, one threat intelligence firm argues that China’s aggressive approach to cyber operations has made it perhaps the world’s greatest cyber power.

Source: Is China the World’s Greatest Cyber Power?

Is China the World’s Greatest Cyber Power?

“The goal is simple: break down trust in democracies, disrupt election cycles or manipulate democratic election results, and gain economic advantage over adversaries to advance global position and power,” according to the report.

“Over the past decade, China has become increasingly forthright in its intentions, and this change has been observed in cyber operations as well,” the report states. “Researchers have observed stark differences in tactics, tone, and behavior from Chinese state-sponsored cyber, military, and political parties over the past several years.”

“When it comes to China, cyber is not a tactical weapon, it is a strategic means to an end,” Maor says. “And if you are wondering what that end is, it is not something secret — it is something that is published every five years.”

There’s A Crisis That Is Quietly Creating New Economic Superpowers…
httpv://www.youtube.com/watch?v=h6GqEpmn_Fk

Tags: Cyber capabilities, cyber military, cyber operations, Cyber Power, Cyber Super Power, Greatest Cyber Power


Aug 31 2020

Hackers are backdooring QNAP NAS devices with 3-year old RCE bug

Category: Hacking,Malware — DISC @ 3:58 pm

Hackers are scanning for vulnerable network-attached storage (NAS) devices running multiple QNAP firmware versions, trying to exploit a remote code execution (RCE) vulnerability addressed by QNAP in a previous release.

Source: Hackers are backdooring QNAP NAS devices with 3-year old RCE bug


CISA says 62,000 QNAP NAS devices have been infected with the QSnatch malwareQSnatch malware, first spotted in late 2019, has grown from 7,000 bots to more than 62,000, according to a joint US CISA and UK NCSC security alert.


QSnatch And How To Protect Your QNAP NAS From Online Intruders

QNAP urges users to update Malware Remover after QSnatch alert

Tags: Backdoor, backdooring


Aug 29 2020

The Best DEF CON Talks Of All Time!

Category: Hacking — DISC @ 11:22 am

As the title of this post suggests we’ve sourced what we believe to be the best DEF CON presentations from 1993 to the present day. For those that don’t know, DEF CON is literally the ‘poster-child’

Source: The Best DEF CON Talks Of All Time!

Tags: DEF CON


Aug 28 2020

Cisco engineer resigns then nukes 16k WebEx accounts, 456 VMs

Category: Access Control,Information Security — DISC @ 9:06 am

A former Cisco employee pleaded guilty to accessing the company’s cloud infrastructure in 2018, five months after resigning, to deploy code that led to the shut down of more than 16,000 WebEx Teams accounts and the deletion of 456 virtual machines.

According to a plea agreement filed on July 30, 2020, 30-year-old Sudhish Kasaba Ramesh accessed Cisco’s cloud infrastructure hosted on Amazon Web Services without permission on September 24, 2018 — he resigned from the company in April 2018.

Source: Cisco engineer resigns then nukes 16k WebEx accounts, 456 VMs

From Weakest Link to Human Firewall in Seven Days

Download a Security Risk Assessment Steps paper!

Security Risk assessment Quiz – Find Out How Your security risk assessment Stands Up!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet


Aug 26 2020

Safari Bug That Allows Stealing Data Disclosed After Apple Delays A Patch

Category: data security,Web Security — DISC @ 10:37 pm

Apple planned to release a fix for the Safari bug by Spring 2021, delaying it for one year. The bug allows stealing local data files.

Source: Safari Bug That Allows Stealing Data Disclosed After Apple Delays A Patch


Data Loss/Leak Prevention | Security Basics
httpv://www.youtube.com/watch?v=5CU9KYA-sz8


Aug 25 2020

Expert discloses unpatched Safari flaw that allows stealing local files

Category: Security vulnerabilities,Web Security — DISC @ 10:19 pm

A researcher disclosed technical details of an unpatched vulnerability in Apple’s Safari web browser that can be exploited to steal files from the targeted system.

Source: Expert discloses unpatched Safari flaw that allows stealing local files


Download a Security Risk Assessment Steps paper!

Security Risk assessment Quiz – Find Out How Your security risk assessment Stands Up!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet

Aug 24 2020

Google Urgently Fixed A Gmail Bug After Delaying It For Months

Category: Email Security — DISC @ 10:51 am

Email spoofing Gmail bug could bypass SPF, DMARC checks. After 137 days of report, Google fixed the bug within 7 hours of public disclosure.

Source: Google Urgently Fixed A Gmail Bug After Delaying It For Months

How to secure your GMAIL account like a pro | YubiKey Tutorial
httpv://www.youtube.com/watch?v=CBE1Oua0j4I

Secure your login and protect your Gmail, Facebook, Dropbox, Outlook, LastPass, Dashlane, 1Password, accounts and more.

Download a Security Risk Assessment Steps paper!

Security Risk assessment Quiz – Find Out How Your security risk assessment Stands Up!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet

Aug 22 2020

New Vulnerability Could Put IoT Devices at Risk

Category: IoT Security — DISC @ 11:36 am

A new vulnerability targets Thales, a leading maker of IoT components. Learn how the X-Force Red team identified the security flaw and best practices for addressing the risk.

Society relies so heavily on technology that the number of internet connected devices used globally is predicted to grow to 55.9 billion by 2025. Many of these devices span parts of Industrial Control Systems (ICS) that impact the physical world, assist us in our daily lives at home and monitor and automate everything from energy usage to machine maintenance at work. The potential to abuse these systems has already caught the eye of cybercriminals; according to the 2020 IBM X-Force Threat Intelligence Index, attacks against these systems increased over 2000% since 2018.

As part of their ongoing research, IBM’s team of hackers, X-Force Red, have discovered a new IoT vulnerability that can be exploited remotely. The manufacturer, Thales, has made a patch available for CVE-2020-15858 to customers since February 2020 and X-Force Red has been working together to ensure users are aware of the patch and taking steps to secure their systems.

Of the billions of smart devices in use today, Thales is one of leading makers of components that enable them to connect to the internet, securely store information and verify identities. Thales’ entire portfolio connects more than 3 billion things every year and more than 30,000 organizations rely on its solutions for everything from smart energy meters to medical monitoring devices and cars.

Source: New Vulnerability Could Put IoT Devices at Risk


How dangerous are IOT devices? | Yuval Elovici | TEDxBGU
httpv://www.youtube.com/watch?v=vgoX_m6Mkko


The IoT Architect’s Guide to Attainable Security and Privacy


Download a Security Risk Assessment Steps paper!

Security Risk assessment Quiz – Find Out How Your security risk assessment Stands Up!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet

Aug 21 2020

Mozilla offers rewards for Bypassing Firefox Exploit Mitigations

Category: cyber security,Hacking,Security vulnerabilities — DISC @ 10:34 am

Mozilla has expanded its bug bounty program including rewards for bypass methods for the exploit mitigations and security features in Firefox.

Source: Mozilla offers rewards for Bypassing Firefox Exploit Mitigations


Why Firefox is the best browser for privacy and how to configure things properly
httpv://www.youtube.com/watch?v=NH4DdXC0RFw


Tags: Bypassing controls, Exploit Mitigations, Mozilla security


Aug 20 2020

5 Common Accidental Sources of Data Leaks

Category: data security — DISC @ 11:39 am


5 Common Accidental Sources of Data Leaks – Nightfall AI

How do bad actors gain access to a company’s data? Most of the time, well-meaning everyday people are the real source of data insecurity.

In cybersecurity and infosec, it’s common to assume that criminals are behind all data breaches and major security events. Bad actors are easy to blame for information leaks or account takeovers, because they’re the ones taking advantage of vulnerabilities in systems to worm their way in and cause massive damage. But how do they gain access in the first place? Most of the time, well-meaning everyday people are the real source of data insecurity.

A study of data from 2016 and 2017 indicated that 92% of security data incidents and 84% of confirmed data breaches were unintentional or inadvertent. Accidental data loss continues to plague IT teams, especially as more organizations are rapidly moving to the cloud. While it’s important to prioritize action against outside threats, make sure to include a strategy to minimize the damage from accidental breaches as well.

This list of five common sources of accidental data leaks will help you identify the problems that could be lurking in your systems, apps, and platforms. Use these examples to prepare tighter security controls and keep internal problems from becoming major issues across your entire organization.

Source: 5 Common Accidental Sources of Data Leaks – Nightfall AI

Tags: Data Leaks, data loss prevention, data privacy, data ptotection, data security


Aug 19 2020

edX Courses | View all online computer science courses on edX

Category: Information Security — DISC @ 1:18 pm

Find online courses from top universities. Search all edX MOOCs from Harvard, MIT and more and enroll in a free course today.

Source: edX Courses | View all online courses on edX.org


Download a Security Risk Assessment Steps paper!

Security Risk assessment Quiz – Find Out How Your security risk assessment Stands Up!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet
Tags: Computer Science, Computer security


Aug 19 2020

IBM finds vulnerability in IoT chips present in billions of devices

Category: IoT Security,Security vulnerabilities — DISC @ 11:49 am

Manufactured by Thales, the EHS8 module family has security flaws that could allow attackers to take total control over internet-connected industrial machines.

Source: IBM finds vulnerability in IoT chips present in billions of devices


Download a Security Risk Assessment Steps paper!

Security Risk assessment Quiz – Find Out How Your security risk assessment Stands Up!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet


Aug 19 2020

FritzFrog cryptocurrency P2P botnet targets Linux servers over SSH

Category: Linux Security,Security vulnerabilities — DISC @ 11:40 am

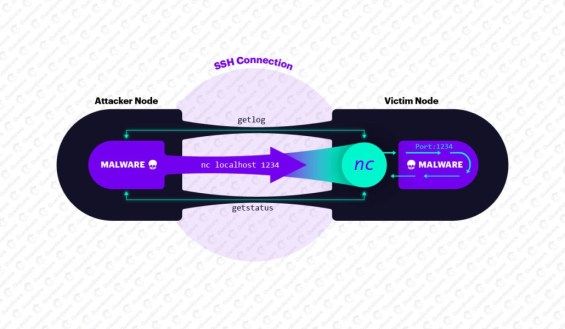
Researchers spotted a new sophisticated peer-to-peer (P2P) botnet, dubbed FritzFrog, that has been actively targeting SSH servers since January 2020.

Source: FritzFrog cryptocurrency P2P botnet targets Linux servers over SSH


Download a Security Risk Assessment Steps paper!

Security Risk assessment Quiz – Find Out How Your security risk assessment Stands Up!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet


Aug 18 2020

Advice for senior management on their responsibilities towards information risk

Category: Risk Assessment,Security Risk Assessment — DISC @ 5:55 pm

IAAC Directors’ Guides

Source:Succinct advice for senior management on their responsibilities towards information risk, courtesy of the IAAC.


Aug 18 2020

Privacy eLearning – Staff InfoSec & Compliance Awareness

Privacy eLearning & Staff Awareness

  • Access staff awareness e-learning programs and train staff on best practice processes
  • Ensure staff can spot and respond to cybersecurity and privacy risks
  • Comply with data protection and information security legislation and standards
  • Test learner knowledge to prove compliance for auditing purposes
  • Train staff under one, manageable contract with these cost-effective annual licenses
  • Developed by industry experts our programs are updated every three months to ensure the content remains relevant
  • Gain access to any new content ITG release throughout your year-long contract
  • Customize the courses by adding links to company documents, policies, and procedures
  • Fast deployment with instant access to all of the courses
  • Reinforce awareness with monthly security updates, which include the latest news and tips


1) Complete Staff Awareness E-learning Suite
Complete Staff Awareness E-learning Suite

2) GDPR Challenge E-learning Game
This short and punchy ten-minute game will test your employees’ knowledge on real-life GDPR-relevant scenarios across different industries.

3) GDPR Staff Awareness E-learning Course
GDPR Staff Awareness eLearning Course

4) GDPR: Email Misuse Staff Awareness E-Learning Course
GDPR: Email Misuse Staff Awareness E-Learning Course

5) Information Security & ISO 27001 Staff Awareness E-Learning Course
ITG eLearning Course: Information Security & ISO27001 Staff Awareness

6) PCI DSS Staff Awareness E-Learning Course
PCI DSS Online Staff Awareness eLearning Course

7) Information Security Staff Awareness E-Learning Course
Information Security | eLearning Course

8) Phishing Staff Awareness E-Learning Course
Phishing Staff Awareness E-Learning Course

9) Data Protection Awareness Posters
Data Protection Awareness Posters

10) Phishing Awareness Posters
Phishing Awareness Posters

11) The ISMS Card Game
The ISMS Card Game

Tags: GRC eLearning, information security awareness, InfoSec eLearning, security awareness training


Aug 17 2020

Google Chrome will warn users when submitting insecure forms

Category: Security Awareness,Security vulnerabilities — DISC @ 11:24 am

Google Chrome will warn users when submitting insecure forms that deliver information via HTTP connections on HTTPS websites starting with version 86.

Source: Google Chrome will warn users when submitting insecure forms


Download a Security Risk Assessment Steps paper!

Security Risk assessment Quiz – Find Out How Your security risk assessment Stands Up!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet

Aug 15 2020

PoC exploit code for two Apache Struts 2 flaws available online

Category: Security vulnerabilities — DISC @ 11:37 am

Security researchers have discovered a PoC code and exploit available online that can be used to trigger unpatched security flaws in Apache Struts 2.

Security researchers have discovered a PoC code and exploit available on GitHub that that can be used to trigger the security vulnerabilities in Apache Struts 2.

The Proof-of-concept exploit code was released last week, it allows to trigger the CVE-2019-0230 and CVE-2019-0233 vulnerabilities in Apache Struts 2 that are classified as remote code-execution and denial-of-service issues respectively. Both vulnerabilities were addressed by the Apache team in November 2019.

According to an advisory published by the Cybersecurity and Infrastructure Security Agency (CISA) the two flaws impact Apache Struts versions 2.0.0 through 2.5.20. The Apache Struts Security Team urges administrators to upgrade their installs to Struts 2.5.22.

Apache Struts 2 is an open-source, extensible framework for creating enterprise-ready Java web applications.

Unpatched installs could allow attackers to carry out malicious activities. In 2017, the credit reporting agency Equifax suffered a massive data breach, attackers exploited the CVE-2017-5638 Apache Struts vulnerability.

The CVE-2019-0230, for which a PoC exploit code is available only, could be triggered when a threat actor sends a malicious Object-Graph Navigation Language (OGNL) expression that can result in a remote code-execution in the context of the affected application.

Depending on the privileges associated with the affected application, an attacker could perform multiple malicious activities, such as install applications; modify or delete data, or create new admin accounts.

The DoS flaw, tracked as CVE-2019-0233, affects the write permissions of file directories that could lead to conditions ripe for a DoS attack.

According to the Apache Struts Wiki description of the bug, this flaw can be triggered with a file upload to a Strut’s Action that exposes the file.

“When a file upload is performed to an Action that exposes the file with a getter, an attacker may manipulate the request such that the working copy of the uploaded file is set to read-only. As a result, subsequent actions on the file will fail with an error.” reads the advisory. “It might also be possible to set the Servlet container’s temp directory to read only, such that subsequent upload actions will fail,”

The Apache security bulletin recommends to upgrade outdated installs and verify no unauthorized system modifications have occurred on the system.

Source: PoC exploit code for two Apache Struts 2 flaws available online

Download a Security Risk Assessment Steps paper!

Security Risk assessment Quiz – Find Out How Your security risk assessment Stands Up!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet


Aug 14 2020

CISA alerts of phishing attack targeting SBA loan relief accounts

Category: Phishing — DISC @ 9:31 am

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday released an alert about phishing attacks targeting various government organizations to steal logins for the Small Business Administration COVID-19 loan relief accounts.

In a newer phishing attack that started in August, security researchers saw the threat actor using convincing tricks to fool potential victims into providing personal and financial information


Some Countermeasures:

Checking the source of the message for the sender address will reveal the real one. Simply comparing it with the legitimate email will show the fraud attempt.

Paying attention to the URL in the address bar should also ensure that you don’t fall for a trick and are on the genuine page.

CISA recommends organizations include warning banners for messages from an external source. Even if the message bypasses email defenses, users may act with more caution.

Source: CISA alerts of phishing attack targeting SBA loan relief accounts


Phishing Scam

Download a Security Risk Assessment Steps paper!

Security Risk assessment Quiz – Find Out How Your security risk assessment Stands Up!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet

Tags: SBA loan relief


Aug 13 2020

Bracing for election day, Facebook rolls out voting resources to US users

Category: Election Security — DISC @ 10:57 am

Eager to avoid a repeat of its disastrous role as a super-spreader of misinformation during the 2016 election cycle, Facebook is getting its ducks in a row. Following an announcement earlier this summer, the company is now launching a voting information hub that will centralize election resources for U.S. users and ideally inoculate at least […]

The voting information center will appear in the menu on both Facebook and Instagram. As part of the same effort, Facebook will also target U.S. users with notifications based on location and age, displaying relevant information about voting in their state. The info center will help users check their state-specific vote-by-mail options, request mail-in ballots and provide voting-related deadlines.

Along with other facets of its pre-election push, Facebook will roll previously-announced “voting alerts,” a feature that will allow state election officials to communicate election-related updates to users through the platform. “This will be increasingly critical as we get closer to the election, with potential late-breaking changes to the voting process that could impact voters,”

Source: Bracing for election day, Facebook rolls out voting resources to US users


Election Security by U.S. Election Assistance Commission
httpv://www.youtube.com/watch?v=wbXO5821SIw


Download a Security Risk Assessment Steps paper!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet
Tags: Commission on Elections, election hacking, election2020, Secure election


Aug 12 2020

If you haven’t yet patched this critical hole in SAP NetWeaver Application Server, today is not your day

Category: Security vulnerabilities — DISC @ 1:32 pm

Full details of security vuln plus proof-of-concept exploits revealed

This critical-severity bug – scoring 9.9 out of 10 on the CVSS v3 meter – can be exploited by a rogue authenticated user, or someone whose access has been hijacked, to inject arbitrary code into an application server. This means they can run malicious commands they shouldn’t be able to on the server, download sensitive information, or crash the installation.

“In consequence, an attacker can break out of the desired syntactic instructions. Injecting ABAP code in the VALUE field allows the attacker to manipulate the source code of the generated subroutine pool and thereby the execution logic of the entire module. Since the attacker can freely choose the characters that can be used in this field, arbitrary ABAP code can be injected.

“To exploit this behavior an attacker can supply special characters like ‘ and . to escape the string quotation that is built into the source code. Afterwards, an attacker can simply specify any semantically valid ABAP code that gets executed by the application server.”

Source: If you haven’t yet patched this critical hole in SAP NetWeaver Application Server, today is not your day


Download a Security Risk Assessment Steps paper!

DISC InfoSec 🔒 securing the business 🔒 via latest InfoSec titles

Subscribe to DISC InfoSec blog by Email

👉 Download a Virtual CISO (#vCISO) and Security Advisory Fact Sheet & Cybersecurity Cheat Sheet


« Previous Page — Next Page »