InfoSec Compliance & AI Governance For over 20 years, DISC InfoSec has been a trusted voice for cybersecurity professionals—sharing practical insights, compliance strategies, and AI governance guidance to help you stay informed, connected, and secure in a rapidly evolving landscape.
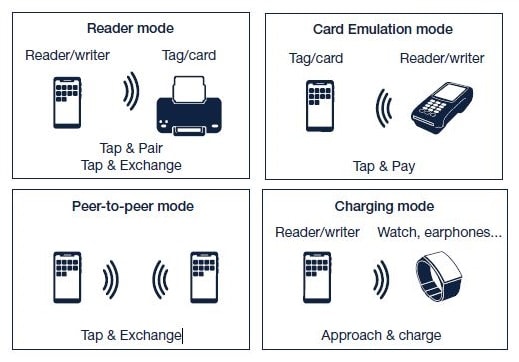
Now Rodriguez has built an Android app that allows his smartphone to mimic those credit card radio communications and exploit flaws in the NFC systems’ firmware. With a wave of his phone, he can exploit a variety of bugs to crash point-of-sale devices, hack them to collect and transmit credit card data, invisibly change the value of transactions, and even lock the devices while displaying a ransomware message. Rodriguez says he can even force at least one brand of ATMs to dispense cash though that “jackpotting” hack only works in combination with additional bugs he says he’s found in the ATMs’ software. He declined to specify or disclose those flaws publicly due to nondisclosure agreements with the ATM vendors.
The “golden age of digital transformation” is upon us, and companies around the globe are scurrying to meet consumers on the digital frontier. For developers, it is a virtual gold rush, as businesses overhaul their infrastructure to meet consumers where they are—their mobile phones. For most, this means developing a mobile app.
Unfortunately, the byproduct of the scramble to build a mobile app is that essential features are often overlooked or omitted entirely. There are many things that can be missed when creating an app (like network tolerance and accessibility)–but confoundingly, the feature that’s most often forgotten is the most important: app security.
Data use and privacy are top-of-mind for users. It is vital that software developers don’t cut corners when it comes to securing a mobile app. A secure app should pass the coffee table test: Would I be comfortable going to the bathroom and leaving my phone on a public coffee table?
First and foremost, before communications can begin, you need to determine if legal engagement with the threat actor is possible. How? An OFAC (Office of Foreign Assets Control) check must be run to see whether any data (i.e., IP addresses, language, system access, etc.) or metadata is associated with an entity that has been put on the U.S. Sanctions list. If the answer is yes, communication with and ransom payments to the attacker is prohibited.
It’s relatively rare for data from an attack to match an entity on the list because threat actors are using tools to mask their identities (i.e., VPNs, proxy connections, language translation, etc.). If you know where to dig, it’s not impossible to discover pieces of information to help unmask threat actors. For example, if a threat actor’s IP address says they are in the Netherlands, but upon reviewing the executable files they dropped on compromised systems you see they are written in Russian, this could reveal the attacker’s true location.
Once you’ve confirmed that legal engagement with the threat actor can proceed, you must weigh your answers to the following questions:
Is my data backed up and accessible on the network?
If not, can I rebuild the data from scratch?
If the stolen data is shared publicly, how will this impact the company?
No cybersecurity plan will ever be perfect, no defense is impenetrable. With the dangers and costs of a successful ransomware attack on an organization increasing daily, it is important for cybersecurity and business leaders to have a prevention and recovery plan before disaster strikes.
In Ransomware Protection Playbook experienced penetration tester and cybersecurity evangelist Roger Grimes lays out the steps and considerations organizations need to have in place including technical preventative measures, cybersecurity insurance, legal plans, and a response plan. From there he looks at the all important steps to stop and recover from an ongoing attack starting with detecting the attack, limiting the damage, and what’s becoming a trickier question with every new attack – whether or not to pay the ransom.
No organization with mission-critical systems or data can afford to be unprepared for ransomware. Prepare your organization with the Ransomware Protection Playbook.
Zero trust as a framework for securing modern enterprises has been around for years, but is drawing renewed attention with the increase in cyberattacks. The United States government is pushing for zero trust implementations across all its agencies, and more vendors are jumping on board the already rolling zero trust product bandwagon.
The mix of user need and vendor hype makes zero trust frameworks especially difficult to evaluate. Can a given zero trust solution stand up to close scrutiny? Buyers need to define and test an impartial, balanced set of complex criteria before making their purchase decisions.
Factors to consider include scalability, advanced patch management, and least-privileged access, and that is just the beginning. As automated AI-based network and application discovery gains traction, buyers must be prepared to assess the effectiveness of AI software, which is no small task.
Zero Trust security has become a major industry trend, and yet there still is uncertainty about what it means. Zero Trust is about fundamentally changing the underlying philosophy and approach to enterprise security―moving from outdated and demonstrably ineffective perimeter-centric approaches to a dynamic, identity-centric, and policy-based approach.
Making this type of shift can be challenging. Your organization has already deployed and operationalized enterprise security assets such as Directories, IAM systems, IDS/IPS, and SIEM, and changing things can be difficult. Zero Trust Security uniquely covers the breadth of enterprise security and IT architectures, providing substantive architectural guidance and technical analysis with the goal of accelerating your organization‘s journey to Zero Trust.
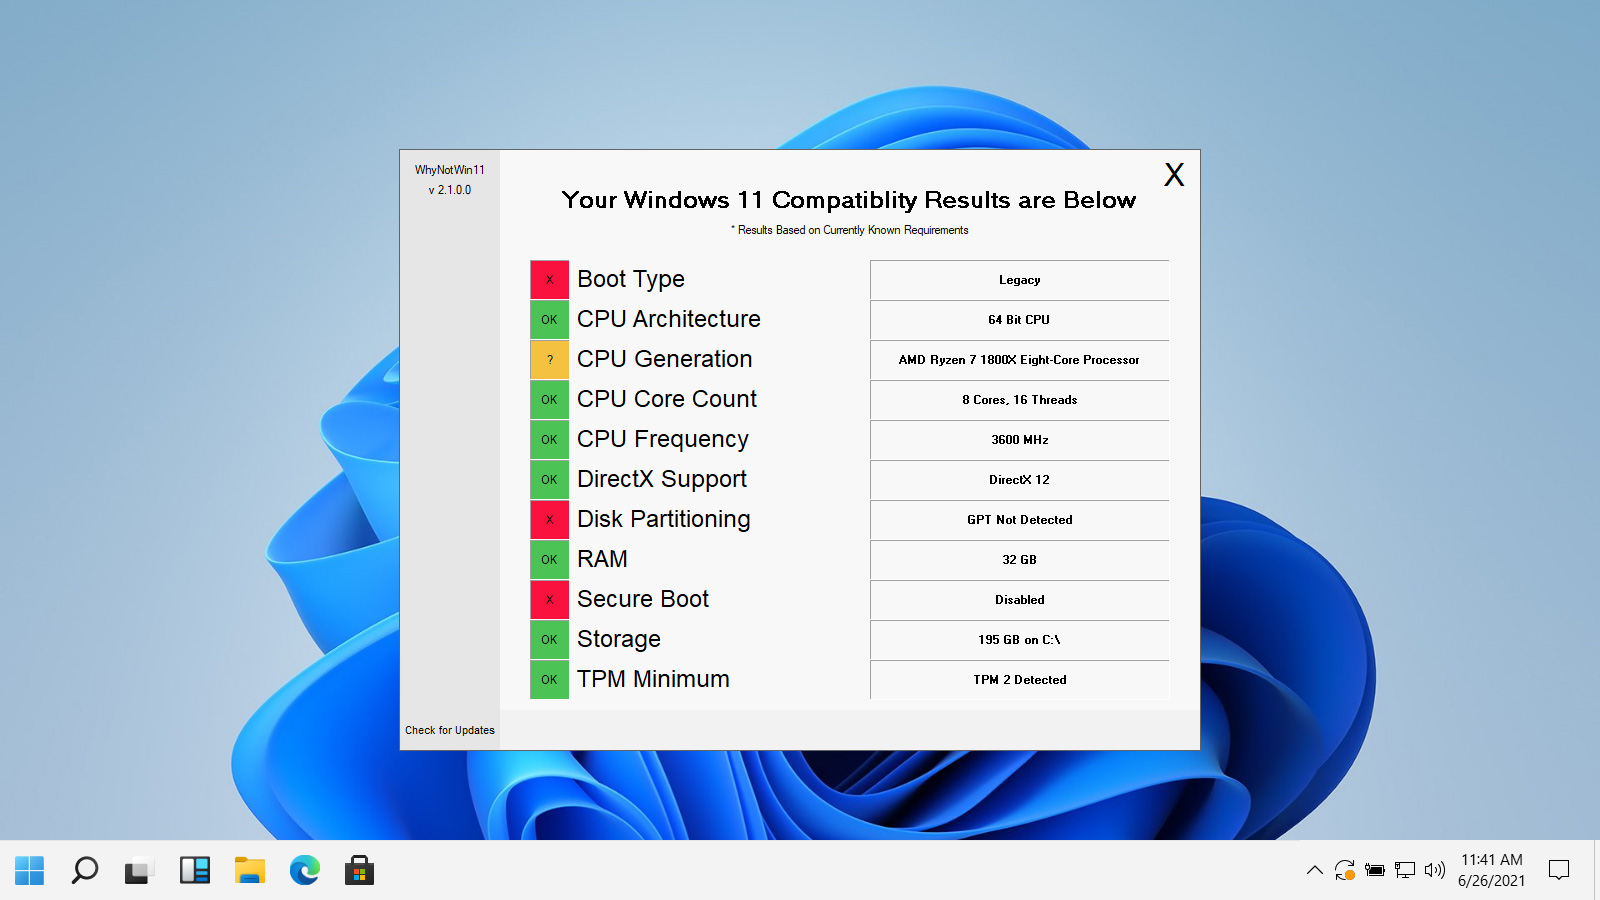
An open-source application called WhyNotWin11 acts as a better drop-in replacement for Microsoft’s PC Health Check app to determine if your hardware is compatible with Windows 11.
This week, Microsoft announced that the next version of Windows is Windows 11 would be the next version of Windows and that it would be released as a free upgrade this fall.
Microsoft released the PC Health Check app to check your computer’s hardware and tell you if it is compatible with Windows 11.
Unfortunately, Microsoft’s first version of the PC Health Check app did not tell users what hardware was failing tests, leading to even more confusion.
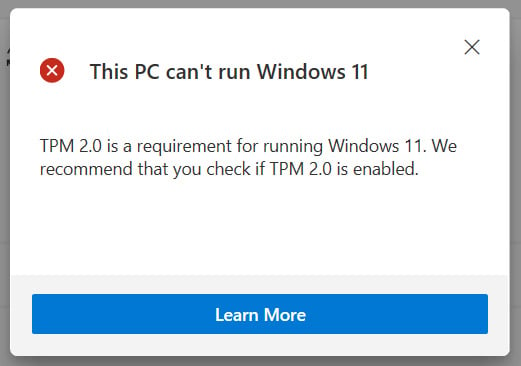
For many people, the issue was that they did not have a required TPM 2 compatible security processor enabled on their computer. As a result, Microsoft released an updated PC Health Check app that specifically warned users that a TPM 2 device was missing.
There are many factors to considered when selecting a public cloud provider, but 56% in a recent survey said security concerns had the most significant influence during the selection process for public cloud providers, IT services management company Ensono said.
Above: Ensono Cloud Clarity Report uncovered several areas that significantly influenced buying decisions.
Google today announced it has extended its Open Source Vulnerabilities (OSV) database to incorporate data from additional open source projects, using a unified schema for “describing vulnerabilities precisely.”
The benefits of open source software are widely understood, but concerns around vulnerabilities frequently rear their head. The vast majority of codebases contain at least one known open source vulnerability, while a report this week concluded that more often that not, developers don’t update third-party libraries after including them in their software. That same report noted that 92% of open source library flaws could be easily fixed with a simple update.
Open source software impacts pretty much everyone, everywhere. From small startups to major enterprises, companies rely on community-driven components in most of their applications. So it’s in everyone’s interests to ensure open source software is properly maintained.
MITRE Engenuity has released ATT&CK Workbench, an open source tool that allows organizations to customize their local instance of the MITRE ATT&CK database of cyber adversary behavior.
The tool allows users to add notes, and create new or extend existing objects – matrices, techniques, tactics, mitigations, groups, and software – with new content. It also allows them to share these insights with other organizations.
All the information technology (IT) literature emphasizes the fact that a properly managed organization should have a well-developed IT disaster recovery plan (DRP) to enable it to continue its operations in the event of a disruption and to be able to survive a disastrous interruption to its information systems. To determine the current status of IT disaster recovery plans in the UAE, this research attempts to answer the following research questions:
1) what is the overall level of disaster preparedness of businesses in the United Arab Emirates?
2) To what extent does your business have a formal and documented disaster recovery plan in place?
3) What is the level of employees’ preparedness and awareness of the existence of the DRB and their role in case of a disaster?
4) The most significant physical and logical risks that pose the most threats to drive the development of the DRB?
5) The extent of the controls in place to mitigate, avoid or transfer risk? and
6) what is the frequency of testing and exercising the DRP? To answer these questions, we surveyed the public companies listed on the Abu Dhabi Securities Exchange (ADX).
Governments and law enforcement hate it when ransomware victims pay the blackmail demands that almost always follow a ransomware attack, and you can understand why, given that today’s payments fund tomorrow’s cybercriminality.
Of course, no one needs to be told that.
Paying up hurts in any number of ways, whether you feel that hurt in your head, in your heart or even just in the pit of your stomach.
“I was happy to pay up for a job well done,” said no ransomware victim ever.
However, it’s easy for people who aren’t looking down the wrong end of the cybercrime barrel to say, “You should never, ever pay. You should let your entire business implode, and let everyone in the company lose their job, because that’s just the price of failure.”
So, if your back’s against the wall and you DO pay up in the hope that you’ll be able to restart a business that has ground to a total halt…
…how well will it all go?
Guess what? You can find out by tuning into a fun but informative talk that we’re giving twice this week.
You need to register, but both events are free to join. (They’re both 100% virtual, given that the UK is still in coronavirus lockdown, so feel free to attend from anywhere.)
We’ll give you a clue by sharing a key slide from the talk:
As you can see, paying up often doesn’t work out very well anyway, even if you have no ethical qualms about doing so, and enough money burning a hole in your pocket to pay without flinching.
And remember that if you lose 1/3 of your data, like 1/2 of our respondents said they did, you don’t get to choose which computers will decrypt OK and which will fail.
Murphy’s law warns you that the laptops you could have reimaged easily enough will probably decrypt just fine, while those servers you really meant to backup but didn’t… probably won’t.
We’re going to try to make the talk amusing (as amusing as we dare be when talking about such a treacherous subject), but with a serious yet not-too-technical side.
We’ll be giving some tips you can use both at work and at home to reduce the risk of getting ransomed in the first place.
No cybersecurity plan will ever be perfect, no defense is impenetrable. With the dangers and costs of a successful ransomware attack on an organization increasing daily, it is important for cybersecurity and business leaders to have a prevention and recovery plan before disaster strikes.
In Ransomware Protection Playbook experienced penetration tester and cybersecurity evangelist Roger Grimes lays out the steps and considerations organizations need to have in place including technical preventative measures, cybersecurity insurance, legal plans, and a response plan. From there he looks at the all important steps to stop and recover from an ongoing attack starting with detecting the attack, limiting the damage, and what’s becoming a trickier question with every new attack – whether or not to pay the ransom.
No organization with mission-critical systems or data can afford to be unprepared for ransomware. Prepare your organization with the Ransomware Protection Playbook.
TOR Anonymity Network 101 If you have been searching for how to access the most private and secure part of the internet, then look no more! The TOR Anonymity Network 101 – An Introduction To The Most Private Part Of The Internet has everything you’ve ever wanted to learn about how to be completely anonymous online. We live in an age where despite our best intentions, everything we do online is open to monitoring or attack. Our own advances in technology which were supposed to make our lives easier can be twisted and used against us. Knowing how to protect our own best interests is a vital skill that everyone should be aware of. The TOR Anonymity Network 101 includes: * How to maintain your anonymity online * The key to networking 101 * An introduction to the most private parts of the internet & much more! TOR doesn’t stop you from being seen on the internet, but it will prevent people from learning your location and using that information against you. If you value your privacy, then you need to check out TOR Anonymity Network 101 – An Introduction To The Most Private Part Of The Internet for yourself!
Threat actors in January attempted to poison the water at a US facility, a circumstance that highlights the importance of cybersecurity for water and wastewater utilities. The news that a threat actor in January attempted to poison the water at a facility…
“The technology controlling United States nuclear weapons predates the Internet. Updating the technology for the digital era is necessary, but it comes with the risk that anything digital can be hacked. Moreover, using new systems for both nuclear and non-nuclear operations will lead to levels of nuclear risk hardly imagined before. This book is the first to confront these risks comprehensively. With Cyber Threats and Nuclear Weapons, Herbert S. Lin provides a clear-eyed breakdown of the cyber risks to the U.S. nuclear enterprise. Featuring a series of scenarios that clarify the intersection of cyber and nuclear risk, this book guides readers through a little-understood element of the risk profile that government decision-makers should be anticipating. What might have happened if the Cuban Missile Crisis took place in the age of Twitter, with unvetted information swirling around? What if an adversary announced that malware had compromised nuclear systems, clouding the confidence of nuclear decision-makers? Cyber Threats and Nuclear Weapons, the first book to consider cyber risks across the entire nuclear enterprise, concludes with crucial advice on how government can manage the tensions between new nuclear capabilities and increasing cyber risk. This is an invaluable handbook for those ready to confront the unique challenges of cyber nuclear risk”–
We don’t often put out programming appeals on Naked Security, especially when the code that we’re looking for is dangerous and destructive.
But this time we’re prepared to make an exception, given that it’s a rainy Friday afternoon where we are, and that this issue is now in its fifteenth consecutive year.
Our attention was drawn to the problem by a tweet from well-known Google cybersecurity researcher Tavis Ormandy, who tweeted today to say:
Carnival Corp. this week confirmed that the data breach that took place in March might have exposed personal information about customers and employees of Carnival Cruise Line, Holland America Line, and Princess Cruises.
Carnival Corporation & plc is a British-American cruise operator, currently the world’s largest travel leisure company, with a combined fleet of over 100 vessels across 10 cruise line brands. A dual-listed company,
Carnival Corporation has over 150,000 employees and 13 million guests annually. The cruise line operates under the brands Carnival Cruise Line, Costa, P&O Australia, P&O Cruises, Princess Cruises, Holland American Line, AIDA, Cunard, and their ultra-luxury cruise line Seabourn.
The company sent a data breach notification letter to its customers to inform them that unauthorized parties might have gained access to their data, including social Security numbers, passport numbers, dates of birth, addresses and health information of people.
At the time of this writing, the number of impacted individuals was not revealed, it is also unclear if the company paid a ransom.
In 2020, the company was the victim of two distinct ransomware attacks that took place in August and December. In October, Carnival Corporation disclosed a data breach as a result of the ransomware attack that took place in August. Ransomware operators have stolen the personal information of customers, employees, and ship crews during the attack.
The recent security breach was spotted on March 19, in response to the incident, the IT staff shut down access and launched an investigation with the help of a cybersecurity.
The company announced to have implemented additional security measured to protect its infrastructure.
The cruise operator set up a call center to provide supports to its customers.
The good news is that the company is not aware of any abuse of personal information stolen during the intrusions.
In the first part of my blog post I focused on calculating the impact of a cybersecurity breach in relation to a company’s size and industry. In part two, I present an approach to better understand how often a company will experience security breaches.
The probability is usually the big unknown. Not particularly helpful is that our abilities to estimate a probability are inferior to our abilities to estimate damage. In addition, we must consider a range of limitations to our abilities to estimate. We don’t estimate well in magnitudes very small or large. Once in 1,000 years and once in 10,000 years is harder to differentiate than once per year and once in 10 years. Also, we tend to overestimate the probability of recently occurred incidents.
The great uncertainty drives risk practitioners to reduce their risk assessments to pure impact assessments (“Estimations of probability can only be wrong!”). However, we can use what is out there on data and make comparisons.
Did you know the odds of being struck by lightning in a given year are only around 1 in 100,000,000? That’s not a scary thought, mainly since 9 out of 10 people survive.
But when it comes to identity theft, the odds are 1 in 15. Worldwide, there’s a new victim every 2 seconds. Now, that is spine-chilling!
Identity theft is the most common consequence of a data breach. Defrauding and stealing someone’s identity is easier today than it has ever been in history.
Let’s go behind the scenes of an identity theft maneuver and learn how you can protect yourself from it.
What is identity theft
Identity theft occurs when someone uses your personal identifying information (like your name, social security number, or credit card number) without your knowledge or permission. The purpose of identity theft is to commit fraud or other crimes.
Identity thieves gain financial advantages or other benefits, while victims suffer financial loss and possibly other severe consequences, including being accused of a crime they didn’t commit.
Most interesting to me is the home countries of these companies. Express VPN is incorporated in the British Virgin Islands. NordVPN is incorporated in Panama. There are VPNs from the Seychelles, Malaysia, and Bulgaria. There are VPNs from more Western and democratic countries like the US, Switzerland, Canada, and Sweden. Presumably all of those companies follow the laws of their home country.
And it matters. I’ve been thinking about this since Trojan Shield was made public. This is the joint US/Australia-run encrypted messaging service that lured criminals to use it, and then spied on everything they did. Or, at least, Australian law enforcement spied on everyone. The FBI wasn’t able to because the US has better privacy laws.
We don’t talk about it a lot, but VPNs are entirely based on trust. As a consumer, you have no idea which company will best protect your privacy. You don’t know the data protection laws of the Seychelles or Panama. You don’t know which countries can put extra-legal pressure on companies operating within their jurisdiction. You don’t know who actually owns and runs the VPNs. You don’t even know which foreign companies the NSA has targeted for mass surveillance. All you can do is make your best guess, and hope you guessed well.
The same should be pertinent for any technology or piece of software or hardware produced in other countries where privacy and copywrite laws are lax , anything supporting technology from a piece of software or hardware.
A flaw in the Peloton Bike+ could be exploited by an attacker with initial physical access to gain root entry to the interactive tablet, taking complete control of the system.
A vulnerability in the popular Peloton Bike+ could have allowed an attacker to gain complete control over the device, including the camera and microphone to spy on the gym users.
The flaw was discovered by researchers from McAfee’s Advanced Threat Research (ATR) team, it could be exploited by attackers to gain remote root access to the Peloton’s “tablet.” The touch screen tablet allows users to access interactive and streaming content.
Experts pointed out that the attackers need physical access to the bike or access during any point in the supply chain (from construction to delivery),
Experts noticed that the tablet is a standard Android device, once compromised it, the attacker could install malware, eavesdrop on traffic, and take the full control of the Bike+.
“A hacker enters a gym or fitness center with a Peloton Bike+. They insert a tiny USB key with a boot image file containing malicious code that grants them remote root access. Since the attacker doesn’t need to factory unlock the bike to load the modified image, there is no sign that it was tampered with.” reads the analysis published by the experts. “With their newfound access, the hacker interferes with the Peloton’s operating system and now has the ability to install and run any programs, modify files, or set up remote backdoor access over the internet. “
The attackers could add malicious apps disguised as popular applications, such as Netflix or Spotify, that could allow them to steal the login credentials of the gym users. An attacker could also gather info regarding users’ workouts or spy on them via the bike’s camera and microphone.
Attackers could decrypt the encrypted communications from the bike to various cloud services and databases it accesses, potentially accessing sensitive information.
The researchers discovered that the Bike’s system did not verify that the device’s bootloader was unlocked before attempting to boot a custom image, allowing the experts to load a file that wasn’t meant for the Peloton hardware.