Aug 01 2022

Threat Actors Circumvent Microsoft Efforts to Block Macros

Category: Cyber Threats,Malware — DISC @ 8:50 am

Microsoft’s announcement that it would block macros in Microsoft Office apps by default didn’t stop threat actors—they have simply resorted to new tricks.

“Threat actors across the landscape responded by shifting away from macro-based threats,” Proofpoint researchers noted in a blog post. In fact, an analysis of campaign data, “which include threats manually analyzed and contextualized,” showed the use of VBA and XL4 Macros ticked down 66% or so between October 2021 and June 2022.

“While Proofpoint observed a notable increase in other attachment types, macro-enabled documents are still used across the threat landscape,” the researchers wrote, explaining that the tactics, techniques and procedures (TTPs) have changed, with miscreants turning to use of container files—like ISO and RAR—and Windows Shortcut files to pass malware along, according to Proofpoint research.

Threat actors have long used VBA macros “to automatically run malicious content when a user has actively enabled macros in Office applications. XL4 macros are specific to the Excel application, but can also be weaponized by threat actors,” researchers pointed out. “Typically, threat actors distributing macro-enabled documents rely on social engineering to convince a recipient the content is important, and enabling macros is necessary to view it.”

Microsoft took steps to block VBA macros by keying on a Mark of the Web (MOTW) attribute called the Zone.Identifier that shows whether a file comes from the internet and is added by Microsoft apps to some documents downloaded from the web. But bad actors can bypass MOTW by using container file formats.

By using container file formats like ISO (.iso), RAR (.rar), ZIP (.zip) and IMG (.img) files to send macro-enabled documents, “ … the ISO, RAR, etc. files will have the MOTW attribute because they were downloaded from the internet, but the document inside, such as a macro-enabled spreadsheet, will not,” researchers noted. “When the document is extracted, the user will still have to enable macros for the malicious code to automatically execute, but the file system will not identify the document as coming from the web.”

They also can distribute payloads directly using container files so that when they’re opened they can contain “additional content such as LNKs, DLLs or executable (.exe) files that lead to the installation of a malicious payload.”

“The change to block macros by default is a very good thing; has been suggested for years and it’s good Microsoft is finally doing it,” said Rob Jenks, SVP strategy and business at Tanium. He explained that “as with all security techniques, it’s not a silver bullet and attackers inevitably move on to the next attack pathway(s)—so the findings aren’t surprising.”

But “regarding the new attacks, there are other restrictions on not trusting zip content, so these other mechanisms throw more consent dialogs into the user’s face, potentially making a phishing attack less reliable,” Jenks said.

Proofpoint researchers have not only noted a two-thirds decrease in macro-enabled documents leveraged as attachments in email-based threats, but they observed “the number of campaigns leveraging container files including ISO and RAR, and Windows Shortcut (LNK) attachments increased nearly 175%,” researchers said.

“They attribute the increase in part to the uptick in use of ISO and LNK files in campaigns. Cybercriminal threat actors are increasingly adopting these as initial access mechanisms, such as actors distributing Bumblebee malware,” they said. “The use of ISO files increased over 150% between October 2021 and June 2022. More than half of the 15 tracked threat actors that used ISO files in this time began using them in campaigns after January 2022.”

Most notably, LNK files have emerged as a go-to for threat actors—at least 10 of them have begun using LNK files since February.  In fact, the number of campaigns containing LNK files exploded an incredible 1,675% since October 2021.

While fewer campaigns are using XL4 macros, Proofpoint did see a spike in macro use in March 2022, which researchers attributed to an uptick in campaigns with higher volumes of messages conducted by the TA542 actor delivering Emotet. “Typically, TA542 uses Microsoft Excel or Word documents containing VBA or XL4 macros,” the researcher wrote. “Emotet activity subsequently dropped off in April and it began using additional delivery methods including Excel Add-In (XLL) files and zipped LNK attachments in subsequent campaigns.”

The adoption of ISO and other container file formats is driving the pivot away from macro-enabled documents to different file types that can bypass the macro-blocking protections offered by Microsoft. “Such filetypes can bypass Microsoft’s macro blocking protections, as well as facilitate the distribution of executables that can lead to follow-on malware, data reconnaissance and theft and ransomware,” said Proofpoint researchers, who called the change “one of the largest email threat landscape shifts in recent history.”

Proofpoint has also observed a slight increase in threat actors using HTML attachments to deliver malware. The number of malware campaigns using HTML attachments more than doubled from October 2021 to June 2022, but the overall number remains low. Proofpoint researchers also observed threat actors increasingly adopt HTML smuggling, a technique used to “smuggle” an encoded malicious file within a specially crafted HTML attachment or web page.

Microsoft Koverse data protection impact assessment DPIA Dell AWS data protection cybersecurity

Tags: Block Macros, Threat actors


Aug 01 2022

A flaw in Dahua IP Cameras allows full take over of the devices

Category: Security vulnerabilities — DISC @ 8:40 am

A vulnerability, tracked as CVE-2022-30563, impacting Dahua IP Camera can allow attackers to seize control of IP cameras.

The CVE-2022-30563 vulnerability impacting Dahua IP Camera can allow attackers to seize control of IP cameras. The issue affects Dahua’s implementation of the Open Network Video Interface Forum (ONVIF).

ONVIF provides and promotes standardized interfaces for effective interoperability of IP-based physical security products.

The vulnerability was discovered by researchers from Nozomi Networks and received a CVSS score of 7.4.

“We’re publishing the details of a new vulnerability (tracked under CVE-2022-30563) affecting the implementation of the Open Network Video Interface Forum (ONVIF) WS-UsernameToken authentication mechanism in some IP cameras developed by Dahua, a very popular manufacturer of IP-based surveillance solutions.” reads the advisory published by Nozomi Networks. “This vulnerability could be abused by attackers to compromise network cameras by sniffing a previous unencrypted ONVIF interaction and replaying the credentials in a new request towards the camera.”

ONVIF-conformant products allow users to perform a variety of actions on the remote device through a set of standardized Application Programming Interfaces (APIs), including watching camera footage, locking or unlocking a smart door, and performing maintenance operations.

The flaw resides in the “WS-UsernameToken” authentication mechanism implemented by Dahua in some of its IP cameras. Due to the lack of checks to prevent reply attacks, a threat actor can sniff an unencrypted ONVIF interaction and indefinitely replay the credentials in new requests towards the camera, which would be accepted as valid authenticated requests by the device.

Once obtained the credentials, an attacker can add an administrator account and use it to obtain full access to the device and perform actions such as watching live footage from the camera as shown below.

An attacker can conduct this attack by capturing one unencrypted ONVIF request authenticated with the WS-UsernameToken schema.

dahua

The following versions of Dahua video products, are affected:

  • Dahua ASI7XXX: Versions prior to v1.000.0000009.0.R.220620
  • Dahua IPC-HDBW2XXX: Versions prior to v2.820.0000000.48.R.220614
  • Dahua IPC-HX2XXX: Versions Prior to v2.820.0000000.48.R.220614

The vendor addressed the issue with the release of a patch on June 28, 2022,

“In addition to building security, surveillance cameras are used throughout many critical infrastructure sectors such as oil & gas, power grids, telecommunications, etc. These cameras are used to oversee many production processes, providing remote visibility to process engineers. Threat actors, nation-state threat groups in particular, could be interested in hacking IP cameras to help gather intel on the equipment or production processes of the target company.” concludes Nozomi. “This information could aid in reconnaissance conducted prior to launching a cyberattack. With more knowledge of the target environment, threat actors could craft custom attacks that can physically disrupt production processes in critical infrastructure.”

Tags: Dahua IP Cameras


Jul 30 2022

Why And How CISOs Are Making API Security A Top Priority

Category: API security — DISC @ 10:45 am
藍色網絡上的鎖

A CISO’s mandate is to empower the business to move forward on key growth initiatives and simultaneously reduce risk. To this end, they must continuously evaluate and weigh the security ramifications of many strategic initiatives, ultimately weighing the potential impact on a company’s:

• Speed to market.

• Competitive advantage.

• Brand reputation.

By focusing on how their security infrastructure helps or hinders delivery on those three fronts, CISOs help drive business success. In today’s landscape, one new area has emerged that is integrally connected to all three of those company dynamics: the use of APIs to fuel innovation.

APIs are eating the world.

APIs are essential for companies to support their innovative and revenue-generating digital transformation initiatives. Open banking services, mobile and online services, digital information sharing apps, brands like DoorDash, Uber, PayPal, Spotify, Netflix, Tesla—you name it—all require APIs to function.

Companies are developing and pushing out APIs faster, and in larger quantities, than ever before. APIs allow companies to build and bring advanced services to market, opening up new avenues of business and revenue streams. Digitalization hastened this trend, and Covid accelerated its implementation. Companies had to quickly deploy remote services for workers and customers and build product integrations to support myriad devices—all of which demanded APIs. It’s no wonder that the public API hub Postman hit a record 20 million users earlier this year.

However, because APIs share highly sensitive data with customers, partners and employees, they have also become a very attractive target for attackers. CISOs have recognized the risk.

According to a new study released by AimPoint Group, W2 Communications and CISOs Connect, titled The CISOs Report, Perspectives, Challenges and Plans for 2022 and Beyond, CISOs identified the following as their top IT components needing security improvement.

• APIs: 42%

• Cloud applications (SaaS): 41%

• Cloud infrastructure (IaaS): 38%

APIs drive speed to market.

The faster a business can bring new services to market, the faster the benefits. For some companies (under Covid), speed to market meant the difference between keeping the business up and running versus shutting down operations. API usage ensured that organizations were open for business.

Businesses must always assess the value and the costs in terms of both achieving or losing the speed-to-market race. They must consider the obstacles that could prevent speed to market. In the case of APIs, security threats pose an enormous obstacle. They can slow down rollouts or, even worse, make them untenable.

By protecting APIs from exploitation, companies ensure their ability to drive speed to market, growth opportunities and competitive advantage.

APIs deliver a competitive advantage.

Speed to market is an important underlying factor that contributes to an organization’s competitive advantage. As an industry front runner, businesses have an opportunity to gain the lion’s share of a market and its profits.

In financial services, competitive advantage is a critical business objective, and technology transformation is its core strategic component. Fintech companies have fueled customer expectations, and open banking is right behind them, offering unimaginable innovation and conveniences by easily linking mobile apps to banking accounts.

Banking and financial institutions must stay on the cutting edge of these services to compete and stay relevant. APIs power these capabilities and allow institutions to leapfrog ahead of the competition.

However, security threats and lack of regulatory adherence can compromise successful API implementation and result in costly fines. Businesses must ensure safe passage between the emerging applications and customers’ valuable financial data. APIs represent the access point to PII and other important data assets that attackers target for their own gain and to the detriment of the business.

Dedicated API security is the cost of doing business.

The monetary growth opportunities promised by APIs are immense, but to harness them, CISOs must ensure the protection of their APIs. APIs support the interconnectivity of a company’s crown jewels—the essential and sensitive data that businesses require to deliver their digital goods and services.

Every company that is developing software has become an API-driven company. For API-driven companies, protecting those APIs is no longer a question—it’s simply the cost of doing business in a digitally transformed landscape. Without dedicated API security to protect these crucial connectivity tools, companies put everything at risk—speed to market, competitive advantage and the brand itself.

Last but not least, CISOs must build a collaborative approach to API security. APIs touch all areas of the business. CISOs need to take an active role in educating teams about their API security initiatives and their importance in reducing the company’s risks. CISOs must provide the answers and insights that empower others to help meet security goals.

CISO after CISO will tell you that creating a strong, cross-functional “security-aware” culture continues to be their number one priority. To generate this security mindset, leaders must prioritize relationships, acknowledge everyone’s contribution to security and continuously communicate the vital importance of security to achieve overall business objectives.

https://www.forbes.com/sites/forbestechcouncil/2022/07/29/why-and-how-cisos-are-making-api-security-a-top-priority/

API Security in Action

Tags: API Security


Jul 29 2022

22 million US health records breached thus far in 2022

Category: hipaa — DISC @ 8:47 am

Hackers can use personal healthcare information to target victims with fraudulent schemes related to their medical history.

A new report from GlobalData estimates that up to 22 million US health records have been breached so far in 2022.

The same report forecasts that spending on cybersecurity in the global healthcare industry will increase by nearly $400 million in the next 3 years.

This increase is sorely needed in a sprawling industry which is so often behind the times in terms of information security. The health care industry is often a prime target of ransomware attacks as they store valuable and confidential information on their customers.

Included in this collection is not only names, date of births and medical record numbers but also private health information (PHI) which can include one’s medical history, address, email addresses, and social security numbers.

Using this information, threat actors can design a number of phishing schemes to target patients for further exploitation. Unlike credit card information or personal identification information, medical history cannot be changed, making it much more valuable on the black market.

Over 41 million individuals in the US alone were affected by healthcare data breaches in 2021, according to reports of breaches affecting 500 individuals or more by the US Department of Health and Human Services (HHS) Office of Civil Rights

The largest presently known breach for 2022 so far was the breach at Shields Health Care Group, which affected as many as two million individuals.

Doctor holding phone

Security Management for Healthcare: Proactive Event Prevention and Effective Resolution

DISC InfoSec

#InfoSecTools and #InfoSectraining

#InfoSecLatestTitles

#InfoSecServices

Ask DISC an InfoSec & compliance related question

Tags: US health records breached


Jul 29 2022

Strong Authentication – Robust Identity and Access Management Is a Strategic Choice

Category: Authentication,Password Security — DISC @ 8:26 am

Passwords no longer meet the demands of today’s identity and access requirements. Therefore, strong authentication methods are needed.

“Usernames and passwords are insufficient and vulnerable means of authentication on their own; therefore, it is essential to employ strong authentication techniques like multi-factor authentication (MFA) to confirm users’ identities before granting secure access to resources,” Sarah Lefavrais, Product Marketing Manager, Thales states in her recent article. It’s true. Passwords no longer meet the demands of today’s identity and access requirements. Therefore, strong authentication methods are needed to improve security without hindering user convenience.

What is Strong Authentication?

Tech Target states that strong authentication is “any method of verifying the identity of a user or device that is intrinsically stringent enough to ensure the security of the system it protects by withstanding any attacks it is likely to encounter.” It is commonly referred to as a way to confirm a user’s identity when passwords are not enough. As Tech Target continues, the European Bank and many that adopt its guidelines state that strong authentication must include “at least two mutually-independent factors” so that the compromise of one will not lead to the compromise of the other. These factors are:

  • Knowledge – Something the user knows
  • Possession – Something the user has
  • Inherence – Something the user is

As Lefavrais states, employing more than one of these measures is needed to ensure only legitimate users can access applications and services,  and when applications contain sensitive data such as confidential, personally identifiable information that needs to be protected. 

In IAM strategy, strong authentication methods like MFA and Modern Authentication are quickly replacing traditional methods like passwords, especially as the new gold standard for how IT and security teams enforce access controls, and gain visibility into access events – especially as workloads move to the cloud, VMs and across remote and hybrid environments.

The IAM Security BoundaryStrong authentication is a critical component of modern-day identity and access management. It not only provides additional layers of security around entry points, but allows for customizable levels of authentication, authorization, and access control throughout your environment, giving users only the permissions (and sign-in requirements) they need. To illustrate that point, we’ll investigate two of the primary methods, MFA and Modern Authentication, further in-depth.

Multi-factor Authentication (MFA) is widely seen as the strongest mode of authentication. MFA allows you to:

  • Protect against the compromise made possible by weak passwords. With MFA, a password alone is insufficient to grant access, so credential stuffing and brute force attacks are rendered useless.
  • Reduce identity theft from phishing and other social engineering schemes. Even if you do click on that email and enter a few credentials, if your bank, work VPN, or other access point requires MFA (especially with tokenization, biometrics, or location-based entry), chances are those credentials won’t be enough, and hackers will move on to easier targets.
  • Stay within compliance boundaries like the OMB Memorandum for Zero Trust Cybersecurity and the European Union Agency for Cybersecurity (ENISA) and CERT-EU guidelines, as noted by Lefavrais. These require MFA use throughout subordinate enterprises.

A few MFA methods used in strong authentication include:

  • FIDO security keys
  • Certificate-based smart cards and certificate-based USB tokens
  • Mobile phone and software-based authentication
  • One Time Password (OTP) authenticators
  • Pattern-based (or grid) authenticators
  • Hybrid tokens

Modern Authentication relies on technologies, such as FIDO and Webauthn, contextual authentication and modern federation protocols, which ensure proper user identity and access controls in cloud environments.  That means you can implement more effective access security for cloud apps, alongside the existing access controls that are already in place for on-premises and legacy applications. Flexible policy-based access enable a friendly experience while maintaining a high level of security for roles or resources requiring it.

What to Look for in a Strong Authentication Service

When choosing a strong authentication service, be it on-premises or in the cloud, features to consider are:

  1. Policy-based access with ability to implement conditional access. In order to optimize the end user experience while maintain the best access security for a particular user and application, look for a solution that can enforce a range of authentication methods through policies and risk scoring.
  2. Resistant to phishing. Phishing accounts for roughly a quarter of all data breaches, according to Verizon’s 2021 DBIR. Strong authentication solutions with FIDO2 can both authenticate securely and prevent attacks.
  3. User experience. Do the methods involved create security fatigue, or is it simple to secure multiple-use authentication journeys?
  4. Adaptability and customizability. Can you assign different access controls based on role or asset? What about context, environment, or use case?

Ultimately, you need to ensure your strong authentication provider supports your industry’s identity and access regulations and integrates smoothly with your current identity environment, deploying flexibly and maintaining equilibrium as you transition over. To maintain a risk-based authentication posture, IAM solutions must continue evolving alongside increased digitization demands.  When a single lock and key no longer suffice to safeguard the VMs, remote environments, and cloud-based assets of today, we must adopt the access management and strong authentication methods that can.

About the Author: Katrina Thompson is an ardent believer in personal data privacy and the technology behind it, Katrina Thompson is a freelance writer leaning into encryption, data privacy legislation and the intersection of information technology and human rights. She has written for Bora, Venafi, Tripwire and many other sites.

Strong Authentication

Solving Identity Management in Modern Applications: Demystifying OAuth 2.0, OpenID Connect, and SAML 2.0

Tags: Identity and Access Management


Jul 28 2022

Experts warn of hacker claiming access to 50 U.S. companies through breached MSP

Category: Hacking,Security Breach — DISC @ 2:23 pm
Experts warn of hacker claiming access to 50 U.S. companies through breached MSP

Experts warn of hacker claiming access to 50 U.S. companies through breached MSP

Cybersecurity experts are raising concerns about an individual on a hacker forum claiming to have access to 50 American companies through an unnamed managed service provider (MSP).

MSPs are paid to manage IT infrastructure and provide support, typically by smaller organizations lacking their own IT departments. In recent years they have been singled out by cybersecurity agencies as potentially vulnerable access points for hackers to exploit.

Harlan Carvey, senior incident responder at cybersecurity firm Huntress, told The Record that on July 18 someone with the handle “Beeper” had posted in Russian on exploit.in asking for help monetizing access to a managed service provider.

“Looking for a Partner for MSP processing. I have access to the MSP panel of 50+ companies. Over 100 ESXi, 1,000+ servers … I want to work qualitatively, but I do not have enough people,” the translated message said.

“In terms of preparation, only little things are left, so my profit share will be high. Please send me a message for more details and suggestions.”

https://therecord.media/experts-warn-of-hacker-claiming-access-to-50-u-s-companies-through-breached-msp/

Several cybersecurity experts have shared the message on Twitter and other social media sites warning of the potential fallout from the kind of access the hacker purportedly has. 

Carvey said it appears that the hacker gained access to an MSP’s management system and has already done some of the initial legwork.

“It sounds as if they’re claiming to have done some pre-work, perhaps something like identifying an account with a high privilege level. As a result, anyone who takes them up on their offer isn’t going to have to do much ‘heavy lifting’ to achieve whatever their goals may be,” Carvey said. “It doesn’t appear that there’s any data involved at this point, per se. Intent isn’t clear at this point, and it may depend upon who responds to the ad. The original poster does seem to be offering to answer questions and provide additional details.”

Carvey added that based on the typical customer base he sees for MSPs, personal details, business data and healthcare information could be at risk. 

Some online noted that Kansas City-based MSP NetStandard announced on Wednesday morning that their hosted environment had been hit by a cyberattack. The company did not respond to requests for comment but told customers they discovered the attack on Tuesday and are “working to isolate the threat and minimize impact.”

“MyAppsAnywhere services, which include Hosted GP, Hosted CRM, Hosted Exchange, and Hosted Sharepoint, will be offline until further notice,” the company said. 

“At this point, no additional information on the extent of the impact nor time to resolution can be provided. We are engaged with our cybersecurity insurance vendor to identify the source of the attack and determine when the environment can be safely brought back online.” 

The cybersecurity authorities of the U.K. (NCSC-UK), Australia (ACSC), Canada (CCCS), New Zealand (NCSC-NZ), and the United States (FBI, CISA and NSA) warned in May that hackers and APT groups have stepped up their targeting of MSPs in their efforts to exploit provider-customer network trust relationships.

Two of the most prominent hacks from the last two years involved popular MSPs – SolarWinds and Kaseya – and caused widespread damage due to the access they have to hundreds of companies and government agencies. 

The CISA alert noted that government agencies are aware of reports of an increase in malicious cyber activity targeting MSPs, adding that they “expect this trend to continue.”

“As this joint advisory makes clear, malicious cyber actors continue to target managed service providers, which can significantly increase downstream risk to the businesses and organizations they support – why it’s critical that MSPs and their customers take action to protect their networks,” said CISA Director Jen Easterly. 

The agencies provided a range of recommendations to MSPs, such as hardening defenses against password spraying and phishing by potential attackers.

Former Obama administration cybersecurity commissioner Tom Kellermann, who now serves as head of cybersecurity strategy at VMware, previously told The Record that cybercrime cartels have studied the interdependencies of financial institutions and have a better understanding of which MSPs are used.

“In turn, these organizations are targeted and hacked to island hop into banks. Rogue nation states love this method of cyber-colonization,” Kellermann explained, referring to an attack that targets a third party in order to gain access to another entity. VMware has found that such attacks have increased 58% over the past year.

“I am concerned that as geopolitical tension metastasizes in cyberspace, these attacks will escalate and Russian cyber-spies will use this stratagem to deploy destructive malware across entire customer bases of MSP,” he said.

Tags: breached MSP


Jul 28 2022

State of Cybersecurity 2022

Category: cyber security,Information Security — DISC @ 10:55 am

State of Cybersecurity 2022 – via ISACA

State of Cybersecurity 2022, Global Update on Workforce Efforts, Resources and Cyberoperations

State of Cybersecurity 2022, Global Update on Workforce Efforts, Resources and Cyberoperations reports the results of an eighth annual global study that looks at the following topics and more:

  • What are the top cybersecurity hiring challenges today?
  • Which cybersecurity skills are in highest demand?
  • How can companies improve retention?
  • How are cybersecurity budgets changing?
  • Which threat vectors are the most concerning?
  • How frequently are companies conducting cyber risk assessments?

See what your peers have to say and how your organization’s challenges, actions and priorities compare to other companies around the world.

Get your free copy by completing the form on ISACA site.

Tags: ISACA, State of Cybersecurity


Jul 28 2022

Messaging Apps Tapped as Platform for Cybercriminal Activity

Category: Cyber crime,Cybercrime,Information Security — DISC @ 8:56 am

Built-in Telegram and Discord services are fertile ground for storing stolen data, hosting malware and using bots for nefarious purposes.

Cybercriminals are tapping the built-in services of popular messaging apps like Telegram and Discord as ready-made platforms to help them perform their nefarious activity in persistent campaigns that threaten users, researchers have found.

Threat actors are tapping the multi-feature nature of messaging apps—in particularly their content-creation and program-sharing components—as a foundation for info-stealing, according to new research from Intel 471.

Specifically, they use the apps “to host, distribute, and execute various functions that ultimately allow them to steal credentials or other information from unsuspecting users,” researchers wrote in a blog post published Tuesday.

“While messaging apps like Discord and Telegram are not primarily used for business operations, their popularity coupled with the rise in remote work means a cybercriminal has a bigger attack surface at their disposal than in past years,” researchers wrote.

Intel 471 identified three key ways in which threat actors are leveraging built-in features of popular messaging apps for their own gain: storing stolen data, hosting malware payloads, and using bots that perform their dirty work, they said.

Storing Exfiltrated Data

Having one’s own dedicated and secure network to store data stolen from unsuspecting victims of cybercrime can be costly and time-consuming. Instead, threat actors are using data-storage features of Discord and Telegram as repositories for info-stealers that actually depend upon the apps for this aspect of functionality, researchers have found.

Indeed, novel malware dubbed Ducktail that steals data from Facebook Business users was recently seen storing exfiltrated data in a Telegram channel, and it’s far from the only one.

Researchers from Intel 471 observed a bot known as X-Files that uses bot commands inside Telegram to steal and store data, they said. Once the malware infects a system, threat actors can swipe passwords, session cookies, login credentials and credit-card details from popular browsers– including Google Chrome, Chromium, Opera, Slimjet and Vivaldi–and then deposit that stolen info “into a Telegram channel of their choosing,” researchers said.

Another stealer known as Prynt Stealer functions in a similar fashion, but does not have the built-in Telegram commands, they added.

Other stealers use Discord as their messaging platform of choice for storing stolen data. One stealer observed by Intel 471, known as Blitzed Grabber, uses Discord’s webhooks feature to deposit data lifted by the malware, including autofill data, bookmarks, browser cookies, VPN client credentials, payment card information, cryptocurrency wallets and passwords, researchers said. Webhooks are similar to APIs in that they simplify the transmission of automated messages and data updates from a victim’s machine to a particular messaging channel.

Blitzed Grabber and two other stealers observed using messaging apps for data storage–—Mercurial Grabber and 44Caliber–also target credentials for the Minecraft and Roblox gaming platforms, researchers added.

“Once the malware spits that stolen information back into Discord, actors can then use it to continue their own schemes or move to sell the stolen credentials on the cybercrime underground,” researchers noted.

Payload Hosting

Tags: Messaging Apps


Jul 28 2022

Critical Samba bug could let anyone become Domain Admin – patch now!

Category: Security patching — DISC @ 8:42 am

Tags: SAMBA


Jul 28 2022

ENISA provides data related to major telecom security incidents in 2021

Category: Information Security,Security Incident — DISC @ 8:36 am

ENISA published a report that includes anonymised and aggregated information about major telecom security incidents in 2021.

ENISA published a report that provides anonymized and aggregated information about major telecom security incidents in 2021.

Every European telecom operator that suffers a security incident, notifies its national authorities which share a summary of these reports to ENISA at the start of every calendar year.

The reporting of security incidents has been part of the EU’s regulatory framework for telecoms
since the 2009 reform of the telecoms package.

This year the report includes data related to reports of 168 incidents submitted by national authorities from 26 EU Member States (MS) and 2 EFTA countries.

The incident had a significant impact on the victim, the total user hours lost (resulted by
multiplying for each incident the number of users by the number of hours) was 5,106 million user
hours. Experts noticed a huge increase compared to 841 million user hours lost in 2020. The reason for this is the impact of a notable EU-wide incident that was reported separately by three MS. ENISA has published technical guidelines on incident reporting under the EECC1, including on thresholds and calculating hours lost.

Below are the takeaways from incidents that took place in 2021:

  • 4,16% of reported incidents in 2021 refer to OTT communication services, for this reason the European Agency required further attention for security incidents related to OTT services.
  • This is the first time that incidents concerning confidentiality and authenticity were reported.
  • The number of incidents labeled as malicious actions passed from 4% in 2020 to 8% in 2021.
  • System failures continue to dominate in terms of impact but the downward trend continues. System failures accounted for 363 million user hours lost compared to 419 million user hours in 2020.
  • The number of Incidents caused by human errors is the same as in 2020.
  • Only 22% of incidents were reported as being related to third-party failures compared to 29%

Let me suggest reading the full report for additional information:

Download

ENISA Telecom Security Incidents 2021

DISC InfoSec

#InfoSecTools and #InfoSectraining

#InfoSecLatestTitles

#InfoSecServices

Ask DISC an InfoSec & compliance related question

Tags: telecom security incidents


Jul 27 2022

How DDoSecrets built the go-to home for Russian leaks

Category: Cyber Threats,Data Breach,Information Security — DISC @ 2:56 pm
How DDoSecrets built the go-to home for Russian leaks

American investigative reporter Emma Best knows how arduous it is to ask for information from government agencies. 

She made more than 5,000 such requests during her career at MuckRock, a non-profit ​​news site that publishes original government documents and conducts investigations based on them. Best was so persistent that the FBI temporarily banned her from filing any more information requests.

She found a way to cut through the government bureaucracy. Together with an anonymous partner known as The Architect, Best founded the whistleblower site Distributed Denial of Secrets (DDoSecrets) in 2018. 

Since then, it has distributed hacked and leaked data from more than 200 entities, including U.S. law enforcement agencies, fascist groups, shell companies, tax havens, and the far-right social media sites Gab and Parler. 

Unlike cybercriminals who sell hacked data on the darknet for personal gain, DDoSecrets says it exposes leaked information for the public good. “Secrets can be used for extortion by threatening to make it public, while public information can’t,” Best said.

Her website has become a go-to place for whistleblowers and hackers, especially given the absence of its most famous predecessor, WikiLeaks, which has been inactive for the last two years.

Russian leaks

https://therecord.media/how-ddosecrets-built-the-go-to-home-for-russian-leaks/

Tags: DDoSecrets


Jul 27 2022

Understand the OT Security and Its Importance

Category: OT/ICS — DISC @ 9:00 am

This article discusses OT security and why it is essential for protecting industrial systems from cyberattacks. We will also discuss common control objectives that can help companies improve their overall cybersecurity posture by implementing effective OT security measures.

Table of Contents

OT Security

Industrial Cybersecurity: Efficiently monitor the cybersecurity posture of your ICS environment, 2nd Edition

IT/OT Security Convergence And Risk Mitigation

DISC InfoSec

#InfoSecTools and #InfoSectraining

#InfoSecLatestTitles

#InfoSecServices

Ask DISC an InfoSec & compliance related question

Tags: ICS & SCADA devices, IT/OT Security, IT/OT Security Convergence, OT security


Jul 27 2022

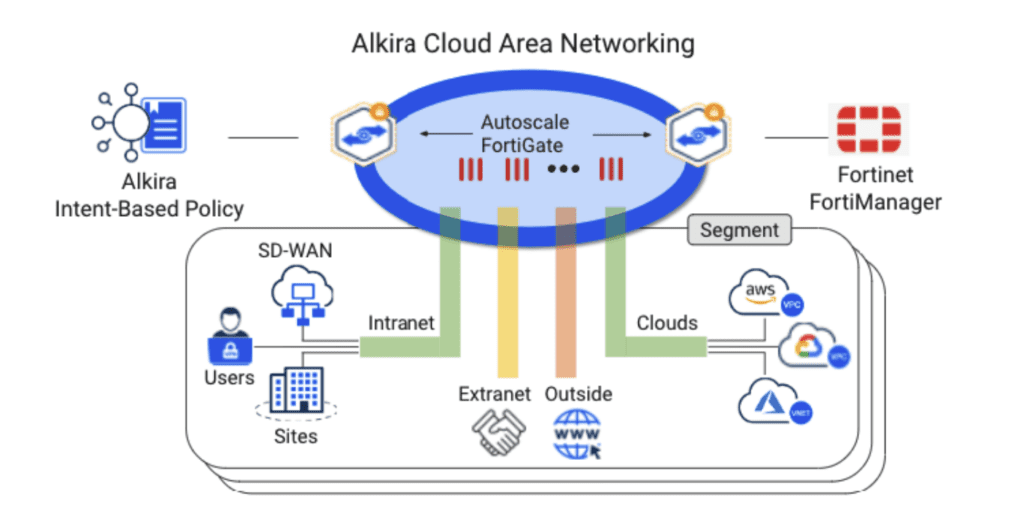
Alkira Partners With Fortinet to Secure Cloud Networks

Category: Cloud computing — DISC @ 8:46 am

Alkira today announced it has integrated its cloud service for connecting multiple networks with firewalls from Fortinet.

Announced at the AWS re:Inforce event, the integration makes it possible to automate the configuration and deployment of Fortinet firewalls via the FortiManager platform using a control plane that integrates with the networking services provided by multiple cloud service providers.

Ahmed Datoo, chief marketing officer for Alkira, said the alliance with Fortinet is in addition to existing support for firewalls from Palo Alto Network.

Alkira is making a case for a control plane for cloud networking that integrates with the application programming interfaces (API) exposed by various cloud service providers. As a result, there is no need for an IT team to deploy agent software on each cloud service to integrate the Alkira service, noted Datoo.

As organizations increasingly deploy workloads across multiple clouds, managing and securing each of the networks that cloud service providers give them access to has become challenging. The Alkira platform is designed to provide a single pane of glass for configuring networking and security services spanning multiple clouds, said Datoo. Those organizations can either use the frameworks provided by vendors such as Fortinet to manage individual elements or use an instance of the open source Terraform tool to programmatically invoke services, he noted.

The challenge organizations face when using multiple clouds is that each one is typically managed in isolation. As a result, IT teams find themselves dedicating IT staff to mastering the various tools required to manage these platforms. Over time, however, the total cost of IT starts to rise as each cloud platform is added to the extended enterprise. Alkira reduces those costs by unifying the provisioning and management of multiple cloud networks, said Datoo. It’s up to each IT organization to decide which cloud platform to use to deploy the Alkira platform to accomplish that goal, he added.

The alliance between Alkira and Fortinet is only the latest example of the convergence of network and security operations. While cybersecurity teams are still needed to define security policies, much of the routine management of firewalls and other security platforms is now handled by network operations—in part, to make up for the chronic shortage of cybersecurity personnel. Network operations, meanwhile, are slowly being integrated with other IT operations workflows to enable organizations to programmatically manage entire IT environments without requiring as many dedicated network specialists.

In the meantime, the attack surface that security teams are being asked to secure continues to expand in the age of the cloud. The issue, of course, is that the size of most organizations’ security teams remains constrained. The only way to secure all those cloud environments at scale is to rethink the entire approach to security operations. In most cases, those approaches were defined in an era where most workloads were deployed on on-premises IT environments that, in comparison, were comparatively simple to secure.

Cloud Security Handbook: Find out how to effectively secure cloud environments using AWS, Azure, and GCP

DISC InfoSec

#InfoSecTools and #InfoSectraining

#InfoSecLatestTitles

#InfoSecServices

Ask DISC an InfoSec & compliance related question

Tags: Alkira, cloud security, Fortinet, Secure Cloud Networks


Jul 27 2022

DUCKTAIL operation targets Facebook’s Business and Ad accounts

Category: Access Control,App Security,Authentication — DISC @ 8:29 am

Researchers uncovered an ongoing operation, codenamed DUCKTAIL that targets Facebook Business and Ad Accounts.

Researchers from WithSecure (formerly F-Secure Business) have discovered an ongoing operation, named DUCKTAIL, that targets individuals and organizations that operate on Facebook’s Business and Ads platform.

Experts attribute the campaign to a Vietnamese financially motivated threat actor which is suspected to be active since 2018.

“Our investigation reveals that the threat actor has been actively developing and distributing malware linked to the DUCKTAIL operation since the latter half of 2021. Evidence suggests that the threat actor may have been active in the cybercriminal space as early as late 2018.” reads the report published by the experts.

The threat actors target individuals and employees that may have access to a Facebook Business account, they use an information-stealer malware that steals browser cookies and abuse authenticated Facebook sessions to steal information from the victim’s Facebook account.

The end goal is to hijack Facebook Business accounts managed by the victims.

The threat actors target individuals with managerial, digital marketing, digital media, and human resources roles in companies. The attackers connected the victims through LinkedIn, some of the samples observed by the experts have been hosted on file or cloud hosting services, such as Dropbox, iCloud, and MediaFire.

WithSecure researchers noticed that samples employed in the DUCKTAIL operation were written in .NET Core and were compiled using its single file feature. This feature bundles all dependent libraries and files into a single executable, it also includes the main assembly. Experts pointed out that the usage of .NET Core and its single-file feature is uncommon in malware development.

The use of .Net Core allows the attackers to embed Telegram.Bot client as well as any other external
dependencies into a single executable and use Telegram channels as Command and Control (C&C).

“Since late last year, the threat actor has shifted entirely to using Telegram as their C&C channel making use of the Telegram Bot functionality. Currently, the adversary only exfiltrates stolen information through the C&C channel and no commands are sent from the C&C to the victim’s machine other than potentially sending e-mail addresses for business hijacking purposes.” continues the report.

In order to steal Facebook session cookies from the victims, the malware scans the machine for popular browsers, including Google Chrome, Microsoft Edge, Brave Browser, and Firefox. For each of the browsers that it finds, it extracts all the stored cookies, including any Facebook session cookie.

The malware also steals information from the victim’s personal Facebook account, including name, email address, date of birth, and user ID, along with other data such as 2FA codes, user agents, IP address, and geolocation

Ducktail

Once obtained the above data, the attackers can access to the victim’s personal account, hijack it by adding their email address retrieved from the Telegram channel and grant themselves Admin and Finance editor access.

“They can edit business credit card information and financial details like transactions, invoices, account spend and payment methods. Finance editors can add businesses to your credit cards and monthly invoices. These businesses can use your payment methods to run ads.” states the report.

Countries affected by DUCKTAIL samples analyzed by the experts includes US, India, Saudi Arabia, Italy, Germany, Sweden, Finland, and the Philippines.

“WithSecure cannot determine the success, or lack thereof, that the threat actor has had in circumventing Facebook’s existing security features and hijacking businesses.” concludes the report. “However, the threat actor has continued to update and push out the malware in an attempt to improve its ability to bypass existing/new Facebook security features alongside other implemented features.”

Facebook Business administrators are recommended to check access permissions for their business accounts and remove any unknown users.

Security Manual. Whatsapp and FacebookSecurity Manual. Whatsapp and FacebookSecurity Manual. Whatsapp and Facebook

Tags: DUCKTAIL operation, Facebook security, Security Manual


Jul 26 2022

Phishing Attacks Skyrocket with Microsoft and Facebook as Most Abused Brands

Category: Information Security,Phishing — DISC @ 4:03 pm

Instances of phishing attacks leveraging the Microsoft brand increased 266 percent in Q1 compared to the year prior.

The bloom is back on phishing attacks with criminals doubling down on fake messages abusing popular brands compared to the year prior. Microsoft, Facebook and French bank Crédit Agricole are the top abused brands in attacks, according to study on phishing released Tuesday.

According to the report by researchers at Vade, phishing attacks abusing the Microsoft brand increased 266 percent in the first quarter of 2022, compared to the year prior. Fake Facebook messages are up 177 percent in the second quarter of 2022 within the same timeframe.

The study by Vade analyzed unique instances of phishing URLs used by criminals carrying out phishing attacks and not the number of phishing emails associated with the URLs. The report tallied the 25 most commonly targeted companies, along with the most abused industries and days of the week for phishing emails.

Phishing By the Numbers

Other top abused brands in phishing attacks include Credit Agricole, WhatsApp, and French telecommunications company Orange. Popular brands also included PayPal, Google and Apple (see chart).

Through the first half of 2022, 34 percent of all unique phishing attacks tracked by the researchers impersonated financial services brands. The next most popular industry for criminals to abuse is cloud and the firms Microsoft, Google and Adobe. Social media was also a popular target with Facebook, WhatsApp and Instagram leading the list of brands leveraged in attacks.

The report revealed the most popular days for sending phishing emails is between Monday and Wednesday. Less than 20 percent of malicious emails are sent on the weekend.

“Phishing attacks are more sophisticated than ever,” wrote Adrien Gendre, chief tech and product officer at Vade in an email to Threatpost.

“Hackers have an arsenal of tools at their disposal to manipulate end users and evade email security, including phishing kits that can identify when they are being scanned by a vendor and trigger benign webpages to avoid detection. End users need to be continually trained to identify the latest phishing techniques,” he wrote.

Phishing Attacks: Advanced Attack Techniques

Tags: phishing attacks


Jul 26 2022

Twitter hacker touting the data of over 5.4 million users, including celebrities and companies, for $30,000

Category: Information Security,Social network — DISC @ 3:30 pm
A Twitter logo is seen on a computer screen

Over 5.4 million Twitter users have reportedly been targeted in a major breach of personal data following revelations earlier this year that the site had a serious security flaw. 

The security flaw came to light in January, when a user on HackerOne named “zhirinovskiy” pointed out that Twitter was vulnerable to hackers seeking to use information for malicious purposes.

At the time, Zhirinovskiy detailed exactly how to exploit the bug and described it as a “serious threat” even in the hands of those with only a “basic knowledge” of scripting and coding. 

Twitter acknowledged the problem five days later and appeared to have fixed the problem a week after that, when it rewarded Zhirinovskiy with a $5,040 bounty for bringing the vulnerability to its attention. 

A seller with the username ‘devil’ claims that “Celebrities, to Companies, randoms, OGs, etc” are included in the data set and is asking for at least $30,000, RestorePrivacy says. 

A spokesperson from Twitter told Fortune: “We received a report of this incident several months ago through our bug bounty program, immediately investigated thoroughly and fixed the vulnerability.”

The spokesperson added that Twitter was “reviewing the latest data to verify the authenticity of the claims and ensure the security of the accounts in question.”

https://fortune.com/2022/07/26/twitter-user-data-breach-hacker-lists-database-of-5-million-users-for-sale/

Tags: Twitter Hack


Jul 26 2022

AWS Adds More Tools to Secure Cloud Workloads

Category: AWS Security — DISC @ 2:16 pm

Amazon Web Services (AWS) today expanded its portfolio of cloud security tools as part of an ongoing effort to make it simpler to secure application environments running on its infrastructure.

The additional services, announced at the AWS re:Inforce event, include support for Amazon EBS Volumes within the Amazon GuardDuty Malware Protection service and the ability to automatically share security findings between Amazon GuardDuty and AWS Security Hub.

In addition, the Amazon Macie data security service can now review and validate sensitive data found in an Amazon S3 cloud storage service, while Amazon Detective can now analyze logs generated by the Amazon Elastic Kubernetes Service (EKS).

AWS is also making it possible to assign a numeric compliance measurement value to Conformance Packs to make it easier to identify major deviations in security posture and is making available in preview an encrypted collaboration service dubbed AWS Wickr.

Finally, AWS is making available in preview tools to assess the security of third-party applications in its marketplace and revealed that the AWS Single Sign-On service (AWS SSO) has been rebranded AWS IAM Identity Center to better reflect the expanded role of the platform.

CJ Moses, CISO and vice president of security engineering for AWS, reminded conference attendees that they should be encrypting everything in the cloud and that they should only be providing external access to data and applications when required. Organizations should especially block access to cloud storage services, he noted.

The rollout of the latest AWS security services comes at a time of intense focus on cloud security as part of a larger effort to better secure software supply chains after a series of high-profile breaches. In general, cloud platforms are more secure than on-premises IT environments; however, the processes used to build and deploy cloud applications are often problematic and can introduce risk. Developers routinely employ open source tools like Terraform to provision cloud infrastructure and accelerate application development. Most of those developers have limited cybersecurity expertise so, inevitably, mistakes are made. The chronic shortage of cybersecurity expertise means most organizations are not able to keep pace with the rate at which workloads are being deployed in the cloud.

AWS contends its platform is more secure than rival platforms because of what it describes as automated reasoning technology that employs mathematical logic to, for example, detect entire classes of misconfigurations. As a result, AWS said it is able to empirically prove a cloud environment is secure. The issue that organizations encounter is that every cloud service provider assumes the organization using its service assumes responsibility for both configuring the infrastructure correctly and then securing the applications deployed on it. Developers, unfortunately, tend to assume more automation is being applied to secure workloads.

On the plus side, more organizations are also starting to embrace DevSecOps best practices to make software supply chains more secure. The challenge is that no matter how much time and effort is made to educate developers, there will always be a development team that makes a mistake— and cybercriminals will find a way to exploit it.

AWS Spring4Shell flaws vulnerabilities WhiteSource Python

AWS Security Cookbook: Practical solutions for managing security policies, monitoring, auditing, and compliance with AWS

DISC InfoSec

#InfoSecTools and #InfoSectraining

#InfoSecLatestTitles

#InfoSecServices

Ask DISC an InfoSec & compliance related question

Tags: AWS security, AWS Security Cookbook, AWS tools


Jul 26 2022

T-Mobile to cough up $500 million over 2021 data breach

Category: Data Breach,data security — DISC @ 8:46 am

Just under a year ago, the US arm of telecomms giant T-Mobile admitted to a data breach after personal information about its customers was offered for sale on an underground forum.

At the time, VICE Magazine claimed to have communicated with the hacker behind the breach via online chat, and to have been offered “T-Mobile USA. Full customer info.”

VICE’s Motherboard reporters wrote at the time that:

The data include[d] social security numbers, phone numbers, names, physical addresses, unique IMEI numbers, and driver licenses information, the seller said. Motherboard has seen samples of the data, and confirmed they contained accurate information on T-Mobile customers.

IMEI is short for International Mobile Equipment Identity, a globally unique serial number burned into your phone when it’s manufactured. Because the IMEI is considered a “non-resettable identifier”, apps on both Android and iOS are restricted from accessing it unless they have been granted special device management privileges, and developers are instructed to rely on user-resettable identifiers such as advertising IDs when legitimately tracking users and devices. You can view your phone’s IMEI by dialling the special phone number *#06#.

Reuters reports that T-Mobile has agreed, in a US federal court in Missouri, to make $350,000,000 available for what are known in America as class-action settlements.

Class actions involve individuals, who would otherwise need to sue individually for impossibly small amounts, banding together with a team of attorneys to bring lawsuits that combine their individual complaints.

Part of the $350 million mega-settlement, says Reuters, is up to $105,000,000 (30% of the total amount) for the lawyers, leaving a slightly less dramatic $245 million for the individuals who joined the suit.

Apparently, more than 75 million people were affected in the breach, though with the standard payout listed by Reuters as $25 per person, it looks as though fewer than 10 million of them decided to sign up to be part of the legal action.

According to Reuters, T-Mobile will also commit to spending “an additional US$150 million to upgrade data security”, bringing its total settlement pledge to half-a-billion dollars.

In return, T-Mobile doesn’t have to admit guilt, so this isn’t a fine or a criminal penalty – it’s a civil agreement to settle the matter.

The settlement still needs approval from from the court, something that’s expected to happen by the end of 2022.

Cyber Insurance counts in a big Data Breach like this, may even be business limiting factor if you don’t have enough coverage.

DISC InfoSec

#InfoSecTools and #InfoSectraining

#InfoSecLatestTitles

#InfoSecServices

Ask DISC an InfoSec & compliance related question

Tags: T-Mobile


Jul 25 2022

PCI DSS: Which PCI SAQ is Right for My Business?

Category: pci dss — DISC @ 12:25 pm

Organisations that fall within Levels 2–4 of the PCI DSS (Payment Card Industry Data Security Standard) can attest to compliance with an SAQ (self-assessment questionnaire).

You will fall into one of those levels if your organisation processes fewer than six million card transactions per year.

There are several types of questionnaire, and in this blog we help you understand which one is right for you.

What is a PCI SAQ?

Organisations that are subject to the PCI DSS must demonstrate that they have taken appropriate steps to secure the payment card data that they hold.

There are two ways to do this: with a PCI SAQ or an RoC (report on compliance). Each payment brand (American Express, Discover, JCB, MasterCard and Visa) has its own requirements, so they establish the eligibility criteria for SAQ or RoC.

The PCI SAQ is the less rigorous method and is typically used for organisations that process fewer than six million transactions annually.

Once it’s completed, the PCI SAQ is signed off by an officer of the merchant or service provider, validating the organisation’s compliance practices.

PCI SAQ types

There are several types of PCI SAQ that apply in certain circumstances. It’s essential that organisations choose the correct assessment. They are as follows:

SAQ A

For merchants that outsource their entire card data processing to validated third parties. This includes e-commerce merchants and mail/telephone order merchants. 

It applies where: 

  • The merchant’s website is hosted and managed by a PCI-compliant third-party payment processor; or 
  • The merchant’s website provides an iframe (inline frame) or URL that redirects customers to a PCI-compliant third-party payment processor. 

Nearly all online merchants aim for SAQ A, because it is the simplest, least time-consuming assessment.

SAQ A-EP

For e-commerce merchants that don’t receive cardholder data but do control the method through which data is redirected to a third-party payment processor. 

It applies where: 

  • The merchant’s website creates a payment form and “direct posts” payment data to a PCI-compliant third-party payment processor; or 
  • The merchant’s website provides an iframe or URL that redirects a consumer to a PCI-compliant third-party payment processor, but some elements of the payment page originate from the merchant website. 

SAQ B

For merchants that only process credit card data via imprint machines or via a standalone dial-out terminal. 

Card imprint machines are non-electronic machines that make an imprint of the payment card, transferring the imprint onto a carbon paper receipt, which is then stored by the merchant. 

Dial-out terminals are electronic machines that use chip and PIN and swipe cards, or require users to manually key in information. To be eligible for SAQ B, a merchant’s standalone dial-out terminal must be connected to a phone line and nothing else. 

SAQ B-IP

For merchants that don’t store card data in electronic format but use IP-connected POI (point-of-interaction) devices. These merchants may handle either card-present or card-not-present transactions.

SAQ C-VT

For merchants that process cardholder data via a virtual payment terminal rather than a computer system. A virtual terminal provides web-based access to a third party that hosts the virtual terminal payment-processing function. 

SAQ C

For merchants that process cardholder data via POS (point-of-sale) systems or other payment application systems connected to the Internet. 

To be eligible for SAQ C, a merchant must operate isolated payment application systems that are connected to the Internet and don’t store electronic cardholder data. 

SAQ D

For those that don’t fit into any of the above categories. It is often referred to as ‘Report on Compliance Light’, because it requires organisations to go through all 12 PCI DSS requirements, albeit on a reduced scale. 

There are separate forms for merchants and service providers. 

SAQ P2PE-HW

For merchants that use card-present transactions, meaning it is not applicable to organisations that deal in e-commerce. 

Merchants that use a PCI-validated P2PE (point-to-point encryption) solution and have implemented it successfully are eligible for SAQ P2PE-HW. 

Identify the right SAQ with IT Governance

Hopefully you’ve now identified which SAQ applies to you, but how do you go about completing the form?

That’s where our PCI DSS Documentation Toolkit can help. It contains all the template documents you need to ensure complete coverage of your PCI DSS requirements.

All you need do is fill in the sections that are relevant to your organisation.

The toolkit also contains a document checker to help you select and edit the appropriate policy, so that you can create and amend documents as needs arise.

The toolkit supports all self-assessment questionnaires, regardless of your specific payment scenario.

It’s fully aligned with the PCI DSS, so you can be sure that your policies are accurate and compliant with the Standard.

PCI DSS Subscription Program

PCI DSS: An Integrated Data Security Standard Guide 

DISC InfoSec

#InfoSecTools and #InfoSectraining

#InfoSecLatestTitles

#InfoSecServices

Ask DISC an InfoSec & compliance related question

Tags: pci dss, PCI SAQ


Jul 25 2022

Office macro security: on-again-off-again feature now BACK ON AGAIN!

Category: Cyber Spy — DISC @ 8:28 am

The phrase Office macros is a harmless-sounding, low-tech name that refers, in real life, to program code you can squirrel away inside Office files so that the code travels along with the text of a document, or the formulas of a spreadsheet, or the slides in a presentation…

…and even though the code is hidden from sight in the file, it can nevertheless sneakily spring into life as soon as you use the file in any way.

Those hidden macros, indeed, can be configured (by the sender, not by the recipient, you understand!) to trigger automatically when the file is opened; to override standard items in Office’s own menu bar; to run secondary programs; to create network connections; and much more.

Almost anything, in fact, that you could do with a regular .EXE file, which is the sort of file that few of us would willingly accept via email at all, even from someone we knew, and that most of us would be deeply cautious about downloading from a website we didn’t already know and trust.

Fighting back against cybercriminals

Thanks to macros and the hidden programming power they provide, Office documents have been widely used by cybercriminals for implanting malware since the 1990s.

Curiously, though, it took Microsoft 20 years (actually, closer to 25, but we’ll be charitable and round it down to two decades) to block Office macros by default in files that arrived over the internet.

As regular Naked Security readers will know, we were as keen as mustard about this simple change of heart, proclaiming the news, back in February 2022, with the words, “At last!”

To be fair, Microsoft already had an operating system setting that you could use to turn on this safety feature for yourself, but by default it was off.

Enabling it was easy in theory, but not straightforward in practice, especially for small businesses and home users.

Either you needed a network with a sysadmin, who could turn it on for you using Group Policy, or you had to know exactly where to go and what to tweak by yourself on your own computer, using the policy editor or hacking the registry yourself.

So, turning this setting on by default felt like an uncontroversial cybersecurity step forward for the vast majority of users, especially given that the few who wanted to live dangerously could use the aforementioned policy edits or registry hacks to turn the security feature back off again.

Apparently, however, these “few” turned out [a] to be more numerous than you might have guessed and [b] to have been more inconvenienced by the change than you might have expected:

https://twitter.com/NakedSecurity/status/1548992597129043970?ref_src=twsrc%5Etfw%7Ctwcamp%5Etweetembed%7Ctwterm%5E1548992597129043970%7Ctwgr%5E%7Ctwcon%5Es1_c10&ref_url=https%3A%2F%2Fnakedsecurity.sophos.com%2F2022%2F07%2F23%2Foffice-macro-security-on-again-off-again-feature-now-back-on-again%2F

Notably, many people using cloud servers (including, of course, Microsoft’s own online data storage services such as SharePoint and OneDrive) had got used to using external servers, with external servernames, as repositories that their friends or colleagues were expected to treat as if they were internal, company-owned resources.

Remember that old joke that “the cloud” is really just shorthand for “someone else’s computer”? Turns out that there’s many a true word spoken in jest.

Organisations that relied on sharing documents via cloud services, and who hadn’t taken the appropriate precautions to denote which external servers should be treated as official company sources…

…found their macros blocked by default, and voiced their displeasure loudly enough that Microsoft officially relented around the middle of 2022.

Within 20 weeks, a change that cybersecurity experts had spent 20 years hoping for had been turned off once more:

What to do?

The hows, whys and wherefores of Office macro security are now officially explained in two Microsoft documents:

Beginning Security with Microsoft Technologies: Protecting Office 365, Devices, and Data

DISC InfoSec

#InfoSecTools and #InfoSectraining

#InfoSecLatestTitles

#InfoSecServices

Ask DISC an InfoSec & compliance related question

Tags: Office macro security


« Previous Page — Next Page »