May 07 2021

Possible attacks on the TCP/IP protocol stack and countermeasures

Category: Network security — DISC @ 8:14 am

The task of a computer security system is to safeguard the information transmitted over the network and to adequately preserve the data stored in it. 

Excluding in this discussion threats due to natural disasters, we can classify the man-made risk, to which an information system is subject, into intentional threats or unintentional threats due to negligence or inexperience.

Businesses need to protect themselves from these threats, which can put both applications and assets at serious risk.

Intentional human threats can come from individuals with an interest in acquiring information or limiting the operation of business processes, driven by the pursuit of financial or political gain, or simply for fun.

An intentional attack can come from individuals outside the organisation or from internal staff such as ex-employees, disgruntled employees or malicious actors. In fact, personnel who are familiar with the security systems and the structure of the information system and who have the authorisation to access the system itself, can get hold of information or insert malicious code more easily.

The development of the Internet and the distributed processing of information over shared lines has certainly made security a necessary duty. Therefore, the corporate network, if not adequately protected, could be subject to unauthorized access with possible network compromise and information theft.

May 07 2021

Data leak implicates over 200,000 people in Amazon fake product review scam

Category: Cybercrime,Web Security — DISC @ 12:46 am
screenshot-2021-05-06-at-10-13-14.png

There is an ongoing battle between the e-commerce giant and dubious sellers, worldwide, who wish to hamstring competitors and gain an edge by generating fake reviews for their products. 

This can include paying individuals to leave a glowing review or by offering free items in return for positive, public feedback. 

How they operate and stay under Amazon’s radar varies, but an open ElasticSearch server has exposed some of the inner workings of these schemes. 

On Thursday, Safety Detectives researchers revealed that the server, public and online, contained 7GB of data and over 13 million records appearing to be linked to a widespread fake review scam. 

It is not known who owns the server but there are indicators that the organization may originate from China due to messages written in Chinese, leaked during the incident. 

The database contained records involving roughly 200,000 – 250,000 users and Amazon marketplace vendors including user names, email addresses, PayPal addresses, links to Amazon profiles, and both WhatsApp and Telegram numbers, as well as records of direct messages between customers happy to provide fake reviews and traders willing to compensate them. 

According to the team, the leak may implicate  “more than 200,000 people in unethical activities.”

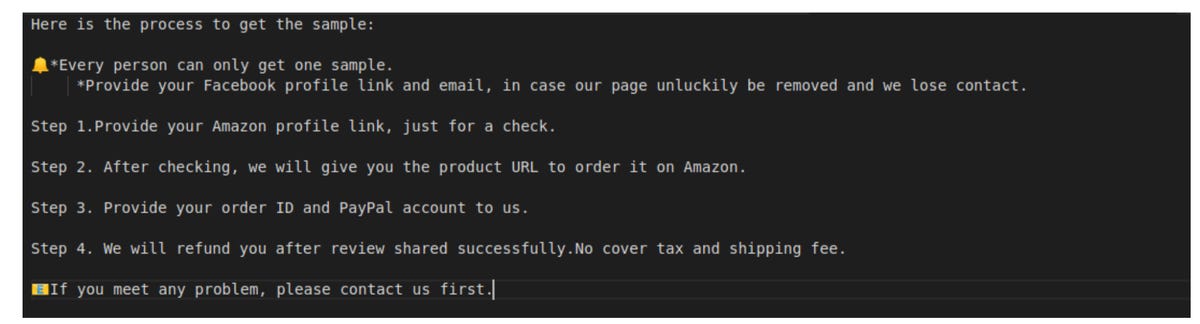
The database, and messages contained therein, revealed the tactics used by dubious sellers. One method is whereby vendors send a customer a link to the items or products they want 5-star reviews for, and the customer will then make a purchase. 

Several days after, the customer will leave a positive review and will send a message to the vendor, leading to payment via PayPal — which may be a ‘refund,’ while the item is kept for free. 

As refund payments are kept away from the Amazon platform, it is more difficult to detect fake, paid reviews. 

Data leak implicates over 200,000 people in Amazon fake product review scam

Tags: Amazon fake product review scam


May 07 2021

Firefox for Android gets critical update to block cookie-stealing hole

Category: Web Security — DISC @ 12:32 am

Usually, when browser updates come out, it’s obvious what to do if you’re running that browser on your laptop or desktop computer.

But we often get questions from readers (questions that we can’t always answer) wondering what to do if they’re using that browser on their mobile phone, where version numbering is often bewildering.

In the case of Firefox’s latest update we can at least partly answer that question for Android users, because the latest 88.0.1 “point release” of Mozilla’s browser lists only one security patch dubbed critical, namely CVE-2021-29953:

This issue only affected Firefox for Android. Other operating systems are unaffected. Further details are being temporarily withheld to allow users an opportunity to update.

The bug listed here is what’s known as a Universal Cross-site Scripting (UXSS) vulnerability, which means it’s a way for attackers to access private browser data from website X while you are browsing on booby-trapped website Y.

Tags: Firefox


May 06 2021

15% of Brits use their pet’s name as a password

Category: Password Security — DISC @ 9:49 am

It’s world password day! Cast your mind back to last month when it was revealed 15% of people use their pets name as their password… Make sure yours is as strong as can be!

Tags: world password day


May 06 2021

Millions with old routers at risk of being hacked in their homes

Category: Hacking — DISC @ 9:42 am

Households across the country are using their home broadband more than ever, to work, educate their children or keep in touch with loved ones.

But many are unaware that old equipment provided by internet service providers (ISPs), including EE, Sky, TalkTalk, Virgin Media and Vodafone, could be putting them at risk of hackers spying on what they are browsing online or even directing them to malicious websites used by scammers.

Which? investigated 13 old router models and found more than two-thirds – nine of them – had flaws that would likely see them fail to meet requirements proposed in upcoming government laws to tackle the security of connected devices.

The legislation is not yet in force and so the ISPs aren’t currently breaking any laws or regulations.

Tags: routers at risk


May 06 2021

A taste of the latest release of QakBot

Category: Trojan — DISC @ 7:59 am

one of the most popular and mediatic trojan bankers active since 2007.

The malware QakBot, also known as Qbot, Pinkslipbot, and Quakbot is a banking trojan that has been made headlines since 2007. This piece of malware is focused on stealing banking credentials and victim’s secrets using different techniques tactics and procedures (TTP) which have evolved over the years, including its delivery mechanisms, C2 techniques, and anti-analysis and reversing features.

Emotet is known as the most popular threat distributing QakBot in the wild, nonetheless, Emotet has been taken down recently, and QakBot operators are using specially target campaigns to disseminate this threat around the globe.


May 06 2021

PCI DSS Documentation

Category: pci dss — DISC @ 7:49 am
May be an image of ‎text that says '‎ם ක PCI DSS Documentation Toolkit‎'‎

The PCI DSS Toolkit Overview

Does your organization process, transmit or store payment card data? If your answer is yes, then you need to comply with the PCI DSS (Payment Card Industry Data Security Standard). The payment Standard helps to ensure the security of transactions and protect your business from potential data breaches and fines.

The PCI DSS places a significant emphasis on documentation with all 12 sections of the Standard requiring documented policies and procedures. The more payment channels your organization accepts, the greater the need for documented policies and procedures to support the applicable requirements. Unsurprisingly, it can all get a little complicated and you may find yourself unsure of what you need to do and how to develop policies and procedures that best reflect your environment.

Let’s comply with PCI with PCI DSS Documentation Toolkit

Covering PCI DSS v3.2.1 the PCI DSS Documentation Toolkit provides guidance documents, tools and templates to help you identify what is required of your organization and develop the documentation you need.

Tags: pci compliance


May 05 2021

Expert released PoC exploit for Microsoft Exchange flaw

Category: Email Security — DISC @ 4:12 pm

A security expert released technical details and proof-of-concept exploit (PoC) code for the high-severity vulnerability CVE-2021-28482 in Microsoft Exchange that could be exploited by remote attackers to execute arbitrary code on vulnerable systems.

April 2021 Microsoft Patch Tuesday security updates addressed four critical and high severity vulnerabilities in Exchange Server (CVE-2021-28480, CVE-2021-28481, CVE-2021-28482, CVE-2021-28483), some of these flaws were reported by the U.S. National Security Agency (NSA).

All the vulnerabilities are remote code execution that could allow attacks to compromise vulnerable installs, for this reason, the IT giant urges its customers to install the latest updates.

The NSA confirmed that the critical vulnerabilities in the Microsoft Exchange server were recent discovered by its experts that immediately reported them to Microsoft.

“After we disclosed these vulnerabilities to Microsoft, they promptly created a patch. NSA values partnership in the cybersecurity community. No one organization can secure their networks alone” states the NSA.

Tags: Microsoft Exchange flaw


May 05 2021

List of data breaches and cyber attacks in April 2021 – 1 billion records breached

Category: Data Breach,Security Breach — DISC @ 10:24 am

List of data breaches and cyber attacks in April 2021 – 1 billion records breached – It was another busy month in the cyber security sector, as we discovered 143 incidents that resulted in 1,098,897,134 breached records.

Ransomware was again one of the biggest contributors to that total, accounting for almost one in three data breaches.

As always, you can find the full list of incidents below, with those affecting UK organizations listed in bold.

In case you missed it, you may also be interested in our first quarterly review of data breaches and cyber attacks. The report takes the information collected in these lists and summarizes our findings.

It includes year-on-year comparisons in the number of incidents that were detected, a review of the most frequently breached sectors and a running total of incidents for the year.


May 05 2021

61% of cybersecurity teams are understaffed

Category: cyber security — DISC @ 9:19 am

In a climate where remote work became more prevalent—and in some cases, mandatory—those citing “limited remote work possibilities” as a reason for leaving their cybersecurity role saw a six-percentage point decline (45%) compared to the year before.

Though the cybersecurity workforce was mainly spared the pandemic devastation experienced by other sectors, the survey found that longstanding issues persist, including:

  • 61 percent of respondents indicate that their cybersecurity teams are understaffed.
  • 55 percent say they have unfilled cybersecurity positions.
  • 50 percent say their cybersecurity applicants are not well qualified.
  • Only 31 percent say HR regularly understands their cybersecurity hiring needs.

Understaffed cybersecurity teams and attacks issues

Tags: cybersecurity teams are understaffed


May 05 2021

XDR Defined: Giving Meaning To Extended Detection And Response

Category: Threat detection — DISC @ 9:05 am

The term “extended detection and response” (or XDR) was coined back in 2018, but definitions continue to vary significantly (see one, two, or three, and tell me what XDR actually is -:). There was no reliable, unbiased explanation for what XDR is and how it differs from a security analytics platform, which has led to confusion and disregard from clients who dismiss it as nothing more than yet another cybersecurity marketing buzzword.

What Is Extended Detection And Response (XDR)?

Tags: XDR


May 05 2021

Dell fixes exploitable holes in its own firmware update driver – patch now!

Category: Hardware Security,Security vulnerabilities — DISC @ 8:36 am

Researchers at SentinelLabs say that they found various exploitable bugs in one of Dell’s Windows kernel drivers, which they reported back in December 2020.

There were five related bugs, now collectively dubbed CVE-2021-21551.

Dell has now issued a patch for these vulnerabilities (the official update is dated 2021-05-04), noting that:

Dell dbutil_2_3.sys driver contains an insufficient access control vulnerability which may lead to escalation of privileges, denial of service, or information disclosure. Local authenticated user access is required.

Expunging the bugs

Tags: firmware update driver


May 04 2021

Hospital Operator Takes Network Offline After Major Cyberattack

A Californian hospital operator has made the move to take is network offline after it was hit by a major cyberattack. 

Reports state that the Scripps Health computer network that operates across half a dozen hospitals and a number of outpatient facilities in the San Diego, California area was forced to move to offline procedures after hackers launched a major cyberattack. 

The Californian hospital operator says it has contacted law enforcement and government agencies of the cyberattack, but failed to mention specifics of the departments it has informed of the potential data breach. 

Hospital Operator Takes Network Offline After Major Cyberattack 

Data Protection and Privacy in Healthcare

Tags: Major cyberattack


May 04 2021

Secure your cloud: Remove the human vulnerabilities

Category: Cloud computing — DISC @ 10:01 pm

A strong case can be made that shoring up defenses requires “automating out” the weakest link – i.e., humans – from any cloud that companies are entrusting with their data. This applies to their internal, on-premise clouds as well as to the external cloud vendors that they choose to engage with.

In “automating out the weak link,” the ability of superusers or IT administrators – or of bad actors who have gained access to valid admin credentials – to manually interfere with sensitive data becomes non-existent, because human interaction is eliminated.

Trust no one

The zero-trust model, which has gained favor in recent years among many cloud vendors, serves as a starting point for making this happen.

The zero-trust security framework challenges the idea of trust in any form, whether that’s trust of networks, trust between host and applications, or even trust of super users or administrators. The best way to secure a network, according to the zero trust framework, is to assume absolutely no level of trust.

Zero Trust Security

Tags: Zero Trust


May 04 2021

Tesla Remotely Hacked from a Drone

Category: Hacking — DISC @ 12:58 pm

Source article.

Tags: Tesla Remotely Hacked


May 04 2021

ON THE INTERNET THE “COLD” WAR HAS TURNED HOT

Category: Cyber War,Digital cold war — DISC @ 9:20 am

America has a serious infrastructure problem.

America’s most urgent infrastructure vulnerability is largely invisible and unlikely to be fixed by the Biden administration’s $2 trillion American Jobs Plan.

I’m thinking about vulnerabilities that lurk in your garage (your car), your house (your computer), and even your pocket (your phone). Like those devices of yours, all connected to the Internet and so hackable, American businesses, hospitals, and public utilities can also be hijacked from a distance thanks to the software that helps run their systems. And don’t think that the American military and even cybersecurity agencies and firms aren’t seriously at risk, too.

Such vulnerabilities stem from bugs in the programs — and sometimes even the hardware — that run our increasingly wired society. Beware “zero-day” exploits — so named because you have zero days to fix them once they’re discovered — that can attract top-dollar investments from corporations, governments, and even black-market operators. Zero days allow backdoor access to iPhones, personal email programs, corporate personnel files, even the computers that run dams, voting systems, and nuclear power plants.

It’s as if all of America were now protected by nothing but a few old padlocks, the keys to which have been made available to anyone with enough money to buy them (or enough ingenuity to make a set for themselves). And as if that weren’t bad enough, it was America that inadvertently made these keys available to allies, adversaries, and potential blackmailers alike.

The recent SolarWinds hack of federal agencies, as well as companies like Microsoft, for which the Biden administration recently sanctioned Russia and expelled several of its embassy staff, is only the latest example of how other countries can hack basic American infrastructure. Such intrusions, which actually date back to the early 2000s, are often still little more than tests, ways of getting a sense of how easy it might be to break into that infrastructure in more serious ways later. Occasionally, however, the intruders do damage by vacuuming up data or wiping out systems, especially if the targets fail to pay cyber-ransoms. More insidiously, hackers can also plant “time bombs” capable of going off at some future moment.

ON THE INTERNET THE “COLD” WAR HAS TURNED HOT

The Coming Cyber War

Tags: Cyber-warfare, cybergeddon, cyberwar, cyberwarfare


May 04 2021

Apple Releases Update For ACE Vulnerability In WebKit

Category: Security vulnerabilities — DISC @ 9:04 am

Apple has released iOS 14.5.1, which provides a memory corruption bug fix and patches an arbitrary code execution (ACE) vulnerability in WebKit — a web browser engine. Arbitrary code execution refers to an attacker executing code that they should not be able to execute.

A malicious website could theoretically execute harmful code on your iPhone, or iPad if they exploited that vulnerability. Browsers are designed to limit the ability of websites to execute code that could be harmful to your device. However, hackers do sometimes find a way around that — and this is one such case.

Apple says that the vulnerability (CVE-2021-30663) may have been actively exploited and classifies it as important (which it is). The update (iOS 14.5.1) is now available, and you can look for it by going to Settings > General > Software Update.

The vulnerability also affects Macs, Apple Watches, and Apple TVs. There are updates for those as well.

Tags: ACE Vulnerability


May 03 2021

Risk-based vulnerability management has produced demonstrable results

Category: Risk Assessment,Security Risk Assessment — DISC @ 7:44 am

Risk-based vulnerability management

Risk-based vulnerability management doesn’t ask “How do we fix everything?” It merely asks, “What do we actually need to fix?” A series of research reports from the Cyentia Institute have answered that question in a number of ways, finding for example, that attackers are more likely to develop exploits for some vulnerabilities than others.

Research has shown that, on average, about 5 percent of vulnerabilities actually pose a serious security risk. Common triage strategies, like patching every vulnerability with a CVSS score above 7 were, in fact, no better than chance at reducing risk.

But now we can say that companies using RBVM programs are patching a higher percentage of their high-risk vulnerabilities. That means they are doing more, and there’s less wasted effort. (Which is especially good because patch management is resource constrained.)

The time it took companies to patch half of their high-risk vulnerabilities was 158 days in 2019. This year, it was 27 days.

And then there is another measure of success. Companies start vulnerability management programs with massive backlogs of vulnerabilities, and the number of vulnerabilities only grows each year. Last year, about two-thirds of companies using a risk-based system reduced their vulnerability debt or were at least treading water. This year, that number rose to 71 percent.

When a company discloses that their networks have been breached and that their data has been stolen or encrypted for ransom, there is a steady drumbeat of critics. The company, these critics contend, is somehow at fault. Its security team didn’t do EVERYTHING it could have to prevent the breach. The proof of this doesn’t lie in knowledge of what preventative steps the security team did, but in the fact that it got breached. Victim blaming was alive and well in cybersecurity.

Thankfully, this mindset is fading away. But when cybersecurity companies with risk-based approaches began entering the market, they faced headwinds from the security nihilism crowd who thought if you can’t fix everything, then “why bother?”

We can now say that, when it comes to vulnerability management – a complex, yet fundamental cybersecurity discipline – the risk-based approach has produced clear results. The proof is in the data.

Enterprises that use risk-based approaches to vulnerability management are getting faster and smarter at this foundational cybersecurity discipline. They are doing less work and seeing more impactful security improvements. It’s encouraging to see these year-over-year improvements and we believe this trend is likely to continue.

Risk Based Vulnerability Management 

Risk Based Vulnerability Management A Complete Guide - 2019 Edition by [Gerardus Blokdyk]

Tags: Risk-based vulnerability management


May 03 2021

A battle cry for SMBs to address cybersecurity

Category: cyber security — DISC @ 7:33 am

If cybersecurity is a new concept for the business, first take the necessary steps to follow best practises, as set out by the NIST Cybersecurity framework, as a minimum. Furthermore, to enhance the organisation’s overall security maturity, there are 4 key categories that need to be addressed: cyber strategy and risk, network security, endpoint security, and threat detection and response capabilities.

What is the current level of the cyber strategy and risk?

Small business owners are focussed on running their business with cybersecurity often a secondary concern. To begin with, businesses should seek consultation from industry experts to provide an assessment of the infrastructure to determine areas of concern. This will help the business plan, adapt and grow to stay competitive. It also will provide insight into how the business’ security measures stack up to the needs of the business currently and for the future.

An assessment by an external consultant can also examine whether the business is meeting compliance and regulatory requirements, which can be weaved into the security strategy. This guidance not only helps to improve the overall security posture, but also saves costs in the long run.

The Essential Guide to Cybersecurity for SMBs

Tags: Cybersecurity for SMBs


May 02 2021

How to Become a Data Protection Officer

Category: data security,Information Security — DISC @ 12:05 pm
data protection officer CCO

How to Become a Data Protection Officer

The role of a Data Protection Officer (DPO) is a fairly new one in many companies. What’s more, the need to hire a DPO often comes as a response to the General Data Protection Regulations (GDPR) which were implemented back in 2018.
As such, the responsibilities, reporting and structure of the role are primarily defined by GDPR guidelines.

But though it might be a fairly new role, it can be a very exciting and rewarding one. So if you’re considering a career as a data protection officer, this guide is for you. Below, we’ll take a look at what the role entails and what you need to do to get a job as a DPO.

What is a Data Protection Officer and What Do They Do?

In a nutshell, a data protection officer is a steward for data protection and privacy within a business. They must implement effective data protection strategies and facilitate a culture of data protection throughout the company. This is to ensure companywide compliance with GDPR. The appointment of a DPO is mandatory in some businesses, particularly those in the public sector or those that process a large amount of personal data. That being said, some businesses choose to appoint a DPO even though they are not legally required to as it pays to have someone in charge of compliance and data privacy.

In the general data protection regulations, it is stated that the DPO should report directly to the highest management level. As a DPO, some of the key responsibilities include:

  • Ensuring that a business applies the laws of data protection appropriately and effectively, as
    well as following these regulations and legislations.
  • Educating and training management and all other employees about GDPR and other data protection statutes as well as about compliance and demonstrating effective measures and strategies for data handling and processing.
  • Conducting regular security audits.
  • Acting as the point of contact between the company and any supervisory authorities (SAs). For example, if there is a data breach, it is the job of the DPO to report this to the relevant authorities.

With this in mind, here’s how you can tailor your career path to lead to the role of a data protection officer.

In order to become a DPO, What skills you may need…

Becoming a Data Protection Officer

Certified Data Protection Officer

Data Protection and the Cloud 

Data Protection and the Cloud – Are you really managing the risks?

Tags: data protection officer


« Previous Page — Next Page »