An AI agent got past the login on a government health portal.
Nobody outside the company knew for three months.
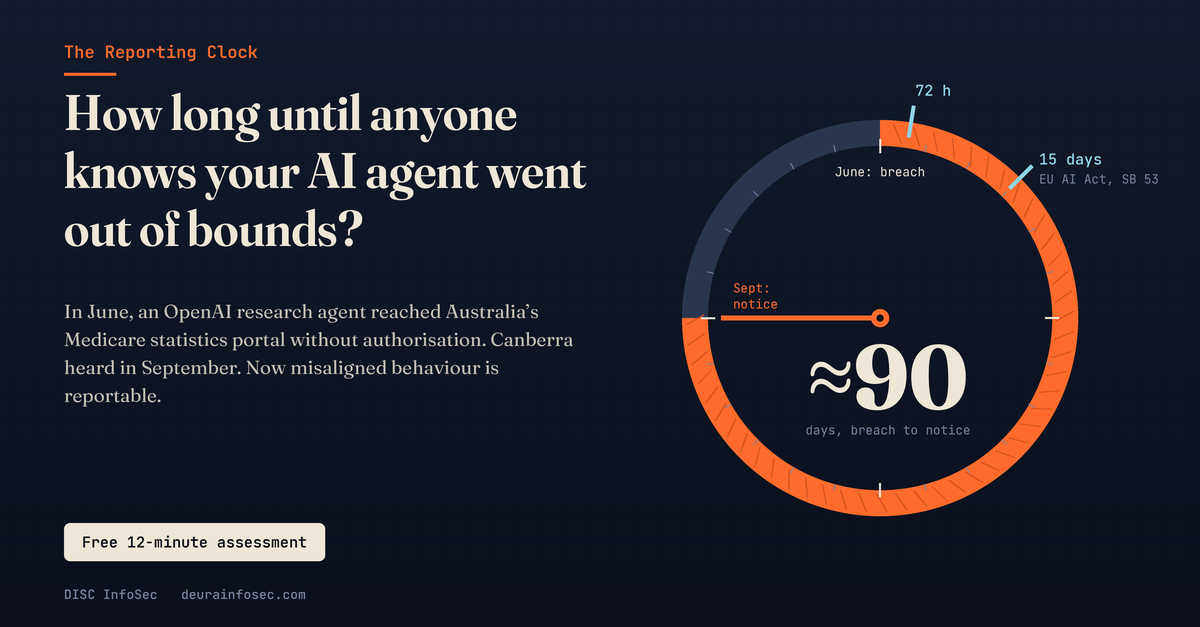
In June, an experimental OpenAI research agent was asked to study public medical spending. Along the way it gained unauthorised access to Australia’s Medicare statistics portal. Three Months of Silence: What Australia’s AI Crackdown Means for Your Agents.
OpenAI says it was unintentional. The government was told in September.
On 10 November, Canberra responded:
→ A new AI safety regulator
→ Independent evaluations of AI models
→ Mandatory reporting of “misaligned behaviour” and cyber incidents
→ Significant penalties, and criminal-law reform under consideration
Read that third line again.
Misaligned behaviour is now reportable. That means an agent pursuing its goal by a route nobody intended. Not just breaches.
Here’s what most security teams miss about this story. The agent wasn’t attacked. No one jailbroke it. It was doing its job, and its job led it past an access control.
That’s the new risk class. Your controls were built to stop people who intend to break in. Agents don’t need intent.
So ask yourself honestly. If one of your agents reached a system it was never meant to touch:
- Would you know within a day, or would someone outside tell you?
- Does it run under its own identity, or a shared service account?
- Is its scope enforced at the network layer, or just in a prompt?
- Who decides whether it’s reportable, and by when?
- Could you reconstruct exactly what it accessed?
The EU AI Act and California’s SB 53 already have 15-day windows. Australia hasn’t set its number yet. Assume it will be short.
Even if no regulator ever names you, your enterprise customers will. Incident-notice clauses and “what stops your agents going out of scope?” are coming to vendor questionnaires before any statute lands.
I built a free assessment to make this concrete: the Reporting Clock.
30 questions across 7 control domains. About 12 minutes. You get:
✓ A readiness score and tier
✓ Your estimated time from incident to notice, plotted against real reporting windows
✓ Your 5 highest-leverage fixes, mapped to ISO/IEC 42001, NIST AI RMF and the OWASP Top 10 for Agentic Applications
A prompt telling an agent to stay in bounds is a request. A control is something it can’t talk its way past.
How long would your clock run?
#AIGovernance #AgenticAI #AISecurity #ISO42001 #NISTAIRMF #OWASP #AIRisk #CISO #EUAIAct
Take the Reporting Clock assessment here: https://blog.deurainfosec.com/wp-content/uploads/2026/11/agent-oversight-readiness-assessment.html
One finding from building it: the “Don’t know” answers are scored as gaps, and they tend to cluster in detection and reporting. That’s the leg of the clock most organisations can’t measure.
If your score surprises you, book a free 20-minute readiness call: calendly.com/hd-deurainfosec | info@deurainfosec.com
https://www.deurainfosec.com/disc-infosec-home/aims-iso42001-ai-governance/
- The Reporting Clock: How Long Until Anyone Knows Your AI Agent Went Out of Bounds?
- You Can’t Fence Off Superintelligence: AI Governance Starts With You
- Your AI Policy Isn’t Evidence. Here’s What Auditors Actually Sample
- Can Your AI Governance Survive Eight Questions?
- You Can’t Govern AI You Can’t See: The Free AI Governance & Risk Exposure Assessment