InfoSec Compliance & AI Governance For over 20 years, DISC InfoSec has been a trusted voice for cybersecurity professionals—sharing practical insights, compliance strategies, and AI governance guidance to help you stay informed, connected, and secure in a rapidly evolving landscape.
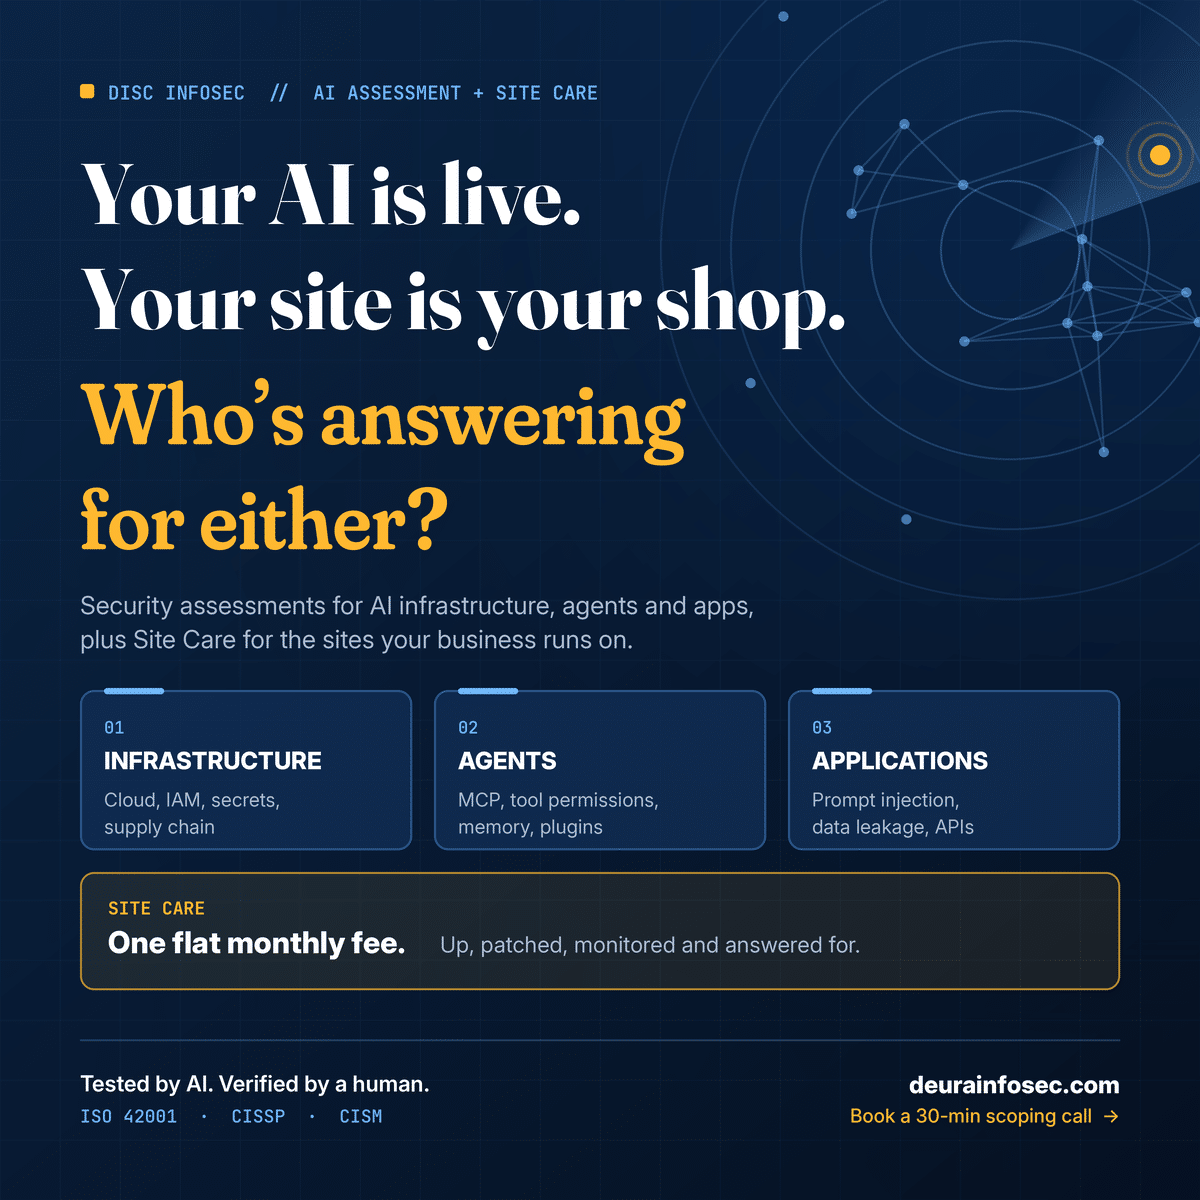
Your AI Is Already in Production. Is It Governed? DISC InfoSec AI Infrastructure, Agents & Applications Assessment
Most small firms didn’t design their AI stack; it piled up. There’s a model API in the website, an agent with inbox access, and a plugin someone installed to solve last Tuesday’s problem. Each one works, and each one opens a door nobody has checked.
DISC InfoSec runs security and AI infrastructure assessments for SMBs. We also build governed AI infrastructure for firms whose name goes on the work: founders, agencies, and research and consulting teams who need AI that fixes this week’s problem without creating next quarter’s liability.
How we test. We run authorized, scoped testing with a modern AI-driven offensive toolkit: Claude Guide for Pentesting, Burp Suite Professional with Burp AI, Microsoft PyRIT, CyberSentinel-AI, CyberStrike, Metatron, PentestCode, SecureSecSuite, SecSuite, Xalgorix, and PenTestSwarmAI. Automation gives us breadth, and a senior practitioner checks every finding, so you get real risk and not scanner noise. AI-assisted testing, vulnerability verification, validation, and report generation.
AI-powered penetration testing tools that leverage AI models to support security assessments, verify and validate vulnerabilities, reduce false positives, and automate technical report generation.
What we cover
Infrastructure: cloud, identity, secrets, and supply chain.
Agents: tool permissions, MCP servers, memory, and third-party plugins, tested against the OWASP Agentic Top 10.
Applications: prompt injection, data leakage, and API and web flaws, tested against the OWASP LLM and Web Top 10.
Governance: alignment with ISO 42001, NIST AI RMF, and the EU AI Act, so your fixes also hold up in customer due diligence.
Site Assurance: Your website is your storefront. Who’s protecting it when you’re not there?
Keep your website secure, updated, monitored, and running smoothly—all for one predictable monthly fee.
Don’t wait for downtime or a security breach to take action. Contact us today for a Site Assurance consultation and discover how affordable proactive website protection can be.
Annual prepay: $2,490 a year, two months free.
Multi-site discount: $249 per site, $199 per site from the third site on.
One-time onboarding fee: around $299 to audit the site.
Sites with ecommerce, logins, or AI features such as chatbots, agents, or forms connected to models carry more risk. Consider a separate “Site Care Plus” around $449, DISC scope them as a project instead of stretching the flat fee to cover them.
Why DISC InfoSec. We led Virtual Data Room to ISO 42001 certification on the first attempt and authored their MCP Governance Standard. Our credentials include AICP, CISSP, CISM, and ISO 42001 and 27001 Lead Implementer. You get enterprise rigor at a size that fits your firm.
Book a 30-minute scoping call: calendly.com/hd-deurainfosec · info@deurainfosec.com
Identify AI Vulnerabilities, Reduce Business Risk, and Prevent Costly Security Incidents.
Download AI Penetration Testing Datasheet to Explore Our Testing Approach and Business Benefits.
MITRE CALDERA is an open-source cybersecurity platform developed by MITRE for automated adversary emulation and security assessment. It enables organizations to simulate real-world cyberattacks based on MITRE ATT&CK techniques to test and improve their defenses.
Key Features:
Automated Red Teaming – Simulates adversary behaviors using predefined or custom attack chains.
Run CALDERA: python3 server.py --insecure Access the web UI at http://localhost:8888 (default credentials: admin:admin). This default may not work in ver 5.0 – check conf/default.yml
2. Deploying Agents
CALDERA uses lightweight agents to simulate adversarial actions on endpoints.
Create New Adversary Profiles: Define a new attack sequence with custom scripts or commands.
Use Plugins: Enhance CALDERA with plugins like Stockpile (TTP Library) and Manx (Remote Access Tool).
Use Case Examples
Credential Dumping Simulation – Test if your security tools detect LSASS process memory access.
Lateral Movement Testing – Simulate adversaries moving between hosts using SMB or RDP.
Data Exfiltration Exercise – See if your DLP solutions flag unauthorized file transfers.
Creating Custom Attack Simulations in CALDERA
To build a tailored adversary emulation plan, you’ll need to create custom TTPs (Tactics, Techniques, and Procedures) and integrate them into an adversary profile.
Automating Response Testing – Check if your SIEM or SOAR detects and mitigates the attack.
Example for a specific attack scenario, like lateral movement or credential dumping:
Example: Simulating Lateral Movement Using CALDERA
Lateral movement techniques help assess an organization’s ability to detect and respond to adversaries moving across systems. In this example, we’ll create a CALDERA attack simulation that uses SMB-based remote command execution (ATT&CK ID: T1021.002).
1. Creating the Lateral Movement TTP (Ability)
We’ll define an ability that uses psexec (a common SMB-based remote execution tool).
Test Defense Evasion: Modify commands to use encoded PowerShell payloads.
Check SIEM Logs: Verify if your security tools detected and logged the lateral movement attempt.
Example: Simulating Lateral Movement on Linux Using SSH
Lateral movement on Linux often involves SSH-based remote command execution (MITRE ATT&CK ID: T1021.004). This simulation will test whether security controls detect an attacker moving across Linux systems via SSH.
1. Creating a Custom SSH Lateral Movement TTP (Ability)
yamlCopyEdit- id: fghij67890
  name: Linux Lateral Movement Test
  description: Simulates an adversary moving laterally via SSH on Linux
  atomic_ordering:
    - abcde12345
Save this file in caldera/data/adversaries/.
3. Running the Lateral Movement Simulation
Restart CALDERA to load the new configurations:bashCopyEditpython server.py --insecure
Deploy an Agent on an initial Linux system.
Ensure SSH Credentials Are Available:
Modify the agent to include SSH credentials using CALDERA’s fact system:cssCopyEditfact: {remote.user: "testuser", remote.pass: "password123", remote.host: "192.168.1.100"}
Create a New Operation:
Go to: Operations → Create Operation
Adversary Profile: Select Linux Lateral Movement Test
Assign an Agent
Start the Operation
Monitor Execution:
If successful, the target machine will have a file /tmp/loot.txt containing the username.
Check logs to verify execution.
4. Enhancing the Simulation
Use Key-Based Authentication Instead of Passwords:yamlCopyEditcommand: | ssh -i /home/#{remote.user}/.ssh/id_rsa #{remote.user}@#{remote.host} "whoami > /tmp/loot.txt"
Simulate Data Exfiltration: Copy files from the remote system using scp.
Test SIEM Detection: Ensure logs capture unauthorized SSH connections.
1. MISP (Malware Information Sharing Platform & Threat Sharing)
Purpose: Designed to facilitate sharing threat intelligence between organizations, MISP is invaluable for building a collaborative defense strategy against cyber threats.
Key Features:
Collects, stores, and shares indicators of compromise (IOCs) efficiently.
Supports STIX/TAXII for standardized threat intelligence sharing.
Offers real-time alerts, advanced tagging, and classification of incidents.
Use Case: Organizations use MISP to streamline incident response and threat intelligence management, making it a cornerstone of cybersecurity strategies.
Tracecat is an open-source automation platform for security teams. The developers believe security automation should be accessible to everyone, especially understaffed small- to mid-sized teams. Core features, user interfaces, and day-to-day workflows are based on existing best practices from best-in-class security teams.
Use specialized AI models to label, summarize, and enrich alerts. Contextualize alerts with internal evidence and external threat intel:
Find cases using semantic search
MITRE ATT&CK labels
Whitelist / blacklist identities
Categorize related cases
MITRE D3FEND suggestions
Upload evidence and threat intel
Tracecat is not a 1-to-1 mapping of Tines / Splunk SOAR. The developers aim to give technical teams a Tines-like experience but with a focus on open-source and AI features.
While Tracecat is designed for security, its workflow automation and case management system are also suitable for various alerting environments, such as site reliability engineering, DevOps, and physical systems monitoring.
Turn security alerts into solvable cases:
Click-and-drag workflow builder – Automate SecOps using pre-built actions (API calls, webhooks, data transforms, AI tasks, and more) combined into workflows. No code required.
Built-in case management system – Open cases direct from workflows. Track and manage security incidents all-in-one platform.
Tracecat is cloud-agnostic and deploys anywhere that supports Docker. It’s available for free on GitHub.
The framework conducts reconnaissance on active assets and completes its operation with a scan for vulnerabilities, secrets, misconfigurations, and potential phishing domains, utilizing open-source and proprietary tools.
Some of the features that make Mantis stand out are:
Automated discovery, recon, and scan
Distributed scanning (split a single scan across multiple machines)
Scan customization
Dashboard support
Vulnerability management
Advanced alerting
DNS service integration
Integrate new tools (existing and custom) in minutes
“Last year, we explored open-source frameworks our organization can use to monitor assets. We wanted to set up an asset discovery framework that allows us to add custom scripts, enable or disable tools to run based on configs, scale, and deploy the framework across a cluster of VMs. We also wanted to find a way to ingest domains from DNS services into our databases. This led us to create Mantis, an asset discovery framework that could help bug bounty hunters as well as security teams,” Prateek Thakare, lead developer of Mantis, told Help Net Security.
System requirements
Supported OS: Ubuntu, macOS
4GB RAM
2 cores
16GB of storage
Mantis is CPU intensive, so it’s advisable to run it on a dedicated virtual machine.
Future plans and download
“We are planning to have our dashboard making it easier to view and monitor the assets. We will also work on improvising the discovery, recon, and scan process by adding new tools and custom scripts,” Thakare concluded.