The Evidence Lifecycle: Which Organizational Events to Log for Liability — and How Long to Keep Them
Oct 16, 2026 · @disc infosec
Why logs are your liability defense
When an auditor, regulator, or plaintiff’s attorney asks “prove it,” your logs are the only answer that counts. Policies show intent. Logs show what actually happened, who did it, and when.
Most organizations log plenty of data and still lose the argument. They capture firewall noise for 30 days but can’t produce the board minute that approved an AI system, the access review from the quarter a contractor left, or the model version that made a disputed credit decision 18 months ago.
The fix is to stop thinking about logs as an IT setting and start thinking about them as an evidence lifecycle: identify the events that create legal or regulatory exposure, decide what proof each one needs, and keep that proof exactly as long as the exposure lasts — no shorter, and no longer.
This post gives you a method for finding those events, a lifecycle map for both the organization and its AI systems, what ISO/IEC 27001, ISO/IEC 42001, the EU AI Act, and the NIST AI RMF actually require, and a retention matrix you can adapt this week.
How to identify the key events: the four-question test
A “key event” is any moment that someone may later need you to prove. Not every log line qualifies. Run each candidate event through four questions; one “yes” makes it a key event.
- Does it grant, change, or remove authority? Board approvals, delegations, access grants, admin elevation, an AI agent receiving a new tool or permission.
- Does it change your risk posture? A new vendor, a new AI model in production, a material configuration change, an exception to policy, an accepted risk.
- Does it create an obligation to someone outside the company? A customer contract, a regulator notification clock, a consent captured from a data subject, a breach that starts a 72-hour timer.
- Could it be disputed later? An automated decision about a person, a termination, a pricing or credit outcome, a model output a customer relied on.
Then find the events where they actually live. You don’t need to invent them. They are already sitting in six places:
- Legal and regulatory register — every law, contract clause, and standard you’re bound to implies events you must prove.
- Risk register and AI risk assessments — every treated risk implies a control, and every control implies evidence.
- AI system inventory — every system has a lifecycle; every lifecycle stage has a decision.
- HR and identity systems — joiners, movers, leavers, and privileged roles.
- Contracts and vendor register — onboarding, reassessment, termination, data return.
- Incident and complaint history — what has already gone wrong tells you what will be asked about next.
The output of this exercise is an event catalog: event, owner, system of record, evidence produced, legal driver, and retention period. Everything else in this post fills in that catalog.
The organizational lifecycle map
Every stage of a company’s life produces events that a buyer, auditor, regulator, or court may later examine. Formation and exit happen once; change and crisis repeat many times, and each repetition creates a fresh evidence obligation.
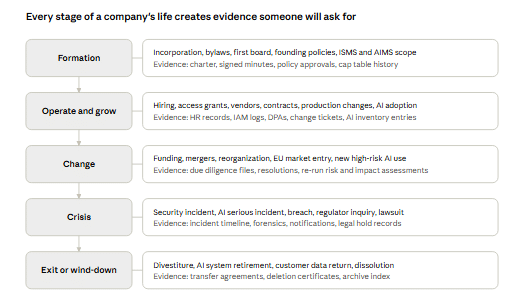
The stages that bite hardest are the ones teams don’t plan for. During an acquisition, the buyer’s diligence team will ask for three years of access reviews and every AI impact assessment. During a wind-down, you still owe customers proof that their data was returned or destroyed, and that proof must outlive the company’s operating systems.
The AI system lifecycle: events that must leave a trail
Every AI system you build or buy runs a lifecycle inside the organization’s lifecycle, and each stage owes its own evidence. ISO/IEC 42001 A.6.2.8 sets the floor: event logs at least while the system is in use. The EU AI Act asks for logs across the system’s whole lifetime.
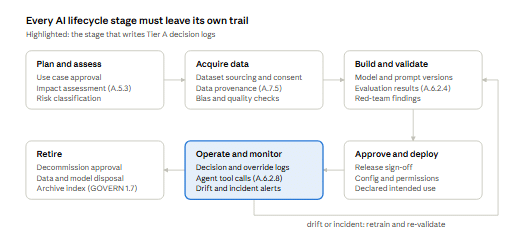
The operate stage writes most of the volume and most of the liability. It is where a customer disputes a decision, where an agent takes an action nobody approved, and where a regulator’s reporting clock starts. It is also the stage that loops: each retraining creates new versions, evaluations, and approvals that have to be traceable back to the decisions they produced.
The question to ask at every stage is simple: if this system harmed someone two years from now, could we show what it was, who approved it, what data shaped it, and what it actually did?
What the frameworks actually require
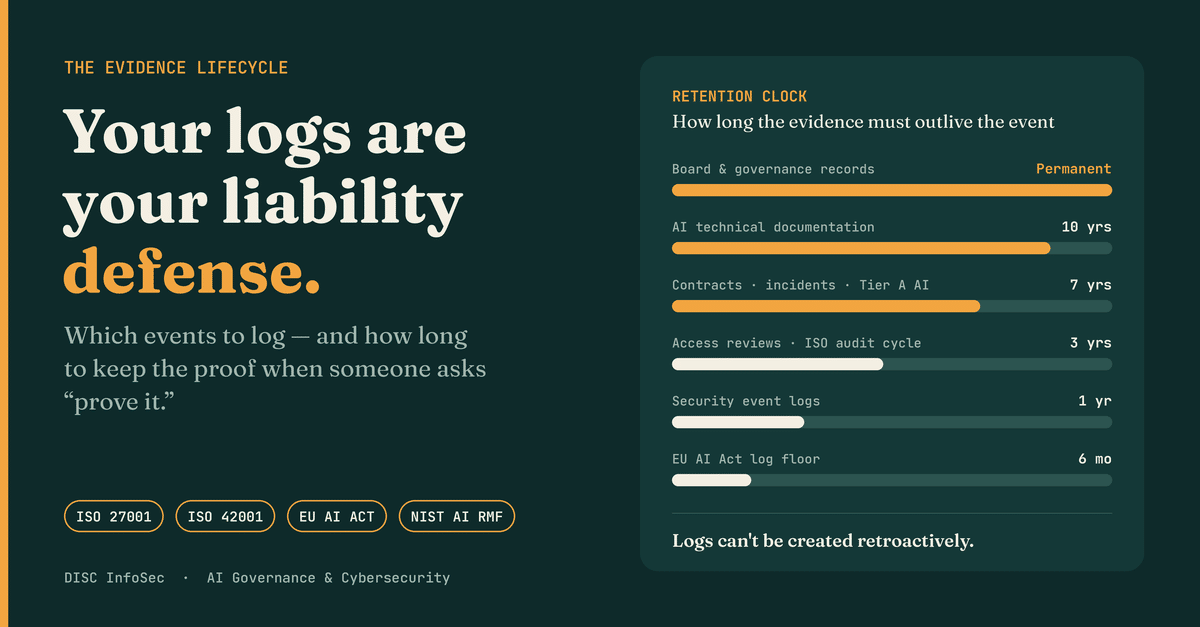
Only one of the four frameworks sets a hard retention clock for logs: the EU AI Act. The two ISO standards require you to define retention and prove you follow it. The NIST AI RMF expects you to be able to trace and reconstruct. Your retention schedule has to satisfy all four at once.
| Framework | What it requires you to log or keep | Retention it sets | Status |
|---|---|---|---|
| ISO/IEC 27001:2022 | Cl. 7.5 documented information; A.8.15 logging; A.8.16 monitoring; A.8.17 clock synchronization; A.5.28 collection of evidence; A.5.33 protection of records; A.5.24–5.27 incident records | None fixed. A.5.31 and A.5.33 tie it to your legal, regulatory, and contractual requirements | Certifiable; 3-year certification cycle |
| ISO/IEC 42001:2023 | Cl. 7.5; A.6.2.8 AI system event logs; A.5.3 documented impact assessments; A.6.2.7 technical documentation; A.7.5 data provenance; Cl. 10.2 nonconformity records | None fixed. A.6.2.8 requires logging at least while the AI system is in use, with defined retention | Certifiable; 3-year certification cycle |
| EU AI Act (high-risk) | Art. 12 automatic event logging across the system’s lifetime; Art. 18 documentation; Art. 72 post-market monitoring; Art. 73 serious incident reporting | Logs: at least 6 months for providers (Art. 19) and deployers (Art. 26(6)), longer if other law requires. Technical documentation, QMS records, and declaration of conformity: 10 years after placing on the market | Mandatory. Annex III systems from 2 Dec 2027; Annex I systems from 2 Aug 2028 |
| NIST AI RMF 1.0 | GOVERN 1.6 AI system inventory; GOVERN 1.7 decommissioning; MEASURE 3 tracking of risks over time; MANAGE 4.1 post-deployment monitoring; MANAGE 4.3 incident tracking and communication | None. Expects enough record to reconstruct decisions and outcomes | Voluntary; the de facto US benchmark |
Three points matter for liability.
The EU AI Act clock moved, but it didn’t stop. The AI Omnibus, Regulation (EU) 2026/1744, entered into force on 27 July 2026 and deferred the stand-alone high-risk obligations to 2 December 2027. The classification rules didn’t change, and Article 50 transparency duties largely still apply from August 2026. A high-risk system you deploy today will need 2027-grade logs, and logs can’t be created retroactively.
Six months is a floor, not a target. The Act’s six-month minimum yields to any longer period in Union or national law. A credit model’s decision log will usually be governed by the lending record rules and limitation periods around it, not by Article 26.
“Not specified” doesn’t mean “optional.” An ISO auditor will ask for your retention schedule, then sample it. A log you said you keep for 2 years and can’t produce at month 14 is a nonconformity. A log you keep for 10 years with no reason is a GDPR storage-limitation problem. Both standards reward a schedule that is written down, justified, and followed.
The retention matrix: what to keep and for how long
The rule behind every row: keep evidence as long as someone can still hold you to the event, plus a margin, and not a day longer. That means the longest of (a) the regulatory minimum, (b) the contractual commitment, (c) the limitation period for claims, and (d) one full ISO certification cycle so your auditor can sample it.
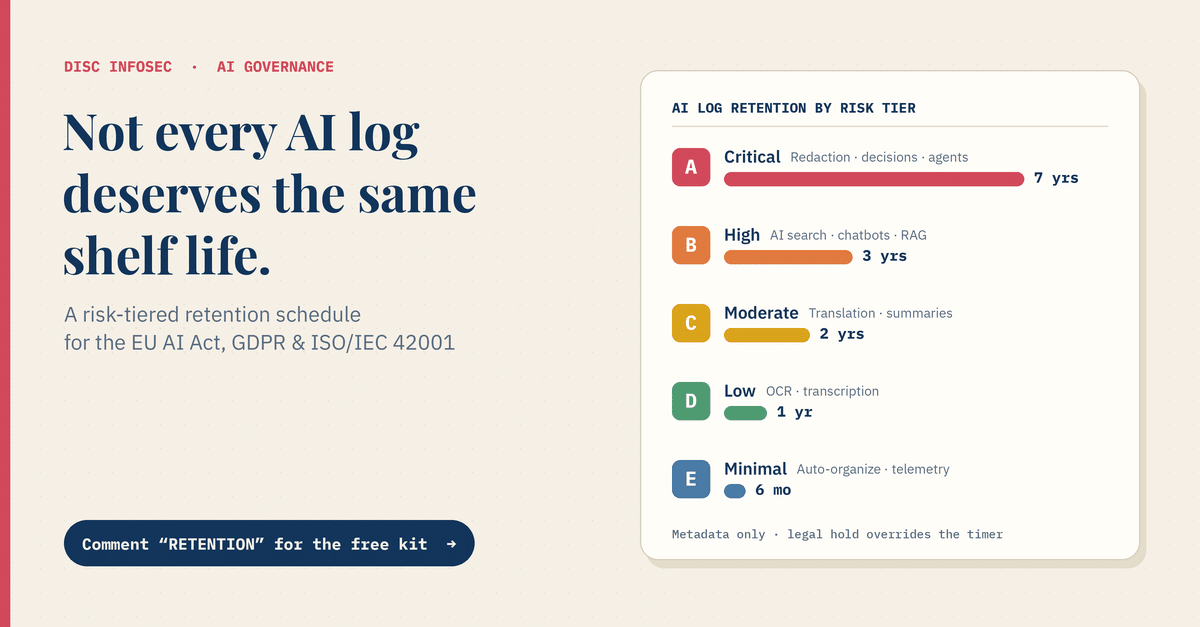
In our previous post, AI Log Retention: Why Every AI Log Doesn’t Deserve the Same Shelf Life, we tiered AI logs from Tier A (critical) to Tier E (minimal). This matrix places those tiers inside the wider organizational picture.
| Event category | Key events | Evidence to keep | Recommended retention | Main drivers |
|---|---|---|---|---|
| Corporate governance | Formation, bylaws, board and committee approvals, equity changes, AI policy adoption, risk appetite | Signed minutes, resolutions, cap table history, policy approval records | Permanent (life of entity, then per dissolution rules) | State corporate law; M&A due diligence; ISO 27001/42001 Cl. 5 leadership evidence |
| Finance and tax | Transactions, audits, revenue recognition | Ledgers, audit workpapers, approvals | 7 years | IRS; SOX §802 for public companies |
| Contracts and customers | Signature, amendments, SLA breaches, termination, data return | Executed contracts, change history, notices, deletion certificates | Contract end + 7 years | Limitation periods; customer audit clauses |
| People (joiner, mover, leaver) | Hire, screening, role change, privileged role grant, termination | HR records, screening results, acknowledgments, offboarding checklists | Termination + 4–7 years; Form I-9 per federal rule | FLSA; IRS; EEOC; ISO 27001 A.6.1, A.6.5 |
| Identity and access | Account creation, privilege elevation, access reviews, removal | IAM audit logs, review sign-offs, break-glass records | 3 years (reviews); 1 year minimum for raw logs | ISO 27001 A.5.18, A.8.2, A.8.15; PCI DSS 10.5.1 |
| Security monitoring | Authentication, admin actions, alerts, data egress | SIEM events, alert triage notes | 12 months hot, archive to 3 years | ISO 27001 A.8.15–8.17; PCI DSS; cyber insurance terms |
| Change and configuration | Production changes, emergency changes, policy-as-code updates | Tickets, approvals, diffs, rollback records | 3 years | ISO 27001 A.8.32; ISO 42001 A.6.2.5 |
| Risk and compliance | Risk assessments, risk acceptances, SoA versions, audit findings, management reviews | Versioned registers, signed acceptances, CAPA records | Superseded + 3 years | ISO 27001/42001 Cl. 6, 9, 10 |
| Vendors and AI suppliers | Onboarding, due diligence, reassessment, offboarding | Questionnaires, SOC 2/ISO reports, DPAs, exit evidence | Relationship end + 7 years | ISO 27001 A.5.19–5.22; ISO 42001 A.10; GDPR Art. 28 |
| Privacy | Consent, DSARs, DPIAs, transfers | Consent records, request logs, DPIA versions | Consent: processing period + limitation period; CCPA request records: 24 months | GDPR Arts. 5, 7, 30, 35; CCPA regulations |
| Incidents and breaches | Detection, triage, notification, closure | Timeline, forensic evidence, notifications, lessons learned | Closure + 7 years; indefinite under legal hold | ISO 27001 A.5.24–5.28; state breach laws; EU AI Act Art. 73 |
| AI governance records | AI inventory entries, impact assessments, technical documentation, conformity | Versioned AIIAs, model cards, declarations | 10 years after placing on the market or retirement (high-risk); retirement + 3 years otherwise | EU AI Act Art. 18; ISO 42001 A.5.3, A.6.2.7; NIST GOVERN 1.6 |
| AI decisions (Tier A) | Consequential outputs about people: credit, hiring, insurance, access | Decision record: input reference, model version, output, human reviewer, override | At least 6 months; in practice the governing record rule, often 3–7 years | EU AI Act Arts. 12, 19, 26(6); sector lending and employment rules |
| AI operations (Tiers B–E) | Agent tool calls, permission grants, retrieval, guardrail blocks, drift alerts | Metadata-only event logs; prompt and response content minimized | 6 months to 3 years by tier | ISO 42001 A.6.2.6, A.6.2.8; NIST MANAGE 4.1 |
| AI model and data provenance | Training data sourcing, evaluation, bias testing, release, retraining, decommission | Dataset lineage, eval reports, version registry, retirement record | Life of the model + 10 years (high-risk); + 3 years otherwise | ISO 42001 A.6.2.4, A.7.5; NIST GOVERN 1.7 |
These periods are defensible starting points for a US-based B2B SaaS or financial services firm with EU exposure. They are not legal advice. Sector rules (for example, broker-dealer, HIPAA, or lending record rules) can lengthen any row, so have counsel confirm the final schedule.
Seven liability traps, including the new ones AI creates
A retention schedule fails in court for predictable reasons. Five are classic; two are new with AI.
1. Deleting under legal hold. Once litigation or an investigation is reasonably anticipated, every scheduled deletion of relevant records must stop. Automated lifecycle rules don’t know that. Build a hold flag that overrides deletion jobs, and log who set and released it.
2. Keeping too much. Retention beyond your stated purpose violates GDPR storage limitation and inflates discovery cost. Every extra year of raw prompts is another year of exposure in a breach or subpoena. Defensible deletion — scheduled, documented, and verified — is as much a control as retention.
3. Logs that can be edited aren’t evidence. ISO 27001 A.5.33 and A.8.15 require protection against falsification. Use write-once storage (for example, S3 Object Lock or Azure immutable blobs), hash chaining, and A.8.17 clock synchronization. Restrict log deletion rights to a role nobody uses day to day.
4. Logs held by someone else. If your LLM provider, agent platform, or SaaS vendor holds the logs, you have a retention promise you can’t keep. Put export rights, retention periods, and legal-hold cooperation into the contract, and test the export before you need it.
5. The oversight checkbox. A “reviewed by human” flag records the reviewer’s statement, not what they saw or changed. For Tier A decisions, log the model output, what the reviewer saw, the action they took, and the time spent. That is the difference between claiming oversight under EU AI Act Article 14 and proving it.
6. Log poisoning (new). Attackers now plant prompt-injection payloads in fields that end up in logs: user agents, file names, support tickets, chat messages. When an AI SOC assistant or summarizer later reads those logs, the payload runs. Treat log content as untrusted input to any AI tool, and never give a log-reading agent write or delete rights over the logs it reads.
7. Agents erasing their own trail (new). An over-permissioned agent with infrastructure access can change logging configuration, rotate logs, or delete them, by accident or under injection. Log every agent tool call and permission grant to a store the agent can’t reach. Alert on any change to logging configuration made by a non-human identity.
One more caution: AI logs leak. Prompts carry PII, secrets, and deal terms, which turns your log store into a high-value target. Default to metadata-only AI logs, keep content only where a Tier A decision needs it, and redact before storage, not after.
Your 90-day plan
You can go from scattered logs to an auditable evidence lifecycle in one quarter.
- Days 1–30: Find the events. Run the four-question test across your legal register, risk register, AI inventory, HR, vendor list, and incident history. Produce the event catalog with an owner and system of record for each event.
- Days 31–60: Set the clocks. Assign every catalog entry a retention period using the matrix above. Tier your AI logs A to E. Have counsel sign off, then publish the schedule as part of your records management standard under ISO 27001 and ISO 42001 Clause 7.5.
- Days 61–90: Make it provable. Configure retention in each system, add immutable storage and the legal-hold override, move agent logs out of agents’ reach, and add vendor export clauses. Then test it: pick five events from 14 months ago and try to produce the evidence in under an hour.
That last test is the one that matters. Controls are rarely why organizations fail audits or lose disputes; missing evidence is.
Need a hand?
DISC InfoSec helps B2B SaaS and financial services firms build evidence that holds up under ISO/IEC 27001, ISO/IEC 42001, the EU AI Act, and the NIST AI RMF. We led Virtual Data Room through ISO/IEC 42001 Stage 2 certification on the first attempt, including its AI log retention and records management standard.
Book a free 30-minute call at calendly.com/hd-deurainfosec, or email info@deurainfosec.com. Comment EVIDENCE on the LinkedIn post and we’ll send you the event catalog and retention matrix template.
Sources
- EU Digital Omnibus on AI enters into force — National Law Review
- EU AI Act’s high-risk deadline: deferred, not cancelled — Cloud Security Alliance
- The AI Act implementation timeline under the AI Omnibus — Future of Privacy Forum
- Regulation (EU) 2024/1689 (EU AI Act), Articles 12, 14, 18, 19, 26, 72, 73
- ISO/IEC 27001:2022 and ISO/IEC 42001:2023, Clause 7.5 and Annex A
- NIST AI 100-1, AI Risk Management Framework 1.0
- Your ISO 27001 Certificate Has an AI-Shaped Hole in It
- Someone Is Running Your AI Models Right Now. You’re Paying for It
- Your AI Agent Is Only as Secure as Its Harness: The Hidden Layer of AI Risk
- Your AI Is Live. Your Site Is Your Shop. Who’s Answering for Either?
- Sam Altman Just Issued His Scariest Warning Yet — Fear Tactic or Real Signal?